

This page provides an overview of the design principles, implementation options, and security blueprints used to establish enterprise landing zones on Google Cloud.
If you are a cloud architect, security administrator, or platform engineer, use the information on this page to evaluate landing zone deployment models, establish resource hierarchies, configure identity federation and hybrid networking, and enforce compliance controls before executing workload migrations.
Before you read this page, you should have a basic understanding of your organization's governance model, network topology, and compliance requirements.
Landing zone implementation options
Google Cloud provides a structured progression of tools for building landing zones, as shown in the following diagram:
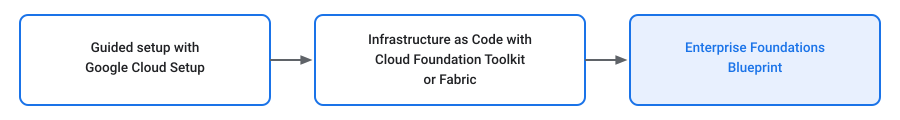
Guided setup with Google Cloud Setup
For small teams or initial pilot migrations, the Google Cloud Setup guided flow provides interactive console guidance to configure basic organization settings, billing accounts, administrative users, and initial project structures.
Infrastructure as Code with Cloud Foundation Toolkit or Fabric
For repeatable, automated enterprise deployments, construct landing zones by using Infrastructure as Code (IaC) templates based on the following toolkits:
- Foundation Toolkit (CFT): a collection of modular, production-ready Terraform blueprints created by Google Cloud that enforce standard security and networking patterns.
- Cloud Foundation Fabric (CFF): an open-source suite of composable Terraform modules and end-to-end blueprint examples designed for fast implementation of enterprise environments.
Enterprise foundations blueprint
For enterprise organizations requiring advanced security boundaries and compliance guardrails, deploy the Enterprise Foundations Blueprint. Based on Foundation Toolkit modules, this blueprint provides the following features:
- Organizational hierarchy: structured folders for development, staging, and production workloads.
- Identity and access management: Cloud Identity federation and strict Identity and Access Management (IAM) role assignments.
- Hybrid networking: Shared VPC network with Partner Interconnect or Dedicated Interconnect and Cloud DNS routing.
- Perimeter guardrails: enforced organization policies and VPC Service Controls to prevent data exfiltration.
Compliance framework mapping
When migrating regulated workloads to Google Cloud, map on-premises security controls to the following cloud security features:
- PCI-DSS and HIPAA compliance: enforce VPC Service Controls perimeters and use Assured Workloads to manage data residency and encryption keys.
- FedRAMP compliance: deploy pre-configured FedRAMP landing zones by using Assured Workloads control packages.
- Audit reporting: enable Cloud Audit Logs and export logs to BigQuery for compliance reporting.
Reference architectures
For architectural patterns, security controls, and design guides, see the following resources in the Google Cloud Architecture Center:
- Migration to Google Cloud: Building your foundation
- Google Cloud Landing Zone Design Guide
- Enterprise Security Foundations Blueprint
- Google Cloud Deployment Archetypes
- Google Cloud Well-Architected Framework