# Collect Microsoft 365 logs
Supported in:
This document describes how you can collect Microsoft 365 logs by setting up a Google Security Operations
feed and how log fields map to Google Security Operations Unified Data Model (UDM) fields.
This document also lists the supported audited activities and supported Microsoft 365 version.
For an overview about data ingestion to Google Security Operations, see [Data ingestion to Google Security Operations](https://docs.cloud.google.com/chronicle/docs/data-ingestion-flow).
## Overview
The following deployment architecture diagram shows how Microsoft 365 and Google Security Operations feed
is configured to send logs to Google Security Operations. Each customer deployment might
differ from this representation and might be more complex.

The architecture diagram shows the following components:
- **Microsoft 365**. The Microsoft 365 service from which you collect logs.
- **Google Security Operations feed**. The Google Security Operations feed that fetches logs from Microsoft 365 and writes logs to Google Security Operations.
- **Google Security Operations**. Google Security Operations retains and analyzes the logs from
Microsoft 365.
> [!NOTE]
> **Note:** The Google Security Operations parser for Microsoft 365 supports logs only in English language.
An ingestion label identifies the parser which normalizes raw log data
to structured UDM format. The information in this document applies to the parser
with the `OFFICE_365` ingestion label.
## Before you begin
Ensure you have the following prerequisites:
- All systems in the deployment architecture are configured with the UTC time zone.
- Microsoft 365 version 2204 Build 16.0.15128.20248 or later
- A [Microsoft 365 Enterprise E5 subscription](https://www.microsoft.com/en-in/microsoft-365/enterprise/e5) with Microsoft Security and Compliance Center feature
### Deployment Overview
- A typical deployment consists of Microsoft Office 365 which sends the logs, and the Google SecOps feed which fetches the logs.
### How to configure Microsoft 365 logs
- Grant the required privileges and permissions to the user to generate and export
different events for all the supported Microsoft products. A user whose credentials
are used to authenticate against the API must have the `ActivityFeed.Read` permission.
To ingest DLP data, the `ActivityFeed.ReadDlp` permission is required.
For information about permissions, see [Permissions to access management APIs](https://docs.microsoft.com/en-us/office/office-365-management-api/get-started-with-office-365-management-apis#specify-the-permissions-your-app-requires-to-access-the-office-365-management-apis)
- Configure Microsoft 365 to search and export logs. Microsoft Entra ID
is the directory service for Microsoft 365. It takes up to 24 hours to generate the logs.
For more information, see [Search the audit log](https://docs.microsoft.com/en-us/microsoft-365/compliance/search-the-audit-log-in-security-and-compliance?view=o365-worldwide)
Microsoft Office 365 logs collection in Google SecOps is done via third-party API feeds integration. To configure it, you need to create and configure a Microsoft Entra App that Google SecOps will use. Follow these steps to create and configure the Entra ID App:
- [Set up the Microsoft Entra ID app](https://learn.microsoft.com/en-us/entra/identity-platform/quickstart-register-app?tabs=client-secret,expose-a-web-api)
> [!CAUTION]
> **Caution:** To avoid **HTTP 429 (Too Many Requests)** errors and ingestion delays, don't reuse the same shared key or storage account across multiple feeds.
- [Configure the Microsoft Entra for permissions](https://learn.microsoft.com/en-us/entra/identity-platform/quickstart-configure-app-access-web-apis) This link shows an example of how to configure the permissions for Microsoft Graph API
- [Create client secret in the Entra app](https://learn.microsoft.com/en-us/entra/identity-platform/quickstart-register-app?tabs=client-secret#add-credentials)
## Permissions for Office 365 Management APIs
| Permission | Type | Usecase of the Permission | Description |
|---|---|---|---|
| **ActivityFeed.Read** | Application | **(Required)** To read standard audit logs | Read activity data for your organization |
| **ActivityFeed.ReadDlp** | Application | **(Optional)** If you want to ingest DLP data | Read DLP policy events including detected sensitive data |
- **Note:**
- For the Google SecOps feed, Entra App needs to have Application-level permissions (not Delegated permissions):
- Grant the required privileges and permissions to the user to generate and export different events for all the supported Microsoft products.
- A user whose credentials are used to authenticate against the API must have the ActivityFeed.Read permission.
- To ingest DLP data, the ActivityFeed.ReadDlp permission is required.
- For information about permissions, see [Permissions to access management APIs](https://docs.microsoft.com/en-us/office/office-365-management-api/get-started-with-office-365-management-apis#specify-the-permissions-your-app-requires-to-access-the-office-365-management-apis)
- Note down the created Entra App Client Secret, Entra App Client ID, Entra ID Tenant ID.
- The created client secret value is displayed only at the time of creation.
## Set up feeds
There are two different entry points to set up feeds in the
Google SecOps platform:
- **Settings \> Data Management \> Feeds \> Add New Feed** (On SIEM-only platform, **Settings \> Feeds \> Add New Feed**)
- **Content Hub \> Content Packs \> Get Started**
> [!NOTE]
> **Note:** The Content Hub is not available on the SIEM standalone platform. To upgrade, contact your Google SecOps representative.
## Set up feeds from Settings \> Data Management \> Feeds
1. Click the **Azure platform** pack.
2. Locate the **Office 365** feed.
3. Specify values for the following fields:
- **Source Type**: Third party API (recommended)
- **OAUTH client ID**: Specify the client ID that you obtained previously.
- **OAUTH client secret**: Specify the client secret that you obtained previously.
- **Tenant ID**: Specify the tenant ID that you obtained previously.
- **Content Type** : Specify type from the following options.
- Audit.AzureActiveDirectory: User identity management.
- Audit.Exchange: Mail and calendaring server.
- Audit.SharePoint: Web-based collaborative platform.
- Audit.General: Includes all other workloads not included in the previous content types.
- DLP.All: Data loss prevention workloads.
- **API Full path**: Microsoft Graph REST API endpoint URL.
- **API Authentication Endpoint**: Microsoft Active Directory Authentication Endpoint.
**Advanced Options**
- **Feed Name**: A prepopulated value that identifies the feed.
- **Asset Namespace** : [Namespace associated with the feed](https://docs.cloud.google.com/chronicle/docs/investigation/asset-namespaces.md.txt).
- **Ingestion Labels**: Labels applied to all events from this feed.
> [!NOTE]
> **Note:** Source API returns duplicate events for this log type. This is the intended behavior to prevent loss of any audit events.
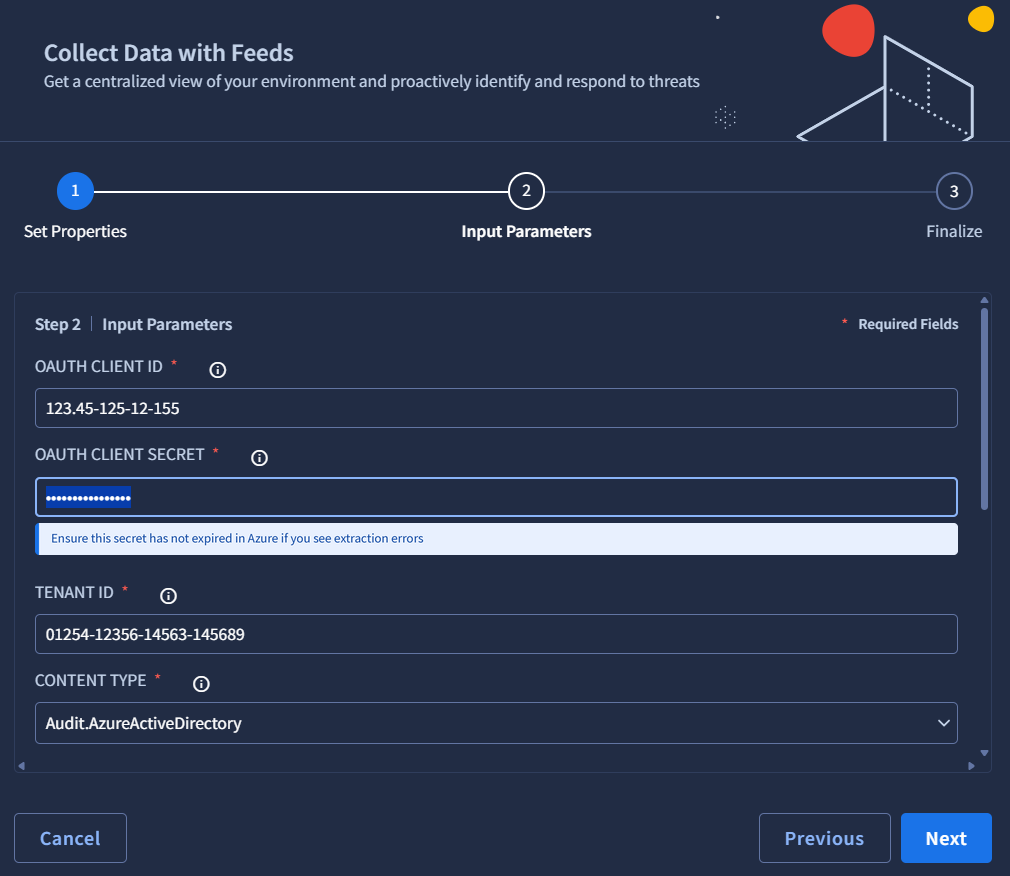
**Figure 1.** Microsoft 365 feed configuration showing the OAuth Client Secret field and expiration callout
4. Click **Create feed**.
For more information about Google Security Operations feeds, see [Google Security Operations feeds documentation](https://docs.cloud.google.com/chronicle/docs/administration/feed-management.md.txt).
### Supported Activities and Products for the Google Security Operations
- Review the activities and products that the Google Security Operations parser supports.
The following table list the activities and products that the Google Security Operations parser supports:
| Activities | Products |
|---|---|
| File and page activities | SharePoint Online and OneDrive for Business |
| Folder activities | SharePoint Online and OneDrive for Business |
| SharePoint list activities | SharePoint Online |
| Sharing and access request activities | SharePoint Online and OneDrive for Business |
| Synchronization activities | SharePoint Online and OneDrive for Business |
| Site permissions activities | SharePoint Online |
| Site administration activities | SharePoint Online |
| Exchange mailbox activities | Microsoft 365 Group mailboxes |
| User administration activities | Microsoft 365 admin center |
| Azure AD group administration activities | Microsoft 365 admin center |
| Application administration activities | When an administrator adds or changes an application that is registered in Azure AD |
| Role administration activities | Microsoft 365 admin center |
| Directory administration activities | Microsoft 365 admin center |
| Power BI activities | Power BI |
| Microsoft Teams activities | Microsoft Teams |
| Microsoft Teams Shifts activities | Shifts app in Microsoft Teams |
| Microsoft Teams Healthcare activities | Patients application in Microsoft Teams |
| Microsoft Teams Shifts activities | Shifts app in Microsoft Teams |
| Yammer activities | Yammer |
| Microsoft Power Automate activities | Power Automate (formerly called Microsoft Flow) |
| Microsoft PowerApps activities | Power Apps |
| Microsoft Stream activities | Microsoft Stream |
| Quarantine activities | Quarantine email messages in Office 365 |
| Microsoft Forms activities | Microsoft Teams |
| Sensitivity label activities | Labeling activities for SharePoint Online and Teams |
| Retention policy and retention label activities | NA |
| Briefing email activities | Briefing email |
| MyAnalytics activities | MyAnalytics |
| Information barriers activities | NA |
| Disposition review activities | NA |
| Communication compliance activities | NA |
| Undefined Activity | NA |
## Supported Microsoft 365 log formats
The Microsoft 365 parser supports logs in JSON format.
## Supported Microsoft 365 Sample Logs
- JSON
{
"ClientIP": "198.51.100.1",
"CreationTime": "2024-12-01T03:04:31",
"EndpointMetaData": {
"Application": "msedge.exe",
"DeviceName": "dummy.device.com",
"DlpAuditEventMetadata": {
"DlpPolicyMatchId": "2a755fab-cc10-4",
"EvaluationTime": "2024-12-01T03:02:00.0350707+00:00"
},
"EAv2Enriched": false,
"EndpointOperation": "FilePrinted",
"EnforcementMode": 1,
"FileExtension": "pdf",
"FileSize": 44117,
"FileType": "PDF",
"GroupName": "",
"Hidden": false,
"JitTriggered": false,
"Justification": "",
"MDATPDeviceId": "MDATPDeviceId",
"OriginatingDomain": "dummy.domain.com",
"ParentArchiveHash": "",
"Platform": 1,
"PreviousFileName": "",
"RMSEncrypted": false,
"SensitiveInfoTypeData": [
{
"ClassifierType": "PatternMatch",
"Confidence": 75,
"Count": 1,
"SensitiveInfoTypeId": "5fc14ed1-1a76-4189-b8b4-7a95297532e4",
"SensitiveInfoTypeName": "Profanity Blocker Level 2 words",
"SensitiveInformationDetailedClassificationAttributes": [
{
"Confidence": 65,
"Count": 1
},
{
"Confidence": 75,
"Count": 1
},
{
"Confidence": 85,
"Count": 0
}
],
"SensitiveInformationDetectionsInfo": {
"DetectedValues": [
{
"Name": "Off",
"Value": "tional information, reference the Flexible Time Off policy in the Grant Thornton Personnel Handbook"
},
{
"Name": "off",
"Value": "iness expenditures on the corporate card and pay off any balance related to personal expenses (inclu"
}
]
},
"SensitiveTypeSource": "Tenant",
"UniqueCount": 1
},
{
"ClassifierType": "PatternMatch",
"Confidence": 75,
"Count": 1,
"SensitiveInfoTypeId": "e165b7af-ec",
"SensitiveInfoTypeName": "Profanity Blocker All update",
"SensitiveInformationDetailedClassificationAttributes": [
{
"Confidence": 65,
"Count": 1
},
{
"Confidence": 75,
"Count": 1
},
{
"Confidence": 85,
"Count": 0
}
],
"SensitiveInformationDetectionsInfo": {
"DetectedValues": [
{
"Name": "Off",
"Value": "tional information, reference the Flexible Time Off policy in the Grant Thornton Personnel Handbook"
},
{
"Name": "off",
"Value": "iness expenditures on the corporate card and pay off any balance related to personal expenses (inclu"
}
]
},
"SensitiveTypeSource": "Tenant",
"UniqueCount": 1
},
{
"ClassifierType": "PatternMatch",
"Confidence": 75,
"Count": 11,
"SensitiveInfoTypeId": "668896ff-1809",
"SensitiveInfoTypeName": "tensions",
"SensitiveInformationDetailedClassificationAttributes": [
{
"Confidence": 65,
"Count": 11
},
{
"Confidence": 75,
"Count": 11
},
{
"Confidence": 85,
"Count": 0
}
],
"SensitiveInformationDetectionsInfo": {
"DetectedValues": [
{
"Name": "avi",
"Value": "or SEC client may impact independence.) *Please navigate to the Reportable Investment List (RIL) to "
},
{
"Name": "avi",
"Value": "l information, reference What To Do If You Are Leaving The Firm, Corporate Card Resource Center, and"
},
{
"Name": "pdf",
"Value": "t.com and request what paystubs you would like a pdf copy of. The request should include your name, "
},
{
"Name": "pdf",
"Value": " to CSV, Export to oel, Download Certificates (pdf) or Download Certificates (ZIP) After departing"
},
{
"Name": "iso",
"Value": "tems. Share that list with your engagement supervisor to ensure client is notified and access to cli"
},
{
"Name": "iso",
"Value": "e client. Please work with your engagement supervisor and client to confirm where they should be ret"
},
{
"Name": "iso",
"Value": "ecovery team with a CC: to your engagement supervisor with client address, phone number and client i"
},
{
"Name": "iso",
"Value": "int site, etc.) and notify your engagement supervisor or appropriate supervisor/individual. Confirm"
},
{
"Name": "iso",
"Value": " your engagement supervisor or appropriate supervisor/individual. Confirm all client software and/o"
},
{
"Name": "ini",
"Value": "t not limited to data, workpapers, templates, training materials, deliverables, contracts, or agreem"
},
{
"Name": "ini",
"Value": " or part of the offer letter you received when joining the firm. If you do not have a copy, reach ou"
},
{
"Name": "ZIP",
"Value": "oad Certificates (pdf) or Download Certificates (ZIP) After departing from the Firm, if you need ver"
},
{
"Name": "sys",
"Value": "em Client/Project Transition If you have client system/network access, identify any clients for who"
},
{
"Name": "sys",
"Value": "ess to client networks or information technology systems. Share that list with your engagement super"
},
{
"Name": "sys",
"Value": "o ensure client is notified and access to client systems are disabled. If you have client assets and"
},
{
"Name": "sys",
"Value": " personal records by accessing the CPE reporting system, https://grantthornt"
},
{
"Name": "sys",
"Value": "departed from Grant Thornton, your access to the system will be removed. Unused points will expire s"
},
{
"Name": "mov",
"Value": "nt-licensed software and information have been removed from any personally owned computer. Senior M"
},
{
"Name": "mov",
"Value": " in Intune/CompPortal, you are responsible for removing it from said device. To remove Intune, go to"
},
{
"Name": "mov",
"Value": "sponsible for removing it from said device. To remove Intune, go to the Intune FAQs in Canvas for a "
},
{
"Name": "mov",
"Value": "Intune FAQs in Canvas for a copy of the Intune removal guide. If you need additional assistance, con"
},
{
"Name": "mov",
"Value": "sonal device, personal email, cloud account or removable drive. Confirm all firm software and/or fi"
},
{
"Name": "mov",
"Value": "rm-licensed software and information have been removed from any personally owned device. Confirm th"
},
{
"Name": "mov",
"Value": "ersonally owned device. Confirm that you have removed personal, non-work-related files from any fir"
},
{
"Name": "mov",
"Value": "nt Thornton, your access to the system will be removed. Unused points will expire seven (7) calendar"
},
{
"Name": "mov",
"Value": "sent to the last address we have on file. If you move to a new address before the end of the year, p"
},
{
"Name": "dot",
"Value": " the appropriate jurisdiction • Select the three dots at the top right • Select one of the available"
},
{
"Name": "Doc",
"Value": " A copy of your NDA or NDNS can be found in your Document Records in myGT (myGT \\u003e Me \\u003e Personal Info"
},
{
"Name": "Doc",
"Value": "ords in myGT (myGT \\u003e Me \\u003e Personal Information \\u003e Document Records). Your NDA or NDNS could be a stan"
},
{
"Name": "doc",
"Value": "Records). Your NDA or NDNS could be a standalone document or part of the offer letter you received w"
},
{
"Name": "doc",
"Value": "ts: Please refer to the Benefits Upon Separation document, regarding health insurance, 401(k) benefi"
},
{
"Name": "cab",
"Value": "nton. Please note that not all items may be applicable to you. Completed Item Client/Project Transit"
},
{
"Name": "cab",
"Value": "rief with the Facility Security Office. If applicable, transfer ownership of an inbox, distribution"
},
{
"Name": "cab",
"Value": ".gt.com. Please note, this process is only applicable to Grant Thornton assets and badges. For guid"
},
{
"Name": "CSV",
"Value": "t one of the available options: Print, Export to CSV, Export to Excel, Download Certificates (pdf) o"
}
]
},
"SensitiveTypeSource": "Tenant",
"UniqueCount": 11
},
{
"ClassifierType": "PatternMatch",
"Confidence": 85,
"Count": 1,
"SensitiveInfoTypeId": "50b8b56b-4ef8e",
"SensitiveInfoTypeName": "All Full Names",
"SensitiveInformationDetailedClassificationAttributes": [
{
"Confidence": 65,
"Count": 1
},
{
"Confidence": 75,
"Count": 1
},
{
"Confidence": 85,
"Count": 1
}
],
"SensitiveInformationDetectionsInfo": {
"DetectedValues": [
{
"Name": "Dummy User",
"Value": "klist to assist you as you transition from Grant Thornton. Please note that not all items may be app"
},
{
"Name": "Dummy User",
"Value": " you will receive a welcome email from the Grant Thornton Alumni Community with details for activati"
},
{
"Name": "Dummy User",
"Value": " sites to reflect dates of employment with Grant Thornton Time \\u0026 Expenses Submit and release your t"
},
{
"Name": "Dummy User",
"Value": "rence the Flexible Time Off policy in the Grant Thornton Personnel Handbook. All rights reserved. F"
},
{
"Name": "Dummy User",
"Value": "he Expense Entry tool. Upon departure from Grant Thornton, the cardholder must cease using the corpo"
},
{
"Name": "Dummy User",
"Value": "with the firm. Once you have departed from Grant Thornton, your access to the system will be removed"
},
{
"Name": "Dummy User",
"Value": "e reward at the standard payroll tax rate. Grant Thornton will cover sales tax and shipping costs. "
},
{
"Name": "Dummy User",
"Value": " email with a pre-paid FedEx label to your Grant Thornton and lifetime email addresses ahead of your"
},
{
"Name": "Dummy User",
"Value": "of laptop(s) and associated peripherals to Grant Thornton's account. If you do not receive the email"
},
{
"Name": "Dummy User",
"Value": "e note, this process is only applicable to Grant Thornton assets and badges. For guidance on returni"
}
]
},
"SensitiveTypeSource": "OutOfBox",
"UniqueCount": 1
},
{
"ClassifierType": "MlModel",
"Confidence": 1,
"Count": 0,
"SensitiveInfoTypeId": "11631f87-7ff",
"SensitiveInfoTypeName": "HR",
"SensitiveInformationDetailedClassificationAttributes": [],
"SensitiveInformationDetectionsInfo": {
"DetectedValues": []
},
"SensitiveTypeSource": "OutOfBox",
"UniqueCount": 0
},
{
"ClassifierType": "MlModel",
"Confidence": 1,
"Count": 0,
"SensitiveInfoTypeId": "8137d8fc-fb7a-40d",
"SensitiveInfoTypeName": "Customer Complaints",
"SensitiveInformationDetailedClassificationAttributes": [],
"SensitiveInformationDetectionsInfo": {
"DetectedValues": []
},
"SensitiveTypeSource": "OutOfBox",
"UniqueCount": 0
},
{
"ClassifierType": "MlModel",
"Confidence": 1,
"Count": 0,
"SensitiveInfoTypeId": "839aecf8-c67b-4270-8aaf-378127b23b7f",
"SensitiveInfoTypeName": "Unauthorized disclosure",
"SensitiveInformationDetailedClassificationAttributes": [],
"SensitiveInformationDetectionsInfo": {
"DetectedValues": []
},
"SensitiveTypeSource": "OutOfBox",
"UniqueCount": 0
}
],
"Sha1": "b099a0d448673d5146c4295fe4100f59cc116d5d",
"Sha256": "d286766d5982fce63de8f11f9dfb9f05d8b16cc8f6c1f07e2b0b7aae820f82a2",
"SourceLocationType": 1,
"TargetDomain": "",
"TargetFilePath": "",
"TargetPrinterName": "HP7B6969.hsd1.md.comcast.net (HP Color LaserJet Pro M478f-9f)"
},
"EvidenceFile": {
"FullUrl": "",
"StorageName": ""
},
"Id": "6a54c2c7-8df2-303b-af83-b646d2ab2473",
"IncidentId": "c1e93bdc-c4cb-4238-8b39-7a440067cf81",
"ObjectId": "C:\\\\Users\\\\us21830\\\\Downloads\\\\ESignDocumentReport_EEDeparture_ESignDocumentReport_EEDeparture.pdf",
"Operation": "DlpRuleMatch",
"OrganizationId": "7d76d45a-a201-4a68-bf3a-597f0a5fa533",
"PolicyDetails": [
{
"PolicyId": "8f9d032f-571c-4652-a961-124288fddb58",
"PolicyName": "Suspicious Employee USB \\u0026 Cloud BLOCK Policy-P\\u0026C",
"Rules": [
{
"ConditionsMatched": {
"OtherConditions": [
{
"Name": "ContentFileTypeMatches",
"Value": "pdf"
}
]
},
"ManagementRuleId": "690bd15b-95fd-4211-9f8b-3f657462421d",
"RuleId": "690bd15b-95fd-4211-9f8b-3f657462421d",
"RuleMode": "Enable",
"RuleName": "Block Cloud \\u0026 USB Data Transfer"
}
]
}
],
"RecordType": 108,
"SensitiveInfoDetectionIsIncluded": true,
"UserId": "dummy.user@domain.com",
"UserKey": "UserKey",
"UserType": 0,
"Version": 1,
"Workload": "Endpoint"
}
## Field mapping reference
This section explains how the Google Security Operations parser maps Microsoft 365 log fields to Google Security Operations Unified Data Model (UDM) fields for the supported operations and workloads.
### Common fields
The following table lists the common log fields and their corresponding UDM fields.
| Common log field | UDM field | Logic |
|---|---|---|
| `AgentType` | `principal.resource.attribute.labels[agent_type]` | |
| `ForAllUsers` | `target.resource.attribute.labels[for_all_users]` | |
| `IsHiddenList` | `target.resource.attribute.labels[is_hidden_list]` | |
| `IsDocLib` | `target.resource.attribute.labels[is_doc_lib]` | |
| `CustomEvent` | `additional.fields[CustomEvent]` | |
| `HostAppId` | `additional.fields[HostAppId]` | |
| `ActorIP` | `principal.ip` | |
| `CloudInstanceName` | `principal.resource.attribute.labels[cloud_instance_name]` | |
| `AuthType` | `additional.fields[AuthType]` | |
| `TokenType` | `additional.fields[TokenType]` | |
| `CrossMailboxOperations` | `additional.fields[CrossMailboxOperations]` | |
| `MbxLoginLocalQueueADLookupInfo.Puid` | `principal.user.attribute.labels[MbxLoginLocalQueueADLookupInfo_Puid]` | |
| `MbxLoginLocalQueueADLookupInfo.OrgIdPuid` | `principal.group.product_object_id` | |
| `MbxLoginLocalQueueADLookupInfo.Smtp` | `principal.user.email_addresses` | |
| `MbxLoginLocalQueueADLookupInfo.SearchScope` | `additional.fields[MbxLoginLocalQueueADLookupInfo_SearchScope]` | |
| `MbxLoginLocalQueueADLookupInfo.ConsumerMailbox` | `principal.user.attribute.labels[MbxLoginLocalQueueADLookupInfo_ConsumerMailbox]` | |
| `AttachmentId` | `about.resource.attribute.labels[attachment_id]` | |
| `AttachmentSizeInBytes` | `about.resource.attribute.labels[attachment_size_in_bytes]` | |
| `AggregateDurationInSeconds` | `additional.fields[AggregateDurationInSeconds]` | |
| `Item.ParentMessage.Id` | `additional.fields[Item_ParentMessage_Id]` | |
| `Item.ParentMessage.Path` | `additional.fields[Item_ParentMessage_Path]` | |
| `Item.ImmutableId` | `additional.fields[Item_ImmutableId]` | |
| `Item.ComplianceLabel` | `target.resource.attribute.labels[Item_ComplianceLabel]` | |
| `Item.IsRecord` | `target.resource.attribute.labels[Item_IsRecord]` | |
| `Item.IsPriorityCleanup` | `additional.fields[Item_IsPriorityCleanup]` | |
| `Item.Sensitivity` | `target.resource.attribute.labels[Item_Sensitivity]` | |
| `Client` | `additional.fields[Client]` | |
| `UserDomain` | `principal.user.attribute.labels[UserDomain]` | |
| `EndpointMetaData.SensitiveInformation.Location` | `security_result.detection_fields[SensitiveInformation_EndpointMetaData_%{index}_Location]` | |
| `Object2Id` | `target.resource.attribute.labels[Object2Id]` | |
| `Object2Name` | `target.resource.attribute.labels[Object2Name]` | |
| `QueryFiles` | `additional.fields[QueryFiles]` | |
| `MeetingId` | `target.resource.attribute.labels[MeetingId]` | |
| `DataCenterSecurityEventType` | `additional.fields[DataCenterSecurityEventType]` | |
| `ElevationTime` | `additional.fields[ElevationTime]` | |
| `ElevationApprover` | `additional.fields[ElevationApprover]` | |
| `ElevationApprovedTime` | `additional.fields[ElevationApprovedTime]` | |
| `ElevationRequestId` | `additional.fields[ElevationRequestId]` | |
| `ElevationRole` | `additional.fields[ElevationRole]` | |
| `ElevationDuration` | `additional.fields[ElevationDuration]` | |
| `GenericInfo` | `additional.fields[GenericInfo]` | |
| `Delivery Action` | `additional.fields[Delivery_Action]` | |
| `Original Delivery location` | `additional.fields[Original_Delivery_location]` | |
| `Latest Delivery location` | `additional.fields[Latest_Delivery_location]` | |
| `Batch ID` | `security_result.detection_fields[Batch_Id]` | |
| `Campaign ID` | `additional.fields[Campaign_ID]` | |
| `Course ID` | `additional.fields[Course_ID]` | |
| `AdminSubmissionRegistered` | `additional.fields[AdminSubmissionRegistered]` | |
| `AdminSubmissionDeliveryCheck` | `additional.fields[AdminSubmissionDeliveryCheck]` | |
| `AdminSubmissionSubmitting` | `additional.fields[AdminSubmissionSubmitting]` | |
| `AdminSubmissionSubmitted` | `additional.fields[AdminSubmissionSubmitted]` | |
| `AdminSubmissionTriage` | `additional.fields[AdminSubmissionTriage]` | |
| `AdminSubmissionTimeout` | `additional.fields[AdminSubmissionTimeout]` | |
| `CustomSubmission` | `additional.fields[CustomSubmission]` | |
| `AttackSimUserSubmission` | `additomal.fields[AttackSimUserSubmission]` | |
| `SubmissionNotification` | `additional.fields[SubmissionNotification]` | |
| `Reason` | `security_result.detection_fields[Reason]` | |
| `ActivityParameters` | `additional.fields[ActivityParameters]` | |
| `AttachmentName` | `target.file.names` | |
| `JobType` | `principal.resource.attribute.labels[JobType]` | |
| `SourceUserId` | `principal.resource.attribute.labels[SourceUserId]` | |
| `ResultMessage` | `security_result.detection_fields[ResultMessage]` | |
| `IsRetry` | `additional.fields[IsRetry]` | |
| `ExportTriggeredAt` | `additional.fields[ExportTriggeredAt]` | |
| `NameOfDownloadedZipFile` | `target.file.names` | |
| `Invitation.ShareId` | `target.resource.attribute.labels[Invitation_ShareId]` | |
| `Invitation.Invitees` | `about.user.attribute.labels` | |
| `Invitation.InviteeTenantId` | `target.resource.attribute.labels[Invitation_InviteeTenantId]` | |
| `Invitation.ShareName` | `target.resource.attribute.labels[Invitation_ShareName]` | |
| `Invitation.SyncStartTime` | `additional.fields[Invitation_SyncStartTime]` | |
| `RoadmapEnabled` | `additional.fields[RoadmapEnabled]` | |
| `AssignedToMeEnabled` | `additional.fields[AssignedToMeEnabled]` | |
| `CountOfArtifactsBeingAdded` | `additional.fields[CountOfArtifactsBeingAdded]` | |
| `CountOfArtifactsBeingRemoved` | `additional.fields[CountOfArtifactsBeingRemoved]` | |
| `CreationMethodology` | `additional.fields[CreationMethodology]` | |
| `RestoreTime` | `additional.fields[RestoreTime]` | |
| `RestoreLocationType` | `target.resource.attribute.labels[RestoreLocationType]` | |
| `RestoreLocation` | `target.resource.attribute.labels[RestoreLocation]` | |
| `BackupItemID` | `src.resource.attribute.labels[BackupItemID]` | |
| `SuccessStatus` | `security_result.detection_fields[SuccessStatus]` | |
| `BackupItemType` | `target.resource.attribute.labels[BackupItemType]` | |
| `ProtectionUnitID` | `about.resource.attribute.labels[ProtectionUnitID]` | |
| `ResultStatus` | `security_result.detection_fields[ResultStatus]` | |
| `EditMethodology` | `additional.fields[EditMethodology]` | |
| `ConfigId` | `target.resource.attribute.labels[ConfigId]` | |
| `ConfigName` | `target.resource.attribute.labels[ConfigName]` | |
| `Groups` | `target.group.attribute.labels` | |
| `Priority` | `security_result.detection_fields[Priority]` | |
| `ProfileName` | `target.resource.attribute.labels[ProfileName]` | |
| `Deadline` | `additional.fields[Deadline]` | |
| `TAK` | `additional.fields[TAK]` | |
| `RollbackDevicesRollbackBuildNumber` | `target.resource.attribute.labels[RollbackDevices_RollbackBuildNumber]` | |
| `Location.City` | `principal.location.city` | |
| `Location.CountryOrRegion` | `principal.location.country_or_region` | |
| `Location.GeoCoordinates.Altitude` | `additional.fields[GeoCoordinates_Altitude]` | |
| `Location.GeoCoordinatesLatitude` | `principal.location.region_coordinates.latitude` | |
| `Location.GeoCoordinatesLongitude` | `principal.location.region_coordinates.longitude` | |
| `Location.State` | `principal.location.state` | |
| `URLPath` | `additional.fields[URLPath]` | |
| `DomainURL` | `additional.fields[DomainURL]` | |
| `ScenarioType` | `additional.fields[ScenarioType]` | |
| `PromptText` | `additional.fields[PromptText]` | |
| `AutomationId` | `additional.fields[AutomationId]` | |
| `TriggerMode` | `additional.fields[TriggerMode]` | |
| `PlaceType` | `target.resource.attribute.labels[PlaceType]` | |
| `DatabaseName` | `target.resource.attribute.labels[DatabaseName]` | |
| `SessionDurationInSecs` | `network.session_duration.seconds` | |
| `SessionStartTime` | `additional.fields[SessionStartTime]` | |
| `SessionEndTime` | `additional.fields[SessionEndTime]` | |
| `KernalId` | `principal.process.product_specific_process_id` | |
| `Interface` | `principal.resource.attribute.labels[Interface]` | |
| `EventTime` | `additional.fields[EventTime]` | |
| `Job Type` | `target.resource.attribute.labels[Job_Type]` | |
| `Job ID` | `target.resource.attribute.labels[Job_ID]` | |
| `Job Name` | `target.resource.attribute.labels[Job_Name]` | |
| `Compute` | `target.resource.attribute.labels[Compute]` | |
| `Schedule` | `additional.fields[Schedule]` | |
| `Run ID` | `additional.fields[Run_ID]` | |
| `JobRunStatus` | `additional.fields[JobRunStatus]` | |
| `Logs` | `additional.fields[Logs]` | |
| `JobExecutionDurationInSecs` | `additional.fields[JobExecutionDurationInSecs]` | |
| `JobTotalDurationInSecs` | `additional.fields[JobTotalDurationInSecs]` | |
| `JobStartTime` | `additional.fields[JobStartTime]` | |
| `JobEndTime` | `additional.fields[JobEndTime]` | |
| `ResultTableCount` | `additional.fields[ResultTableCount]` | |
| `QueryResponse` | `additional.fields[QueryResponse]` | |
| `ComponentFault` | `security_result.detection_fields[ComponentFault]` | |
| `ExecutionDuration` | `additional.fields[ExecutionDuration]` | |
| `TotalCPU` | `additional.fields[TotalCPU]` | |
| `MemoryPeak` | `additional.fields[MemoryPeak]` | |
| `BillingAzureSubscriptionId` | `principal.resource.attribute.labels[BillingAzureSubscriptionId]` | |
| `BillingAzureResourceGroupName` | `principal.resource.attribute.labels[BillingAzureResourceGroupName]` | |
| `TenantId` | `metadata.product_deployment_id` | |
| `ProvisioningStatus` | `additional.fields[ProvisioningStatus]` | |
| `DataOnboardingAtSetup` | `additional.fields[DataOnboardingAtSetup]` | |
| `DataOnboardingStatus` | `additional.fields[DataOnboardingStatus]` | |
| `EventOccurenceTime` | `additional.fields[EventOccurenceTime]` | |
| `ToolID` | `principal.resource.attribute.labels[ToolID]` | |
| `ToolName` | `principal.resource.attribute.labels[ToolName]` | |
| `InputParameters` | `additional.fields[InputParameters]` | |
| `FailureReason` | `security_result.detection_fields[FailureReason]` | |
| `DataScanned` | `additional.fields[DataScanned]` | |
| `TotalCpuHours` | `additional.fields[TotalCpuHours]` | |
| `TotalSCUHours` | `additional.fields[TotalSCUHours]` | |
| `GraphName` | `target.resource.attribute.labels[GraphName]` | |
| `OperationInput` | `additional.fields[OperationInput]` | |
| `GraphQuery Stats` | `additional.fields[GraphQuery_Stats]` | |
| `GraphQuery Status` | `additional.fields[GraphQuery_Status]` | |
| `ClassificationMode` | `additional.fields[ClassificationMode]` | |
| `ClassificationPosture` | `additional.fields[ClassificationPosture]` | |
| `ClassificationResult` | `additional.fields[ClassificationResult]` | |
| `WaveDelay` | `additional.fields[WaveDelay]` | |
| `DocumentMetaData.itemCreationTime` | `additional.fields[DocumentMetaData_itemCreationTime]` | |
| `DocumentMetaData.SiteCollectionGuid` | `target.resource.attribute.labels[DocumentMetaData_SiteCollectionGuid]` | |
| `DocumentMetaData.SiteCollectionUrl` | `target.resource.attribute.labels[DocumentMetaData_SiteCollectionUrl]` | |
| `DocumentMetaData.FileName` | `target.file.names` | |
| `DocumentMetaData.FileOwner` | `about.user.attribute.labels[DocumentMetaData_FileOwner]` | |
| `DocumentMetaData.FileOwnerEmail` | `about.user.email_addresses` | |
| `DocumentMetaData.FilePathUrl` | `additional.fields[DocumentMetaData_FilePathUrl]` | |
| `DocumentMetaData.DocumentLastModifier` | `target.resource.attribute.labels[DocumentMetaData_DocumentLastModifier]` | |
| `DocumentMetaData.UniqueId` | `target.resource.attribute.labels[DocumentMetaData_UniqueId]` | |
| `DocumentMetaData.LastModifiedTime` | `target.file.last_modification_time` | |
| `DestFolder.MemberSid` | `additional.fields[DestFolder_MemberSid]` | |
| `Folder.MemberSid` | `additional.fields[Folder_MemberSid]` | |
| `Item.ParentFolder.Name` | `additional.fields[Item_ParentFolder_Name]` | |
| `Item.ParentFolder.MemberSid` | `additional.fields[Item_ParentFolder_MemberSid]` | |
| `DestFolder.MemberRights` | `additional.fields[DestFolder_MemberRights]` | |
| `Folder.MemberRights` | `additional.fields[Folder_MemberRights]` | |
| `DestFolder.MemberUpn` | `additional.fields[DestFolder_MemberUpn]` | |
| `Folder.MemberUpn` | `additional.fields[Folder_MemberUpn]` | |
| `DestFolder.Name` | `additional.fields[DestFolder_Name]` | |
| `Folder.Name` | `additional.fields[Folder_Name]` | |
| `UserAssignments` | `additional.fields[UserAssignments]` | Iterate for each key, value pair of log field `UserAssignments`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `FormTypes` | `target.resource.attribute.labels[FormTypes]` | If the `FormTypes` log field value is equal to `0` then, the `target.resource.attribute.labels[FormTypes]` UDM field is set to `Form`. Else, if `FormTypes` log field value is equal to `1` then, the `target.resource.attribute.labels[FormTypes]` UDM field is set to `Quiz`. Else, if `FormTypes` log field value is equal to `2` then, the `target.resource.attribute.labels[FormTypes]` UDM field is set to `Survey`. |
| `APIsCalled` | `additional.fields[APIsCalled]` | Iterate for each key, value pair of log field `APIsCalled`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `SubscriptionsEnabled` | `target.resource.attribute.labels` | Iterate for each element `subs_info` with index `index` in the `SubscriptionsEnabled` log field array, then The `target.resource.attribute.labels.key` UDM field is set to `SubscriptionsEnabled_%{index}` and the `subs_info` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Tables` | `target.resource.attribute.labels` | Iterate for each element `table_name` with index `index` in the `Tables` log field array, then The `target.resource.attribute.labels.key` UDM field is set to `Tables_%{index}` and the `table_name` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `TotalRows` | `additional.fields[TotalRows_%{index}]` | Iterate for each element `num_rows` with index `index` in the `TotalRows` log field array, then The `additional.fields.key` UDM field is set to `TotalRows_%{index}` and the `num_rows` log field is mapped to the `additional.fields.value` UDM field. |
| `DatabaseName` | `target.resource.attribute.labels` | Iterate for each element `db_name` with index `index` in the `DatabaseName` log field array, then The `target.resource.attribute.labels.key` UDM field is set to `DatabaseName_%{index}` and the `db_name` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `TablesWrite` | `target.resource.attribute.labels` | Iterate for each element `tw_info` with index `index` in the `TablesWrite` log field array, then The `target.resource.attribute.labels.key` UDM field is set to `TablesWrite_%{index}` and the `tw_info` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `TablesRead` | `src.resource.attribute.labels` | Iterate for each element `tr_info` with index `index` in the `TablesRead` log field array, then The `src.resource.attribute.labels.key` UDM field is set to `TablesRead_%{index}` and the `tr_info` log field is mapped to the `src.resource.attribute.labels.value` UDM field. |
| `DatabasesWrite` | `target.resource.attribute.labels` | Iterate for each element `dw_info` with index `index` in the `DatabasesWrite` log field array, then The `target.resource.attribute.labels.key` UDM field is set to `DatabasesWrite_%{index}` and the `dw_info` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `DatabasesRead` | `src.resource.attribute.labels` | Iterate for each element `dr_info` with index `index` in the `DatabasesRead` log field array, then The `src.resource.attribute.labels.key` UDM field is set to `DatabasesRead_%{index}` and the `dr_info` log field is mapped to the `src.resource.attribute.labels.value` UDM field. |
| `ProfileState` | `target.resource.attribute.labels[ProfileState]` | If the `ProfileState` log field value is equal to `1` then, the `target.resource.attribute.labels[ProfileState]` UDM field is set to `Enabled`. Else, if `ProfileState` log field value is equal to `2` then, the `target.resource.attribute.labels[ProfileState]` UDM field is set to `Disabled`. Else, if `ProfileState` log field value is equal to `3` then, the `target.resource.attribute.labels[ProfileState]` UDM field is set to `Paused`. |
| `UpdateValidationState` | `additional.fields[UpdateValidationState]` | If the `UpdateValidationState` log field value is equal to `1` then, the `additional.fields[UpdateValidationState]` UDM field is set to `Enabled`. Else, if `UpdateValidationState` log field value is equal to `2` then, the `additional.fields[UpdateValidationState]` UDM field is set to `Disabled`. |
| `Messages.Id` | `additional.fields[Messages_%{index}_Id]` | Iterate for each element `message` in the `Messages` log field array, then the `additional.fields.key` UDM field is set to `Messages_%{index}_Id` and the `message.Id` log field is mapped to the `additional.fields.value` UDM field. |
| `Messages.Path` | `additional.fields[Messages_%{index}_Path]` | Iterate for each element `message` in the `Messages` log field array, then the `additional.fields.key` UDM field is set to `Messages_%{index}_Path` and the `message.Path` log field is mapped to the `additional.fields.value` UDM field. |
| `Messages.MessageItems.SizeInBytes` | `about.file.size` | Iterate for each element `message` in the `Messages` log field array, then Iterate for each element `item` in the `Messages.MessageItems` log field array, then the `about.file.size` UDM field is set to `item.SizeInBytes` |
| `Messages.MessageItems.Id` | `about.resource.product_object_id` | Iterate for each element `message` in the `Messages` log field array, then Iterate for each element `item` in the `Messages.MessageItems` log field array, then the `about.resource.product_object_id` UDM field is set to `item.Id` |
| `LoginStatus` | `security_result.action` | If the `LoginStatus` log field value contains `1` or `3` then, the `security_result.action` UDM field is set to `ALLOW`. Else, if `LoginStatus` log field value contains `2` or `5` then, the `security_result.action` UDM field is set to `BLOCK`. Else `security_result.action` UDM field is set to `UNKNOWN_ACTION`. |
| `Folders.FolderItems.ImmutableId` | `additional.fields[Folders_%{index}_FolderItems_%{item_index}_ImmutableId]` `about.resource.attribute.labels[ImmutableId]` | If the `Workload` log field value is equal to `Exchange` and the `Operation` log field value is equal to `MailItemsAccessed`, then iterate for each element `folder` in the `Folders` log field array and each element `item` in the `Folders.FolderItems` log field array, where the `about.resource.attribute.labels.key` UDM field is set to `ImmutableId` and the `item.ImmutableId` log field is mapped to the `about.resource.attribute.labels.value` UDM field. Otherwise, if `Operation` is not equal to `MailItemsAccessed`, then iterate for each element `folder` in the `Folders` log field array and each element `item` in the `Folders.FolderItems` log field array, where the `additional.fields.key` UDM field is set to `Folders_%{index}_FolderItems_%{item_index}_ImmutableId` and the `item.ImmutableId` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.FolderItems.SizeInBytes` | `additional.fields[Folders_%{index}_FolderItems_%{item_index}_SizeInBytes]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then Iterate for each element `item` in the `Folders.FolderItems` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_FolderItems_%{item_index}_SizeInBytes` and the `item.SizeInBytes` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.FolderItems.Teams` | `additional.fields[Folders_%{index}_FolderItems_%{item_index}_Teams]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then Iterate for each element `item` in the `Folders.FolderItems` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_FolderItems_%{item_index}_Teams` and the `item.Teams` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.FolderItems.InternetMessageId` | `additional.fields[Folders_%{index}_FolderItems_%{item_index}_InternetMessageId]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then Iterate for each element `item` in the `Folders.FolderItems` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_FolderItems_%{item_index}_InternetMessageId` and the `item.InternetMessageId` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.FolderItems.ClientRequestId` | `additional.fields[Folders_%{index}_FolderItems_%{item_index}_ClientRequestId]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then Iterate for each element `item` in the `Folders.FolderItems` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_FolderItems_%{item_index}_ClientRequestId` and the `item.ClientRequestId` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.FolderItems.Sensitivity` | `target.resource.attribute.labels[Folders_%{index}_FolderItems_%{item_index}_Sensitivity]` `about.resource.attribute.labels[Sensitivity]` | If the `Workload` log field value is equal to `Exchange` and the `Operation` log field value is equal to `MailItemsAccessed`, then iterate for each element `folder` in the `Folders` log field array and each element `item` in the `Folders.FolderItems` log field array, where the `about.resource.attribute.labels.key` UDM field is set to `Sensitivity` and the `item.Sensitivity` log field is mapped to the `about.resource.attribute.labels.value` UDM field. Otherwise, if `Operation` is not equal to `MailItemsAccessed`, then iterate for each element `folder` in the `Folders` log field array and each element `item` in the `Folders.FolderItems` log field array, where the `target.resource.attribute.labels.key` UDM field is set to `Folders_%{index}_FolderItems_%{item_index}_Sensitivity` and the `item.Sensitivity` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Folders.FolderItems.Id` | `target.resource.attribute.labels[Folders_%{index}_FolderItems_%{item_index}_Id]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then Iterate for each element `item` in the `Folders.FolderItems` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `Folders_%{index}_FolderItems_%{item_index}_Id` and the `item.Id` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Folders.FolderItems.CreationTime` | `target.resource.attribute.creation_time` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then Iterate for each element `item` in the `Folders.FolderItems` log field array, then the `item.CreationTime` log field is mapped to the `target.resource.attribute.creation_time` UDM field. |
| `Folders.FolderItems.Subject` | `network.email.subject` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then Iterate for each element `item` in the `Folders.FolderItems` log field array, then the `item.Subject` log field is mapped to the `network.email.subject` UDM field. |
| `Folders.Path` | `additional.fields[Folders_%{index}_Path]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_Path` and the `folder.Path` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.MemberSid` | `additional.fields[Folders_%{index}_Path]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_Path` and the `folder.Path` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.MemberRights` | `additional.fields[Folders_%{index}_MemberRights]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_MemberRights` and the `folder.MemberRights` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.MemberUpn` | `additional.fields[Folders_%{index}_MemberUpn]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_MemberUpn` and the `folder.MemberUpn` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.Name` | `additional.fields[Folders_%{index}_Name]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_Name` and the `folder.Name` log field is mapped to the `additional.fields.value` UDM field. |
| `Folders.Id` | `additional.fields[Folders_%{index}_Id]` | If Operation is not equal to `MailItemsAccessed` then Iterate for each element `folder` in the `Folders` log field array, then the `additional.fields.key` UDM field is set to `Folders_%{index}_Id` and the `folder.Id` log field is mapped to the `additional.fields.value` UDM field. |
| `EndpointMetaData.SensitiveInformation.Confidence` | `security_result.confidence` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then If the `s_info.Confidence` log field value is greater than `80` then, the `security_result.confidence` UDM field is set to `HIGH_CONFIDENCE`. Else, if `s_info.Confidence` log field value is greater than `50` then, the `security_result.confidence` UDM field is set to `MEDIUM_CONFIDENCE`. Else, `security_result.confidence` UDM field is set to `LOW_CONFIDENCE`. |
| `EndpointMetaData.SensitiveInformation.Count` | `security_result.detection_fields[EndpointMetaData_SensitiveInformation_%{index}_Count]` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then the `security_result.detection_fields.key` UDM field is set to `EndpointMetaData_SensitiveInformation_%{index}_Count` and the `s_info.Count` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `EndpointMetaData.SensitiveInformation.Location` | `security_result.detection_fields[EndpointMetaData_SensitiveInformation_%{index}_Location]` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then the `security_result.detection_fields.key` UDM field is set to `EndpointMetaData_SensitiveInformation_%{index}_Location` and the `s_info.Location` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `EndpointMetaData.SensitiveInformation.UniqueCount` | `security_result.detection_fields[EndpointMetaData_SensitiveInformation_%{index}_UniqueCount]` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then the `security_result.detection_fields.key` UDM field is set to `EndpointMetaData_SensitiveInformation_%{index}_UniqueCount` and the `s_info.UniqueCount` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `EndpointMetaData.SensitiveInformation.SensitiveType` | `security_result.rule_id` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then the `s_info.SensitiveType` log field is mapped to the `security_result.rule_id` UDM field. |
| `EndpointMetaData.SensitiveInformation.SensitiveInformationTypeName` | `security_result.threat_name` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then the `s_info.SensitiveInformationTypeName` log field is mapped to the `security_result.threat_name` UDM field. |
| `EndpointMetaData.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated` | `additional.fields[EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetections_ResultsTruncated]` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then the `additional.fields.key` UDM field is set to `EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetections_ResultsTruncated` and the `s_info.SensitiveInformationDetections.ResultsTruncated` log field is mapped to the `additional.fields.value` UDM field. |
| `EndpointMetaData.SensitiveInformation.SensitiveInformationDetections.DetectedValues` | `security_result.detection_fields[EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetections_DetectedValues_%{dv.Name}]` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then Iterate for each element `dv` in the `s_info.SensitiveInformationDetections.DetectedValues` log field array, then the `security_result.detection_fields.key` UDM field is set to `EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetections_DetectedValues_%{dv.Name}` and the `dv.Value` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `EndpointMetaData.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.Confidence` | `security_result.detection_fields[EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Confidence]` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then Iterate for each element `att` in the `s_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Confidence` and the `att.Confidence` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `EndpointMetaData.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.Count` | `security_result.detection_fields[EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Count]` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then Iterate for each element `att` in the `s_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Count` and the `att.Count` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `EndpointMetaData.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch` | `security_result.detection_fields[EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_IsMatch]` | Iterate for each element `s_info` in the `EndpointMetaData.SensitiveInformation` log field array, then Iterate for each element `att` in the `s_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `EndpointMetaData_SensitiveInformation_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_IsMatch` and the `att.IsMatch` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `ClassificationInfo.Confidence` | `security_result.confidence` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then If the `c_info.Confidence` log field value is greater than `80` then, the `security_result.confidence` UDM field is set to `HIGH_CONFIDENCE`. Else, if `c_info.Confidence` log field value is greater than `50` then, the `security_result.confidence` UDM field is set to `MEDIUM_CONFIDENCE`. Else, `security_result.confidence` UDM field is set to `LOW_CONFIDENCE`. |
| `ClassificationInfo.Count` | `security_result.detection_fields[ClassificationInfo_%{index}_Count]` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then the `security_result.detection_fields.key` UDM field is set to `ClassificationInfo_%{index}_Count` and the `c_info.Count` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `ClassificationInfo.Location` | `security_result.detection_fields[ClassificationInfo_%{index}_Location]` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then the `security_result.detection_fields.key` UDM field is set to `ClassificationInfo_%{index}_Location` and the `c_info.Location` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `ClassificationInfo.UniqueCount` | `security_result.detection_fields[ClassificationInfo_%{index}_UniqueCount]` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then the `security_result.detection_fields.key` UDM field is set to `ClassificationInfo_%{index}_UniqueCount` and the `c_info.UniqueCount` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `ClassificationInfo.SensitiveType` | `security_result.rule_id` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then the `c_info.SensitiveType` log field is mapped to the `security_result.rule_id` UDM field. |
| `ClassificationInfo.SensitiveInformationTypeName` | `security_result.threat_name` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then the `c_info.SensitiveInformationTypeName` log field is mapped to the `security_result.threat_name` UDM field. |
| `ClassificationInfo.SensitiveInformationDetections.ResultsTruncated` | `additional.fields[ClassificationInfo_%{index}_SensitiveInformationDetections_ResultsTruncated]` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then the `additional.fields.key` UDM field is set to `ClassificationInfo_%{index}_SensitiveInformationDetections_ResultsTruncated` and the `c_info.SensitiveInformationDetections.ResultsTruncated` log field is mapped to the `additional.fields.value` UDM field. |
| `ClassificationInfo.SensitiveInformationDetections.DetectedValues` | `security_result.detection_fields[ClassificationInfo_%{index}_SensitiveInformationDetections_DetectedValues_%{dv.Name}]` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then Iterate for each element `dv` in the `c_info.SensitiveInformationDetections.DetectedValues` log field array, then the `security_result.detection_fields.key` UDM field is set to `ClassificationInfo_%{index}_SensitiveInformationDetections_DetectedValues_%{dv.Name}` and the `dv.Value` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `ClassificationInfo.SensitiveInformationDetailedClassificationAttributes.Confidence` | `security_result.detection_fields[ClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Confidence]` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then Iterate for each element `att` in the `c_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `ClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Confidence` and the `att.Confidence` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `ClassificationInfo.SensitiveInformationDetailedClassificationAttributes.Count` | `security_result.detection_fields[ClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Count]` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then Iterate for each element `att` in the `c_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `ClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Count` and the `att.Count` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `ClassificationInfo.SensitiveInformationDetailedClassificationAttributes.IsMatch` | `security_result.detection_fields[ClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_IsMatch]` | Iterate for each element `c_info` in the `ClassificationInfo` log field array, then Iterate for each element `att` in the `c_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `ClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_IsMatch` and the `att.IsMatch` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PreviousClassificationInfo.Confidence` | `security_result.confidence` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then If the `c_info.Confidence` log field value is greater than `80` then, the `security_result.confidence` UDM field is set to `HIGH_CONFIDENCE`. Else, if `c_info.Confidence` log field value is greater than `50` then, the `security_result.confidence` UDM field is set to `MEDIUM_CONFIDENCE`. Else, `security_result.confidence` UDM field is set to `LOW_CONFIDENCE`. |
| `PreviousClassificationInfo.Count` | `security_result.detection_fields[PreviousClassificationInfo_%{index}_Count]` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then the `security_result.detection_fields.key` UDM field is set to `PreviousClassificationInfo_%{index}_Count` and the `c_info.Count` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PreviousClassificationInfo.Location` | `security_result.detection_fields[PreviousClassificationInfo_%{index}_Location]` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then the `security_result.detection_fields.key` UDM field is set to `PreviousClassificationInfo_%{index}_Location` and the `c_info.Location` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PreviousClassificationInfo.UniqueCount` | `security_result.detection_fields[PreviousClassificationInfo_%{index}_UniqueCount]` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then the `security_result.detection_fields.key` UDM field is set to `PreviousClassificationInfo_%{index}_UniqueCount` and the `c_info.UniqueCount` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PreviousClassificationInfo.SensitiveType` | `security_result.rule_id` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then the `c_info.SensitiveType` log field is mapped to the `security_result.rule_id` UDM field. |
| `PreviousClassificationInfo.SensitiveInformationTypeName` | `security_result.threat_name` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then the `c_info.SensitiveInformationTypeName` log field is mapped to the `security_result.threat_name` UDM field. |
| `PreviousClassificationInfo.SensitiveInformationDetections.ResultsTruncated` | `additional.fields[PreviousClassificationInfo_%{index}_SensitiveInformationDetections_ResultsTruncated]` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then the `additional.fields.key` UDM field is set to `PreviousClassificationInfo_%{index}_SensitiveInformationDetections_ResultsTruncated` and the `c_info.SensitiveInformationDetections.ResultsTruncated` log field is mapped to the `additional.fields.value` UDM field. |
| `PreviousClassificationInfo.SensitiveInformationDetections.DetectedValues` | `security_result.detection_fields[PreviousClassificationInfo_%{index}_SensitiveInformationDetections_DetectedValues_%{dv.Name}]` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then Iterate for each element `dv` in the `c_info.SensitiveInformationDetections.DetectedValues` log field array, then the `security_result.detection_fields.key` UDM field is set to `PreviousClassificationInfo_%{index}_SensitiveInformationDetections_DetectedValues_%{dv.Name}` and the `dv.Value` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PreviousClassificationInfo.SensitiveInformationDetailedClassificationAttributes.Confidence` | `security_result.detection_fields[PreviousClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Confidence]` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then Iterate for each element `att` in the `c_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `PreviousClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Confidence` and the `att.Confidence` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PreviousClassificationInfo.SensitiveInformationDetailedClassificationAttributes.Count` | `security_result.detection_fields[PreviousClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Count]` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then Iterate for each element `att` in the `c_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `PreviousClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_Count` and the `att.Count` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PreviousClassificationInfo.SensitiveInformationDetailedClassificationAttributes.IsMatch` | `security_result.detection_fields[PreviousClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_IsMatch]` | Iterate for each element `c_info` in the `PreviousClassificationInfo` log field array, then Iterate for each element `att` in the `c_info.SensitiveInformationDetailedClassificationAttributes` log field array, then the `security_result.detection_fields.key` UDM field is set to `PreviousClassificationInfo_%{index}_SensitiveInformationDetailedClassificationAttributes_%{att_index}_IsMatch` and the `att.IsMatch` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `Messages.AADGroupId` | `target.resource.attribute.labels[Messages_%{index}_AADGroupId]` | Iterate for each element `message` in the `Messages` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `Messages_%{index}_AADGroupId` and the `message.AADGroupId` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Messages.ChannelGuid` | `target.resource.attribute.labels[Messages_%{index}_ChannelGuid]` | Iterate for each element `message` in the `Messages` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `Messages_%{index}_ChannelGuid` and the `message.ChannelGuid` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Messages.ChannelName` | `target.resource.attribute.labels[Messages_%{index}_ChannelName]` | Iterate for each element `message` in the `Messages` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `Messages_%{index}_ChannelName` and the `message.ChannelName` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Messages.ChannelType` | `target.resource.attribute.labels[Messages_%{index}_ChannelType]` | Iterate for each element `message` in the `Messages` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `Messages_%{index}_ChannelType` and the `message.ChannelType` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Messages.ChatName` | `target.resource.attribute.labels[Messages_%{index}_ChatName]` | Iterate for each element `message` in the `Messages` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `Messages_%{index}_ChatName` and the `message.ChatName` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Messages.ChatThreadId` | `target.resource.attribute.labels[Messages_%{index}_ChatThreadId]` | Iterate for each element `message` in the `Messages` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `Messages_%{index}_ChatThreadId` and the `message.ChatThreadId` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Messages.Version` | `target.resource.attribute.labels[Messages_%{index}_Version]` | Iterate for each element `message` in the `Messages` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `Messages_%{index}_Version` and the `message.Version` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Messages.TeamGuid` | `target.group.attribute.labels[Messages_%{index}_TeamGuid]` | Iterate for each element `message` in the `Messages` log field array, then the `target.group.attribute.labels.key` UDM field is set to `Messages_%{index}_TeamGuid` and the `message.TeamGuid` log field is mapped to the `target.group.attribute.labels.value` UDM field. |
| `Messages.TeamName` | `target.group.attribute.labels[Messages_%{index}_TeamName]` | Iterate for each element `message` in the `Messages` log field array, then the `target.group.attribute.labels.key` UDM field is set to `Messages_%{index}_TeamName` and the `message.TeamName` log field is mapped to the `target.group.attribute.labels.value` UDM field. |
| `Messages.ParentMessageId` | `additional.fields[Messages_%{index}_ParentMessageId]` | Iterate for each element `message` in the `Messages` log field array, then the `additional.fields.key` UDM field is set to `Messages_%{index}_ParentMessageId` and the `message.ParentMessageId` log field is mapped to the `additional.fields.value` UDM field. |
| `Messages.SizeInBytes` | `additional.fields[Messages_%{index}_SizeInBytes]` | Iterate for each element `message` in the `Messages` log field array, then the `additional.fields.key` UDM field is set to `Messages_%{index}_SizeInBytes` and the `message.SizeInBytes` log field is mapped to the `additional.fields.value` UDM field. |
| `Policies.PolicyId` | `additional.fields[Policies_%{index}_PolicyId]` | Iterate for each element `policy` in the `Policies` log field array, then the `additional.fields.key` UDM field is set to `Policies_%{index}_PolicyId` and the `policy.PolicyId` log field is mapped to the `additional.fields.value` UDM field. |
| `Policies.PolicyName` | `additional.fields[Policies_%{index}_PolicyName]` | Iterate for each element `policy` in the `Policies` log field array, then the `additional.fields.key` UDM field is set to `Policies_%{index}_PolicyName` and the `policy.PolicyName` log field is mapped to the `additional.fields.value` UDM field. |
| `Policies.Value` | `additional.fields[Policies_%{index}_Value]` | Iterate for each element `policy` in the `Policies` log field array, then the `additional.fields.key` UDM field is set to `Policies_%{index}_Value` and the `policy.Value` log field is mapped to the `additional.fields.value` UDM field. |
| `Policies.SettingId` | `additional.fields[Policies_%{index}_Settings_%{index1}_SettingId]` | Iterate for each element `policy` in the `Policies` log field array, then Iterate for each element `setting` in the `policy.Settings` log field array, then the `additional.fields.key` UDM field is set to `Policies_%{index}_Settings_%{index1}_SettingId` and the `settings.SettingId` log field is mapped to the `additional.fields.value` UDM field. |
| `Policies.SettingName` | `additional.fields[Policies_%{index}_Settings_%{index1}_SettingName]` | Iterate for each element `policy` in the `Policies` log field array, then Iterate for each element `setting` in the `policy.Settings` log field array, then the `additional.fields.key` UDM field is set to `Policies_%{index}_Settings_%{index1}_SettingName` and the `settings.SettingName` log field is mapped to the `additional.fields.value` UDM field. |
| `Priorities.ConfigId` | `additional.fields[Priorities_%{index}_ConfigId]` | Iterate for each element `priority` in the `Priorities` log field array, then the `additional.fields.key` UDM field is set to `Priorities_%{index}_ConfigId` and the `priority.ConfigId` log field is mapped to the `additional.fields.value` UDM field. |
| `Priorities.ConfigName` | `additional.fields[Priorities_%{index}_ConfigName]` | Iterate for each element `priority` in the `Priorities` log field array, then the `additional.fields.key` UDM field is set to `Priorities_%{index}_ConfigName` and the `priority.ConfigName` log field is mapped to the `additional.fields.value` UDM field. |
| `Priorities.Value` | `additional.fields[Priorities_%{index}_Value]` | Iterate for each element `priority` in the `Priorities` log field array, then the `additional.fields.key` UDM field is set to `Priorities_%{index}_Value` and the `priority.Value` log field is mapped to the `additional.fields.value` UDM field. |
| `Waves.Name` | `additional.fields[Waves_%{index}_Name]` | Iterate for each element `wave` in the `Waves` log field array, then the `additional.fields.key` UDM field is set to `Waves_%{index}_Name` and the `wave.Name` log field is mapped to the `additional.fields.value` UDM field. |
| `Waves.Type` | `additional.fields[Waves_%{index}_Type]` | Iterate for each element `wave` in the `Waves` log field array, then the `additional.fields.key` UDM field is set to `Waves_%{index}_Type` If the `wave.Type` log field value is equal to `1` then, the `additional.fields.value` UDM field is set to `Groups`. Else, if `wave.Type` log field value is equal to `2` then, the `additional.fields.value` UDM field is set to `RemainingDevices` |
| `Waves.Groups` | `additional.fields[Waves_%{index}_Groups_%{wave_group.Name}]` | Iterate for each element `wave` in the `Waves` log field array, then Iterate for each element `wave_group` in the `wave.Groups` log field array, then the `additional.fields.key` UDM field is set to `Waves_%{index}_Groups_%{wave_group.Name}`and the `wave_group.Value` log field is mapped to the `additional.fields.value` UDM field. |
| `ProfileExclusionWindows.Name` | `additional.fields[ProfileExclusionWindows_%{index}_Name]` | Iterate for each element `window` in the `ProfileExclusionWindows` log field array, then the `additional.fields.key` UDM field is set to `ProfileExclusionWindows_%{index}_Name`and the `window.Name` log field is mapped to the `additional.fields.value` UDM field. |
| `ProfileExclusionWindows.StartDate` | `additional.fields[ProfileExclusionWindows_%{index}_StartDate]` | Iterate for each element `window` in the `ProfileExclusionWindows` log field array, then the `additional.fields.key` UDM field is set to `ProfileExclusionWindows_%{index}_StartDate`and the `window.StartDate` log field is mapped to the `additional.fields.value` UDM field. |
| `ProfileExclusionWindows.EndDate` | `additional.fields[ProfileExclusionWindows_%{index}_EndDate]` | Iterate for each element `window` in the `ProfileExclusionWindows` log field array, then the `additional.fields.key` UDM field is set to `ProfileExclusionWindows_%{index}_EndDate`and the `window.EndDate` log field is mapped to the `additional.fields.value` UDM field. |
| `ProfileExclusionWindows.Groups` | `additional.fields[ProfileExclusionWindows_%{index}_Groups_%{wave_group.Name}]` | Iterate for each element `window` in the `ProfileExclusionWindows` log field array, then Iterate for each element `group` in the `window.Groups` log field array, then the `additional.fields.key` UDM field is set to `ProfileExclusionWindows_%{index}_Groups_%{group.Name}`and the `group.Value` log field is mapped to the `additional.fields.value` UDM field. |
| `Attachments.FileName` | `target.group.attribute.labels[Attachments_%{att_index}_FileName]` | Iterate for each element `attachment` in the `Attachments` log field array, then the `target.group.attribute.labels.key` UDM field is set to `Attachments_%{att_index}_FileName` and the `attachment.FileName` log field is mapped to the `target.group.attribute.labels.value` UDM field. |
| `Attachments.Details` | `target.group.attribute.labels[Attachments_%{att_index}_Details]` | Iterate for each element `attachment` in the `Attachments` log field array, then the `target.group.attribute.labels.key` UDM field is set to `Attachments_%{att_index}_Details` and the `attachment.Details` log field is mapped to the `target.group.attribute.labels.value` UDM field. |
| `Invitation.SyncFrequency` | `additional.fields[SyncFrequency]` | `additional.fields.key` UDM field is set to `SyncFrequency` If the `Invitation.SyncFrequency` log field value is equal to `0` then, the `additional.fields.value` UDM field is set to `Hourly`. Else, if `Invitation.SyncFrequency` log field value is equal to `1` then, the `additional.fields.value` UDM field is set to `Daily` |
| `ConfigScope` | `additional.fields[ConfigScope]` | `additional.fields.key` UDM field is set to `ConfigScope` If the `ConfigScope` log field value is equal to `1` then, the `additional.fields.value` UDM field is set to `Tenant`. Else, if `ConfigScope` log field value is equal to `2` then, the `additional.fields.value` UDM field is set to `Anonymous` Else, if `ConfigScope` log field value is equal to `3` then, the `additional.fields.value` UDM field is set to `User` |
| `ExclusionList` | `additional.fields[ExclusionList_%{el_item.Name}]` | Iterate for each element `el_item` in the `ExclusionList` log field array, then the `additional.fields.key` UDM field is set to `ExclusionList_%{el_item.Name}`and the `el_item.Value` log field is mapped to the `additional.fields.value` UDM field. |
| `RollbackDevices.RollbackType` | `target.resource.attribute.labels[RollbackDevices_RollbackType]` | `target.resource.attribute.labels.key` UDM field is set to `RollbackDevice_RollbackType` If the `RollbackDevices.RollbackType` log field value is equal to `1` then, the `target.resource.attribute.labels.value` UDM field is set to `SpecificDevices`. Else, if `RollbackDevices.RollbackType` log field value is equal to `2` then, the `target.resource.attribute.labels.value` UDM field is set to `AllDevices` |
| `RollbackDevices.Devices` | `target.resource.attribute.labels[RollbackDevices_Device_%{dev_index}]` | Iterate for each element `device` in the `RollbackDevices.Devices` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `RollbackDevices_Device_%{dev_index}` and the `device` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `ChannelChangeDevices.ChannelChange` | `target.resource.attribute.labels[ChannelChangeDevices_ChannelChange]` | `target.resource.attribute.labels.key` UDM field is set to `ChannelChangeDevices_ChannelChange` If the `ChannelChangeDevices.ChannelChange` log field value is equal to `1` then, the `target.resource.attribute.labels.value` UDM field is set to `MonthlyEnterpriseChannel`. Else, if `ChannelChangeDevices.ChannelChange` log field value is equal to `2` then, the `target.resource.attribute.labels.value` UDM field is set to `CurrentChannel` |
| `ChannelChangeDevices.Devices` | `target.resource.attribute.labels[ChannelChangeDevices_Device_%{cc_dev_index}]` | Iterate for each element `cc_device` in the `ChannelChangeDevices.Devices` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `ChannelChangeDevices_Device_%{cc_dev_index}` and the `cc_device` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `ChannelChangeDevices.Groups` | `target.resource.attribute.labels[ChannelChangeDevices_Group_%{cc_group_index.Name}]` | Iterate for each element `cc_group` in the `ChannelChangeDevices.Groups` log field array, then the `target.resource.attribute.labels.key` UDM field is set to `ChannelChangeDevices_Device_%{cc_group_index.Name}` and the `cc_group.Value` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `AttachmentData.MalwareFamily` | `security_result.detection_fields[AttachmentData_%{in}_MalwareFamily]` | Iterate for each element `file` in the `AttachmentData` log field array, then the `security_result.detection_fields.key` UDM field is set to `AttachmentData_%{in}_MalwareFamily` and the `file.MalwareFamily` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `OperationStatus` | `security_result.action` | If the `OperationStatus` log field value is equal to `0` then, the `security_result.action` UDM field is set to `ALLOW`. Else, if `OperationStatus` log field value is equal to `1` then, the `security_result.action` UDM field is set to `BLOCK`. Else `security_result.action` UDM field is set to `UNKNOWN_ACTION`. |
| `FailureType` | `security_result.detection_fields[FailureType]` | `security_result.detection_fields.key` UDM field is set to `FailureType` If the `FailureType` log field value is equal to `0` then, the `security_result.detection_fields.value` UDM field is set to `Default`. Else, if `FailureType` log field value is equal to `1` then, the `security_result.detection_fields.value` UDM field is set to `MailboxWrite` |
| `DataStoreType` | `security_result.detection_fields[DataStoreType]` | `security_result.detection_fields.key` UDM field is set to `DataStoreType` If the `DataStoreType` log field value is equal to `0` then, the `security_result.detection_fields.value` UDM field is set to `CanonicalStore`. Else, if `DataStoreType` log field value is equal to `1` then, the `security_result.detection_fields.value` UDM field is set to `StagingStore` |
| `UserAction` | `additional.fields[UserAction]` | `additional.fields.key` UDM field is set to `UserAction` If the `UserAction` log field value is equal to `0` then, the `additional.fields.value` UDM field is set to `TriggerExport`. Else, if `UserAction` log field value is equal to `1` then, the `additional.fields.value` UDM field is set to `DownloadZipFile` |
| `SharePointMetadata.SiteCollectionGuid` | `target.resource.attribute.labels[SharePointMetadata_SiteCollectionGuid]` | If the Operation contains one of the following values, then the `target.resource.attribute.labels.key` UDM field is set to `SharePointMetadata_SiteCollectionGuid` and the `SharePointMetadata.SiteCollectionGuid` log field is mapped to the `target.resource.attribute.labels.value` UDM field: - `MipLabel` - `DlpRuleMatch` - `DLPRuleMatch` - `DlpRuleUndo` - `DLPRuleUndo` - `DlpInfo` |
| `SharePointMetadata.DocumentLastModifier` | `target.resource.attribute.labels[SharePointMetadata_DocumentLastModifier]` | If the Operation contains one of the following values, then the `target.resource.attribute.labels.key` UDM field is set to `SharePointMetadata_DocumentLastModifier` and the `SharePointMetadata.DocumentLastModifier` log field is mapped to the `target.resource.attribute.labels.value` UDM field: - `MipLabel` - `DlpRuleMatch` - `DLPRuleMatch` - `DlpRuleUndo` - `DLPRuleUndo` - `DlpInfo` |
| `SharePointMetadata.UniqueId` | `target.resource.attribute.labels[SharePointMetadata_UniqueId]` | If the Operation contains one of the following values, then the `target.resource.attribute.labels.key` UDM field is set to `SharePointMetadata_UniqueId` and the `SharePointMetadata.UniqueId` log field is mapped to the `target.resource.attribute.labels.value` UDM field: - `MipLabel` - `DlpRuleMatch` - `DLPRuleMatch` - `DlpRuleUndo` - `DLPRuleUndo` - `DlpInfo` |
| `SharePointMetadata.FileOwner` | `about.resource.attribute.labels[SharePointMetadata_FileOwner]` | If the Operation contains one of the following values, then the `about.resource.attribute.labels.key` UDM field is set to `SharePointMetadata_FileOwner` and the `SharePointMetadata.FileOwner` log field is mapped to the `about.resource.attribute.labels.value` UDM field: - `MipLabel` - `DlpRuleMatch` - `DLPRuleMatch` - `DlpRuleUndo` - `DLPRuleUndo` - `DlpInfo` |
| `SharePointMetadata.LastModifiedTime` | `additional.fields[SharePointMetadata_LastModifiedTime]` | If the Operation contains one of the following values, then the `additional.fields.key` UDM field is set to `SharePointMetadata_LastModifiedTime` and the `SharePointMetadata.LastModifiedTime` log field is mapped to the `additional.fields.value` UDM field: - `MipLabel` - `DlpRuleMatch` - `DLPRuleMatch` - `DlpRuleUndo` - `DLPRuleUndo` - `DlpInfo` |
| ID | `metadata.product_log_id` | |
| RecordType | security_result.detection_fields.key/value security_result.detection_fields.key is set to {RecordeType} - RecordTypeNameFromDoc security_result.detection_fields.value is set to RecordTypeDescriptionFromDoc | |
| CreationTime | `metadata.event_timestamp` | |
| Operation | `metadata.product_event_type` | |
| OrganizationId | `principal.resource.product_object_id` | |
| ActorInfoString | `network.http.user_agent` | If the `ActorInfoString` log field value is not empty and if it matches the regular expression pattern `*?UserAgent=(?[^;]+).*` then, the `temp_agent` extracted field is mapped to the `network.http.user_agent` UDM field. If `ActorInfoString` log field value contains substring as `UserAgent=NoUserAgent` and if `ClientInfoString` log field value matches the regular expression pattern `Client=.*;(?[^;]+).*\\[AppId=` then, the `agent` extracted field is mapped to the `network.http.user_agent` UDM field. Else it will map empty string. If `ActorInfoString` log field value contains substring as `Client=` and if it matches the regular expression pattern `Client=.*;(?[^;]+).*\\[AppId=` then, the `temp_agent` extracted field is mapped to the `network.http.user_agent` UDM field. If `ActorInfoString` doesn't matches any regular expression pattern, then the `ActorInfoString` log field value is mapped to the `network.http.user_agent` UDM field. If `ActorInfoString` log field value is empty, then the `ClientInfoString` log field value is mapped to the `network.http.user_agent` UDM field. |
| UserType | `principal.user.attribute.roles.name` | |
| UserId | principal.user.email_addresses or principal.user.userid target.user.email_addresses or target.user.userid If is Operation is UserLoggedIn, UserLoginFailed, Add OAuth2PermissionGrant, TeamsUserSignedOut, or Add delegated permission grant then UserId is mapped to target.user else UserId is mapped to principal.user If UserId value contains email address then it is mapped to email_address, else it is mapped to userid. | |
| ClientIP | principal.ip and principal.port | |
| Workload | `target.application` | |
| AppAccessContext | network.session.id security_result.detection_fields.key/value AADSessionId is mapped to network.session.id CorrelationId is mapped to security_result.detection_fields.key/value | |
| `AdditionalData` | `additional.fields[AdditionalData]` | Iterate for each key, value pair of log field `AdditionalData`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `InsightData` | `additional.fields[InsightData]` | Iterate for each key, value pair of log field `InsightData`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `PropertyCollection` | `additional.fields[PropertyCollection]` | Iterate for each key, value pair of log field `PropertyCollection`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ItemDetails` | `additional.fields[ItemDetails]` | Iterate for each key, value pair of log field `ItemDetails`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ModifiedFields` | `additional.fields[ModifiedFields]` | Iterate for each key, value pair of log field `ModifiedFields`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `SubscriptionDetails` | `additional.fields[SubscriptionDetails]` | Iterate for each key, value pair of log field `SubscriptionDetails`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ExceptionInfo` | `additional.fields[ExceptionInfo]` | Iterate for each key, value pair of log field `ExceptionInfo`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ArtifactsShared` | `additional.fields[ArtifactsShared]` | Iterate for each key, value pair of log field `ArtifactsShared`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ExportedArtifactInfo` | `additional.fields[ExportedArtifactInfo]` | Iterate for each key, value pair of log field `ExportedArtifactInfo`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ExportedArtifactDownloadInfo` | `additional.fields[ExportedArtifactDownloadInfo]` | Iterate for each key, value pair of log field `ExportedArtifactDownloadInfo`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `HostedContents` | `additional.fields[HostedContents]` | Iterate for each key, value pair of log field `HostedContents`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ProtectionEventData` | `additional.fields[ProtectionEventData]` | Iterate for each key, value pair of log field `ProtectionEventData`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `GitIntegrationRequest` | `additional.fields[GitIntegrationRequest]` | Iterate for each key, value pair of log field `GitIntegrationRequest`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ArtifactAccessRequestInfo` | `additional.fields[ArtifactAccessRequestInfo]` | Iterate for each key, value pair of log field `ArtifactAccessRequestInfo`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `PaginatedReportDataSources` | `additional.fields[PaginatedReportDataSources]` | Iterate for each key, value pair of log field `PaginatedReportDataSources`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `SRPolicyMatchDetails` | `additional.fields[SRPolicyMatchDetails]` | Iterate for each key, value pair of log field `SRPolicyMatchDetails`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `GatewayClusterDatasources` | `additional.fields[GatewayClusterDatasources]` | Iterate for each key, value pair of log field `GatewayClusterDatasources`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `DatasourceInformations` | `additional.fields[DatasourceInformations]` | Iterate for each key, value pair of log field `DatasourceInformations`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `CustomProperties` | `additional.fields[CustomProperties]` | Iterate for each key, value pair of log field `CustomProperties`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `PinReportToTabInformation` | `additional.fields[PinReportToTabInformation]` | Iterate for each key, value pair of log field `PinReportToTabInformation`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `WorkspaceAccessList` | `additional.fields[WorkspaceAccessList]` | Iterate for each key, value pair of log field `WorkspaceAccessList`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `FileData.DocumentId` | `target.resource.product_object_id` | |
| `FileData.FileName` | `target.file.full_path` | |
| `FileData.FilePath` | `target.url` | |
| `FileData.FileSize` | `target.file.size` | |
| `FileData.FileVerdict` | `security_result.detection_fields[file_vedict]` | |
| `FileData.FileVerdict` | `security_result.category` | If the `FileData.FileVerdict` log field value *not* empty then, the `security_result.category` UDM field is set to `SOFTWARE_MALICIOUS`. |
| `FileData.MalwareFamily` | `security_result.threat_name` | |
| `FileData.SHA256` | `target.file.sha256` | |
| `FileData` | `additional.fields[FileData]` | Iterate for each key, value pair of log field `FileData`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `EventDetails` | `additional.fields[EventDetails]` | Iterate for each key, value pair of log field `EventDetails`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `AuditData` | `additional.fields[AuditData]` | Iterate for each key, value pair of log field `AuditData`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `OpenShift` | `additional.fields[OpenShift]` | Iterate for each key, value pair of log field `OpenShift`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `DeliveryMessageInfo` | `additional.fields[DeliveryMessageInfo]` | Iterate for each key, value pair of log field `DeliveryMessageInfo`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `RescanResult` | `additional.fields[RescanResult]` | Iterate for each key, value pair of log field `RescanResult`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `GradingResult` | `additional.fields[GradingResult]` | Iterate for each key, value pair of log field `GradingResult`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `Sources` | `additional.fields[Sources]` | Iterate for each key, value pair of log field `Sources`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ExternalResource` | `additional.fields[ExternalResource]` | Iterate for each key, value pair of log field `ExternalResource`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `Settings` | `additional.fields[Settings]` | Iterate for each key, value pair of log field `Settings`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `EditedEntities` | `additional.fields[EditedEntities]` | Iterate for each key, value pair of log field `EditedEntities`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `EntityData` | `additional.fields[EntityData]` | Iterate for each key, value pair of log field `EntityData`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `NewEntities` | `additional.fields[NewEntities]` | Iterate for each key, value pair of log field `NewEntities`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `RuleActions` | `additional.fields[RuleActions]` | Iterate for each key, value pair of log field `RuleActions`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `MembershipInformation` | `additional.fields[MembershipInformation]` | Iterate for each key, value pair of log field `MembershipInformation`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ModelSettings` | `additional.fields[ModelSettings]` | Iterate for each key, value pair of log field `ModelSettings`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `RemovedEntities` | `additional.fields[RemovedEntities]` | Iterate for each key, value pair of log field `RemovedEntities`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `GatewayClusters` | `additional.fields[GatewayClusters]` | Iterate for each key, value pair of log field `GatewayClusters`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `AttackSimulationInfo` | `additional.fields[AttackSimulationInfo]` | Iterate for each key, value pair of log field `AttackSimulationInfo`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `UpdateDatasourcesRequest` | `additional.fields[UpdateDatasourcesRequest]` | Iterate for each key, value pair of log field `UpdateDatasourcesRequest`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `AuthorizedGroup` | `additional.fields[AuthorizedGroup]` | Iterate for each key, value pair of log field `AuthorizedGroup`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `ExtendedProperties` | `additional.fields[ExtendedProperties]` | Iterate for each key, value pair of log field `ExtendedProperties`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `AffectedItems` | `additional.fields[AffectedItems]` | Iterate for each key, value pair of log field `AffectedItems`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `Attendees` | `additional.fields[Attendees]` | Iterate for each key, value pair of log field `Attendees`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `SubscribeeInformation` | `additional.fields[SubscribeeInformation]` | Iterate for each key, value pair of log field `SubscribeeInformation`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `SubscriptionSchedule` | `additional.fields[SubscriptionSchedule]` | Iterate for each key, value pair of log field `SubscriptionSchedule`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `SharePointMetaData` | `additional.fields[SharePointMetaData]` | Iterate for each key, value pair of log field `SharePointMetaData`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `SharingInformation` | `additional.fields[SharingInformation]` | Iterate for each key, value pair of log field `SharingInformation`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `FolderAccessRequests` | `additional.fields[FolderAccessRequests]` | Iterate for each key, value pair of log field `FolderAccessRequests`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `DeploymentPipelineAccesses` | `additional.fields[DeploymentPipelineAccesses]` | Iterate for each key, value pair of log field `DeploymentPipelineAccesses`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `Folders` | `additional.fields[Folders]` | Iterate for each key, value pair of log field `Folders`, then `key` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `GeoLocation` | `principal.location.name` | |
| `DestinationFileName` | `target.file.full_path` | `%{DestinationRelativeUrl} - %{DestinationFileName}` log field is mapped to the `target.file.full_path` UDM field. |
| `AppId` | `additional.fields[app_id]` | |
| `TokenTenantId` | `additional.fields[token_tenant_id]` | |
| `EventSignature` | `additional.fields[event_signature]` | |
| `CustomizedDoclib` | `additional.fields[customized_doclib]` | |
| `ListName` | `additional.fields[list_name]` | |
| `ListUrl` | `additional.fields[list_url]` | |
| `SaveToSentItems` | `additional.fields[save_to_sent_items]` | |
| `CrossMailboxOperation` | `additional.fields[cross_mailbox_operation]` | |
| `ClientRegion` | `additional.fields[client_region]` | |
| `CopilotLogVersion` | `additional.fields[copilot_log_version]` | |
| `TargetUserOrGroupType` | `target.user.attributes.labels[target_user_or_group_type]` | |
| `ErrorNumber` | `additional.fields[error_number]` | |
| `TokenObjectId` | `additional.fields[token_object_id]` | |
| `ResourceTenantId` | `additional.fields[resource_tenant_id]` | |
| `FileSizeBytes` | `additional.fields[file_size_bytes]` | |
| `DoNotDistributeEvent` | `additional.fields[do_not_distribute_event]` | |
| `UniqueSharingId` | `additional.fields[UniqueSharingId]` | |
| `CompletionStatus` | `additional.fields[completion_status]` | |
| `IsInternalServiceRequest` | `additional.fields[is_internal_service_request]` | |
| `ResultsCount` | `additional.fields[results_count]` | |
| `SearchFilters` | `additional.fields[search_filters]` | |
| `SearchJobId` | `additional.fields[search_job_id]` | |
| `SearchJobName` | `additional.fields[search_job_name]` | |
| `SearchSource` | `additional.fields[search_source]` | |
| `CustomUniqueId` | `additional.fields[custom_unique_id]` | |
| `SearchQueryText` | `additional.fields[search_query_text]` | |
| `ListItemVersion` | `additional.fields[list_item_version]` | |
| `DeviceId` | `principal.asset.attribute.labels[device_id]` | |
| `OldValue` | `target.resource.attribute.labels[old_value]` | |
| `CrossScopeSyncDelete` | `additional.fields[cross_scope_sync_delete]` | |
| `IsCopilotMentioned` | `additional.fields[is_copilot_mentioned]` | |
| `ParentMessageId` | `target.resource_ancestors.product_object_id` | |
| `SendOnBehalfOfUserMailboxGuid` | `additional.fields[send_on_behalf_of_user_mailbox_guid]` | |
| `NonPIIParameters` | `additional.fields[non_pii_parameters]` | |
| `AppPoolName` | `additional.fields[app_pool_name]` | |
| `UserTenantId` | `additional.fields[user_tenant_id]` | |
| `CommunicationSubType` | `additional.fields[communication_sub_type]` | |
| `ConferenceUri` | `additional.fields[conference_uri]` | |
| `ICalUid` | `additional.fields[ical_uid]` | |
| `ProviderTypes` | `additional.fields[provider_types]` | |
| `ExchangeId` | `additional.fields[exchange_id]` | |
| `EnvironmentId` | `additional.fields[environment_id]` | |
| `JsonPropertiesCollection` | `additional.fields[json_properties_collection]` | |
| `RequiresCustomerKeyEncryption` | `additional.fields[requires_customer_key_encryption]` | |
| `RecipientDataverseId` | `additional.fields[recipient_dataverse_id]` | |
| `RecipientDataverseType` | `additional.fields[recipient_dataverse_type]` | |
| `UserUPN` | `additional.fields[user_upn]` | |
| `ContactEmail1DisplayName` | `additional.fields[contact_email1_display_name]` | |
| `ContactEmail1EmailAddress` | `additional.fields[contact_email1_email_address]` | |
| `ContactEmail2DisplayName` | `additional.fields[contact_email2_display_name]` | |
| `ContactEmail2EmailAddress` | `additional.fields[contact_email2_email_address]` | |
| `FilteringDate` | `additional.fields[filtering_date]` | |
| `SubmissionChannel` | `additional.fields[submission_channel]` | |
| `SubmissionContentSubType` | `additional.fields[submission_content_sub_type]` | |
| `SubmitterDisplayName` | `additional.fields[submitter_display_name]` | |
| `SubmitterId` | `additional.fields[submitter_id]` | |
| `RemoteItemWebUrl` | `additional.fields[remote_item_web_url]` | |
| `InternalTarget` | `additional.fields[internal_target]` | |
| `IrmContentId` | `additional.fields[irm_content_id]` | |
| `OperationDateTime` | `additional.fields[operation_date_time]` | |
| `TargetPrinterName` | `additional.fields[target_printer_name]` | |
| `TargetUrl` | `additional.fields[target_url]` | |
| `Detail` | `target.resource.attribute.labels[detail]` | |
| `OrganizationAdmins` | `target.user.first_name` | |
| `OrganizationOwner` | `target.user.attributes.labels[organization_owner]` | |
| `DlpOriginalFilePath` | `additional.fields[dlp_original_file_path]` | |
| `SiteSensitivityLabelId` | `additional.fields[site_sensitivity_label_id]` | |
| `BillingType` | `additional.fields[billing_type]` | |
| `HasFullReportAttachment` | `additional.fields[has_full_report_attachment]` | |
| `TopicId` | `additional.fields[topic_id]` | |
| `AppReportId` | `additional.fields[app_report_id]` | |
| `MessageDeleteType` | `additional.fields[message_delete_type]` | |
| `ParentArchiveHash` | `additional.fields[parent_archive_hash]` | |
| `IsJoinedFromLobby` | `additional.fields[is_joined_from_lobby]` | |
| `RmsContentInstanceId` | `additional.fields[rms_content_instance_id]` | |
| `AccountId` | `additional.fields[account_id]` | |
| `CollectionName` | `additional.fields[collection_name]` | |
| `DomainReference` | `additional.fields[domain_reference]` | |
| `PolicyType` | `additional.fields[policy_type]` | |
| `IsCustomEntity` | `additional.fields[is_custom_entity]` | |
| `OperationType` | `additional.fields[operation_type]` | |
| `LabelAction` | `additional.fields[label_action]` | |
| `ImportId` | `additional.fields[import_id]` | |
| `UserName` | `principal.user.first_name` | |
| `UserRole` | `principal.user.attributes.labels[user_role]` | |
| `Classification` | `principal.resource.attribute.labels[classification]` | |
| `Comment` | `principal.user.attribute.labels[comment]` | |
| `Requestor` | `additional.fields[requestor]` | |
| `ResolvingComment` | `additional.fields[resolving_comment]` | |
| `AppExternalId` | `additional.fields[app_external_id]` | |
| `AlertCreationTime` | `additional.fields[alert_creation_time]` | |
| `AlertSeverity` | `additional.fields[alert_severity]` | |
| `AlertUri` | `additional.fields[alert_uri]` | |
| `MachineFQDN` | `additional.fields[machine_fqdn]` | |
| `WDATPMachineID` | `additional.fields[wdatp_machine_id]` | |
| `SharedWithContainerAccessLevel` | `target.resource.attribute.labels[shared_with_container_access_level]` | If the `SharedWithContainerAccessLevel` log field value is equal to `1` then, the `target.resource.attribute.labels[shared_with_container_access_level]` UDM field is set to `ReadAccess`. Else, if `SharedWithContainerAccessLevel` log field value is equal to `2` then, the `target.resource.attribute.labels[shared_with_container_access_level]` UDM field is set to `ReadWriteAccess`. Else, if `SharedWithContainerAccessLevel` log field value is equal to `3` then, the `target.resource.attribute.labels[shared_with_container_access_level]` UDM field is set to `FullAccess`. |
| `SharedWithContainerId` | `target.resource.attribute.labels[shared_with_container_id]` | |
| `SharedWithContainerType` | `target.resource.attribute.labels[shared_with_container_type]` | If the `SharedWithContainerType` log field value is equal to `0` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `Invalid`. Else, if `SharedWithContainerType` log field value is equal to `2` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `Group`. Else, if `SharedWithContainerType` log field value is equal to `3` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `TeamsConversation`. Else, if `SharedWithContainerType` log field value is equal to `4` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `OfficeDocument`. Else, if `SharedWithContainerType` log field value is equal to `5` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `Roster`. Else, if `SharedWithContainerType` log field value is equal to `6` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `Project`. Else, if `SharedWithContainerType` log field value is equal to `7` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `User`. Else, if `SharedWithContainerType` log field value is equal to `8` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `TeamsChannel`. Else, if `SharedWithContainerType` log field value is equal to `10` then, the `target.resource.attribute.labels[shared_with_container_type]` UDM field is set to `PlannerTask`. |
| `NewPlanId` | `target.resource.attribute.labels[new_plan_id]` | |
| `OriginalContainerId` | `target.resource.attribute.labels[original_container_id]` | |
| `ExcludePersonalWorkspaces` | `additional.fields[exclude_personal_workspaces]` | |
| `ContainerInstanceId` | `additional.fields[container_instance_id]` | |
| `ContainerTypeId` | `additional.fields[container_type_id]` | |
| `SubstrateGroupId` | `additional.fields[substrate_group_id]` | |
| `AgentId` | `additional.fields[agent_id]` | |
| `AgentName` | `additional.fields[agent_name]` | |
| `SourceLabel` | `target.file.tags` | |
| `ActivityStartTime` | `additional.fields[activity_start_time]` | |
| `AlertCategory` | `security_result.category_details` | |
| `AlertDescription` | `security_result.summary` | |
| `AlertStatus` | `additional.fields[alert_status]` | |
| `CatalogId` | `additional.fields[catalog_id]` | |
| `ChangeRequestId` | `additional.fields[change_request_id]` | |
| `ObjectCollectionId` | `additional.fields[object_collection_id]` | |
| `ObjectCollectionId` | `additional.fields[object_collection_id]` | |
| `ObjectFullyQualifiedName` | `additional.fields[object_fully_qualified_name]` | |
| `ObjectName` | `additional.fields[object_name]` | |
| `ServiceType` | `target.resource.attribute.labels[service_type]` | |
| `DataSourceModifiedTime` | `additional.fields[data_source_modified_time]` | |
| `SharingScope` | `additional.fields[sharing_scope]` | |
| `ContactEmail3DisplayName` | `additional.fields[contact_email3_display_name]` | |
| `ContactEmail3EmailAddress` | `additional.fields[contact_email3_email_address]` | |
| `EvaluationSource` | `additional.fields[evaluation_source]` | |
| `CredentialSetupMode` | `additional.fields[credential_setup_mode]` | |
| `NewContainerId` | `target.resource.attribute.labels[new_container_id]` | |
| `NewContainerType` | `target.resource.attribute.labels[new_container_type]` | If the `NewContainerType` log field value is equal to `0` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `Invalid`. Else, if `NewContainerType` log field value is equal to `2` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `Group`. Else, if `NewContainerType` log field value is equal to `3` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `TeamsConversation`. Else, if `NewContainerType` log field value is equal to `4` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `OfficeDocument`. Else, if `NewContainerType` log field value is equal to `5` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `Roster`. Else, if `NewContainerType` log field value is equal to `6` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `Project`. Else, if `NewContainerType` log field value is equal to `7` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `User`. Else, if `NewContainerType` log field value is equal to `8` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `TeamsChannel`. Else, if `NewContainerType` log field value is equal to `10` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `PlannerTask`. |
| `OriginalContainerType` | `target.resource.attribute.labels[original_container_type]` | If the `OriginalContainerType` log field value is equal to `0` then, the `target.resource.attribute.labels[original_container_type]` UDM field is set to `Invalid`. Else, if `OriginalContainerType` log field value is equal to `2` then, the `target.resource.attribute.labels[original_container_type]` UDM field is set to `Group`. Else, if `OriginalContainerType` log field value is equal to `3` then, the `target.resource.attribute.labels[original_container_type]` UDM field is set to `TeamsConversation`. Else, if `OriginalContainerType` log field value is equal to `4` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `OfficeDocument`. Else, if `OriginalContainerType` log field value is equal to `5` then, the `target.resource.attribute.labels[original_container_type]` UDM field is set to `Roster`. Else, if `OriginalContainerType` log field value is equal to `6` then, the `target.resource.attribute.labels[original_container_type]` UDM field is set to `Project`. Else, if `OriginalContainerType` log field value is equal to `7` then, the `target.resource.attribute.labels[original_container_type]` UDM field is set to `User`. Else, if `OriginalContainerType` log field value is equal to `8` then, the `target.resource.attribute.labels[original_container_type]` UDM field is set to `TeamsChannel`. Else, if `OriginalContainerType` log field value is equal to `10` then, the `target.resource.attribute.labels[original_container_type]` UDM field is set to `PlannerTask`. |
| `ObjectFullyQualifiedName` | `additional.fields[object_fully_qualified_name]` | |
| `ObjectName` | `additional.fields[object_name]` | |
| `ServiceType` | `target.resource.attribute.labels[service_type]` | |
| `DataSourceModifiedTime` | `additional.fields[data_source_modified_time]` | |
| `SharingScope` | `additional.fields[sharing_scope]` | |
| `ContactEmail3DisplayName` | `additional.fields[contact_email3_display_name]` | |
| `ContactEmail3EmailAddress` | `additional.fields[contact_email3_email_address]` | |
| `EvaluationSource` | `additional.fields[evaluation_source]` | |
| `CredentialSetupMode` | `additional.fields[credential_setup_mode]` | |
| `NewContainerId` | `target.resource.attribute.labels[new_container_id]` | |
| `NewContainerType` | `target.resource.attribute.labels[new_container_type]` | If the `NewContainerType` log field value is equal to `0` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `Invalid`. Else, if `SharedWithContainerType` log field value is equal to `2` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `Group`. Else, if `SharedWithContainerType` log field value is equal to `3` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `TeamsConversation`. Else, if `SharedWithContainerType` log field value is equal to `4` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `OfficeDocument`. Else, if `SharedWithContainerType` log field value is equal to `5` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `Roster`. Else, if `SharedWithContainerType` log field value is equal to `6` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `Project`. Else, if `SharedWithContainerType` log field value is equal to `7` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `User`. Else, if `SharedWithContainerType` log field value is equal to `8` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `TeamsChannel`. Else, if `SharedWithContainerType` log field value is equal to `10` then, the `target.resource.attribute.labels[new_container_type]` UDM field is set to `PlannerTask`. |
| `NewPlanId` | `target.resource.attribute.labels[new_plan_id]` | |
| `OriginalContainerId` | `target.resource.attribute.labels[original_container_id]` | |
| `OriginalPlanId` | `target.resource.attribute.labels[original_plan_id]` | |
| `SubfolderId` | `additional.fields[subfolder_id]` | |
| `SubfolderName` | `additional.fields[subfolder_name]` | |
| `SubfolderObjectId` | `additional.fields[subfolder_object_id]` | |
| `ClientIPs` | `additional.fields[client_ips]` | |
| `ParentCommentId` | `additional.fields[parent_comment_id]` | |
| `Invitee` | `target.user.email_addresses` | |
| `IsWorkflow` | `additional.fields[is_workflow]` | |
| `EndTimeUtc` | `target.resource.attribute.labels[end_time_utc]` | |
| `FormType` | `target.resource.attribute.labels[form_type]` | |
| `Actions` | `security_result.detection_fields[actions]` | |
| `RunningTime` | `additional.fields[running_time]` | |
| `IsPolicyHit` | `additional.fields[is_policy_hit]` | |
| `PackageId` | `additional.fields[package_id]` | |
| `GatewayClusterId` | `additional.fields[gateway_cluster_id]` | |
| `IsTenantAdminApi` | `additional.fields[is_tenant_admin_api]` | |
| `SingleSignOnType` | `additional.fields[single_sign_on_type]` | |
| `CloudType` | `additional.fields[cloud_type]` | |
| `ResourceSpecificApplicationPermissions` | `additional.fields[resource_specific_application_permissions]` | |
| `ModelId` | `additional.fields[model_id]` | |
| `Monikers` | `additional.fields[monikers]` | |
| `ActingCallerId` | `additional.fields[acting_caller_id]` | |
| `ActingCallerUPN` | `additional.fields[acting_caller_upn]` | |
| `ExceptionMessage` | `additional.fields[exception_message]` | |
| `PostExecutionMessage` | `additional.fields[post_execution_message]` | |
| `PreExecutionMessage` | `additional.fields[pre_execution_message]` | |
| `RemoteTenantId` | `additional.fields[remote_tenant_id]` | |
| `RemoteUserId` | `additional.fields[remote_user_id]` | |
| `IsDiscoverable` | `additional.fields[is_discoverable]` | |
| `Experience` | `additional.fields[experience]` | |
| `ObjectDisplayName` | `additional.fields[object_display_name]` | |
| `OperationId` | `additional.fields[operation_id]` | |
| `Timestamp` | `additional.fields[timestamp]` | |
| `ContactEmail` | `additional.fields[contact_email]` | |
| `UrlClickAction` | `security_result.action_details` | If the `UrlClickAction` log field value is equal to `2` then, the `security_result.action_details` UDM field is set to `Blockpage`. Else, if `UrlClickAction` log field value is equal to `3` then, the `security_result.action_details` UDM field is set to `PendingDetonationPage`. Else, if `UrlClickAction` log field value is equal to `4` then, the `security_result.action_details` UDM field is set to `BlockPageOverride`. Else, if `UrlClickAction` log field value is equal to `5` then, the `"security_result.action_details` UDM field is set to `PendingDetonationPageOverride`. |
| `CustodianId` | `additional.fields[custodian_id]` | |
| `MD5Hash` | `additional.fields[md5_hash]` | |
| `SHA256Hash` | `additional.fields[sha256_hash]` | |
| `InviteeTeamName` | `additional.fields[invitee_team_name]` | |
| `GatewayClustersObjectIds` | `additional.fields[gateway_clusters_object_ids]` | |
| `OwningAppContext` | `additional.fields[owning_app_context]` | |
| `ModelsSnapshots` | `additional.fields[models_snapshots]` | |
| `UniqueTokenIdentifier` | `target.resource.attribute.labels[unique_token_identifier]` | |
| `QueryId` | `additional.fields[query_id]` | |
| `CopilotMessageId` | `additional.fields[copilot_message_id]` | |
| `DelegatedFrom` | `additional.fields[delegated_from]` | |
| `WpaUserRole` | `principal.user.attribute.roles.name` | |
| `DatasourceObjectIds` | `additional.fields[datasource_object_ids]` | |
| `TargetUserRole` | `additional.fields[target_user_role]` | |
| `QueryText` | `additional.fields[query_text]` | |
| `ClientUserAgent` | `additional.fields[client_user_agent]` | |
| `QuerySource` | `additional.fields[query_source]` | |
| `ScenarioName` | `additional.fields[scenario_name]` | |
| `MessageType` | `additional.fields[message_type]` | |
| `CurrentLabel` | `additional.fields[current_label]` | |
| `DecisionDate` | `additional.fields[decision_date]` | |
| `StageId` | `additional.fields[stage_id]` | |
| `StageName` | `additional.fields[stage_name]` | |
| `SnapshotId` | `additional.fields[snapshot_id]` | |
| `AppIdentity` | `additional.fields[app_identity]` | |
| `MarkType` | `additional.fields[mark_type]` | |
| `ReactionEventType` | `additional.fields[reaction_event_type]` | |
| `ArchiveStatus` | `additional.fields[archive_status]` | |
| `ObjectVersion` | `additional.fields[object_version]` | |
| `EventName` | `additional.fields[event_name]` | |
| `PulseId` | `additional.fields[pulse_id]` | |
| `AppConsentOAuthScope` | `additional.fields[app_consent_oauth_scope]` | |
| `AppConsentUserObjectId` | `additional.fields[app_consent_user_object_id]` | |
| `Details` | `security_result.detection_fields[details]` | |
| `TimeOfClick` | `additional.fields[time_of_click]` | |
| `GatewayStatus` | `additional.fields[gateway_status]` | |
| `AzureTrustMode` | `additional.fields[azure_trust_mode]` | |
| `DetectionDate` | `additional.fields[detection_date]` | |
| `LastModifiedBy` | `target.resource.attribute.labels[last_modified_by]` | |
| `LastModifiedDate` | `target.resource.attribute.labels[last_modified_date]` | |
| `DatasourceDetails` | `additional.fields[datasource_details]` | |
| `IncludeExpressions` | `additional.fields[include_expressions]` | |
| `IncludeSubartifacts` | `additional.fields[include_subartifacts]` | |
| `Lineage` | `additional.fields[lineage]` | |
| `RequiredWorkspaces` | `additional.fields[required_workspaces]` | |
| `WorkspacesSemicolonDelimitedList` | `additional.fields[workspaces_semicolon_delimited_list]` | |
| `DataflowCertificationStage` | `additional.fields[dataflow_certification_stage]` | |
| `ImpactedUserId` | `additional.fields[impacted_user_id]` | |
| `ImpactedUserName` | `additional.fields[impacted_user_name]` | |
| `AddedReviewer` | `additional.fields[added_reviewer]` | |
| `WorkloadType` | `additional.fields[workload_type]` | |
| `WorkspacesModifiedSince` | `additional.fields[workspaces_modified_since]` | |
| `EndPoint` | `additional.fields[end_point]` | |
| `ItemIds` | `additional.fields[item_ids]` | |
| `ItemNames` | `additional.fields[Item_names]` | |
| `Object1Type` | `target.resource.attribute.labels[object1_type]` | |
| `Object2Type` | `target.resource.attribute.labels[object2_type]` | |
| `ModifiedProperty` | `additional.fields[modified_property]` | |
| `OperationDetail` | `additional.fields[operation_detail]` | |
| `GroupId` | `additional.fields[group_id]` | |
| `ExportEventEndDateTimeParameter` | `additional.fields[export_event_end_date_time_parameter]` | |
| `ExportEventStartDateTimeParameter` | `additional.fields[export_event_start_date_time_parameter]` | |
| `AddedRolePermission` | `additional.fields[added_role_permission]` | |
| `RoleAssignment` | `additional.fields[role_assignment]` | |
| `RoleDefinitionId` | `additional.fields[role_definition_id]` | |
| `ArtifactObjectId` | `additional.fields[artifact_object_id]` | |
| `AddedScopes` | `additional.fields[added_scopes]` | |
| `DeletedScopes` | `additional.fields[deleted_scopes]` | |
| `IsScopedToAll` | `additional.fields[is_scoped_to_all]` | |
| `RoleAssignmentId` | `additional.fields[role_assignment_id]` | |
| `ProjectId` | `target.resource.attribute.labels[project_id]` | |
| `TaskId` | `target.resource.attribute.labels[task_id]` | |
| `RecipientUPN` | `additional.fields[recipient_upn]` | |
| `DeletedRoleAssignment` | `additional.fields[deleted_role_assignment]` | |
| `MemberIds` | `target.resource.attribute.labels[member_ids]` | |
| `ReportMobileLayoutAction` | `additional.fields[report_mobile_layout_action]` | |
| `CopiedReportId` | `additional.fields[copied_report_id]` | |
| `CopiedReportName` | `additional.fields[copied_report_name]` | |
| `TargetWorkspaceId` | `additional.fields[target_workspace_id]` | |
| `TraceId` | `additional.fields[trace_id]` | |
| `IsTemplateAppFromMarketplace` | `additional.fields[is_template_app_from_marketplace]` | |
| `IsUpdateAppActivity` | `additional.fields[is_update_app_activity]` | |
| `TemplateAppIsInstalledWithAutomation` | `additional.fields[template_app_is_installed_with_automation]` | |
| `DataflowAllowNativeQueries` | `additional.fields[dataflow_allow_native_queries]` | |
| `GatewayMemberId` | `additional.fields[gateway_member_id]` | |
| `PaginatedReportMonikers` | `additional.fields[paginated_report_monikers]` | |
| `SkipForServiceWorker` | `additional.fields[skip_for_service_worker]` | |
| `MentionedUsersInformation` | `additional.fields[mentioned_users_information]` | |
| `RoadmapId` | `target.resource.attribute.labels[roadmap_id]` | |
| `RoadmapItemId` | `target.resource.attribute.labels[roadmap_item_id]` | |
| `OriginalOwner` | `additional.fields[original_owner]` | |
| `TakingOverOwner` | `additional.fields[taking_over_owner]` | |
| `NewLabel` | `additional.fields[new_label]` | |
| `AppInstanceId` | `additional.fields[app_instance_id]` | |
| `ExtendedDate` | `additional.fields[extended_date]` | |
| `Seveirty` | `typo` | |
| `BCLValue` | `additional.fields[bcl_value]` | |
| `Language` | `additional.fields[language]` | |
| `AssociatedAdminUnits` | `additional.fields[AssociatedAdminUnits_%{index}]` | Iterate for each element `admin_unit` with index `index` in the `AssociatedAdminUnits` log field array, then The `additional.fields.key` UDM field is set to `AssociatedAdminUnits_%{index}` and the `admin_unit` log field is mapped to the `additional.fields.value` UDM field. |
| `CertificateIssuer` | `additional.fields[certificate_issuer]` | |
| `CertificateSerialNumber` | `additional.fields[certificate_serial_number]` | |
| `CertificateSubject` | `additional.fields[certificate_subject]` | |
| `CreatedBySource` | `additional.fields[created_by_source]` | |
| `IndicatorAction` | `additional.fields[indicator_action]` | |
| `IndicatorAlertSeverity` | `additional.fields[indicator_alert_severity]` | |
| `IndicatorBypassDuration` | `additional.fields[indicator_bypass_duration]` | |
| `IndicatorDescription` | `additional.fields[indicator_description]` | |
| `IndicatorDeviceGroups` | `additional.fields[indicator_device_groups]` | |
| `IndicatorGenerateAlerts` | `additional.fields[indicator_generate_alerts]` | |
| `IndicatorId` | `additional.fields[indicator_id]` | |
| `IndicatorNotificationUrl` | `additional.fields[indicator_notification_url]` | |
| `IndicatorTitle` | `additional.fields[indicator_title]` | |
| `IndicatorType` | `additional.fields[indicator_type]` | |
| `IndicatorValue` | `additional.fields[indicator_value]` | |
| `SourceReferenceId` | `additional.fields[source_reference_id]` | |
| `IoaDefinitionId` | `additional.fields[ioa_definition_id]` | |
| `IsEnabled` | `additional.fields[is_enabled]` | |
| `RuleConditions` | `additional.fields[rule_conditions]` | |
| `RuleTitle` | `additional.fields[rule_title]` | |
| `ScopeConditions` | `additional.fields[scope_conditions]` | |
| `SuppressionRuleId` | `additional.fields[suppression_rule_id]` | |
| `DestMailboxId` | `target.user.attribute.labels[dest_mailbox_id]` | |
| `DestMailboxOwnerSid` | `target.user.attribute.labels[dest_mailbox_owner_sid]` | |
| `DestMailboxOwnerUPN` | `target.user.attribute.labels[dest_mailbox_owner_upn]` | |
| `DeploymentMethod` | `additional.fields[deployment_method]` | |
| `OsFamily` | `additional.fields[os_family]` | |
| `PackageExpiration` | `additional.fields[package_expiration]` | |
| `JobId` | `target.process.pid` | |
| `Object1Id` | `target.resource.attribute.labels[object1_id]` | |
| `Object1Name` | `target.resource.attribute.labels[object1_name]` | |
| `Justification` | `security_result.detection_fields[justification]` | |
| `Audit` | `additional.fields[audit]` | |
| `Event` | `additional.fields[event]` | |
| `EventId` | `additional.fields[event_id]` | |
| `EventValue` | `target.user.email_addresses` | |
| `GatewayName` | `additional.fields[gateway_name]` | |
| `ReasonForExport` | `additional.fields[reason_for_export]` | |
| `ActionComment` | `additional.fields[action_comment]` | |
| `FileMD5` | `additional.fields[file_md5]` | |
| `FileSHA1` | `additional.fields[file_sha1]` | |
| `FileSHA256` | `additional.fields[file_sha256]` | |
| `FileSigner` | `additional.fields[file_signer]` | |
| `CommandType` | `additional.fields[command_type]` | |
| `GALChangeType` | `additional.fields[gal_change_type]` | |
| `PolicyChangeType` | `additional.fields[policy_change_type]` | |
| `RecipientId` | `additional.fields[recipient_id]` | |
| `DestMailboxOwnerMasterAccountSid` | `target.user.attribute.labels[dest_mailbox_owner_master_account_sid]` | |
| `AeDObjectType` | `additional.fields[aed_object_type]` | |
| `OnlineMeetingId` | `additional.fields[online_meeting_id]` | |
| `ExportName` | `additional.fields[export_name]` | |
| `DisplayName` | `principal.user.attribute.labels[display_name]` | |
| `ImpersonationType` | `additional.fields[impersonation_type]` | |
| `RecordNumber` | `additional.fields[record_number]` | |
| `PersonIds` | `additional.fields[person_ids]` | |
| `BcCompanyName` | `additional.fields[bc_company_name]` | |
| `BcCustomDimensions` | `additional.fields[bc_custom_dimensions]` | |
| `BcEnvironmentName` | `additional.fields[bc_environment_name]` | |
| `BcEnvironmentType` | `additional.fields[bc_environment_type]` | |
| `BcOperationName` | `additional.fields[bc_operation_name]` | |
| `AddedGALMemberships` | `additional.fields[added_gal_memberships]` | |
| `SensitivityLabelOrder` | `additional.fields[sensitivity_label_order]` | |
| `SiteSensitivityLabelOrder` | `additional.fields[site_sensitivity_label_order]` | |
| `NonCustodianSourceId` | `additional.fields[non_custodian_source_id]` | |
| `AccessRequestMessage` | `additional.fields[access_request_message]` | |
| `AccessRequestType` | `additional.fields[access_request_type]` | |
| `AffectedApps` | `additional.fields[affected_apps]` | |
| `AffectedGroups` | `target.group.attribute.labels[affected_groups]` | |
| `Initiator` | `additional.fields[initiator]` | |
| `PowerPlatformEnvironmentId` | `additional.fields[power_platform_environment_id]` | |
| `ShareWithCurrentFilter` | `additional.fields[share_with_current_filter]` | |
| `ReportCertificationStage` | `additional.fields[report_certification_stage]` | |
| `GatewayState` | `additional.fields[gateway_state]` | |
| `ItemNewName` | `additional.fields[item_new_name]` | |
| `LabelVersion` | `additional.fields[label_version]` | |
| `DeploymentPipelineOperationId` | `additional.fields[deployment_pipeline_operation_id]` | |
| `ProjectEnabled` | `additional.fields[project_enabled]` | |
| `CustomVisualAccessTokenEtag` | `additional.fields[custom_visual_access_token_etag]` | |
| `CompletedLocations` | `additional.fields[completed_locations]` | |
| `ExpectedLocations` | `additional.fields[expected_locations]` | |
| `FailedLocations` | `additional.fields[failed_locations]` | |
| `MatchedItemCount` | `additional.fields[matched_item_count]` | |
| `TogetherModeSceneMetadataUrl` | `additional.fields[together_mode_scene_metadata_url]` | |
| `TogetherModeScenePreviewUrl` | `additional.fields[together_mode_scene_preview_url]` | |
| `ManagementRuleId` | `additional.fields[management_rule_id]` | |
| `Scenario` | `additional.fields[scenario]` | |
| `SimulationStatistics` | `additional.fields[simulation_statistics]` | |
| `SimulationStatus` | `additional.fields[simulation_status]` | |
| `TotalItemCount` | `additional.fields[total_item_count]` | |
| `TargetUserUPN` | `additional.fields[target_user_upn]` | |
| `ResultingPolicy` | `additional.fields[resulting_policy]` | |
| `ItemsCount` | `additional.fields[items_count]` | |
| `FeatureId` | `additional.fields[feature_id]` | |
| `ModuleId` | `additional.fields[module_id]` | |
| `AirAdminActionSource` | `additional.fields[air_admin_action_source]` | |
| `AirAdminActionType` | `additional.fields[air_admin_action_type]` | |
| `Approver` | `additional.fields[approver]` | |
| `ActionActivity` | `additional.fields[action_activity]` | |
| `ActionId` | `additional.fields[action_id]` | |
| `ActionName` | `additional.fields[action_name]` | |
| `ActionScore` | `additional.fields[action_score]` | |
| `ActionScoreChange` | `additional.fields[action_score_change]` | |
| `ManagedBy` | `additional.fields[managed_by]` | |
| `SourceReportId` | `additional.fields[source_report_id]` | |
| `SourceReportName` | `additional.fields[source_report_name]` | |
| `SourceWorkspaceId` | `additional.fields[source_workspace_id]` | |
| `ScopingEntityIds` | `additional.fields[scoping_entity_ids]` | |
| `ScopingEntityType` | `additional.fields[scoping_entity_type]` | |
| `SubscriptionType` | `additional.fields[subscription_type]` | |
| `UpdatedName` | `additional.fields[updated_description]` | |
| `UpdatedDescription` | `additional.fields[updated_description]` | |
| `ExternalUserTenantId` | `additional.fields[external_user_tenant_id]` | |
| `WorkspaceType` | `additional.fields[workspace_type]` | |
| `ResourceGroup` | `additional.fields[resource_group]` | |
| `Condition` | `additional.fields[condition]` | |
| `ContentContainsSensitiveInformation` | `security_result.detection_fields[content_contains_sensitive_information]` | |
| `ContentMatchesDataModel` | `security_result.detection_fields[content_matches_data_model]` | |
| `ContentSources` | `security_result.detection_fields[content_sources]` | |
| `ManuallyPaused` | `additional.fields[manually_paused]` | |
| `PreservationPeriodInDays` | `additional.fields[preservation_period_in_days]` | |
| `Reviewers` | `additional.fields[reviewers]` | |
| `SamplingRate` | `additional.fields[sampling_rate]` | |
| `NonCustodianSourceIds` | `additional.fields[non_custodian_source_ids]` | |
| `SettingName` | `additional.fields[setting_name]` | |
| `SettingsNewValue` | `additional.fields[dettings_new_value]` | |
| `AddedRoleAssignment` | `additional.fields[added_role_assignment]` | |
| `NewEnablementState` | `additional.fields[new_enablement_state]` | |
| `URBACWorkload` | `additional.fields[urbac_workload]` | |
| `DeletedRolePermission` | `additional.fields[deleted_role_permission]` | |
| `CommunicationId` | `additional.fields[communication_id]` | |
| `Custodians` | `additional.fields[custodians]` | |
| `UserCancelled` | `additional.fields[user_cancelled]` | |
| `TargetObjectId` | `target.user.attribute.labels[target_object_id]` | |
| `AttackSimAdminEvent` | `additional.fields[attack_sim_admin_event]` | |
| `CampaignType` | `additional.fields[campaign_type]` | |
| `CourseId` | `additional.fields[course_id]` | |
| `Purpose` | `additional.fields[purpose]` | |
| `Sender` | `network.email.from` | |
| `DestFolder.Id` | `target.resource.product_object_id` | |
| `DestFolder.Path` | `target.resource.name` `target.file.full_path` | If the `Workload` log field value is equal to `Exchange` and the `Operation` log field value is `Move`, `MoveToDeletedItems`, `SoftDelete`, or `HardDelete`, then the `DestFolder.Path` log field is also mapped to the `target.file.full_path` UDM field. |
| `OperationProperties` | `security_result.detection_fields[OperationProperties]` | |
| `Members.UserId` | `additional.fields[member_user_id]` | |
| `Members.UserObjectId` | `additional.fields[member_user_object_id]` | |
| `Members.OrganizationId` | `additional.fields[member_organization_id]` | |
| `Members.EmailAddress` | `about.user.email_addresses` | |
| `Members.UPN` | `about.user.email_addresses` `about.user.product_object_id` `about.user.userid` | Iterate for each element `member` in the log field `Members`, then If the `member.UPN` log field value contains an email address, then the `member.UPN` log field value is mapped to the `about.user.email_addresses` UDM field. Otherwise, the `member.UPN` log field value is mapped to the `about.user.product_object_id` UDM field. In addition, the `member.UPN` log field value is mapped to the `about.user.userid` UDM field. |
| `CallId` | `network.session_id` | If the `Workload` log field value is equal to `MicrosoftTeams` and the `Operation` log field value does not contain one of the following values, then the `CallId` log field is mapped to the `network.session_id` UDM field: - `MemberRemoved` - `MemberAdded` - `ChannelAdded` - `ConnectorAdded` - `MemberRoleChanged` - `DeletedAllOrganizationApps` - `TeamDeleted` - `BotRemovedFromTeam` - `ConnectorRemoved` - `ConnectorUpdated` - `ChannelDeleted` - `TabUpdated` - `TabAdded` - `TabRemoved` - `BotAddedToTeam` - `MessageCreatedNotification` - `MessageUpdatedNotification` - `MessageCreatedHasLink` - `MessageEditedHasLink` - `MessagesListed` - `PerformedCardAction` - `MessageSent` - `MessageUpdated` - `MessageReadReceiptReceived` |
| `DeviceInformation` | `principal.asset.attribute.labels[DeviceInformation]` | If the `Workload` log field value is equal to `MicrosoftTeams` and the `Operation` log field value does not contain one of the following values, then the `principal.asset.attribute.labels.key` UDM field is set to `DeviceInformation` and the `DeviceInformation` log field is mapped to the `principal.asset.attribute.labels.value` UDM field: - `MemberRemoved` - `MemberAdded` - `ChannelAdded` - `ConnectorAdded` - `MemberRoleChanged` - `DeletedAllOrganizationApps` - `TeamDeleted` - `BotRemovedFromTeam` - `ConnectorRemoved` - `ConnectorUpdated` - `ChannelDeleted` - `TabUpdated` - `TabAdded` - `TabRemoved` - `BotAddedToTeam` - `MessageCreatedNotification` - `MessageUpdatedNotification` - `MessageCreatedHasLink` - `MessageEditedHasLink` - `MessagesListed` - `PerformedCardAction` - `MessageSent` - `MessageUpdated` - `MessageReadReceiptReceived` |
| `JoinTime` | `additional.fields[JoinTime]` | If the `Workload` log field value is equal to `MicrosoftTeams` and the `Operation` log field value does not contain one of the following values, then the `additional.fields.key` UDM field is set to `JoinTime` and the `JoinTime` log field is mapped to the `additional.fields.value` UDM field: - `MemberRemoved` - `MemberAdded` - `ChannelAdded` - `ConnectorAdded` - `MemberRoleChanged` - `DeletedAllOrganizationApps` - `TeamDeleted` - `BotRemovedFromTeam` - `ConnectorRemoved` - `ConnectorUpdated` - `ChannelDeleted` - `TabUpdated` - `TabAdded` - `TabRemoved` - `BotAddedToTeam` - `MessageCreatedNotification` - `MessageUpdatedNotification` - `MessageCreatedHasLink` - `MessageEditedHasLink` - `MessagesListed` - `PerformedCardAction` - `MessageSent` - `MessageUpdated` - `MessageReadReceiptReceived` |
| `LeaveTime` | `additional.fields[LeaveTime]` | If the `Workload` log field value is equal to `MicrosoftTeams` and the `Operation` log field value does not contain one of the following values, then the `additional.fields.key` UDM field is set to `LeaveTime` and the `LeaveTime` log field is mapped to the `additional.fields.value` UDM field: - `MemberRemoved` - `MemberAdded` - `ChannelAdded` - `ConnectorAdded` - `MemberRoleChanged` - `DeletedAllOrganizationApps` - `TeamDeleted` - `BotRemovedFromTeam` - `ConnectorRemoved` - `ConnectorUpdated` - `ChannelDeleted` - `TabUpdated` - `TabAdded` - `TabRemoved` - `BotAddedToTeam` - `MessageCreatedNotification` - `MessageUpdatedNotification` - `MessageCreatedHasLink` - `MessageEditedHasLink` - `MessagesListed` - `PerformedCardAction` - `MessageSent` - `MessageUpdated` - `MessageReadReceiptReceived` |
| `ObjectId` | `about.resource.product_object_id` | If the `Workload` log field value is equal to `PowerBI`, then the `ObjectId` log field is mapped to the `about.resource.product_object_id` UDM field. |
| `ObjectType` | `about.resource.attribute.labels[ObjectType]` | If the `Workload` log field value is equal to `PowerBI`, then the `about.resource.attribute.labels.key` UDM field is set to `ObjectType` and the `ObjectType` log field is mapped to the `about.resource.attribute.labels.value` UDM field. |
| `WorkspaceId` | `target.resource.product_object_id` | If the `Workload` log field value is equal to `PowerBI`, then the `WorkspaceId` log field is mapped to the `target.resource.product_object_id` UDM field. |
| `WorkspaceName` | `target.resource.attribute.labels[WorkspaceName]` | If the `Workload` log field value is equal to `PowerBI`, then the `target.resource.attribute.labels.key` UDM field is set to `WorkspaceName` and the `WorkspaceName` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `SourceWorkload` | `target.resource.attribute.labels[source_workload]` | If the `SourceWorkload` log field value is equal to `0` then, the `target.resource.attribute.labels[source_workload]` UDM field is set to `SharePoint Online`. Else, if `SourceWorkload` log field value is equal to `1` then, the `target.resource.attribute.labels[source_workload]` UDM field is set to `OneDrive for Business`. Else, if `SourceWorkload` log field value is equal to `3` then, the `target.resource.attribute.labels[source_workload]` UDM field is set to `Microsoft Teams`. |
| `AuthenticationStatus` | `additional.fields[authentication_status]` | If the `AuthenticationStatus` log field value is equal to `0` then, the `additional.fields[authentication_status]` UDM field is set to `Success`. Else, if `AuthenticationStatus` log field value is equal to `1` then, the `additional.fields[authentication_status]` UDM field is set to `Failure`. |
| `UserTrainingEvent` | `principal.user.attribute.labels[user_training_event]` | If the `UserTrainingEvent` log field value is equal to `1` then, the `principal.user.attribute.labels[user_training_event]` UDM field is set to `TrainingAssigned`. Else, if `UserTrainingEvent` log field value is equal to `2` then, the `principal.user.attribute.labels[user_training_event]` UDM field is set to `TrainingUpdated`. Else, if `UserTrainingEvent` log field value is equal to `3` then, the `principal.user.attribute.labels[user_training_event]` UDM field is set to `TrainingCompleted`. Else, if `UserTrainingEvent` log field value is equal to `4` then, the `principal.user.attribute.labels[user_training_event]` UDM field is set to `TrainingPreviouslyAssigned`. Else, if `UserTrainingEvent` log field value is equal to `5` then, the `principal.user.attribute.labels[user_training_event]` UDM field is set to `TrainingNotCompleted`. |
| ParticipantInfo.HasForeignTenantUsers | `security_result.detection_fields.key/value` | |
| ParticipantInfo.HasGuestUsers | `security_result.detection_fields.key/value` | |
| ParticipantInfo.HasOtherGuestUsers | `security_result.detection_fields.key/value` | |
| ParticipantInfo.HasUnauthenticatedUsers | `security_result.detection_fields.key/value` | |
| ParticipantInfo.ParticipatingTenantIds | `security_result.detection_fields.key/value` | |
| Organizer | `principal.user.product_object_id` | |
| EmailInfo.cc | `network.email.cc` | |
| EmailInfo.bcc | `network.email.bcc` | |
| EmailInfo.from | `network.email.from` | |
| EmailInfo.subject | `network.email.subject` | |
| EmailInfo.to | `network.email.to` | |
| DlpAuditEventMetadata.DlpPolicyMatchId | `security_result.detection_fields[DlpPolicyMatchId]` |
| DlpAuditEventMetadata.EvaluationTime | `security_result.detection_fields[DlpAuditEventMetadata_EvaluationTime]` |
| MatchedPolicies.PolicyId | `security_result.detection_fields[MatchedPolicies_PolicyId]` |
| MatchedPolicies.PolicyName | `security_result.detection_fields[MatchedPolicies_PolicyName]` |
| MatchedPolicies.RuleId | `security_result.rule_id` |
| MatchedPolicies.RuleName | `security_result.rule_name` |
| RemovableMediaDeviceAttributes.Manufacturer | `target.asset.hardware.manufacturer ` |
| RemovableMediaDeviceAttributes.Model | `target.asset.hardware.model ` |
| RemovableMediaDeviceAttributes.SerialNumber | `target.asset.hardware.serial_number ` |
| `ExchangeMetaData.Subject` | `network.email.subject` | |
| `PolicyMatchInfo.PolicyId` | `target.resource.product_object_id` | |
| `PolicyMatchInfo.RuleId` | `security_result.rule_id` | |
| `PolicyMatchInfo.RuleName` | `security_result.rule_name` | |
| `PolicyMatchInfo.PolicyName` | `security_result.summary` | |
| `Folder.Id` | `src.resource.product_object_id` | |
| `Folder.Path` | `src.resource.name` `src.file.full_path` | If the `Workload` log field value is equal to `Exchange` and the `Operation` log field value is `Move`, `MoveToDeletedItems`, `SoftDelete`, or `HardDelete`, then the `Folder.Path` log field is also mapped to the `src.file.full_path` UDM field. |
| `Item.Attachments` | `about.file.names` | |
| `Item.ParentFolder.Path` | `target.file.full_path` | |
| `Item.SizeInBytes` | `target.file.size` | |
| `Item.InternetMessageId` | `network.email.id` | |
| `Item.Id` | `additional.fields[item_id]` | |
| `Item.Subject` | `network.email.subject` | |
| `Item.ParentFolder.MemberRights` | `target.resource.attribute.permissions.name` | |
| `Item.ParentFolder.MemberUpn` | `target.user.email_addresses` | |
| ConditionMatch.SensitiveInformation.ClassifierType | `security_result.detection_fields[SensitiveInformation_ClassifierType]` | |
| ConditionMatch.SensitiveInformation.Confidence | `security_result.confidence_details` | |
| ConditionMatch.SensitiveInformation.Count | `security_result.detection_fields[SensitiveInformation_Count]` | |
| ConditionMatch.SensitiveInformation.Id | `security_result.detection_fields[SensitiveInformation_Id]` | |
| `ConditionMatch.SensitiveInformation.Location` | `security_result.detection_fields[SensitiveInformation_Location]` `security_result.detection_fields[SensitiveInfoLocation]` | Iterate for each element in `ConditionMatch.SensitiveInformation`, then the `Location` log field value is mapped to `security_result.detection_fields[SensitiveInformation_Location]` and `security_result.detection_fields[SensitiveInfoLocation]`. |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[SensitiveInformationDetailedClassificationAttributes_Confidence]` | |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[SensitiveInformationDetailedClassificationAttributes_Count]` | |
| `ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch` | `security_result.detection_fields[SensitiveInformationDetailedClassificationAttributes_IsMatch]` `security_result.detection_fields[IsMatch]` | Iterate for each element in `ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes`, then the `IsMatch` log field value is mapped to `security_result.detection_fields[SensitiveInformationDetailedClassificationAttributes_IsMatch]` and `security_result.detection_fields[IsMatch]`. |
| ConditionMatch.SensitiveInformation.UniqueCount | `security_result.detection_fields[SensitiveInformation_UniqueCount]` | |
| DataflowAccessTokenRequestParameters.entityName | `additional.fields[Entity_name]` | |
| DataflowAccessTokenRequestParameters.partitionUri | `additional.fields[Partition URI]` | |
| DataflowAccessTokenRequestParameters.permissions | `additional.fields[Token Permission]` | |
| DataflowAccessTokenRequestParameters.tokenLifetimeInMinutes | `additional.fields[TokenLifetimeInMinutes]` | |
| AuditedArtifactInformation.Name | `target.resource.name` | |
| AuditedArtifactInformation.ArtifactObjectId | `target.resource.product_object_id` | |
| AuditedArtifactInformation.AnnotatedItemType | `target.resource.attribute.labels[AnnotatedItemType]` | |
| PropertyBag.AssessmentStatusPerInitiative.ArnEventId | `additional.fields[ArnEventId]` |
| |
| PropertyBag.AssessmentStatusPerInitiative.CloudProvider | `additional.fields[Cloud_provider]` | |
| PropertyBag.AssessmentStatusPerInitiative.CustomerResourceId | `about.resource.product_object_id` | |
| PropertyBag.AssessmentStatusPerInitiative.EventType | `additional.fields[EventType]` | |
| PropertyBag.AssessmentStatusPerInitiative.PolicyInitiativeId | `additional.fields[PolicyInitiativeId_]` | |
| PropertyBag.AssessmentStatusPerInitiative.PolicyInitiativeName | `additional.fields[PolicyInitiativeName_]` | |
| PropertyBag.AssessmentStatusPerInitiative.ResourceName | `about.resource.name ` | |
| PropertyBag.AssessmentStatusPerInitiative.ResourceType | `about.resource.resource_subtype ` | |
| PropertyBag.AssessmentStatusPerInitiative.SecurityAssessmentId | `additional.fields[SecurityAssessmentId]` | |
| PropertyBag.AssessmentStatusPerInitiative.StatusChangeDate | `additional.fields[StatusChangeDate]` | |
| PropertyBag.AssessmentStatusPerInitiative.StatusCode | `additional.fields[StatusCode]` | |
| PropertyBag.AssessmentStatusPerInitiative.StatusFirstEvaluationDate | `additional.fields[StatusFirstEvaluationDate_]` | |
| PropertyBag.AssessmentStatusPerInitiative.SubscriptionId | `additional.fields[SubscriptionId]` | |
| PropertyBag.AssessmentStatusPerInitiative.SubscriptionName | `additional.fields[SubscriptionName]` | |
| PropertyBag.DataType | `additional.fields[PropertyBag Datatype]` | |
| AggregatedWorkspaceInformation.WorkspaceCount | `additional.fields[workspace_count]` | |
| AggregatedWorkspaceInformation.WorkspacesByCapacitySku | `additional.fields[workspaces_by_capacity_sku]` | |
| AggregatedWorkspaceInformation.WorkspacesByType | `additional.fields[workspaces_type]` | |
| ExchangeDetails.From | `network.email.from` | |
| ExchangeDetails.InternetMessageId | `network.email.mail_id` | |
| ExchangeDetails.Subject | `network.email.subject` | |
| Common.ProcessName | `target.process.command_line` | |
| Common.ApplicationName | `target.resource.name` | |
| Common.ApplicationId | `target.resource.product_object_id` | |
| Common.DeviceName | `target.hostname` | |
| Common.ProductVersion | `metadata.product_version` | |
| PreviousProtectionType.protectionType | `target.resource.attribute.labels[previous_protection_type_protection_type]` | |
| PreviousProtectionType.documentEncrypted | `target.resource.attribute.labels[previous_protection_type_document_encrypted]` | |
| PreviousProtectionType.templateId | `target.resource.attribute.labels[previous_protection_type_template_id]` | |
| PreviousProtectionType.owner | `target.resource.attribute.labels[previous_protection_type_owner]` | |
| CurrentProtectionType.protectionType | `target.resource.attribute.labels[current_protection_type_protection_type]` | |
| CurrentProtectionType.documentEncrypted | `target.resource.attribute.labels[current_protection_type_document_encrypted]` | |
| CurrentProtectionType.templateId | `target.resource.attribute.labels[current_protection_type_template_id]` | |
| CurrentProtectionType.owner | `security_result.about.user.email_addresses` | |
| `PolicyDetails.Rules.Actions` | `additional.fields[Actions]` `security_result.action_details` | Iterate for each key, value pair of log field `PolicyDetails`, then Iterate for each key, value pair of log field `PolicyDetails.Rules`, then Iterate for each key, value pair of log field `PolicyDetails.Rules.Actions`, then `Actions_%{key}` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `Actions_%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `Actions_%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. In addition, each action in `PolicyDetails.Rules.Actions` is mapped to the `security_result.action_details` UDM field. |
| `PolicyDetails.Rules.ActionParameters` | `additional.fields[ActionParameters]` | Iterate for each key, value pair of log field `PolicyDetails`, then Iterate for each key, value pair of log field `PolicyDetails.Rules`, then Iterate for each key, value pair of log field `PolicyDetails.Rules.ActionParameters`, then `ActionParameters_%{key}` log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value`, then `ActionParameters_%{key}%{key1}`*log field is mapped to the `additional.fields.key` UDM field. Iterate for each key, value pair of log field `value1`, then `ActionParameters_%{key}`* `%{key1}_%{key2}` log field is mapped to the `additional.fields.key` UDM field. |
| `PolicyDetails.Rules.ConditionsMatched.DocumentProperties` | `additional.fields[{Name}_%{index}]` | Iterate for log field `PolicyDetails`, then Iterate for log field `PolicyDetails.Rules`, then Iterate for each Name, Value pair of log field `PolicyDetails.Rules.ConditionsMatched.DocumentProperties`, then `{Name}_%{index}` log field is mapped to the `additional.fields.key` UDM field and `%{Value}` log field is mapped to the `additional.fields.value` UDM field. |
| `PolicyDetails.Rules.ConditionsMatched.OtherConditions` | `additional.fields[{Name}_%{index}]` `security_result.detection_fields[%{Name}]` | Iterate for log field `PolicyDetails`, then Iterate for log field `PolicyDetails.Rules`, then Iterate for each Name, Value pair of log field `PolicyDetails.Rules.ConditionsMatched.OtherConditions`, then `%{Name}_%{index}` log field is mapped to the `additional.fields.key` UDM field and `%{Value}` log field is mapped to the `additional.fields.value` UDM field. In addition, the `security_result.detection_fields.key` UDM field is set to `%{Name}` and the `%{Value}` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| PolicyDetails.PolicyVersion | `security_result.detection_fields[policy_details_policy_version]` | Iterate for each key, value pair of log field `PolicyDetails`, then `PolicyVersion` log field value is mapped to `security_result.detection_fields` UDM field. |
| PolicyDetails.Rules.RuleMode | `security_result.detection_fields[policy_details_rules_rules_mode]` | Iterate for each key, value pair of log field `PolicyDetails`, then Iterate for each key, value pair of log field `PolicyDetails.Rules`, then `RuleMode` log field value is mapped to `security_result.detection_fields` UDM field. |
| PolicyDetails.Rules.RuleVersion | `security_result.detection_fields[policy_details_rules_rule_version]` | Iterate for each key, value pair of log field `PolicyDetails`, then Iterate for each key, value pair of log field `PolicyDetails.Rules`, then `RuleVersion` log field value is mapped to `security_result.detection_fields` UDM field. |
| ExchangeMetaData.AttachmentDetails | `target.file.names` | Iterate for each index, attachment pair of log field `ExchangeMetaData.AttachmentDetails`, then `attachment.Name`log field value is mapped to `target.file.names` UDM field. |
| EndpointMetaData | `security_result.action_details` `target.file.size` `target.file.file_type` `additional.fields[EndpointMetaData_FileType]` | Iterate for each Endpointkey, Endpointvalue pair of log field `EndpointMetadata` then If `EndpointKey` is `EnforcementMode` then, if ````` Endpointvalue```` is 1 then, ``` audit``value is mapped to `security_result.action_details` UDM field.`` ``` ```` ````` ``````` `````` Otherwise if ````` Endpointvalue```` is 2 then, ``` warn(block with override)``value is mapped to `security_result.action_details` UDM field. `` ``` ```` ````` `````` ``````` ``````` `````` Otherwise if ````` Endpointvalue```` is 3 then, ``` warn and bypass``value is mapped to `security_result.action_details` UDM field.`` ``` ```` ````` `````` ``````` ``````` `````` Otherwise if ````` Endpointvalue```` is 4 then, ``` block``value is mapped to `security_result.action_details` UDM field.`` ``` ```` ````` `````` ``````` ``````` `````` Otherwise if ````` Endpointvalue```` is 5 then, ``` allow(audit without alerts)``value is mapped to `security_result.action_details` UDM field.`` ``` ```` ````` `````` ``````` ``` `` Otherwise If `EndpointKey` is `FileSize` then, `Endpointvalue` is mapped to the `target.file.size` UDM field. Otherwise If `EndpointKey` is `FileType` then, `Endpointvalue` is mapped to the `target.file.file_type` UDM field. Otherwise `EndpointMetaData_%{index}` value is mapped to the `additional.fields.key` UDM field and `%{Endpointvalue}` field is mapped to the `additional.fields.value` UDM field. Iterate for each Endpointsubkey, Endpointsubvalue pair of log field `Endpointvalue`, then `EndpointMetaData_%{Endpointkey}_%{Endpointsubkey}` value is mapped to the `additional.fields.key` UDM field and `%{Endpointsubvalue}` field is mapped to the `additional.fields.value` UDM field.`` ``` |
| `Common.Location` | `target.location.name` | If the `Workload` log field value is equal to `Aip` and the `Operation` log field value is `FileDeleted`, `Discover`, `SensitivityLabelApplied`, `SensitivityLabelUpdated`, `SensitivityLabelRemoved`, or `ProtectionApplied`, then the `Common.Location` log field is mapped to the `target.location.name` UDM field. |
| `ApplicationName` | `target.application` | If the `Workload` log field value is `Copilot` or `ConnectedAIApp` and the `Operation` log field value is `CopilotInteraction` or `ConnectedAIAppInteraction`, then the `ApplicationName` log field is mapped to the `target.application` UDM field. |
| `ConversationId` | `network.session_id` | If the `Workload` log field value is `Copilot` or `ConnectedAIApp` and the `Operation` log field value is `CopilotInteraction` or `ConnectedAIAppInteraction`, then the `ConversationId` log field is mapped to the `network.session_id` UDM field. |
| `CopilotEventData.ConversationId` | `security_result.detection_fields[ConversationId]` | If the `Workload` log field value is `Copilot` or `ConnectedAIApp` and the `Operation` log field value is `CopilotInteraction` or `ConnectedAIAppInteraction`, then the `security_result.detection_fields.key` UDM field is set to `ConversationId` and the `CopilotEventData.ConversationId` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `CopilotEventData.CorrelationId` | `additional.fields[CorrelationId]` | If the `Workload` log field value is `Copilot` or `ConnectedAIApp` and the `Operation` log field value is `CopilotInteraction` or `ConnectedAIAppInteraction`, then the `additional.fields.key` UDM field is set to `CorrelationId` and the `CopilotEventData.CorrelationId` log field is mapped to the `additional.fields.value.string_value` UDM field. |
| `CopilotEventData.SensitivityLabelId` | `target.resource.attribute.labels[SensitivityLabelId]` | If the `Workload` log field value is `Copilot` or `ConnectedAIApp` and the `Operation` log field value is `CopilotInteraction` or `ConnectedAIAppInteraction`, then the `target.resource.attribute.labels.key` UDM field is set to `SensitivityLabelId` and the `CopilotEventData.SensitivityLabelId` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `CopilotEventData.AccessedResources.listItemUniqueId` | `about.resource.product_object_id` | Iterate for each element in `CopilotEventData.AccessedResources`, then the `listItemUniqueId` log field is mapped to the `about.resource.product_object_id` UDM field. |
| `CopilotEventData.AccessedResources.PolicyDetails.PolicyType` | `security_result.rule_type` | Iterate for each element in `CopilotEventData.AccessedResources` and each element in `PolicyDetails`, then the `PolicyType` log field is mapped to the `security_result.rule_type` UDM field. |
| `CopilotEventData.AccessedResources.PolicyDetails.PolicyOutcomes` | `security_result.action_details` | Iterate for each element in `CopilotEventData.AccessedResources`, each element in `PolicyDetails`, and each element in `PolicyOutcomes`, then the outcome value is mapped to the `security_result.action_details` UDM field. |
| `CopilotEventData.Messages.Id` | `about.resource.product_object_id` | Iterate for each element in `CopilotEventData.Messages`, then the `Id` log field is mapped to the `about.resource.product_object_id` UDM field. |
| `CopilotEventData.Messages.isPrompt` | `security_result.detection_fields[isPrompt]` | Iterate for each element in `CopilotEventData.Messages`, then the `security_result.detection_fields.key` UDM field is set to `isPrompt` and the `isPrompt` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `CopilotEventData.Messages.JailbreakDetected` | `security_result.detection_fields[JailbreakDetected]` | Iterate for each element in `CopilotEventData.Messages`, then the `security_result.detection_fields.key` UDM field is set to `JailbreakDetected` and the `JailbreakDetected` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `CopilotEventData.AISystemPlugin.Id` | `about.resource.product_object_id` | Iterate for each element in `CopilotEventData.AISystemPlugin`, then the `Id` log field is mapped to the `about.resource.product_object_id` UDM field. |
| `CopilotEventData.AISystemPlugin.Name` | `about.resource.name` | Iterate for each element in `CopilotEventData.AISystemPlugin`, then the `Name` log field is mapped to the `about.resource.name` UDM field. |
| `CopilotEventData.ParticipatingAgents.AgentId` | `about.resource.product_object_id` | Iterate for each element in `CopilotEventData.ParticipatingAgents`, then the `AgentId` log field is mapped to the `about.resource.product_object_id` UDM field. |
| `CopilotEventData.ParticipatingAgents.AgentName` | `about.resource.name` | Iterate for each element in `CopilotEventData.ParticipatingAgents`, then the `AgentName` log field is mapped to the `about.resource.name` UDM field. |
| `ItemPropertyBag.LastModifiedDate` | `target.file.last_modification_time` | If the `Workload` log field value is `SharePoint` or `OneDrive` and the `Operation` log field value is equal to `FileRecycled`, then the `ItemPropertyBag.LastModifiedDate` log field is mapped to the `target.file.last_modification_time` UDM field. |
| `Location` | `target.location.name` | If the `Workload` log field value is equal to `DLP` and the `Operation` log field value is `DLPRuleMatch` or `DlpRuleMatch`, then the `Location` log field is mapped to the `target.location.name` UDM field. |
| `ItemMetadata.Id` | `target.resource.product_object_id` | If the `Workload` log field value is equal to `DLP` and the `Operation` log field value is `DLPRuleMatch` or `DlpRuleMatch`, then the `ItemMetadata.Id` log field is mapped to the `target.resource.product_object_id` UDM field. |
| `ItemMetadata.Name` | `target.resource.name` | If the `Workload` log field value is equal to `DLP` and the `Operation` log field value is `DLPRuleMatch` or `DlpRuleMatch`, then the `ItemMetadata.Name` log field is mapped to the `target.resource.name` UDM field. |
| `ItemMetadata.Path` | `target.file.full_path` | If the `Workload` log field value is equal to `DLP` and the `Operation` log field value is `DLPRuleMatch` or `DlpRuleMatch`, then the `ItemMetadata.Path` log field is mapped to the `target.file.full_path` UDM field. |
| `ItemMetadata.CorrelationId` | `additional.fields[ItemMetadata.CorrelationId]` | If the `Workload` log field value is equal to `DLP` and the `Operation` log field value is `DLPRuleMatch` or `DlpRuleMatch`, then the `additional.fields.key` UDM field is set to `ItemMetadata.CorrelationId` and the `ItemMetadata.CorrelationId` log field is mapped to the `additional.fields.value.string_value` UDM field. |
| `SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence` | `security_result.detection_fields[Confidence]` | Iterate for each element in `SensitiveInfoTypeData` and each element in `SensitiveInformationDetailedClassificationAttributes`, then the `security_result.detection_fields.key` UDM field is set to `Confidence` and the `Confidence` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count` | `security_result.detection_fields[Count]` | Iterate for each element in `SensitiveInfoTypeData` and each element in `SensitiveInformationDetailedClassificationAttributes`, then the `security_result.detection_fields.key` UDM field is set to `Count` and the `Count` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch` | `security_result.detection_fields[IsMatch]` | Iterate for each element in `SensitiveInfoTypeData` and each element in `SensitiveInformationDetailedClassificationAttributes`, then the `security_result.detection_fields.key` UDM field is set to `IsMatch` and the `IsMatch` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `ConditionMatch.OtherConditions` | `security_result.detection_fields[%{Name}]` | Iterate for each `Name`, `Value` pair in `ConditionMatch.OtherConditions`, then the `security_result.detection_fields.key` UDM field is set to `%{Name}` and the `%{Value}` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PolicyDetails.Rules.OverriddenActions` | `security_result.action_details` | Iterate for each element in `PolicyDetails`, each element in `Rules`, and each element in `OverriddenActions`, then the overridden action value is mapped to the `security_result.action_details` UDM field. |
| `PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType` | `security_result.detection_fields[SensitiveType]` | Iterate for each element in `PolicyDetails`, each element in `Rules`, and each element in `ConditionsMatched.SensitiveInformation`, then the `security_result.detection_fields.key` UDM field is set to `SensitiveType` and the `SensitiveType` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location` | `security_result.detection_fields[SensitiveInfoLocation]` | Iterate for each element in `PolicyDetails`, each element in `Rules`, and each element in `ConditionsMatched.SensitiveInformation`, then the `security_result.detection_fields.key` UDM field is set to `SensitiveInfoLocation` and the `Location` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch` | `security_result.detection_fields[IsMatch]` | Iterate for each element in `PolicyDetails`, each element in `Rules`, each element in `ConditionsMatched.SensitiveInformation`, and each element in `SensitiveInformationDetailedClassificationAttributes`, then the `security_result.detection_fields.key` UDM field is set to `IsMatch` and the `IsMatch` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues` | `security_result.detection_fields[%{Name}]` | Iterate for each element in `PolicyDetails`, each element in `Rules`, each element in `ConditionsMatched.SensitiveInformation`, and each `Name`, `Value` pair in `SensitiveInformationDetections.DetectedValues`, then the `security_result.detection_fields.key` UDM field is set to `%{Name}` and the `%{Value}` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated` | `security_result.detection_fields[ResultsTruncated]` | Iterate for each element in `PolicyDetails`, each element in `Rules`, and each element in `ConditionsMatched.SensitiveInformation`, then the `security_result.detection_fields.key` UDM field is set to `ResultsTruncated` and the `SensitiveInformationDetections.ResultsTruncated` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence` | `security_result.detection_fields[Confidence]` | If the `Workload` log field value is equal to `Endpoint` and the `Operation` log field value is `DlpRuleMatch` or `DLPRuleMatch`, then iterate for each element in `EndpointMetaData.SensitiveInfoTypeData` and each element in `SensitiveInformationDetailedClassificationAttributes`, where the `security_result.detection_fields.key` UDM field is set to `Confidence` and the `Confidence` log field is mapped to the `security_result.detection_fields.value` UDM field. |
| `EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetectionsInfo.DetectedValues` | `security_result.detection_fields[%{Name}]` | If the `Workload` log field value is equal to `Endpoint` and the `Operation` log field value is `DlpRuleMatch` or `DLPRuleMatch`, then iterate for each element in `EndpointMetaData.SensitiveInfoTypeData` and each `Name`, `Value` pair in `SensitiveInformationDetectionsInfo.DetectedValues`, where the `security_result.detection_fields.key` UDM field is set to `%{Name}` and the `%{Value}` log field is mapped to the `security_result.detection_fields.value` UDM field. |
For reference information about UDM mappings for supported operations, refer to
the following sections:
### FileAccessed
The following table lists the log fields and corresponding UDM mappings for the operation "Fileaccessed" and workload "SharePoint" or "OneDrive":
`UrlClickAction``5`
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| FileSizeBytes | `target.file.size` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileAccessedExtended
The following table lists the log fields and corresponding UDM mappings for the operation "FileAccessedExtended" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "FileDeleted" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| Common.Location | `target.location.name` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### FileCopied
The following table lists the log fields and corresponding UDM mappings for the operation "FileCopied" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_COPY target.resource.resource_type is set to STORAGE_OBJECT |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | `target.url` If the `EventData` log field is not `empty`, the extracted `target_url` field from `EventData` is mapped to the `target.url` UDM field. |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileModified
The following table lists the log fields and corresponding UDM mappings for the operation "FileModified" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_MODIFICATION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| FileSizeBytes | `target.file.size` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### FileDownloaded
The following table lists the log fields and corresponding UDM mappings for the operation "FileDownloaded" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED target.resource.resource_type is set to STORAGE_OBJECT ObjectId is set to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| UserSessionId | `network.http.session_id` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| ZipFileName | `target.file.names` The `ZipFileName` log field is mapped to the `target.file.names` UDM field. |
### FileModifiedExtended
The following table lists the log fields and corresponding UDM mappings for the operation "FileModifiedExtended" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_MODIFICATION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| FileSizeBytes | `target.file.size` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` |
### FileMoved
The following table lists the log fields and corresponding UDM mappings for the operation "FileMoved" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED target.resource.resource_type is set to STORAGE_OBJECT ObjectId is set to src.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| DestinationRelativeUrl | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileName | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileExtension | `target.file.mime_type` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FilePreviewed
The following table lists the log fields and corresponding UDM mappings for the operation "FilePreviewed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileRenamed
The following table lists the log fields and corresponding UDM mappings for the operation "FileRenamed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_MOVE target.resource.resource_type is set to STORAGE_OBJECT ObjectId is set to src.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| DestinationRelativeUrl | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileName | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileExtension | `target.file.mime_type` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### FileUploaded
The following table lists the log fields and corresponding UDM mappings for the operation "FileUploaded" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| ImplicitShare | `target.resource.attribute.labels.key/value` |
### FileVersionsAllDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "FileVersionsAllDeleted" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### FileCheckedIn
The following table lists the log fields and corresponding UDM mappings for the operation "FileCheckedIn" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_MODIFICATION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | workload map with intermediary.application |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileCheckedOut
The following table lists the log fields and corresponding UDM mappings for the operation "FileCheckedOut" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | Uniquely Identify resource in site like File or Folder |
| ItemType | This field contain values like File, Folder, Web, Site, Tenant, and DocumentLibrary |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | Information about the user's browser. This information is provided by the browser. |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | We can not map it with target.file.full_path because of SiteUrl field not contains value related to system path |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### ComplianceSettingChanged
The following table lists the log fields and corresponding UDM mappings for the operation "ComplianceSettingChanged" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
### LockRecord
The following table lists the log fields and corresponding UDM mappings for the operation "LockRecord" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### UnlockRecord
The following table lists the log fields and corresponding UDM mappings for the operation "UnlockRecord" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileDeletedFirstStageRecycleBin
The following table lists the log fields and corresponding UDM mappings for the operation "FileDeletedFirstStageRecycleBin" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileDeletedSecondStageRecycleBin
The following table lists the log fields and corresponding UDM mappings for the operation "FileDeletedSecondStageRecycleBin" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### RecordDelete
The following table lists the log fields and corresponding UDM mappings for the operation "RecordDelete" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### DocumentSensitivityMismatchDetected
The following table lists the log fields and corresponding UDM mappings for the operation "DocumentSensitivityMismatchDetected" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### DocumentSensitivityMismatchDetected
The following table lists the log fields and corresponding UDM mappings for the operation "DocumentSensitivityMismatchDetected" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileCheckOutDiscarded
The following table lists the log fields and corresponding UDM mappings for the operation "FileCheckOutDiscarded" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileVersionsAllMinorsRecycled
The following table lists the log fields and corresponding UDM mappings for the operation "FileVersionsAllMinorsRecycled" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileVersionsAllRecycled
The following table lists the log fields and corresponding UDM mappings for the operation "FileVersionsAllRecycled" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileVersionRecycled
The following table lists the log fields and corresponding UDM mappings for the operation "FileVersionRecycled" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileRestored
The following table lists the log fields and corresponding UDM mappings for the operation "FileRestored" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_MOVE target.resource.resource_type is set to STORAGE_OBJECT ObjectId is set to src.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| DestinationRelativeUrl | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileName | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileExtension | `target.file.mime_type` |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileMalwareDetected
The following table lists the log fields and corresponding UDM mappings for the operation "FileMalwareDetected" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCAN_UNCATEGORIZED target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| VirusInfo | `security_result.threat_name` |
| VirusVendor | `security_result.threat_feed_name` |
| VirusVendor | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### SearchQueryPerformed
The following table lists the log fields and corresponding UDM mappings for the operation "SearchQueryPerformed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT target.resource.resource_type is set to STORAGE_OBJECT |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SearchQueryText | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| EventData | `additional.fields[client_type]` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### PageViewed
The following table lists the log fields and corresponding UDM mappings for the operation "PageViewed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### PagePrefetched
The following table lists the log fields and corresponding UDM mappings for the operation "PagePrefetched" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### ClientViewSignaled
The following table lists the log fields and corresponding UDM mappings for the operation "ClientViewSignaled" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url NOTE: Because ClientViewSignaled events are signaled by the client, rather than the server, it's possible the event may not be logged by the server and therefore may not appear in the audit log. It's also possible that information in the audit record may not be trustworthy. However, because the user's identity is validated by the token used to create the signal, the user's identity listed in the corresponding audit record is accurate. |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### PageViewedExtended
The following table lists the log fields and corresponding UDM mappings for the operation "PageViewedExtended" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### FolderCreated
The following table lists the log fields and corresponding UDM mappings for the operation "FolderCreated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FolderDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "FolderDeleted" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FolderMoved
The following table lists the log fields and corresponding UDM mappings for the operation "FolderMoved" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_MOVE target.resource.resource_type is set to STORAGE_OBJECT |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} SourceRelativeUrl field not getting in log |
| DestinationRelativeUrl | DestinationRelativeUrl field not getting in log target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileName | DestinationFileName field not getting in log target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileExtension | `target.file.mime_type` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | `target.url` If the `EventData` log field is not `empty`, the extracted `target_url` field from `EventData` is mapped to the `target.url` UDM field. |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FolderRenamed
The following table lists the log fields and corresponding UDM mappings for the operation "FolderRenamed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_MOVE |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| DestinationRelativeUrl | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileName | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileExtension | `target.file.mime_type` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FolderModified
The following table lists the log fields and corresponding UDM mappings for the operation "FolderModified" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FolderCopied
The following table lists the log fields and corresponding UDM mappings for the operation "FolderCopied" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_COPY target.resource.resource_type is set to STORAGE_OBJECT ObjectId is set to src.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | `src.file.full_path` |
| SourceRelativeUrl | `src.file.full_path` |
| DestinationRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| DestinationFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| DestinationFileExtension | `target.file.mime_type` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FolderRestored
The following table lists the log fields and corresponding UDM mappings for the operation "FolderRestored" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED target.resource.resource_type is set to STORAGE_OBJECT ObjectId is set to src.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| DestinationRelativeUrl | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileName | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileExtension | `target.file.mime_type` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FolderDeletedFirstStageRecycleBin
The following table lists the log fields and corresponding UDM mappings for the operation "FolderDeletedFirstStageRecycleBin" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FolderDeletedSecondStageRecycleBin
The following table lists the log fields and corresponding UDM mappings for the operation "FolderDeletedSecondStageRecycleBin" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileSyncDownloadedFull
The following table lists the log fields and corresponding UDM mappings for the operation "FileSyncDownloadedFull" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED ObjectId is set to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| FileSyncBytesCommitted | `target.file.size` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileSyncDownloadedPartial
The following table lists the log fields and corresponding UDM mappings for the operation "FileSyncDownloadedPartial" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| FileSyncBytesCommitted | `target.file.size` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileSyncUploadedFull
The following table lists the log fields and corresponding UDM mappings for the operation "FileSyncUploadedFull" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| FileSyncBytesCommitted | `target.file.size` |
| ImplicitShare | `target.resource.attribute.labels.key/value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### FileSyncUploadedPartial
The following table lists the log fields and corresponding UDM mappings for the operation "FileSyncUploadedPartial" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| FileSizeBytes | `target.file.size` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| FileSyncBytesCommitted | `target.file.size` |
| ImplicitShare | `target.resource.attribute.labels.key/value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### ManagedSyncClientAllowed
The following table lists the log fields and corresponding UDM mappings for the operation "ManagedSyncClientAllowed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZED |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| Site | `target.resource.product_object_id` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `about.resource.product_object_id` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| AppAccessContext.UserObjectId | `principal.user.product_object_id` |
### UnmanagedSyncClientBlocked
The following table lists the log fields and corresponding UDM mappings for the operation "UnmanagedSyncClientBlocked" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZED |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### AddedToGroup
The following table lists the log fields and corresponding UDM mappings for the operation "AddedToGroup" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is mapped to target.url |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| EventData | `target.group.group_display_name` |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### GroupAdded
The following table lists the log fields and corresponding UDM mappings for the operation "GroupAdded" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_CREATION ObjectId is mapped to target.url |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ModifiedProperties | if Name is Name then NewValue is mapped to target.group.group_display_name |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### GroupRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "GroupRemoved" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ModifiedProperties | if Name is Name then NewValue is mapped to target.group.group_display_name |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### WebRequestAccessModified
The following table lists the log fields and corresponding UDM mappings for the operation "WebRequestAccessModified" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ModifiedProperties | If the `Name` log field value is equal to `RequestAccessEmail`, then the `NewValue` log field is mapped to the `target.user.email_addresses` or `target.user.userid` UDM field. Else, the `NewValue` log field is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| ItemType | `target.resource.attribute.labels.key/value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### WebMembersCanShareModified
The following table lists the log fields and corresponding UDM mappings for the operation "WebMembersCanShareModified" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS ObjectId is mapped to target.url |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| version | `metadata.product_version` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### PermissionLevelModified
The following table lists the log fields and corresponding UDM mappings for the operation "PermissionLevelModified" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ModifiedProperties | `target.resource.attribute.labels[Action Client Name]`
Iterate for each element `field` in the `ModifiedProperties` log field array, then If the `field.Name` value is equal to `Action Client Name` then, the `target.resource.attribute.labels.key` UDM field is set to `Action Client Name` and the `field.NewValue` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| version | `metadata.product_version` |
| WebID | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### SiteCollectionAdminAdded
The following table lists the log fields and corresponding UDM mappings for the operation "SiteCollectionAdminAdded" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| ModifiedProperties | If Name is set SiteAdmin then NewValue is mapped to target.user.userid or target.user.email_addresses |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### SiteCollectionAdminRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "SiteCollectionAdminRemoved" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| ModifiedProperties | If Name is set SiteAdmin then NewValue is mapped to target.user.userid or target.user.email_addresses |
| AssertingApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### PermissionLevelRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "PermissionLevelRemoved" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | `target.resource.attribute.permissions.name` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### RemovedFromGroup
The following table lists the log fields and corresponding UDM mappings for the operation "RemovedFromGroup" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | `target.group.group_display_name` |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### GroupUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "GroupUpdated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.referral_url` |
| ModifiedProperties | if Name is Name then NewValue is mapped to target.group.group_display_name |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### ProjectCheckedOut
The following table lists the log fields and corresponding UDM mappings for the operation "ProjectCheckedOut" and workload "Project":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| ItemType | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Entity | `metadata.product_name` |
| Version | `metadata.product_version` |
| Action | `security_result.action_details` If `Action` is equal to `Accepted` then, the UDM field `security_result.action_details` is set to "Accepted - The user accepted an event or workflow." Else if `Action` is equal to `Accessed` then, the UDM field `security_result.action_details` is set to "Accessed - The user accessed an entity." Else if `Action` is equal to `Activated` then, the UDM field `security_result.action_details` is set to "Activated - The user activated an entity, event or workflow." Else if `Action` is equal to `Cancelled` then, the UDM field `security_result.action_details` is set to "Cancelled - The user cancelled an event or workflow." Else if `Action` is equal to `CheckedIn` then, the UDM field `security_result.action_details` is set to "CheckedIn - The user check in an entity." Else if `Action` is equal to `CheckedOut` then, the UDM field `security_result.action_details` is set to "CheckedOut - The user checkout an entity." Else if `Action` is equal to `Copied` then, the UDM field `security_result.action_details` is set to "Copied - The user copied an entity." Else if `Action` is equal to `Created` then, the UDM field `security_result.action_details` is set to "Created - The user created an entity." Else if `Action` is equal to `Deactivated` then, the UDM field `security_result.action_details` is set to "Deactivated - The user deactivated an entity." Else if `Action` is equal to `Deleted` then, the UDM field `security_result.action_details` is set to "Deleted - The user deleted an entity." Else if `Action` is equal to `Exported` then, the UDM field `security_result.action_details` is set to "Exported - The user exported an entity." Else if `Action` is equal to `ForceCheckedIn` then, the UDM field `security_result.action_details` is set to "ForceCheckedIn - The user caused an entity to be force checked in." Else if `Action` is equal to `Modified` then, the UDM field `security_result.action_details` is set to "Modified - The user modified an entity." Else if `Action` is equal to `Published` then, the UDM field `security_result.action_details` is set to "Published - The user published an entity." Else if `Action` is equal to `Redacted` then, the UDM field `security_result.action_details` is set to "Redacted - The user redacted an entity." Else if `Action` is equal to `Rejected` then, the UDM field `security_result.action_details` is set to "Rejected - The user rejected an entity." Else if `Action` is equal to `Restarted` then, the UDM field `security_result.action_details` is set to "Restarted - The user restarted an event or workflow." Else if `Action` is equal to `Saved` then, the UDM field `security_result.action_details` is set to "Saved - The user saved an entity." Else if `Action` is equal to `Sent` then, the UDM field `security_result.action_details` is set to "Sent - The user sent an entity." Else if `Action` is equal to `Submitted` then, the UDM field `security_result.action_details` is set to "Submitted - The user submitted an entity for review or workflow." |
| OnBehalfOfResId | `additional.fields.key` and `additional.fields.value.string_value` |
### ProjectAccessed
The following table lists the log fields and corresponding UDM mappings for the operation "ProjectAccessed" and workload "Project":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT |
| ItemType | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Entity | `metadata.product_name` |
| Version | `metadata.product_version` |
| Action | `security_result.action_details` If `Action` is equal to `Accepted` then, the UDM field `security_result.action_details` is set to "Accepted - The user accepted an event or workflow." Else if `Action` is equal to `Accessed` then, the UDM field `security_result.action_details` is set to "Accessed - The user accessed an entity." Else if `Action` is equal to `Activated` then, the UDM field `security_result.action_details` is set to "Activated - The user activated an entity, event or workflow." Else if `Action` is equal to `Cancelled` then, the UDM field `security_result.action_details` is set to "Cancelled - The user cancelled an event or workflow." Else if `Action` is equal to `CheckedIn` then, the UDM field `security_result.action_details` is set to "CheckedIn - The user check in an entity." Else if `Action` is equal to `CheckedOut` then, the UDM field `security_result.action_details` is set to "CheckedOut - The user checkout an entity." Else if `Action` is equal to `Copied` then, the UDM field `security_result.action_details` is set to "Copied - The user copied an entity." Else if `Action` is equal to `Created` then, the UDM field `security_result.action_details` is set to "Created - The user created an entity." Else if `Action` is equal to `Deactivated` then, the UDM field `security_result.action_details` is set to "Deactivated - The user deactivated an entity." Else if `Action` is equal to `Deleted` then, the UDM field `security_result.action_details` is set to "Deleted - The user deleted an entity." Else if `Action` is equal to `Exported` then, the UDM field `security_result.action_details` is set to "Exported - The user exported an entity." Else if `Action` is equal to `ForceCheckedIn` then, the UDM field `security_result.action_details` is set to "ForceCheckedIn - The user caused an entity to be force checked in." Else if `Action` is equal to `Modified` then, the UDM field `security_result.action_details` is set to "Modified - The user modified an entity." Else if `Action` is equal to `Published` then, the UDM field `security_result.action_details` is set to "Published - The user published an entity." Else if `Action` is equal to `Redacted` then, the UDM field `security_result.action_details` is set to "Redacted - The user redacted an entity." Else if `Action` is equal to `Rejected` then, the UDM field `security_result.action_details` is set to "Rejected - The user rejected an entity." Else if `Action` is equal to `Restarted` then, the UDM field `security_result.action_details` is set to "Restarted - The user restarted an event or workflow." Else if `Action` is equal to `Saved` then, the UDM field `security_result.action_details` is set to "Saved - The user saved an entity." Else if `Action` is equal to `Sent` then, the UDM field `security_result.action_details` is set to "Sent - The user sent an entity." Else if `Action` is equal to `Submitted` then, the UDM field `security_result.action_details` is set to "Submitted - The user submitted an entity for review or workflow." |
| OnBehalfOfResId | `additional.fields.key` and `additional.fields.value.string_value` |
### SharingInheritanceBroken
The following table lists the log fields and corresponding UDM mappings for the operation "SharingInheritanceBroken" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
### AddedToSecureLink
The following table lists the log fields and corresponding UDM mappings for the operation "AddedToSecureLink" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventData | target.resource.attribute.labels.key/value Extract using grok grok { match is mapped to { EventData \{type_value}\\{members_share_value}\ } } Type is mapped to target.resource.attribute.labels.key/value MembersCanShareApplied is mapped to target.resource.attribute.labels.key/value |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ApplicationDisplayName | `target.application` |
### CompanyLinkCreated
The following table lists the log fields and corresponding UDM mappings for the operation "CompanyLinkCreated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
### CompanyLinkUsed
The following table lists the log fields and corresponding UDM mappings for the operation "CompanyLinkUsed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### SecureLinkCreated
The following table lists the log fields and corresponding UDM mappings for the operation "SecureLinkCreated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
### SharingInvitationCreated
The following table lists the log fields and corresponding UDM mappings for the operation "SharingInvitationCreated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | target.resource.attribute.labels.key/value Sharing level is mapped to target.resource.attribute.labels.key/value ExpirationDate is mapped totarget.resource.attribute.labels.key/value MembersCanShareApplied is mapped to target.resource.attribute.labels.key/value |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
### SecureLinkDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "SecureLinkDeleted" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | target.resource.attribute.labels.key/value Extract using grok grok { match is mapped to { EventData \{type_value}\ } } Type is mapped to target.resource.attribute.labels.key/value |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| ApplicationDisplayName | `target.application` |
### RemovedFromSecureLink
The following table lists the log fields and corresponding UDM mappings for the operation "RemovedFromSecureLink" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | target.resource.attribute.labels.key/value Extract using grok grok { match is mapped to { EventData \{type_value}\\{members_share_value}\ } } Type is mapped to target.resource.attribute.labels.key/value MembersCanShareApplied is mapped to target.resource.attribute.labels.key/value |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
### SharingInvitationRevoked
The following table lists the log fields and corresponding UDM mappings for the operation "SharingInvitationRevoked" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
### SecureLinkUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "SecureLinkUpdated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | target.resource.attribute.labels.key/value Extract using grok grok { match is mapped to { EventData \{type_value}\\{members_share_value}\ } } Type is mapped to target.resource.attribute.labels.key/value MembersCanShareApplied is mapped to target.resource.attribute.labels.key/value |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
### SecureLinkUsed
The following table lists the log fields and corresponding UDM mappings for the operation "SecureLinkUsed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### SharingRevoked
The following table lists the log fields and corresponding UDM mappings for the operation "SharingRevoked" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS target.resource.resource_type is set to STORAGE_OBJECT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### SharingSet
The following table lists the log fields and corresponding UDM mappings for the operation "SharingSet" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
### PermissionLevelAdded
The following table lists the log fields and corresponding UDM mappings for the operation "PermissionLevelAdded" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | target.resource.attribute.permissions.name BasePermissions is mapped to target.resource.attribute.permissions.name |
### SharingInvitationAccepted
The following table lists the log fields and corresponding UDM mappings for the operation "SharingInvitationAccepted" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | `target.group.group_display_name` If `EventData` is not `empty`, the extracted `target_group_display_name` field from `EventData` is mapped to the `target.group.group_display_name` UDM field. |
### SharingInvitationBlocked
The following table lists the log fields and corresponding UDM mappings for the operation "SharingInvitationBlocked" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| EventData | security_result.summary Reason is mapped to security_result.summary |
### AccessRequestCreated
The following table lists the log fields and corresponding UDM mappings for the operation "AccessRequestCreated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| EventData | target.resource.attribute.labels.key/value Sharing level is mapped to target.resource.attribute.labels.key/value ExpirationDate is mapped totarget.resource.attribute.labels.key/value |
### AnonymousLinkCreated
The following table lists the log fields and corresponding UDM mappings for the operation "AnonymousLinkCreated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | target.resource.attribute.labels.key/value Extract using grok grok { match is mapped to { EventData \{type_value}\\{members_share_value}\ } } Type is mapped to target.resource.attribute.labels.key/value MembersCanShareApplied is mapped to target.resource.attribute.labels.key/value |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
### AccessRequestUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "AccessRequestUpdated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
### CompanyLinkRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "CompanyLinkRemoved" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | target.resource.attribute.labels.key/value Extract using grok grok { match is mapped to { EventData \{type_value}\ } } Type is mapped to target.resource.attribute.labels.key/value |
### AccessRequestApproved
The following table lists the log fields and corresponding UDM mappings for the operation "AccessRequestApproved" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | `target.group.group_display_name` If `EventData` is not `empty`, the extracted `target_group_display_name` field from `EventData` is mapped to the `target.group.group_display_name` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
### AnonymousLinkRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "AnonymousLinkRemoved" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | `target.resource.attribute.labels.key/value` |
| SourceFileExtension | `target.file.mime_type` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | network.http.referral_url Extract using grok grok { match is mapped to { EventData \{type_value}\ } } Type is mapped to target.resource.attribute.labels.key/value |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
### AnonymousLinkUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "AnonymousLinkUpdated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| ApplicationDisplayName | `target.application` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | target.resource.attribute.labels.key/value Extract using grok grok { match is mapped to { EventData \{type_value}\\{members_share_value}\ } } Type is mapped to target.resource.attribute.labels.key/value MembersCanShareApplied is mapped to target.resource.attribute.labels.key/value |
### SharingInvitationUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "SharingInvitationUpdated" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SiteUrl | `target.url_metadata.url` |
| ApplicationDisplayName | `target.application` |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| | event_type is mapped to USER_RESOURCE_ACCESS |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| TargetUserOrGroupName | target.group.group_display_name target.user.userid or target.user.email_addresses if TargetUserOrGroupType values like SecurityGroup or SharepointGroup then TargetUserOrGroupName is mapped to target.group.group_display_name if TargetUserOrGroupType values like Guest or Member then TargetUserOrGroupName is mapped to target.user.userid or target.user.email_addresses |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| SourceRelativeUrl | target.file.full_path is set to SourceRelativeUrl or SourceFileName |
| ApplicationDisplayName | `target.application` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### AnonymousLinkUsed
The following table lists the log fields and corresponding UDM mappings for the operation "AnonymousLinkUsed" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_CREATION ResultStatus is Success Action is set to ALLOW security_result.summary is set to Group creation successful ResultStatus is Failure Action is set to BLOCK security_result.summary is set to Group creation failed |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.group.group_display_name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 1 then ID is mapped to target.group.group_display_name If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add group
The following table lists the log fields and corresponding UDM mappings for the operation "Add group" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ResultStatus is Success then Action is set to ALLOW security_result.summary is set to Group membership updated successfully ResultStatus is Failure then Action is set to BLOCK security_result.summary is set toGroup membership update failed |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.group.product.object_id target.group.group_display_name Group.ObjectId is mapped to target.group.product.object_id Group.DisplayName is mapped to target.group.group_display_name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add member to group
The following table lists the log fields and corresponding UDM mappings for the operation "Add member to group" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_CREATION` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `target.resource.name` If `Name` is `Included Updated Properties` then `NewValue` is mapped to `security_result.summary` If `Name` is `Action Client Name` then `NewValue` is mapped to `target.resource.name` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | `principal.ip and principal.port` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `target.user.userid` or `target.user.email_addresses` `security_result.detection_fields.key/value` If `Type` is 5 then `ID` is mapped to `target.user.userid` or `target.user.email_addresses` else `security_result.detection_fields.key/value` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add user
The following table lists the log fields and corresponding UDM mappings for the operation `Add user` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_PERMISSIONS` |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `target.resource.name` If `Name` is `Included Updated Properties` then `NewValue` is mapped to `security_result.summary` If `Name` is `Action Client Name` then `NewValue` is mapped to `target.resource.name` If `Name` is `Is HardDeleted` then `NewValue` and `OldValue` is mapped to `security_result.detection_fields.key/value` If `Name` is `GivenName` then `NewValue` and `OldValue` is mapped to `target.user.attribute.labels.key/value` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| Target | `target.user.userid or target.user.email_addresses` `security_result.detection_fields.key/value` If `Type` is 5 then `ID` is mapped to `target.user.userid` or `target.user.email_addresses` else `security_result.detection_fields.key/value` |
| Target.1.ID | `target.user.product_object_id` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Change user license.
The following table lists the log fields and corresponding UDM mappings for the operation "Change user license." and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary If Name is Action Client Name then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Change user password
The following table lists the log fields and corresponding UDM mappings for the operation "Change user password" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_DELETION ResultStatus is Success then Action is set to ALLOW security_result.summary is set to Group deletion successful ResultStatus is Failure then Action is set to BLOCK security_result.summary is set to Group deletion failed |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary additional.fields.key and additional.fields.value.struct_value.fields If Name is Included Updated Properties then NewValue is mapped to security_result.summary else additional.fields.key and additional.fields.value.struct_value.fields |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.group.group_display_name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 1 then ID is mapped to target.group.group_display_name If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Delete group
The following table lists the log fields and corresponding UDM mappings for the operation "Delete group" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ResultStatus is Success then Action is set to ALLOW security_result.summary is set to Group membership updated successfully ResultStatus is Failure then Action is set to BLOCK security_result.summary is set to Group membership update failed |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.group.product.object_id target.group.group_display_name Group.ObjectId is mapped to target.group.product.object_id Group.DisplayName is mapped to target.group.group_display_name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Remove member from group
The following table lists the log fields and corresponding UDM mappings for the operation "Remove member from group" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_DELETION if status is Success then action ALLOW security_result.summary User deleted successfully |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary If Name is Action Client Name then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Delete user
The following table lists the log fields and corresponding UDM mappings for the operation `Delete user` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_UNCATEGORIZED` `ResultStatus` is `Success` `Action` is set to `ALLOW` `security_result.summary` is `User updated successfully` `ResultStatus` is `Failure` `Action` is set to `BLOCK` `security_result.summary` is `User update failed` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `target.resource.name` If `Name` is `Included Updated Properties` then `NewValue` is mapped to `security_result.summary` If `Name` is `Action Client Name` then `NewValue` is mapped to `target.resource.name` If `Name` is `HardDeleted` then `NewValue` and `OldValue` is mapped to `security_result.detection_fields.key/value` If `Name` is `GivenName` then `NewValue` and `OldValue` is mapped to `target.user.attribute.labels.key/value` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | `principal.ip and principal.port` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `target.user.userid` or `target.user.email_addresses` `security_result.detection_fields.key/value` If `Type` is 5 then `ID` is mapped to `target.user.userid` or `target.user.email_addresses` else `security_result.detection_fields.key/value` |
| Target.1.ID | `target.user.product_object_id` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Update user
The following table lists the log fields and corresponding UDM mappings for the operation `Update user` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type is mapped to GROUP_MODIFICATION` if `ObjectId` not contain (empty) or `Not Available` then `ObjectId` is set to `target.group.product_object_id` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| `ModifiedProperties` | `security_result.detection_fields.key/value` `target.resource.name` If `Name` is `Included Updated Properties` then `NewValue` is mapped to `security_result.detection_fields.key/value` If `Name` is `Action Client Name` then `NewValue` is mapped to `target.resource.name` If `Name` is `HardDeleted` then `NewValue` and `OldValue` is mapped to `security_result.detection_fields.key/value` If `Name` is `GivenName` then `NewValue` and `OldValue` is mapped to `target.user.attribute.labels.key/value` If the `Name` log field value is equal to `TargetId.UserType`, then the `NewValue` and `Oldvalue` log fields are mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. If `Name` is `StrongAuthenticationPhoneAppDetail` then from `NewValue`, `DeviceName` is mapped to `target.asset.hostname`, `PhoneAppVersion` is mapped to `target.asset.software.version`, `DeviceId` is mapped to `target.asset.asset_id`, `Id` is mapped to `target.asset.product_object_id`, `DeviceToken ` is mapped to `target.asset.attribute.labels.key/value`, `DeviceTag ` is mapped to `target.asset.attribute.labels.key/value`, `OathTokenTimeDrift ` is mapped to `security_result.detection_fields.key/value`, `TimeInterval ` is mapped to `security_result.detection_fields.key/value`, `AuthenticationType ` is mapped to `security_result.detection_fields.key/value`, `NotificationType ` is mapped to `target.asset.attribute.labels.key/value`, `LastAuthenticatedTimestamp ` is mapped to `security_result.detection_fields.key/value`, `AuthenticatorFlavor ` is mapped to `security_result.detection_fields.key/value`, `HashFunction ` is mapped to `security_result.detection_fields.key/value`, `TenantDeviceId ` is mapped to , `additional.fields.key` and `additional.fields.value.string_value`, `SecuredPartitionId ` is mapped to `security_result.detection_fields.key/value`, `SecuredKeyId ` is mapped to `security_result.detection_fields.key/value`. If `Name` is `StrongAuthenticationPhoneAppDetail` then from `OldValue`, `DeviceName` is mapped to `about.asset.hostname`, `PhoneAppVersion` is mapped to `about.asset.software.version`, `DeviceId` is mapped to `about.asset.asset_id`, `Id` is mapped to `about.asset.product_object_id`, `DeviceToken ` is mapped to `about.asset.attribute.labels.key/value`, `DeviceTag ` is mapped to `about.asset.attribute.labels.key/value`, `OathTokenTimeDrift ` is mapped to `security_result.detection_fields.key/value`, `TimeInterval ` is mapped to `security_result.detection_fields.key/value`, `AuthenticationType ` is mapped to `security_result.detection_fields.key/value`, `NotificationType ` is mapped to `about.asset.attribute.labels.key/value`, `LastAuthenticatedTimestamp ` is mapped to `security_result.detection_fields.key/value`, `AuthenticatorFlavor ` is mapped to `security_result.detection_fields.key/value`, `HashFunction ` is mapped to `security_result.detection_fields.key/value`, `TenantDeviceId ` is mapped to , `additional.fields.key` and `additional.fields.value.string_value`, `SecuredPartitionId ` is mapped to `security_result.detection_fields.key`, `SecuredKeyId ` is mapped to `security_result.detection_fields.key`. If `Name` is `StrongAuthenticationUserDetails` and `NewValue` contains a JSON object then from `NewValue`, `Email` is mapped to `target.user.email_addresses`, `PhoneNumber` is mapped to `target.user.phone_numbers`, `AlternativePhoneNumber` is mapped to `target.user.phone_numbers`, `VoiceOnlyPhoneNumber` is mapped to `target.user.phone_numbers`. If `Name` is `StrongAuthenticationUserDetails` and `NewValue` does not contain a JSON object then `security_result.detection_fields.key` is set to `StrongAuthenticationUserDetails_NewValue` and `NewValue` is mapped to `security_result.detection_fields.value`. If `Name` is `StrongAuthenticationUserDetails` and `OldValue` contains a JSON object then from `OldValue`, `Email` is mapped to `target.user.email_addresses`, `PhoneNumber` is mapped to `target.user.phone_numbers`, `AlternativePhoneNumber` is mapped to `target.user.phone_numbers`, `VoiceOnlyPhoneNumber` is mapped to `target.user.phone_numbers`. If `Name` is `StrongAuthenticationUserDetails` and `OldValue` does not contain a JSON object then `security_result.detection_fields.key` is set to `StrongAuthenticationUserDetails_OldValue` and `OldValue` is mapped to `security_result.detection_fields.value`. If `Name` is `StrongAuthenticationMethod` and `NewValue` contains a JSON object then the `StrongAuthenticationMethod_NewValue_{NewValue.key}` log field is mapped to `security_result.detection_fields.key` and `NewValue.value` is mapped to `security_result.detection_fields.value`. If `Name` is `StrongAuthenticationMethod` and `NewValue` does not contain a JSON object then `security_result.detection_fields.key` is set to `StrongAuthenticationMethod_NewValue` and `NewValue` is mapped to `security_result.detection_fields.value`. If `Name` is `StrongAuthenticationMethod` and `OldValue` contains a JSON object then the `StrongAuthenticationMethod_OldValue_{OldValue.key}` log field is mapped to `security_result.detection_fields.key` and `OldValue.value` is mapped to `security_result.detection_fields.value`. If `Name` is `StrongAuthenticationMethod` and `OldValue` does not contain a JSON object then `security_result.detection_fields.key` is set to `StrongAuthenticationMethod_OldValue` and `OldValue` is mapped to `security_result.detection_fields.value`. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | `principal.ip` and `principal.port` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `target.group.group_display_name` `target.user.userid` or `target.user.email_addresses` `security_result.detection_fields.key/value` If `Type` is 1 then `ID` is mapped to `target.group.group_display_name` If `Type` is 5 then `ID` is mapped to `target.user.userid` or `target.user.email_addresses` else `security_result.detection_fields.key/value` |
| Target.1.ID | `target.user.product_object_id` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Update group
The following table lists the log fields and corresponding UDM mappings for the operation "Update group" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_LOGIN If ResultStatus is Succeeded or ResultStatus is Success security_result.action is ALLOW security_result.summary is User login successful else if ResultStatus is Failed or LogonError !is security_result.action is BLOCK security_result.summary is User login failed security_result.description is {LogonError} UserId is mapped to target.user.userid or target.user.email_addresses metadata.description is User Login - {Workload} |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | network.http.user_agent extensions.auth.type extensions.auth.mechanism |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| DeviceProperties | network.session_id principal.platform principal.hostname If Name is OS { If Value is match to Windows then principal.platform is WINDOWS If Value is match to Mac then principal.platform is MAC If Value is match to Linux then principal.platform is LINUX } If Name is SessionId then Value is mapped to network.session_id If Name is OS then Value is mapped to principal.platform If Name is DisplayName then Value is mapped to principal.hostname |
| ErrorCode | security_result.description security_result.description is set to ErrorCode - {ErrorCode} |
| LogonError | `security_result.description` |
### UserLoggedIn
The following table lists the log fields and corresponding UDM mappings for the operation "UserLoggedIn" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_LOGIN security_result.Action is set to BLOCK security_result.summary is User login failed |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | network.http.user_agent extensions.auth.type extensions.auth.mechanism If Name is RequestType and Value is match to Saml.\* or OAuth2.\* then extensions.auth.type is mapped to MACHINE If Name is RequestType and Value is match to Login.\* then extensions.auth.type is mapped to REMOTE_INTERACTIVE If Name is UserAgent then Value is mapped to network.http.user_agent If Name is UserAuthenticationMethod then Based on Value it will map with extensions.auth.type If Name is requestType then Based on Value it will map with extensions.auth.type |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ResultStatusDetail | `security_result.detection_fields.key/value` |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| DeviceProperties | network.session_id principal.platform principal.hostname If Name is OS { If Value is matched to Windows then principal.platform is WINDOWS If Value is matched to Mac then principal.platform is MAC If Value is matched to Linux then principal.platform is LINUX `Value` is mapped to `principal.platform_version` } If Name is SessionId then Value is mapped to network.session_id If Name is OS then Value is mapped to principal.platform If Name is DisplayName then Value is mapped to principal.hostname If `Name` is `Id`, then `Value` is mapped to `principal.asset_id`. If `Name` is `IsCompliant`,then `Value` is mapped to `additional.fields.value.string_value`. If `Name` is `IsCompliantAndManaged`, then `Value` is mapped to `additional.fields.value.string_value`. If `Name` is `BrowserType`, then `Value` is mapped to `principal.asset.software.name`. If `Name` is matched to `TrustType` { If `Value` is `0`,then `additional.fields.value.string_value` is Microsoft Entra registered. If `Value` is `1`,then `additional.fields.value.string_value` is Microsoft Entra joined. If `Value` is `2`,then `additional.fields.value.string_value` is Microsoft Entra hybrid joined. } |
| ErrorCode | security_result.description security_result.description is set to ErrorCode - {ErrorCode} |
| LogonError | security_result.description If LogonError is UserAccountNotFound then extensions.auth.mechanism is set to USERNAME_PASSWORD |
### UserLoginFailed
The following table lists the log fields and corresponding UDM mappings for the operation "UserLoginFailed" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| ResultStatusDetail | `security_result.detection_fields.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Update StsRefreshTokenValidFrom Timestamp
The following table lists the log fields and corresponding UDM mappings for the operation "Update StsRefreshTokenValidFrom Timestamp" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT target.resource.resource_type is DEVICE ResultStatus is Success Action is set to ALLOW ResultStatus is Failure Action is set to BLOCK |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `target.resource.product_object_id` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `targetObjectId`, then the `Value` log field value is mapped to the `target.resource.product_object_id` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.platform target.ptatform_version security_result.description target.resource.name security_result.summary If DisplayName value present in ModifiedProperties field then we will map DisplayName with target.resource.name otherwise map ID of Target field if Type is 1. If Name is DeviceOSType then NewValue is mapped to target.platform If Name is DeviceOSVersion then NewValue is mapped to target.ptatform_version If Name is DevicePhysicalIds then NewValue is mapped to security_result.description If Name is DisplayName then NewVale is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.resource.name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 1 then ID is mapped to target.resource.name If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Update device
The following table lists the log fields and corresponding UDM mappings for the operation "Update device" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING Required fields for SETTING_MODIFICATION UDM validation : principal.machineid (IP or hostname or assetId or mac etc). ClientIP field is mandatory field for all the office 365 activities as per official doc of Office 365, but in some cases ClientIP field is absent If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.resource.name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 1 then ID is mapped to target.resource.name If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Set federation settings on domain
The following table lists the log fields and corresponding UDM mappings for the operation "Set federation settings on domain" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZEDRequired fields for STATUS_UNCATEGORIZED UDM validation : principal.machineid (IP or hostname or assetId or mac etc). ClientIP field is mandatory field for all the office 365 activities as per official doc of Office 365, but in some cases ClientIP field is absent If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| Target | target.resource.name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 1 then ID is mapped to target.resource.name If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Verify domain
The following table lists the log fields and corresponding UDM mappings for the operation "Verify domain" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.resource.name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 1 then ID is mapped to target.resource.name If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Set Company Information
The following table lists the log fields and corresponding UDM mappings for the operation "Set Company Information" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PASSWORD |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Reset user password
The following table lists the log fields and corresponding UDM mappings for the operation "Reset user password" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `security_result.description` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, if `Name` log field value is equal to `AccountEnabled` then AccountEnabled - `NewValue` is mapped to `security_result.description` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Disable account
The following table lists the log fields and corresponding UDM mappings for the operation "Disable account" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Delete application password for user
The following table lists the log fields and corresponding UDM mappings for the operation "Delete application password for user" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION target.resource.resource_type is DEVICE ResultStatus is Success Action is set to ALLOW ResultStatus is Failure Action is set to BLOCK |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.platform target.ptatform_version security_result.description target.resource.name security_result.summaryIf DisplayName value present in ModifiedProperties field then we will map DisplayName with target.resource.name otherwise map ID of Target field if Type is 1. If Name is DeviceOSType then NewValue is mapped to target.platform If Name =DeviceOSVersion then NewValue is mapped to target.ptatform_version If Name is DevicePhysicalIds then NewValue is mapped to security_result.description If Name is DisplayName then NewVale is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.resource.name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 1 then ID is mapped to target.resource.name If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Delete device
The following table lists the log fields and corresponding UDM mappings for the operation "Delete device" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION target.resource.resource_type is DEVICE ResultStatus is Success Action is set to ALLOW ResultStatus is Failure Action is set to BLOCK |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `target.resource.product_object_id` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `targetObjectId`, then the `Value` log field value is mapped to the `target.resource.product_object_id` UDM field. Else, the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.platform target.ptatform_version security_result.description target.resource.name security_result.summaryIf DisplayName value present in ModifiedProperties field then we will map DisplayName with target.resource.name otherwise map ID of Target field if Type is 1. If Name is DeviceOSType then NewValue is mapped to target.platform If Name =DeviceOSVersion then NewValue is mapped to target.ptatform_version If Name is DevicePhysicalIds then NewValue is mapped to security_result.description If Name is DisplayName then NewVale is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.resource.name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 1 then ID is mapped to target.resource.name If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add registered users to device
The following table lists the log fields and corresponding UDM mappings for the operation "Add registered users to device" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.product_object_id target.resource.nameIf Name is Device.ObjectId then NewValue is mapped to target.resource.product_object_id If Name is Device.DisplayName then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add registered owner to device
The following table lists the log fields and corresponding UDM mappings for the operation "Add registered owner to device" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.product_object_id target.resource.name If Name is Device.ObjectId then NewValue is mapped to target.resource.product_object_id If Name is Device.DisplayName then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add owner to group
The following table lists the log fields and corresponding UDM mappings for the operation "Add owner to group" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.group.product_object_id target.group.group_display_nameIf Name is Group.ObjectId then NewValue is mapped to target.group.product_object_id If Name is Group.DisplayName then NewValue is mapped to target.group.group_display_name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add OAuth2PermissionGrant
The following table lists the log fields and corresponding UDM mappings for the operation "Add OAuth2PermissionGrant" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.product_object_id target.resource.name security_result.summaryIf Name is ServicePrincipal.ObjectId then NewValue is mapped to target.resource.product_object_id If Name is ServicePrincipal.DisplayName then NewValue is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add device
The following table lists the log fields and corresponding UDM mappings for the operation "Add device" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_CREATION target.resource.resource_type is DEVICE ResultStatus is Success Action is set to ALLOW ResultStatus is Failure Action is set to BLOCK |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.platform target.ptatform_version security_result.description target.resource.name security_result.summaryIf DisplayName value present in ModifiedProperties field then we will map DisplayName with target.resource.name otherwise map ID of Target field if Type is 1. If Name is DeviceOSType then NewValue is mapped to target.platform If Name is DeviceOSVersion then NewValue is mapped to target.ptatform_version If Name is DevicePhysicalIds then NewValue is mapped to security_result.description If Name is DisplayName then NewVale is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add app role assignment grant to user
The following table lists the log fields and corresponding UDM mappings for the operation "Add app role assignment grant to user" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSION `target.application`
`additional.fields[workload]`
If the log fields `EventSource` and `Workload` are not `empty` and equal, then the log field `EventSource` is mapped to the `target.application` UDM field.
Else If, the log fields `EventSource` and `Workload` are not `empty` and not equal, then the log field `EventSource` is mapped to the `target.application` UDM field and the `Workload` field is mapped to `additional.fields.value` UDM field and the `additional.fields.key` UDM field is set to `workload`.
Else If, the log field `EventSource` is not `empty`, then the log field `EventSource` is mapped to the `target.application` UDM field.
Else If, the log field `Workload` is not `empty`, then the log field `Workload` is mapped to the `target.application` UDM field. |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.user.userid or target.user.email_addresses If Name is User.UPN then NewValue is mapped to target.user.userid or target.user.email_addresses |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Consent to application
The following table lists the log fields and corresponding UDM mappings for the operation "Consent to application" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.resource.name target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Update service principal
The following table lists the log fields and corresponding UDM mappings for the operation "Update service principal" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE target.resource.resource_type is set to SETTING ObjectId is mapped to target.url |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary target.resource.nameIf Name is Included Updated Properties then NewValue is mapped to security_result.summary If Name is DisplayName then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add service principal
The following table lists the log fields and corresponding UDM mappings for the operation "Add service principal" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION ObjectId is mapped to target.url |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary If Name is DisplayName then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Remove service principal
The following table lists the log fields and corresponding UDM mappings for the operation "Remove service principal" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary target.resource.nameIf Name is Included Updated Properties then NewValue is mapped to security_result.summary If Name is DisplayName then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add member to role
The following table lists the log fields and corresponding UDM mappings for the operation `Add member to role` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_CHANGE_PERMISSIONS` `ResultStatus` is `Success` then `Action` is set to `ALLOW` `security_result.summary` is set to `Added a user to an admin role successfully` `ResultStatus` is `Failure` then `Action` is set to `BLOCK` `security_result.summary` is set to `Added a user to an admin role failed` `ObjectId` is mapped to `target.url` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `target.resource.product_object_id` `target.resource.attribute.roles.name` `target.resource.attribute.labels.key/value` if `Name` is `Role.ObjectId` then `NewValue` is `target.resource.product_object_id` If `Name` is `Role.DisplayName` then `NewValue` is `target.user.attribute.roles.name` if `Name` is `Role.TemplateId` then `NewValue` and `OldValue` is `target.user.attribute.labels.key/value` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | `principal.ip` and `principal.port` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `target.user.userid` or `target.user.email_addresses` `security_result.detection_fields.key/value` If `Type` is 5 then `ID` is mapped to `target.user.userid` or `target.user.email_addresses` else `security_result.detection_fields.key/value` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Remove member from role
The following table lists the log fields and corresponding UDM mappings for the operation "Remove member from role" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS ResultStatus is Success then Action is set to ALLOW security_result.summary is Removed a user to an admin role successfully ResultStatus is Failure then Action is set to BLOCK security_result.summary is Removed a user to an admin role failed |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| | event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary If Name is DisplayName then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value if Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add label
The following table lists the log fields and corresponding UDM mappings for the operation "Add label" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION ObjectId is set to target.resource.product_object_id |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary If Name is DisplayName then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemsId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Create company
The following table lists the log fields and corresponding UDM mappings for the operation "Create company" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION ObjectId is set to target.resource.product_object_id |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamName | `target.group.group_display_name` |
| Version | `metadata.product_version` |
### TeamsSessionStarted
The following table lists the log fields and corresponding UDM mappings for the operation "TeamsSessionStarted" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_CREATION target.resource.resource_type is TASK If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. ObjectId is set to `additional.fields[object_id]` |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
### ScheduleGroupAdded
The following table lists the log fields and corresponding UDM mappings for the operation "ScheduleGroupAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_MODIFICATION target.resource.resource_type is TASK If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
### ScheduleGroupEdited
The following table lists the log fields and corresponding UDM mappings for the operation "ScheduleGroupEdited" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_DELETION target.resource.resource_type is TASK If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
### ScheduleGroupDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "ScheduleGroupDeleted" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION target.resource.resource_type is set to SETTING Required fields for SETTING_CREATION UDM validation : principal.machineid (IP or hostname or assetId or mac etc). ClientIP field is mandatory field for all the office 365 activities as per official doc of Office 365, but in some cases ClientIP field is absent If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| Shift | `target.resource.attribute.labels.value` |
### ShiftAdded
The following table lists the log fields and corresponding UDM mappings for the operation "ShiftAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| Shift | `target.resource.attribute.labels.value` |
### ShiftEdited
The following table lists the log fields and corresponding UDM mappings for the operation "ShiftEdited" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_DELETION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| Shift | `target.resource.attribute.labels.value` |
### ShiftDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "ShiftDeleted" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| Shift | `target.resource.attribute.labels.value` |
### TimeOffAdded
The following table lists the log fields and corresponding UDM mappings for the operation "TimeOffAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATIONtarget.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| Shift | `target.resource.attribute.labels.value` |
### TimeOffEdited
The following table lists the log fields and corresponding UDM mappings for the operation "TimeOffEdited" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_DELETIONtarget.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| Shift | `target.resource.attribute.labels.value` |
### TimeOffDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "TimeOffDeleted" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| OpenShift | `target.resource.attribute.labels.key/value` |
### OpenShiftAdded
The following table lists the log fields and corresponding UDM mappings for the operation "OpenShiftAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| OpenShift | `target.resource.attribute.labels.key/value` |
### OpenShiftEdited
The following table lists the log fields and corresponding UDM mappings for the operation "OpenShiftEdited" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_DELETION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| OpenShift | `target.resource.attribute.labels.key/value` |
### OpenShiftDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "OpenShiftDeleted" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_UNCATEGORIZED |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
### ScheduleShared
The following table lists the log fields and corresponding UDM mappings for the operation "ScheduleShared" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
### ClockedIn
The following table lists the log fields and corresponding UDM mappings for the operation "ClockedIn" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
### BreakStarted
The following table lists the log fields and corresponding UDM mappings for the operation "BreakStarted" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
### BreakEnded
The following table lists the log fields and corresponding UDM mappings for the operation "BreakEnded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| ShiftRequest | `target.resource.attribute.labels.key/value` |
### RequestAdded
The following table lists the log fields and corresponding UDM mappings for the operation "RequestAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| ShiftRequest | `target.resource.attribute.label.key/value` |
### RequestRespondedTo
The following table lists the log fields and corresponding UDM mappings for the operation "RequestRespondedTo" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
| ShiftRequest | `target.resource.attribute.label.key/value` |
### RequestCancelled
The following table lists the log fields and corresponding UDM mappings for the operation "RequestCancelled" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| ScheduleId | `target.resource.product_object_id` |
### ScheduleSettingChanged
The following table lists the log fields and corresponding UDM mappings for the operation "ScheduleSettingChanged" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers and target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| Version | `metadata.product_version` |
### TeamSettingChanged
The following table lists the log fields and corresponding UDM mappings for the operation "TeamSettingChanged" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.name` The `Name` log field is mapped to the `target.resource.name` UDM field. |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers and target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| Version | `metadata.product_version` |
### AppInstalled
The following table lists the log fields and corresponding UDM mappings for the operation "AppInstalled" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AddOnGuid | `target.resource.product_object_id` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `target.resource.name` |
| Version | `metadata.product_version` |
| AppDistributionMode | `additional.fields.key` and `additional.fields.value.string_value` |
| AzureADAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.product_object_id` |
### MemberRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "MemberRemoved" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChatName | `target.group.group_display_name` |
| ChatThreadId | target.user.group_identifiers target.group.product_object_id |
### TabRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "TabRemoved" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnGuid | `target.resource.product_object_id` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| AddOnName | `target.resource.name` |
| ChannelName | `target.resource.attribute.labels.key/value` |
| TeamName | `target.group.group_display_name` |
### AppUninstalled
The following table lists the log fields and corresponding UDM mappings for the operation "AppUninstalled" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AddOnGuid | `target.resource.product_object_id` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `target.resource.name` |
| Version | `metadata.product_version` |
| AppDistributionMode | `additional.fields.key` and `additional.fields.value.string_value` |
| AzureADAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.product_object_id` |
### MemberAdded
The following table lists the log fields and corresponding UDM mappings for the operation "MemberAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| Version | `metadata.product_version` |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChatName | `target.group.group_display_name` |
| ChatThreadId | target.user.group_identifiers target.group.product_object_id |
### TabAdded
The following table lists the log fields and corresponding UDM mappings for the operation "TabAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnGuid | `target.resource.product_object_id` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| AddOnName | `target.resource.name` |
| AddOnUrl | `target.url` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamName | `target.group.group_display_name` |
### ClockedOut
The following table lists the log fields and corresponding UDM mappings for the operation "ClockedOut" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| Version | `metadata.product_version` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| ScheduleId | `target.resource.product_object_id` |
### TeamCreated
The following table lists the log fields and corresponding UDM mappings for the operation "TeamCreated" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | `target.resource.product_object_id` |
| TeamName | `target.resource.name` |
| Version | `metadata.product_version` |
### BotAddedToTeam
The following table lists the log fields and corresponding UDM mappings for the operation "BotAddedToTeam" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AddOnGuid | `target.resource.product_object_id` |
| AddOnName | `target.resource.name` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### ChannelAdded
The following table lists the log fields and corresponding UDM mappings for the operation "ChannelAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `target.resource.product_object_id` |
| ChannelName | `target.resource.name` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | `about.user.email_addresses` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### ConnectorAdded
The following table lists the log fields and corresponding UDM mappings for the operation "ConnectorAdded" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | `about.user.email_addresses` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### ChannelSettingChanged
The following table lists the log fields and corresponding UDM mappings for the operation "ChannelSettingChanged" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `target.resource.product_object_id` |
| ChannelName | `target.resource.name` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### TeamsTenantSettingChanged
The following table lists the log fields and corresponding UDM mappings for the operation "TeamsTenantSettingChanged" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### MemberRoleChanged
The following table lists the log fields and corresponding UDM mappings for the operation "MemberRoleChanged" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name DisplayName is mapped to about.user.user_display_name Role is mapped to about.user.attribute.roles.name UPN is mapped to about.user.email_addresses |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### DeletedAllOrganizationApps
The following table lists the log fields and corresponding UDM mappings for the operation "DeletedAllOrganizationApps" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | `about.user.email_addresses` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### ChannelDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "ChannelDeleted" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `target.resource.product_object_id` |
| ChannelName | `target.resource.name` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | `about.user.email_addresses` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### TeamDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "TeamDeleted" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | `about.user.email_addresses` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | `target.resource.product_object_id` |
| TeamName | `target.resource.name` |
### BotRemovedFromTeam
The following table lists the log fields and corresponding UDM mappings for the operation "BotRemovedFromTeam" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | `about.user.email_addresses` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### ConnectorRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "ConnectorRemoved" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | `about.user.email_addresses` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### ConnectorUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "ConnectorUpdated" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | `about.user.email_addresses` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
### TabUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "TabUpdated" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `target.resource.name` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `target.resource.attribute.labels.key/value` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| Members | about.user.userid or about.user.email_addresses about.user.user_display_name about.user.attribute.roles.name |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| Name | `target.resource.attribute.labels.key` |
| NewValue | `target.resource.attribute.labels.value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| TabType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnUrl | `target.url` |
### Update
The following table lists the log fields and corresponding UDM mappings for the operation "Update" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Item | network.email.subject target.resource.product_object_id target.resource.name target.file.size network.email.mail_id target.file.full_path Id is mapped to target.resource.product_object_id Subject is mapped to network.email.subject SizeInBytes is mapped to target.file.size Item.ParentFolder.Path is mapped to target.resource.name InternetMessageId is mapped to network.email.mail_id Attachments is mapped to target.file.full_path |
| Item.Id | `target.resource.product_object_id` |
| Item.ImmutableId | `target.resource.attribute.labels[Item_ImmutableId]` |
| ModifiedProperties | `securiy_result.summary` |
| SessionId | `network.session_id` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### FolderBind
The following table lists the log fields and corresponding UDM mappings for the operation "FolderBind" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| Item | target.resource.product_object_id target_resource_name network.email.mail_id Item.id is mapped to target.resource.product_object_id Item.InternetMessageId is mapped to network.email.mail_id Item.ParentFolder.Path is mapped to target.resource.name |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### SendOnBehalf
The following table lists the log fields and corresponding UDM mappings for the operation "SendOnBehalf" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_TRANSACTION |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Item | network.email.subject network.email.mail_id target.file.full_path target.resource.product_object_id Item.InternetMessageId is mapped to network.email.email_id Item.Subject is mapped to network.email.subject Item.Attachments is mapped to target.file.full_path Item.Id is mapped to target.resource.product_object_id |
| SessionId | `network.session_id` |
| SendOnBehalfOfUserSmtp | target.user.userid or target.user.email_addresses |
| Version | `metadata.product_version` |
### SendAs
The following table lists the log fields and corresponding UDM mappings for the operation "SendAs" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_TRANSACTION |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| SendAsUserMailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| Item | network.email.subject network.email.mail_id target.file.full_path target.resource.product_object_id Item.InternetMessageId is mapped to network.email.mail_id Item.Subject is mapped to network.email.subject Item.Attachments is mapped to target.file.full_path Item.Id is mapped to target.resource.product_object_id |
| SessionId | `network.session_id` |
| SendAsUserSmtp | target.user.userid or target.user.email_addresses |
| Version | `metadata.product_version` |
### Send
The following table lists the log fields and corresponding UDM mappings for the operation "Send" and workload "Exchange":
| Log field | UDM mapping |
|---|---|---|
| | metadata.event_type is mapped to EMAIL_TRANSACTION |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | principal.user.email_addresses or principal.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| Item | network.email.subject network.email.mail_id target.file.full_path target.resource.product_object_id |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| Item.Recipients.Address | `target.user.email_addresses` `network.email.to` | Iterate through each `recipient` in `Item.Recipients` and `recipient.Address` is mapped to the `target.user.email_addresses` and `network.email.to` UDM field. |
| Item.Recipients.Name | `target.user.userid` | Iterate for each element `recipient` with index `index` in the `Item.Recipients` log field array, then If index is 0 then, `recipient` value will be mapped to `target.user.userid` UDM field. Otherwise, `additional.fields.key` UDM field is set to `recipients_%{index}_name` and the `recipient.Name` log field is mapped to the `additional.fields.value` UDM field. |
| UserID | `network.email.from` |
### New-InboxRule
The following table lists the log fields and corresponding UDM mappings for the operation "New-InboxRule" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION target.resource.resource_type is set to SETTING ObjectId is set to target.resource.product_object_id |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| Parameters | `security_result.rule_labels.key/value` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExternalAccess | `principal.user.attributes.labels[external_access]` |
| Parameters.AlwaysDeleteOutlookRulesBlob | `principal.user.attributes.labels[external_access]` |
| Parameters.Force | `additional.fields[force]` |
| Parameters.From | `additional.fields[from]` |
| Parameters.Name | `security_result.rule_name` |
| Parameters.StopProcessingRules | `additional.fields[stop_processing_rules]` |
| ResultStatus | If the `ResultStatus` log field value is equal to `True` then, the `security_result.action` UDM field is set to `ALLOW`. Else, if `ResultStatus` log field value is equal to `False` then, the `security_result.action` UDM field is set to `BLOCK`. |
| Parameters.SubjectContainsWords | `additional.fields[subject_contains_words]` |
| Parameters.MoveToFolder | `additional.fields[move_to_folder]` |
### Set-InboxRule
The following table lists the log fields and corresponding UDM mappings for the operation "Set-InboxRule" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION ObjectId is set to target.resource.product_object_id target.resource.resource_type is set to SETTING |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `security_result.rule_labels.key/value` |
| SessionId | `network.session_id` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ExternalAccess | `principal.user.attributes.labels[external_access]` |
| Parameters.AlwaysDeleteOutlookRulesBlob | `additional.fields[AlwaysDeleteOutlookRulesBlob]` |
| Parameters.Force | `additional.fields[Force]` |
| Parameters.From | `additional.fields[From]` |
| Parameters.Identity | `security_result.detection_fields[parameters_identity]` |
| Parameters.StopProcessingRules | `additional.fields[StopProcessingRules]` |
| Parameters.Name | `security_result.rule_name` |
| ResultStatus | If the `ResultStatus` log field value is equal to `True` then, the `security_result.action` UDM field is set to `ALLOW`. Else, if `ResultStatus` log field value is equal to `False` then, the `security_result.action` UDM field is set to `BLOCK`. |
### MoveToDeletedItems
The following table lists the log fields and corresponding UDM mappings for the operation "MoveToDeletedItems" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| DestFolder | target.resource.product_object_id target.resource.name |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| AffectedItems | about.file.full_path network.email.subject network.email.mail_id Subject is mapped to network.email.subject ParentFolder.Path is mapped to about.file.full_path AffectedItems.0.InternetMessageIdis mapped to network.email.mail_id |
| Folder | src.resource.product_object_id src.resource.name |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Folder.Path | `src.file.full_path` |
| Folder.Id | `src.resource.product_object_id` |
| DestFolder.Path | `target.file.full_path` |
| DestFolder.Id | `target.resource.product_object_id` |
### Move
The following table lists the log fields and corresponding UDM mappings for the operation "Move" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| DestFolder | target.resource.product_object_id target.resource.name |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| AffectedItems | about.file.full_path network.email.subject network.email.mail_id |
| Folder | src.resource.product_object_id src.resource.name |
| Folder.Path | `src.file.full_path` |
| Folder.Id | `src.resource.product_object_id` |
| DestFolder.Path | `target.file.full_path` |
| DestFolder.Id | `target.resource.product_object_id` |
### MailItemsAccessed
The following table lists the log fields and corresponding UDM mappings for the operation "MailItemsAccessed" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| OperationProperties | `security_result.detection_fields.key/value.` |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| OperationCount | `additional.fields.key` and `additional.fields.value.string_value` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Folders | `target.resource.name` Iterate through each `key`, `value` pair in `Folders`: If `key` is equal to `Path`, the `value` is mapped to the `target.resource.name` UDM field. Else if `key` is equal to `id`, the `value` is mapped to the `target.resource.product_object_id` UDM field. Else, iterate through nested maps similar to the old UDM field logic, mapping to `additional.fields`. |
| Folders.FolderItems.ImmutableId | `about.resource.attribute.labels[ImmutableId]` |
| Folders.FolderItems.Sensitivity | `about.resource.attribute.labels[Sensitivity]` |
### MailboxLogin
The following table lists the log fields and corresponding UDM mappings for the operation "MailboxLogin" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_LOGIN auth.Type is MACHINE |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### SoftDelete
The following table lists the log fields and corresponding UDM mappings for the operation "SoftDelete" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| AffectedItems | about.file.full_path network.email.subject network.email.mail_id AffectedItems.Attachments is mapped to about.file.full_path AffectedItems.Subject is mapped to network.email.subject AffectedItems.0.InternetMessageIdis mapped to network.email.mail_id |
| Folder | target.resource.name target.resource.product_object_id Folder.Path is mapped to target.resource.name Folder.Id is mapped to target.resource.product_object_id |
| SessionId | `network.session_id` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| Folder.Path | `src.file.full_path` |
| Folder.Id | `src.resource.product_object_id` |
| DestFolder.Path | `target.file.full_path` |
| DestFolder.Id | `target.resource.product_object_id` |
### HardDelete
The following table lists the log fields and corresponding UDM mappings for the operation "HardDelete" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| AffectedItems | about.file.full_path network.email.subject network.email.mail_id |
| Version | `metadata.product_version` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Folder | target.resource.name target.resource.product_object_id |
| Folder.Path | `src.file.full_path` |
| Folder.Id | `src.resource.product_object_id` |
| DestFolder.Path | `target.file.full_path` |
| DestFolder.Id | `target.resource.product_object_id` |
### Create
The following table lists the log fields and corresponding UDM mappings for the operation "Create" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| Item | target.resource.name target.resource.product_object_id target.file.full_path network.email.subject network.email.mail_id Item.id is mapped to target.resource.product_object_id Item.InternetMessageId is mapped to network.email.mail_id Item.ParentFolder.Path is mapped to target.resource.name Item.Subject is mapped to network.email.subject Attachment may present or not in log so write grok for this. Item.Attachments is mapped to target.file.full_path |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### RemoveFolderPermissions
The following table lists the log fields and corresponding UDM mappings for the operation "RemoveFolderPermissions" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ResultStatus is Succeeded Action is set to ALLOW else Action is set to BLOCK |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| Item | target.file.full_path target.resource.attribute.permissions.name target.user.email_addresses or target.user.userid Item.ParentFolder.MemberUpn is mapped to target.user.email_addresses or target.user.userid Item.ParentFolder.Path is mapped to target.file.full_path User rights is mapped to target.resource.attribute.permissions.name |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### ModifyFolderPermissions
The following table lists the log fields and corresponding UDM mappings for the operation "ModifyFolderPermissions" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ResultStatus is Succeeded Action is set to ALLOW else Action is set to BLOCK |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| Item | target.file.full_path target.user.email_addresses or target.user.userid target.resource.attribute.permissions.name |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### AddFolderPermissions
The following table lists the log fields and corresponding UDM mappings for the operation "AddFolderPermissions" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ResultStatus is Succeeded Action is set to ALLOW else Action is set to BLOCK |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| Item | target.file.full_path target.user.email_addresses or target.user.userid target.resource.attribute.permissions.name Path is mapped to target.file.full_path Item.ParentFolder.MemberUpn is mapped to target.user.email_addresses or target.user.userid User Rights is mapped to target.resource.attribute.permissions.name |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-MailboxPermission
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-MailboxPermission" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### Add-MailboxPermission
The following table lists the log fields and corresponding UDM mappings for the operation "Add-MailboxPermission" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| AppId | `target.resource.attribute.labels.key/value` |
| Parameters | `security_result.detection_fields.key/value` |
| ObjectId | `target.resource.attribute.labels.key/value` |
### UpdateInboxRules
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateInboxRules" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| Item | target.resource.product_object_id target.resource.name Item.ParentFolder.name is mapped to target.resource.name Item.ParentFolder.id is mapped to target.resource.product_object_id |
| OperationProperties | security_result.rule_id security_result.rule_name security_result.action_details security_result.detection_fields.key/value additional.fields.key and additional.fields.value.list_value.values.string_value if Name is RuleId then Value is mapped to security_result.rule_id if Name is RuleName then Value is mapped to security_result.rule_name else security_result.detection_fields.key/value if Name is RuleActions then: Iterate for each element in the JSON array value of RuleActions with index index: - Map ActionType to security_result.action_details. - Iterate for each recipient in the Recipients array: the additional.fields.key is set to RuleActions_%{index}_Recipients and the recipient is mapped to the additional.fields.value.list_value.values.string_value field. |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
### UpdateCalendarDelegation
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateCalendarDelegation" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSIONS target.resource.resource_type is SERVICE_ACCOUNT |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
### ApplyRecordLabel
The following table lists the log fields and corresponding UDM mappings for the operation "ApplyRecordLabel" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
### UpdateFolderPermissions
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateFolderPermissions" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS target.resource.resource_type is set to STORAGE_OBJECT |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
### Set-User
The following table lists the log fields and corresponding UDM mappings for the operation "Set-User" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED ObjectId is set to target.user.userid or target.user.email_addresses |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
### ViewReport
The following table lists the log fields and corresponding UDM mappings for the operation "ViewReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_READ |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.name` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is mapped to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ConsumptionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetId | `target.resource.attribute.label.key/value` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ReportId | `target.resource.product_object_id` |
| ReportType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
### GenerateEmbedToken
The following table lists the log fields and corresponding UDM mappings for the operation "GenerateEmbedToken" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT ObjectId is set to target.file.full_path |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ConsumptionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetId | `target.resource.attribute.label.key/value` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ReportId | `target.resource.attribute.labels.key/value` |
| ReportType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| EmbedTokenId | `target.resource.product_object_id` |
| RLSIdentities | about.user.email_addresses about.user.attribute.roles.name RLSIdentities.UserName is mapped to about.user.email_addresses RLSIdentities.Roles is mapped to about.user.attribute.roles.name |
### CreateDataset
The following table lists the log fields and corresponding UDM mappings for the operation "CreateDataset" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.name` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.product_object_id` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
### GenerateCustomVisualAADAccessToken
The following table lists the log fields and corresponding UDM mappings for the operation "GenerateCustomVisualAADAccessToken" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| CustomVisualAccessTokenResourceId | `target.resource.product_object_id` |
| CustomVisualAccessTokenSiteUri | `target.url` |
### DeleteOrganizationalGalleryItem
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteOrganizationalGalleryItem" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| OrganizationalGalleryItemId | `target.resource.product_object_id` |
| OrganizationalGalleryItemDisplayName | `target.resource.name` |
| OrganizationalGalleryItemPublishTime | `target.resource.attribute.labels.key/value` |
### DeleteAlmPipeline
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteAlmPipeline" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DeploymentPipelineId | `additional.fields.key` and `additional.fields.value.string_value` |
| DeploymentPipelineObjectId | `target.resource.product_object_id` |
### AddDatasourceToGateway
The following table lists the log fields and corresponding UDM mappings for the operation "AddDatasourceToGateway" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| GatewayId | `target.resource.attribute.labels.key/value` |
| GatewayType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasourceId | `target.resource.product_object_id` |
| DatasourceType | `target.resource.attribute.labels.key/value` |
### AssignWorkspaceToPipeline
The following table lists the log fields and corresponding UDM mappings for the operation "AssignWorkspaceToPipeline" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkspaceId | `target.resource.attribute.labels[WorkspaceId]` The `WorkspaceId` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `WorkspaceId`. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DeploymentPipelineId | `additional.fields.key` and `additional.fields.value.string_value` |
| DeploymentPipelineObjectId | `target.resource.product_object_id` |
| DeploymentPipelineStageOrder | `additional.fields.key` and `additional.fields.value.string_value` |
### CancelDataflowRefresh
The following table lists the log fields and corresponding UDM mappings for the operation "CancelDataflowRefresh" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DataflowId | `target.resource.product_object_id` |
| DataflowName | `target.resource.name` |
| DataflowType | `target.resource.attribute.labels.key/value` |
### ChangeCapacityState
The following table lists the log fields and corresponding UDM mappings for the operation "ChangeCapacityState" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| CapacityName | `target.resource.name` |
| CapacityUsers | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityState | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### ChangeGatewayAdministrators
The following table lists the log fields and corresponding UDM mappings for the operation "ChangeGatewayAdministrators" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| GatewayId | `target.resource.product_object_id` |
| UserInformation | `about.user.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### InsertOrganizationalGalleryItem
The following table lists the log fields and corresponding UDM mappings for the operation "InsertOrganizationalGalleryItem" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| OrganizationalGalleryItemId | `target.resource.product_object_id` |
| OrganizationalGalleryItemDisplayName | `target.resource.name` |
| OrganizationalGalleryItemPublishTime | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### CreateAlmPipeline
The following table lists the log fields and corresponding UDM mappings for the operation "CreateAlmPipeline" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| DeploymentPipelineId | `additional.fields.key` and `additional.fields.value.string_value` |
| DeploymentPipelineObjectId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### CreateApp
The following table lists the log fields and corresponding UDM mappings for the operation "CreateApp" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.name` |
| WorkspaceId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### CreateDashboard
The following table lists the log fields and corresponding UDM mappings for the operation "CreateDashboard" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION If IsSuccess is true then security_result.summary is Dashboard created successfully else security_result.summary is Dashboard not created |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DashboardId | `target.resource.product_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
### CreateDataflow
The following table lists the log fields and corresponding UDM mappings for the operation "CreateDataflow" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_CREATION If IsSuccess is true then security_result.summary is Dataflow created successfully else security_result.summary is Dataflow not created |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataflowType | `target.resource.attribute.labels.key/value` |
| DataflowId | `target.resource.product_id` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
### CreateEmailSubscription
The following table lists the log fields and corresponding UDM mappings for the operation "CreateEmailSubscription" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_CREATION If IsSuccess is true then security_result.summary is EmailSubscription created successfully else security_result.summary is EmailSubscription not created ObjectId is set to target.file.full_path |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| SubscriptionSchedule | `additional.fields.key` and `additional.fields.value.string_value` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `additional.fields.key` and `additional.fields.value.string_value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| SubscribeeInformation | `about.user.email_addresses` Iterate through each `key`, `value` pair in `SubscribeeInformation`: Iterate through each `key1`, `value1` pair in `value`: If `key1` is equal to `RecipientEmail`, the `value1` is mapped to the `about.user.email_addresses` UDM field. Else if `key1` is equal to `RecipientName`, the `value1` is mapped to the `about.user.user_display_name` UDM field. Else, the `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `SubscribeeInformation_%{key}_%{key1}`. |
| DashboardId | `target.resource.product_object_id` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.name` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
### CreateFolder
The following table lists the log fields and corresponding UDM mappings for the operation "CreateFolder" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| FolderDisplayName | `target.resource.name` |
| FolderObjectId | `target.resource.attribute.labels.key/value` |
### CreateGateway
The following table lists the log fields and corresponding UDM mappings for the operation "CreateGateway" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| GatewayId | `target.resource.product_object_id` |
| GatewayType | `additional.fields.key` and `additional.fields.value.string_value` |
### CreateTemplateApp
The following table lists the log fields and corresponding UDM mappings for the operation "CreateTemplateApp" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| TemplateAppObjectId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
### DeleteComment
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteComment" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| AuditedArtifactInformation | target.resource.name target.resource.product_object_id target.resource.attribute.labels.key/value Name is mapped to target.resource.name ArtifactObjectId is set to target.resource.product_object_id AnnotatedItemType is mapped to target.resource.attribute.labels.key/value |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
### DeleteDashboard
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteDashboard" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardId | `target.resource.product_object_id` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| DashboardName | `target.resource.name` |
| Datasets | about.resource.product_object_id about.resource.name DatasetId is mapped to about.resource.product_object_id DatasetName is mapped to about.resource.name |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
### DeleteDataflow
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteDataflow" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | `target.user.user_display_name` `target.user.product_object_id` `target.user.email_addresses` `target.user.attribute.permissions.name`
Iterate for each element `info` in the `SharingInformation` log field array, then The `info.RecipientName` log field is mapped to the `target.user.user_display_name` UDM field. The `info.ObjectId` log field is mapped to the `target.user.product_object_id` UDM field. The `info.RecipientEmail` log field is mapped to the `target.user.email_addresses` UDM field. If the `info.ResharePermission` value is not `empty` then, the `info.ResharePermission` log field is mapped to the `target.user.attribute.permissions.name` UDM field. |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DataflowId | `target.resource.product_object_id` |
| DataflowName | `target.resource.name` |
| DataflowType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
### DeleteDataset
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteDataset" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.product_object_id` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
### DeleteEmailSubscription
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteEmailSubscription" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_DELETION ObjectId is set to target.file.full_path |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardId | `target.resource.product_object_id` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.name` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
### DeleteFolder
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteFolder" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION if isSuccess is TRUE then security_result.action is set to ALLOW else security_result.action is set to BLOCK |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| FolderObjectId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### DeleteGateway
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteGateway" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| GatewayId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### DeleteGroup
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteGroup" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.nameRecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.name` |
| WorkspaceId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### DeleteReport
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetId | `target.resource.attribute.label.key/value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| ReportName | `target.resource.name` |
| ReportId | `target.resource.product_object_id` |
| ReportType | `target.resource.attribute.labels.key/value` |
### DownloadReport
The following table lists the log fields and corresponding UDM mappings for the operation "DownloadReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetId | `target.resource.attribute.label.key/value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| ReportName | `target.resource.name` |
| ReportId | `target.resource.product_object_id` |
| ReportType | `target.resource.attribute.labels.key/value` |
### EditDataset
The following table lists the log fields and corresponding UDM mappings for the operation "EditDataset" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.product_object_id` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
### EditDatasetProperties
The following table lists the log fields and corresponding UDM mappings for the operation "EditDatasetProperties" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetId | `target.resource.product_object_id` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.name` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetCertificationStage | `target.resource.attribute.labels.key/value` |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
### EditReport
The following table lists the log fields and corresponding UDM mappings for the operation "EditReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetId | `target.resource.attribute.label.key/value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| ReportName | `target.resource.name` |
| ReportId | `target.resource.attribute.labels.key/value` |
| ReportType | `target.resource.attribute.labels.key/value` |
### ExportDataflow
The following table lists the log fields and corresponding UDM mappings for the operation "ExportDataflow" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT if isSuccess is TRUE then security_result.summary is Dataflow Exported Successfully else security_result.summary is Dataflow Not Exported |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DataflowId | `target.resource.product_id` |
| DataflowName | `target.rsource.name` |
| DataflowType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### ExportReport
The following table lists the log fields and corresponding UDM mappings for the operation "ExportReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT if isSuccess is TRUE then security_result.summary is Report Exported Successfully else security_result.summary is Report Not Exported |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetId | `target.resource.product_object_id` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.name` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
### InstallApp
The following table lists the log fields and corresponding UDM mappings for the operation "InstallApp" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AppName | `target.resource.name` The `AppName` log field is mapped to the `target.resource.name` UDM field. |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `additional.fields.key` and `additional.fields.value.string_value` |
### InstallTemplateApp
The following table lists the log fields and corresponding UDM mappings for the operation "InstallTemplateApp" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `additional.fields.key` and `additional.fields.value.string_value` |
| TemplateAppFolderObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| TemplateAppOwnerTenantObjectId | `about.user.product_object_id` The `TemplateAppOwnerTenantObjectId` log field is mapped to the `about.user.product_object_id` UDM field. |
| TemplateAppVersion | `metadata.product_version` |
| TemplateAppObjectId | `target.resource.product_object_id` |
| TemplatePackageName | `target.resource.name` |
### PostComment
The following table lists the log fields and corresponding UDM mappings for the operation "PostComment" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| AuditedArtifactInformation | target.resource.name target.resource.product_object_id target.resource.attribute.labels.key/value |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### PrintDashboard
The following table lists the log fields and corresponding UDM mappings for the operation "PrintDashboard" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT ObjectId is set to target.file.full_path |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DashboardId | `target.resource.product_object_id` |
| Datasets | about.resource.product_object_id about.resource.name DatasetId is mapped to about.resource.product_object_id DatasetName is mapped to about.resource.name |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
### PrintReport
The following table lists the log fields and corresponding UDM mappings for the operation "PrintReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| ReportName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.attribute.label.key/value` |
| ReportId | `target.resource.product_object_id` |
| ReportType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
### UnassignWorkspaceFromPipeline
The following table lists the log fields and corresponding UDM mappings for the operation "UnassignWorkspaceFromPipeline" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | `target.user.user_display_name` `target.user.product_object_id` `target.user.email_addresses` `target.user.attribute.permissions.name`
Iterate for each element `info` in the `SharingInformation` log field array, then The `info.RecipientName` log field is mapped to the `target.user.user_display_name` UDM field. The `info.ObjectId` log field is mapped to the `target.user.product_object_id` UDM field. The `info.RecipientEmail` log field is mapped to the `target.user.email_addresses` UDM field. If the `info.ResharePermission` value is not `empty` then, the `info.ResharePermission` log field is mapped to the `target.user.attribute.permissions.name` UDM field. |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| DeploymentPipelineId | `target.resource.attribute.labels.key/value` |
| DeploymentPipelineObjectId | `target.resource.product_object_id` |
### RemoveDatasourceFromGateway
The following table lists the log fields and corresponding UDM mappings for the operation "RemoveDatasourceFromGateway" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| GatewayId | `target.resource.attribute.label.key/value` |
| DatasourceId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### RenameDashboard
The following table lists the log fields and corresponding UDM mappings for the operation "RenameDashboard" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is set to target.file.full_path |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DashboardId | `target.resource.product_object_id` |
| Datasets | about.resource.product_object_id about.resource.name DatasetId is mapped to about.resource.product_object_id DatasetName is mapped to about.resource.name |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
### RequestDataflowRefresh
The following table lists the log fields and corresponding UDM mappings for the operation "RequestDataflowRefresh" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DataflowId | `target.resource.product_object_id` |
| DataflowName | `target.resource.name` |
| DataflowRefreshScheduleType | `additional.fields.key` and `additional.fields.value.string_value` |
| DataflowType | `target.resource.attribute.label.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### RefreshDataset
The following table lists the log fields and corresponding UDM mappings for the operation "RefreshDataset" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.product_object_id` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RefreshType | `additional.fields.key` and `additional.fields.value.string_value` |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
### SensitivityLabelApplied
The following table lists the log fields and corresponding UDM mappings for the operation "SensitivityLabelApplied" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. `target.resource.resource_type` is set to `SETTING`. |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission.recipients | `target.user.email_addresses` |
| OrgAppPermission.permissions | `target.user.attribute.permissions.name` |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation.RecipientEmail | `about.user.email_addresses` |
| SharingInformation.RecipientName | `about.user.user_display_name` |
| SharingInformation.ObjectId | `about.user.product_object_id` |
| SharingInformation.ResharePermission | `about.user.attribute.permissions.name` |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.attribute.labels.key/value` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| SensitivityLabelId | `target.resource.product_object_id` |
| ActionSourceDetail | `additional.fields.key` and `additional.fields.value.string_value` |
| LabelEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
| ActionSourceDetail | `additional.fields.key` and `additional.fields.value.string_value` |
| ArtifactType | `additional.fields.key` and `additional.fields.value.string_value` |
| Common.Location | `target.location.name` |
### SensitivityLabelRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "SensitivityLabelRemoved" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE target.resource.resource_type is set to SETTING |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.attribute.labels.key/value` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| OldSensitivityLabelId | `target.resource.product_object_id` |
| ActionSource | `additional.fields.key` and `additional.fields.value.string_value` |
| LabelEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
| ActionSourceDetail | `additional.fields.key` and `additional.fields.value.string_value` |
| ArtifactType | `additional.fields.key` and `additional.fields.value.string_value` |
| Common.Location | `target.location.name` |
### SetScheduledRefreshOnDataflow
The following table lists the log fields and corresponding UDM mappings for the operation "SetScheduledRefreshOnDataflow" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_CREATION target.resource.resource_type is TASK |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DataflowId | `target.resource.product_id` |
| DataflowName | `target.resource.name` |
| DataflowType | `target.resource.attribute.label.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### SetScheduledRefresh
The following table lists the log fields and corresponding UDM mappings for the operation "SetScheduledRefresh" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_CREATION target.resource.resource_type is TASK |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.rsource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.product_id` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| Schedules | `additional.fields.key` and `additional.fields.value.string_value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
### ShareDashboard
The following table lists the log fields and corresponding UDM mappings for the operation "ShareDashboard" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.name` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| DashboardId | `target.resource.product_object_id` |
| Datasets | about.resource.product_object_id about.resource.name DatasetId is mapped to about.resource.product_object_id DatasetName is mapped to about.resource.name |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| SharingAction | `additional.fields.key` and `additional.fields.value.string_value` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
### ShareReport
The following table lists the log fields and corresponding UDM mappings for the operation "ShareReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| Datasets | about.resource.product_object_id about.resource.name |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ArtifactId | `target.resource.product_object_id` |
| ArtifactName | `target.resource.name` |
| SharingAction | `additional.fields.key` and `additional.fields.value.string_value` |
| ShareLinkId | `additional.fields.key` and `additional.fields.value.string_value` |
### OptInForProTrial
The following table lists the log fields and corresponding UDM mappings for the operation "OptInForProTrial" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### UnpublishApp
The following table lists the log fields and corresponding UDM mappings for the operation "UnpublishApp" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkspaceId | `target.resource.product_object_id` |
| WorkSpaceName | `target.resource.name` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### UpdateOrganizationalGalleryItem
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateOrganizationalGalleryItem" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| OrganizationalGalleryItemId | `target.resource.product_object_id` |
| OrganizationalGalleryItemDisplayName | `target.resource.name` |
| OrganizationalGalleryItemPublishTime | `target.resource.attribute.labels.key/value` |
### UpdateAlmPipelineAccess
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateAlmPipelineAccess" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DeploymentPipelineObjectId | `target.resource.product_object_id` |
| DeploymentPipelineDisplayName | `target.resource.name` |
| DeploymentPipelineAccesses | about.user.userid about.user.attribute.permissions.name userid is mapped to about.user.userid Rolepermission is mapped to about.user.attribute.permissions.name |
### UpdateInstalledTemplateAppParameters
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateInstalledTemplateAppParameters" and workload "and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| TemplateAppObjectId | `target.resource.product_object_id` |
| TemplatePackageName | `target.resource.name` |
| TemplateAppVersion | `metadata.product_version` |
| TemplateAppFolderObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
### UpdatedAdminFeatureSwitch
The following table lists the log fields and corresponding UDM mappings for the operation "UpdatedAdminFeatureSwitch" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is mapped to SETTING |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### UpdateApp
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateApp" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.name` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| WorkspaceId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### UpdateDataflow
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateDataflow" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DataflowId | `target.resource.product_object_id` |
| DataflowName | `target.resource.name` |
| DataflowType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### UpdateDatasetParameters
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateDatasetParameters" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.product_object_id` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value` |
### UpdateEmailSubscription
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateEmailSubscription" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_MODIFICATION target.resource.resource_type is mapped to TASK |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| SubscriptionSchedule | `additional.fields.key` and `additional.fields.value.string_value` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `additional.fields.key` and `additional.fields.value.string_value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| SubscribeeInformation | `about.user.email_addresses` Iterate through each `key`, `value` pair in `SubscribeeInformation`: Iterate through each `key1`, `value1` pair in `value`: If `key1` is equal to `RecipientEmail`, the `value1` is mapped to the `about.user.email_addresses` UDM field. Else if `key1` is equal to `RecipientName`, the `value1` is mapped to the `about.user.user_display_name` UDM field. Else, the `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `SubscribeeInformation_%{key}_%{key1}`. |
| DashboardId | `target.resource.product_object_id` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.name` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
### UpdateFolder
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateFolder" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| FolderObjectId | `target.resource.product_object_id` |
| FolderDisplayName | `target.resource.name` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### UpdateFolderAccess
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateFolderAccess" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| FolderObjectId | `target.resource.product_object_id` |
| FolderDisplayName | `target.resource.name` |
| FolderAccessRequests | about.user.userid about.user.product_object_id about.user.attribute.permissions.type UserId is mapped to about.user.userid UserObjectId is set to about.user.product_object_id RolePermissions is mapped to about.user.attribute.permissions.type |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### UpdateDatasourceCredentials
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateDatasourceCredentials" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| GatewayId | `target.resource.attribute.labels.key/value` |
| DatasourceId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### UpdateTemplateAppSettings
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateTemplateAppSettings" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| TemplateAppObjectId | `target.resource.product_object_id` |
### UpdateTemplateAppTestPackagePermissions
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateTemplateAppTestPackagePermissions" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| TemplateAppObjectId | `target.resource.product_object_id` |
### ViewDashboard
The following table lists the log fields and corresponding UDM mappings for the operation "ViewDashboard" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_READ |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ConsumptionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| Datasets | about.resource.product_object_id about.resource.name DatasetId is mapped to about.resource.product_object_id DatasetName is mapped to about.resource.name |
| DashboardId | `target.resource.product_object_id` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.name` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
### ViewDataflow
The following table lists the log fields and corresponding UDM mappings for the operation "ViewDataflow" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_READ |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| CapacityName | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DataflowId | `target.resource.product_object_id` |
| DataflowName | `target.resource.name` |
| DataflowType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### AddTile
The following table lists the log fields and corresponding UDM mappings for the operation "AddTile" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.name` |
| WorkspaceId | `target.resource.product_object_id` |
| TileText | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### RunEmailSubscription
The following table lists the log fields and corresponding UDM mappings for the operation "RunEmailSubscription" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SCHEDULED_TASK_UNCATEGORIZED target.resource.resource_type is TASK If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.label.key/value` |
| DashboardName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.label.key/value` |
| DashboardId | `target.resource.product_object_id` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
### CreateReport
The following table lists the log fields and corresponding UDM mappings for the operation "CreateReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.label.key/value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| ReportName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.label.key/value` |
| DatasetId | `target.resource.attribute.label.key/value` |
| ReportId | `target.resource.product_object_id` |
| ReportType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
### GetSnapshots
The following table lists the log fields and corresponding UDM mappings for the operation "GetSnapshots" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### OptInForPPUTrial
The following table lists the log fields and corresponding UDM mappings for the operation "OptInForPPUTrial" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-MailUser
The following table lists the log fields and corresponding UDM mappings for the operation "Set-MailUser" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED ObjectId is set to target.resource.attribute.labels\[object_id\] |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.user.email_addresses` The extracted `email` from `email_addresses` is mapped to the `target.user.email_addresses` UDM field. The extracted `email_address` from `group_email_address` is mapped to the `target.user.email_addresses` UDM field. |
| Version | `metadata.product_version` |
### Set-MailContact
The following table lists the log fields and corresponding UDM mappings for the operation "Set-MailContact" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED ObjectId is set to target.resource.attribute.labels\[object_id\] |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.user.email_addresses` The extracted `email` from `email_addresses` is mapped to the `target.user.email_addresses` UDM field. The extracted `email_address` from `group_email_address` is mapped to the `target.user.email_addresses` UDM field. |
| Version | `metadata.product_version` |
### Set-Mailbox
The following table lists the log fields and corresponding UDM mappings for the operation "Set-Mailbox" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED Object is mapped to target.resource.attribute.labels\[object_id\] |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### Set-DistributionGroup
The following table lists the log fields and corresponding UDM mappings for the operation "Set-DistributionGroup" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is set to target.group.group_display_name security_result.summary is Group members definition ResultStatus is True Action is set to ALLOW else Action is set to BLOCK |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[accept_messages_only_from_senders_or_members]` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `AcceptMessagesOnlyFromSendersOrMembers`, the `parameter.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `accept_messages_only_from_senders_or_members`. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### Set-Contact
The following table lists the log fields and corresponding UDM mappings for the operation "Set-Contact" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED ObjectId is set to target.group.group_display_name |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.user.email_addresses` The extracted `email` from `email_addresses` is mapped to the `target.user.email_addresses` UDM field. The extracted `email_address` from `group_email_address` is mapped to the `target.user.email_addresses` UDM field. |
| Version | `metadata.product_version` |
### Set-CASMailbox
The following table lists the log fields and corresponding UDM mappings for the operation "Set-CASMailbox" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION ObjectId is set to target.group.group_display_name |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ModifiedObjectResolvedName | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### Set-CalendarProcessing
The following table lists the log fields and corresponding UDM mappings for the operation "Set-CalendarProcessing" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### Set-AdminAuditLogConfig
The following table lists the log fields and corresponding UDM mappings for the operation "Set-AdminAuditLogConfig" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. ObjectId is mapped to target.url target.resource.resource_type is set to SETTING |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ModifiedObjectResolvedName | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### Remove-UnifiedGroup
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-UnifiedGroup" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_DELETION |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
### Remove-MigrationUser
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-MigrationUser" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED ObjectId is set to target.user.userid or target.user.email_addresses |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.user.email_addresses` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity` and `parameter.Value` contains an email address, the `parameter.Value` is mapped to the `target.user.email_addresses` UDM field. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### Update-eDiscoveryCaseAdmin
The following table lists the log fields and corresponding UDM mappings for the operation "Update-eDiscoveryCaseAdmin" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-DistributionGroupMember
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-DistributionGroupMember" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is set to target.group.group_display_name security_result.summary is set to Group Members definition If ResultStatus is True { Action is set to ALLOW } else { Action is set to BLOCK } |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
### ViewedSearchExported
The following table lists the log fields and corresponding UDM mappings for the operation "ViewedSearchExported" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| Case | `about.resource.product_object_id` |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `target.resource.product_object_id` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `CaseId`, then the `Value` log field value is mapped to the `target.resource.product_object_id` UDM field. Else, if the `Name` log field value is equal to `SearchIds`, then the `Value` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ObjectType | `security_result.summary` |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Version | `metadata.product_version` |
### AddWorkingSetQueryToWorkingSet
The following table lists the log fields and corresponding UDM mappings for the operation "AddWorkingSetQueryToWorkingSet" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### AddQueryToWorkingSet
The following table lists the log fields and corresponding UDM mappings for the operation "AddQueryToWorkingSet" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### RunAlgo
The following table lists the log fields and corresponding UDM mappings for the operation "RunAlgo" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### AnnotateDocument
The following table lists the log fields and corresponding UDM mappings for the operation "AnnotateDocument" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### BurnJob
The following table lists the log fields and corresponding UDM mappings for the operation "BurnJob" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### CreateWorkingSet
The following table lists the log fields and corresponding UDM mappings for the operation "CreateWorkingSet" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| CaseId | `target.resource.attribute.labels[case_id]` |
| CaseName | `target.resource.attribute.labels[case_name]` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.product_object_id` Iterate through each `field` in `ExtendedProperties`: If `field.Name` is equal to `WorkingSetId`, the `field.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| Version | `metadata.product_version` |
### CreateWorkingsetSearch
The following table lists the log fields and corresponding UDM mappings for the operation "CreateWorkingsetSearch" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### CreateTag
The following table lists the log fields and corresponding UDM mappings for the operation "CreateTag" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### DeleteWorkingsetSearch
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteWorkingsetSearch" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### DeleteTag
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteTag" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### DownloadDocument
The following table lists the log fields and corresponding UDM mappings for the operation "DownloadDocument" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### UpdateTag
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateTag" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### ExportJob
The following table lists the log fields and corresponding UDM mappings for the operation "ExportJob" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### UpdateCaseSettings
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateCaseSettings" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### UpdateWorkingsetSearch
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateWorkingsetSearch" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### TagFiles
The following table lists the log fields and corresponding UDM mappings for the operation "TagFiles" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### ViewDocument
The following table lists the log fields and corresponding UDM mappings for the operation "ViewDocument" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| CaseId | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| StartTime | `additional.fields[start_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| Version | `metadata.product_version` |
### SearchViewed
The following table lists the log fields and corresponding UDM mappings for the operation "SearchViewed" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | target.resource.product_object_id If Name is SearchIds then Value is mapped to target.resource.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Version | `metadata.product_version` |
### CaseMemberAdded
The following table lists the log fields and corresponding UDM mappings for the operation "CaseMemberAdded" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | target.resource.product_object_id about.user.email_address about.user.product_object_id If Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Name is CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} Extract target_user information using grok grok { match is mapped to { Parameters .\*-(Member\|User) \\{DATA:target_user}\\ } } |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Version | `metadata.product_version` |
### SearchUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "SearchUpdated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`.Else If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the UDM field `target.resource.product_object_id`UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Version | `metadata.product_version` |
### CaseAdminUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "CaseAdminUpdated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | about.user.email_address about.user.product_object_id If Name is CaseAdminsSmtp then Value is mapped to about.user.email_addresses if Name is CaseAdminsGuid then Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Version | `metadata.product_version` |
### CaseUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "CaseUpdated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | target.resource.product_object_id about.user.email_address about.user.product_object_idIf Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Name is CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### CaseMemberUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "CaseMemberUpdated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | target.resrource.product_object_id about.user.email_address about.user.product_object_id If Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Name is CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### SearchPermissionUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "SearchPermissionUpdated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExtendedProperties | `target.user.email_addresses` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `Users` and `data.Value` matches the regular expression pattern `(^.+@.+$)` and `data.Value` matches the regular expression pattern `^.{0,255}$`, the `data.Value` is mapped to the `target.user.email_addresses` UDM field. |
| ExtendedProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### HoldUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "HoldUpdated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`.Else If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the UDM field `target.resource.product_object_id`UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### SearchRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "SearchRemoved" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_DELETION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`.Else If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the UDM field `target.resource.product_object_id`UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### CaseAdminRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "CaseAdminRemoved" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | target.resource.product_object_id about.user.email_address about.user.product_object_id If Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Name is CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line target.user.email_address target.user.userid If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} target_user is mapped to target.user.email_addresses or target.user.userid |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### CaseRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "CaseRemoved" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | target.resource.product_object_id about.user.email_address about.user.product_object_id If Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Name is CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_detail` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### SearchPermissionRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "SearchPermissionRemoved" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `target.user.email_addresses` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `Users`, the `data.Value` is mapped to the `target.user.email_addresses` UDM field. |
| ExtendedProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### HoldRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "HoldRemoved" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`.Else If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the UDM field `target.resource.product_object_id`UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### HoldCreated
The following table lists the log fields and corresponding UDM mappings for the operation "HoldCreated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`.Else If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the UDM field `target.resource.product_object_id`UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### SearchCreated
The following table lists the log fields and corresponding UDM mappings for the operation "SearchCreated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_detail` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`.Else If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the UDM field `target.resource.product_object_id`UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_detail` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_detail` |
### CaseAdminAdded
The following table lists the log fields and corresponding UDM mappings for the operation "CaseAdminAdded" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExtendedProperties | target.resource.product_object_id about.user.email_address about.user.prdouct_object_id If Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Name is CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### SearchStarted
The following table lists the log fields and corresponding UDM mappings for the operation "SearchStarted" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`.Else If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the UDM field `target.resource.product_object_id`UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Version | `metadata.product_version` |
### SearchReport
The following table lists the log fields and corresponding UDM mappings for the operation "SearchReport" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `target.resource.product_object_id` `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### SearchStopped
The following table lists the log fields and corresponding UDM mappings for the operation "SearchStopped" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`.Else If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the UDM field `target.resource.product_object_id`UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_detail` |
### CaseViewed
The following table lists the log fields and corresponding UDM mappings for the operation "CaseViewed" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_detail` |
| ExtendedProperties | target.resource.product_object_id about.user.email_addresses about.user.product_object_id If Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Nameis CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_detail` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_detail` |
### SearchExportDownloaded
The following table lists the log fields and corresponding UDM mappings for the operation "SearchExportDownloaded" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `target.resource.product_object_id` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `CaseId`, then the `Value` log field value is mapped to the `target.resource.product_object_id` UDM field. Else, if the `Name` log field value is equal to `SearchIds`, then the `Value` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ObjectType | `security_result.summary` |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| Version | `metadata.product_version` |
### CaseMemberRemoved
The following table lists the log fields and corresponding UDM mappings for the operation "CaseMemberRemoved" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | target.resource.product_object_id about.user.email_address about.user.product_object_id If Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Name is CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} Extract target_user information using grok grok { match is mapped to { Parameters .\*-(Member\|User) \\{DATA:target_user}\\ } } |
| Version | `metadata.product_version` |
### CaseAdded
The following table lists the log fields and corresponding UDM mappings for the operation "CaseAdded" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | target.resource.product_object_id about.user.email_address about.user.product_object_idIf Name is CaseId then ID is mapped to target.resource.product_object_id If Name is CaseMembersSmtp then each Value is mapped to about.user.email_addresses If Name is CaseMembersGuid then each Value is mapped to about.user.product_object_id |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Version | `metadata.product_version` |
### SearchPermissionCreated
The following table lists the log fields and corresponding UDM mappings for the operation "SearchPermissionCreated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_CREATION ObjectId is set to `target.resource.name` |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `target.user.email_addresses` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `Users`, the `data.Value` is mapped to the `target.user.email_addresses` UDM field. |
| ExtendedProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
| Version | `metadata.product_version` |
### NetworkConfigurationUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "NetworkConfigurationUpdated" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### ProcessProfileFields
The following table lists the log fields and corresponding UDM mappings for the operation "ProcessProfileFields" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### SupervisorAdminToggled
The following table lists the log fields and corresponding UDM mappings for the operation "SupervisorAdminToggled" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### NetworkSecurityConfigurationUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "NetworkSecurityConfigurationUpdated" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### FileCreated
The following table lists the log fields and corresponding UDM mappings for the operation "FileCreated" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_CREATIONIf ResultStatus is TRUE { security_result.action is ALLOW} else {security_result.action is BLOCK} |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### GroupCreation
The following table lists the log fields and corresponding UDM mappings for the operation "GroupCreation" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_CREATION If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### MessageDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "MessageDeleted" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### GroupDeletion
The following table lists the log fields and corresponding UDM mappings for the operation "GroupDeletion" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_DELETION If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### DataExport
The following table lists the log fields and corresponding UDM mappings for the operation "DataExport" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### FileVisited
The following table lists the log fields and corresponding UDM mappings for the operation "FileVisited" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_READ If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### StreamInvokeVideoView
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoView" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `additional.fields[operation_details]` The `OperationDetails` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `operation_details`. |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoShare
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoShare" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION if ResultStatus is SUCCEEDED then action is set to ALLOW else action is set to BLOCK |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `additional.fields[operation_details]` The `OperationDetails` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `operation_details`. |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoLike
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoLike" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoUnLike
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoUnLike" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoUpload
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoUpload" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION if ResultStatus is SUCCEEDED then action is set to ALLOW else action is set to BLOCK |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoDownload
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoDownload" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS if ResultStatus is SUCCEEDED then action is set to ALLOW else action is set to BLOCK |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoSetLink
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoSetLink" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamCreateGroup
The following table lists the log fields and corresponding UDM mappings for the operation "StreamCreateGroup" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_CREATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamEditGroup
The following table lists the log fields and corresponding UDM mappings for the operation "StreamEditGroup" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamDeleteGroup
The following table lists the log fields and corresponding UDM mappings for the operation "StreamDeleteGroup" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_DELETION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamEditGroupMemberships
The following table lists the log fields and corresponding UDM mappings for the operation "StreamEditGroupMemberships" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_UNCATEGORIZED |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamCreateChannel
The following table lists the log fields and corresponding UDM mappings for the operation "StreamCreateChannel" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamEditChannel
The following table lists the log fields and corresponding UDM mappings for the operation "StreamEditChannel" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `network.http.referral_url` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamDeleteChannel
The following table lists the log fields and corresponding UDM mappings for the operation "StreamDeleteChannel" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `network.http.referral_url` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeChannelSetThumbnail
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeChannelSetThumbnail" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `network.http.referral_url` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamEditVideoPermissions
The following table lists the log fields and corresponding UDM mappings for the operation "StreamEditVideoPermissions" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE if ResultStatus is Succeeded then action is ALLOW else action is BLOCK |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamEditVideo
The following table lists the log fields and corresponding UDM mappings for the operation "StreamEditVideo" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamDeleteVideo
The following table lists the log fields and corresponding UDM mappings for the operation "StreamDeleteVideo" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamEditUserSettings
The following table lists the log fields and corresponding UDM mappings for the operation "StreamEditUserSettings" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamEditAdminTenantSettings
The following table lists the log fields and corresponding UDM mappings for the operation "StreamEditAdminTenantSettings" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamCreateVideoComment
The following table lists the log fields and corresponding UDM mappings for the operation "StreamCreateVideoComment" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamDeleteVideoComment
The following table lists the log fields and corresponding UDM mappings for the operation "StreamDeleteVideoComment" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoTextTrackUpload
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoTextTrackUpload" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamDeleteVideoTextTrack
The following table lists the log fields and corresponding UDM mappings for the operation "StreamDeleteVideoTextTrack" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoThumbnailUpload
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoThumbnailUpload" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT if ResultStatus is Succeeded then action is ALLOW else action is BLOCK |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamCreateVideo
The following table lists the log fields and corresponding UDM mappings for the operation "StreamCreateVideo" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### DlpRuleMatch \& DLPRuleMatch
The following table lists the log fields and corresponding UDM mappings for the operation `DlpRuleMatch & DLPRuleMatch` and workload `Exchange` ,`SharePoint` ,`Endpoint` or `OneDrive`:
`security_result.category` is set to `DATA_EXFILTRATION`
`ObjectId`
If `Workload` contains one of the following values:
`ObjectId``target.url`
`Workload``Exchange``ObjectId``network.email.mail_id`
`Workload``Endpoint``ObjectId``target.file.full_path`
`ObjectId``network.email.mail_id`
- `Onedrive`
- `Sharepoint`
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` If `Workload` contains one of the following values: - `Onedrive` - `Sharepoint` then the `metadata.event_type` UDM field is mapped to the `SCAN_FILE`. Otherwise if `Workload` is equal to `Exchange`, the `metadata.event_type` UDM field is mapped to the `EMAIL_UNCATEGORIZED`. Otherwise if `Workload` is equal to `Endpoint`, the `metadata.event_type` UDM field is mapped to the `SCAN_UNCATEGORIZED` |
| SharePointMetaData | `network.http.referral_url` `network.email.from` `target.file.full_path` `target.url` `target.file.size` `SiteCollectionUrl` is mapped to `network.http.referral_url` `From` is mapped to `network.email.from` (if `ExchangeMetadata` field not getting in log) `FileName` is mapped to `target.file.full_path` `FilePathUrl` is mapped to `target.url` `FileSize` is mapped to `target.file.size` |
| ExchangeMetaData | `network.email.from` `network.email.to` `network.email.bcc` `network.email.cc` `network.email.subject` `additional.fields.key` and `additional.fields.value.string_value` The `From` log field value is mapped to the `network.email.from` UDM field. The `To` log field value is mapped to the `network.email.to` UDM field. `BCC` log field value is mapped to `network.email.bcc` UDM field. The`CC` log field value is mapped to the `network.email.cc` UDM field. The `RecipientCount` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. The `Sent` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ExceptionInfo | `additional.fields.key` and `additional.fields.value.string_value` |
| PolicyDetails | `target.resource.product_object_id` `security_result.summary` `security_result.description` `security_result.rule_id` `security_result.rule_name` `security_result.severity` `security_result.confidence_details` `security_result.detection_fields.key/value` `PolicyId` is mapped to `target.resource.product_object_id` `PolicyName` is mapped to `security_result.summary` `SensitiveInformationTypeName` is mapped to `security_result.description` `RuleId` is mapped to `security_result.rule_id` `RuleName` is mapped to `security_result.rule_name` `Severity` is mapped to `security_result.severity` `SensitiveInformationDetailedClassificationAttributes.Confidence` is mapped to `security_result.confidence_details` `SensitiveInformationDetailedClassificationAttributes.Count` is mapped to `security_result.detection_fields.key/value` |
| IncidentId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| EndpointMetaData.SensitiveInfoTypeData.Count | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.Confidence | `security_result.confidence_details` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetectionsInfo.DetectedValues.Name | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.ClassifierType | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInfoTypeName | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveTypeSource | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.UniqueCount | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInfoTypeId | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetectionsInfo.DetectedValues.Value | `security_result.detection_fields.key/value` |
| Location | `target.location.name` |
| ItemMetadata.Id | `target.resource.product_object_id` |
| ItemMetadata.Name | `target.resource.name` |
| ItemMetadata.Path | `target.file.full_path` |
| ItemMetadata.CorrelationId | `additional.fields[ItemMetadata.CorrelationId]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### DlpRuleUndo
The following table lists the log fields and corresponding UDM mappings for the operation "DlpRuleUndo" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE security_result.category is set to DATA_EXFILTRATION ObjectId is set to network.email.mail_id |
| SharePointMetaData | network.http.referral_url network.email.from target.file.full_path target.url target.file.size SiteCollectionUrl is mapped to network.http.referral_url From is mapped to network.email.from (if ExchangeMetadata field not getting in log) FileName is mapped to target.file.full_path FilePathUrl is mapped to target.url FileSize is mapped to target.file.size |
| ExceptionInfo | `additional.fields.key` and `additional.fields.value.string_value` |
| PolicyDetails | target.resource.product_object_id security_result.summary security_result.description security_result.rule_id security_result.rule_name security_result.severity PolicyId is mapped to target.resource.product_object_id PolicyName is mapped to security_result.summary SensitiveInformationTypeName is mapped to security_result.description RuleId is mapped to security_result.rule_id RuleName is mapped to security_result.rule_name Severity is mapped to security_result.severity |
| IncidentId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| EndpointMetaData.SensitiveInfoTypeData.Count | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.Confidence | `security_result.confidence_details` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetectionsInfo.DetectedValues.Name | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.ClassifierType | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInfoTypeName | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveTypeSource | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.UniqueCount | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInfoTypeId | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetectionsInfo.DetectedValues.Value | `security_result.detection_fields.key/value` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### DlpInfo
The following table lists the log fields and corresponding UDM mappings for the operation "DlpInfo" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` If `Workload` contains one of the following values: - `Onedrive` - `Sharepoint` then the `metadata.event_type` UDM field is mapped to the `SCAN_FILE`. Otherwise if `Workload` is equal to `Exchange`, the `metadata.event_type` UDM field is mapped to the `EMAIL_UNCATEGORIZED`. security_result.category is set to DATA_EXFILTRATION `ObjectId` If `Workload` contains one of the following values: - `Onedrive` - `Sharepoint` then the `ObjectId` raw log field is mapped to the `target.url` UDM field. Otherwise if `Workload` is equal to `Exchange`, the `ObjectId` raw log field is mapped to the `network.email.mail_id`UDM field.
|
| SharePointMetaData | network.http.referral_url network.email.from target.file.full_path target.url target.file.size SiteCollectionUrl is mapped to network.http.referral_url From is mapped to network.email.from (if ExchangeMetadata field not getting in log) FileName is mapped to target.file.full_path FilePathUrl is mapped to target.url FileSize is mapped to target.file.size |
| ExceptionInfo | `additional.fields.key` and `additional.fields.value.string_value` |
| PolicyDetails | target.resource.product_object_id security_result.summary security_result.description security_result.rule_id security_result.rule_name security_result.severity PolicyId is mapped to target.resource.product_object_id PolicyName is mapped to security_result.summary SensitiveInformationTypeName is mapped to security_result.description RuleId is mapped to security_result.rule_id RuleName is mapped to security_result.rule_name Severity is mapped to security_result.severity |
| IncidentId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| EndpointMetaData.SensitiveInfoTypeData.Count | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.Confidence | `security_result.confidence_details` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetectionsInfo.DetectedValues.Name | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.ClassifierType | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInfoTypeName | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveTypeSource | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.UniqueCount | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInfoTypeId | `security_result.detection_fields.key/value` |
| EndpointMetaData.SensitiveInfoTypeData.SensitiveInformationDetectionsInfo.DetectedValues.Value | `security_result.detection_fields.key/value` |
### MipLabel
The following table lists the log fields and corresponding UDM mappings for the operation "MipLabel" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED ObjectId is set to network.email.mail_id |
| ApplicationMode | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemName | `network.email.subject` |
| LabelAppliedDateTime | `additional.fields.key` and `additional.fields.value.string_value` |
| LabelId | `target.resource.product_object_id` |
| LabelName | `target.resource.name` |
| Receivers | `network.email.to` |
| Sender | `network.email.from` |
| Version | `metadata.product_version` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### SiteCollectionCreated
The following table lists the log fields and corresponding UDM mappings for the operation "SiteCollectionCreated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventData | `additional.fields[site_creation_source]` The `EventData` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `site_creation_source`. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
| Version | `metadata.product_version` |
### SiteDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "SiteDeleted" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| DestinationRelativeUrl | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileName | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileExtension | `target.file.mime_type` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
### PreviewModeEnabledSet
The following table lists the log fields and corresponding UDM mappings for the operation "PreviewModeEnabledSet" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is mapped to SETTING |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### OfficeOnDemandSet
The following table lists the log fields and corresponding UDM mappings for the operation "OfficeOnDemandSet" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### HubSiteJoined
The following table lists the log fields and corresponding UDM mappings for the operation "HubSiteJoined" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| EventData | target.resource.attribute.labels.key/value target.resource.attribute.labels.key/value PreviousHubSiteIdis mapped to target.resource.attribute.labels.key/value HubSiteIdis mapped to target.resource.attribute.labels.key/value IsHubSiteIdis mapped to target.resource.attribute.labels.key/value |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### HubSiteRegistered
The following table lists the log fields and corresponding UDM mappings for the operation "HubSiteRegistered" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| EventData | target.resource.attribute.labels.key/value target.resource.attribute.labels.key/value HubSiteIdis mapped to target.resource.attribute.labels.key/value IsHubSiteIdis mapped to target.resource.attribute.labels.key/value |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### HubSiteUnjoined
The following table lists the log fields and corresponding UDM mappings for the operation "HubSiteUnjoined" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE ObjectID is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| EventData | target.resource.attribute.labels.key/value IsHubSiteIdis mapped to target.resource.attribute.labels.key/value |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### HubSiteUnregistered
The following table lists the log fields and corresponding UDM mappings for the operation "HubSiteUnregistered" and workload "HubSiteUnregistered":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE ObjectID is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| EventData | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### SharingPolicyChanged
The following table lists the log fields and corresponding UDM mappings for the operation "SharingPolicyChanged" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| CorrelationId | `security_result.detection_fields.key/value` |
| Version | `metadata.product_version` |
| AssertingApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### NetworkAccessPolicyChanged
The following table lists the log fields and corresponding UDM mappings for the operation "NetworkAccessPolicyChanged" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| ModifiedProperties | `about.ip` Iterate through each `field` in `ModifiedProperties`: If `field.NewValue` is not `empty` and if `field.Name` is equal to `IPAddressAllowList`, iterate through `ip_address_allow_list` and map extracted `ip_address` to the `about.ip` UDM field. |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### AlertEntityGenerated
The following table lists the log fields and corresponding UDM mappings for the operation "AlertEntityGenerated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AlertId | `target.resource.product_object_id` |
| AlertType | `target.resource.attribute.labels.key/value` |
| Name | `security_result.description` |
| PolicyId | `security_result.detection_fields[PolicyId]` |
| Status | `security_result.detection_fields[Status]` |
| Severity | `security_result.severity` |
| Category | `security_result.category`If `category`equals`DataLossPrevention`then`security_result.category` UDM field is set to `DATA_EXFILTRATION`. |
| Source | `security_result.detection_fields[Source]` |
| Comments | `security_result.about.investigation.comments` |
| Data | `additional.fields.key` and `additional.fields.value.string_value` |
| AlertEntityId | target.user.userid or target.user.email_addresses |
| EntityType | `target.resource.resource_subtype` The `EntityType` log field is mapped to the `target.resource.resource_subtype` UDM field. |
| Version | `metadata.product_version` |
| Data.tsd | `principal.user.email_addresses` |
| Data.trc | `target.user.email_addresses` |
| Data.imsgid | `network.email.mail_id` |
### AlertTriggered
The following table lists the log fields and corresponding UDM mappings for the operation "AlertTriggered" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT security_result.category is set to DATA_EXFILTRATION |
| AlertId | `target.resource.product_object_id` |
| AlertType | `target.resource.attribute.labels.key/value` |
| Name | `security_result.description` |
| PolicyId | `security_result.detection_fields[PolicyId]` |
| Status | `security_result.detection_fields[Status]` |
| Severity | `security_result.severity` |
| Category | `security_result.category`If `category`equals`DataLossPrevention`then`security_result.category` UDM field is set to `DATA_EXFILTRATION`. |
| Source | `security_result.detection_fields[Source]` |
| Comments | `security_result.about.investigation.comments` |
| Data | `additional.fields.key` and `additional.fields.value.string_value` |
| AlertEntityId | target.user.userid or target.user.email_addresses |
| EntityType | `target.resource.resource_subtype` The `EntityType` log field is mapped to the `target.resource.resource_subtype` UDM field. |
| Version | `metadata.product_version` |
### AlertUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "AlertUpdated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT security_result.category is set to DATA_EXFILTRATION |
| AlertId | `target.resource.product_object_id` |
| AlertType | `target.resource.attribute.labels.key/value` |
| Name | `security_result.description` |
| PolicyId | `security_result.detection_fields[PolicyId]` |
| Status | `security_result.detection_fields[Status]` |
| Severity | `security_result.severity` |
| Category | `security_result.category_details` |
| Source | `security_result.detection_fields[Source]` |
| Comments | `security_result.about.investigation.comments` |
| Data | `additional.fields.key` and `additional.fields.value.string_value` |
| AlertEntityId | target.user.userid or target.user.email_addresses |
| EntityType | `target.resource.resource_subtype` The `EntityType` log field is mapped to the `target.resource.resource_subtype` UDM field. |
| Version | `metadata.product_version` |
### Get-ComplianceCase
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ComplianceCase" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Get-CaseHoldPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Get-CaseHoldPolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Get-ComplianceSearch
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ComplianceSearch" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Remove-CaseHoldPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-CaseHoldPolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Set-CaseHoldPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Set-CaseHoldPolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `target.resource.name` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### New-CaseHoldRule
The following table lists the log fields and corresponding UDM mappings for the operation "New-CaseHoldRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_name` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Remove-CaseHoldRule
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-CaseHoldRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_DELETION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_product_object_id` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-CaseHoldRule
The following table lists the log fields and corresponding UDM mappings for the operation "Set-CaseHoldRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_product_object_id` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-ComplianceSearchAction
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ComplianceSearchAction" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### New-ComplianceCase
The following table lists the log fields and corresponding UDM mappings for the operation "New-ComplianceCase" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Remove-ComplianceCase
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-ComplianceCase" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Set-ComplianceCase
The following table lists the log fields and corresponding UDM mappings for the operation "Set-ComplianceCase" and workload "Set-ComplianceCase":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_WRITTEN target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Add-ComplianceCaseMember
The following table lists the log fields and corresponding UDM mappings for the operation "Add-ComplianceCaseMember" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_name` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-ComplianceCaseMember
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-ComplianceCaseMember" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_name` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Update-ComplianceCaseMember
The following table lists the log fields and corresponding UDM mappings for the operation "Update-ComplianceCaseMember" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### New-ComplianceSearch
The following table lists the log fields and corresponding UDM mappings for the operation "New-ComplianceSearch" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-ComplianceSearch
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-ComplianceSearch" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-ComplianceSearch
The following table lists the log fields and corresponding UDM mappings for the operation "Set-ComplianceSearch" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Start-ComplianceSearch
The following table lists the log fields and corresponding UDM mappings for the operation "Start-ComplianceSearch" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Stop-ComplianceSearch
The following table lists the log fields and corresponding UDM mappings for the operation "Stop-ComplianceSearch" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### New-ComplianceSearchAction
The following table lists the log fields and corresponding UDM mappings for the operation "New-ComplianceSearchAction" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-ComplianceSearchAction
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-ComplianceSearchAction" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### New-ComplianceSecurityFilter
The following table lists the log fields and corresponding UDM mappings for the operation "New-ComplianceSecurityFilter" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-ComplianceSecurityFilter
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-ComplianceSecurityFilter" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-ComplianceSecurityFilter
The following table lists the log fields and corresponding UDM mappings for the operation "Set-ComplianceSecurityFilter" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Add-eDiscoveryCaseAdmin
The following table lists the log fields and corresponding UDM mappings for the operation "Add-eDiscoveryCaseAdmin" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSION |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-eDiscoveryCaseAdmin
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-eDiscoveryCaseAdmin" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSION |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### New-CaseHoldPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "New-CaseHoldPolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Get-AadProtectionLevel
The following table lists the log fields and corresponding UDM mappings for the operation "Get-AadProtectionLevel" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Get-AutoSensitivityLabelPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Get-AutoSensitivityLabelPolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Get-DlpSensitiveInformationType
The following table lists the log fields and corresponding UDM mappings for the operation "Get-DlpSensitiveInformationType" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Get-Label
The following table lists the log fields and corresponding UDM mappings for the operation "Get-Label" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Get-LabelPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Get-LabelPolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Get-PolicyConfig
The following table lists the log fields and corresponding UDM mappings for the operation "Get-PolicyConfig" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### ValidaterbacAccessCheck
The following table lists the log fields and corresponding UDM mappings for the operation "ValidaterbacAccessCheck" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `security_result.description` |
| RelativeUrl | `additional_fields[relative_url]` The `RelativeUrl` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `relative_url`. |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### ApplicableAdaptiveScopeChange
The following table lists the log fields and corresponding UDM mappings for the operation "ApplicableAdaptiveScopeChange" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | target.resource.product_object_id If Name is AssociatedAdaptiveScopeIds then Value is target.resource.product_object_id |
| CorrelationId | `security_result.detection_fields` |
| ObjectType | `security_result.summary` |
### NewComplianceTag
The following table lists the log fields and corresponding UDM mappings for the operation "NewComplianceTag" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### NewRetentionComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "NewRetentionComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### NewRetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "NewRetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### RemoveComplianceTag
The following table lists the log fields and corresponding UDM mappings for the operation "RemoveComplianceTag" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_DELETION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| ObjectType | `security_result.summary` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### RemoveRetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "RemoveRetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | target.user.user_display_name target.resource.name security_result.description target.resource.attribute.labels.key/value If Name is CreatedBy then Value is mapped to target.user.user_display_name If Name is PolicyName then Value is mapped to target.resource.name If Name is Description then Value is security_result.description If Name is RetentionAction or WorkLoad or LabelName then target.resource.attribute.labels.key/value |
| ObjectType | `security_result.summary` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### SetComplianceTag
The following table lists the log fields and corresponding UDM mappings for the operation "SetComplianceTag" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | target.user.user_display_name target.resource.name security_result.description target.resource.attribute.labels.key/value If Name is CreatedBy then Value is mapped to target.user.user_display_name If Name is LabelName then Value is mapped to target.resource.name If Name is Description then Value is security_result.description If Name is RetentionAction or WorkLoad then target.resource.attribute.labels.key/value |
| ObjectType | `security_result.summary` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### SetRetentionComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "SetRetentionComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING Required fields for SETTING_MODIFICATION UDM validation : principal.machineid (IP or hostname or assetId or mac etc). ClientIP field is mandatory field for all the office 365 activities as per official doc of Office 365, but in some cases ClientIP field is absent If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | target.user.user_display_name target.resource.name security_result.description target.resource.attribute.labels.key/value If Name is CreatedBy then Value is mapped to target.user.user_display_name If Name is PolicyName then Value is mapped to target.resource.name If Name is Description then Value is security_result.description If Name is RetentionAction or WorkLoad or LabelName then target.resource.attribute.labels.key/value |
| ObjectType | `security_result.summary` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### SetRetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "SetRetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | target.user.user_display_name target.resource.name security_result.description target.resource.attribute.labels.key/value If Name is CreatedBy then Value is mapped to target.user.user_display_name If Name is PolicyName then Value is mapped to target.resource.name If Name is Description then Value is security_result.description If Name is RetentionAction or WorkLoad or LabelName then target.resource.attribute.labels.key/value |
| ObjectType | `security_result.summary` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### Get-CsTeamsUpgradeOverridePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Get-CsTeamsUpgradeOverridePolicy" and workload "SkypeForBusiness":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| CmdletVersion | `metadata.product_version` |
| Parameters | `target.resource.attribute.labels` Iterate through each `param` in `Parameters`: If `param.Value` is not `empty` and if `param.Name` is equal to `Tenant`, `param.Value` is mapped to `target.resource.attribute.labels.value` and `target.resource.attribute.labels.key` is set to `Tenant`. Else if `param.Name` is equal to `identity`, `param.Value` is mapped to `target.resource.attribute.labels.value` and `target.resource.attribute.labels.key` is set to `Identity`. |
| SkypeForBusinessEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| TenantName | `metadata.product_deployment_id` The `TenantName` log field is mapped to the `metadata.product_deployment_id` UDM field. |
| Version | `metadata.product_version` |
### TeamsAdminAction
The following table lists the log fields and corresponding UDM mappings for the operation "TeamsAdminAction" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED If ResultStatus is Succeeded then Action is set to ALLOW If ResultStatus is Failed then Action is set to BLOCK |
| AdminActionDetail | `security_result.summary` |
| ClientApplication | `network.http.user_agent` |
| ExtraProperties | `security_result.detection_fields` If `ExtraProperties` is not `empty`, iterate through `ExtraProperties`: If `ExtraPropertie.Key` is equal to `CorrelationId`, `ExtraPropertie.Value` is mapped to `security_result.detection_fields.value` and `security_result.detection_fields.key` is set to `ExtraProperties_%{index}_%{ExtraPropertie.Key}`. The `ExtraPropertie.Value` is also mapped to `additional.fields.value` and `additional.fields.key` is set to `ExtraProperties_%{index}_%{ExtraPropertie.Key}`. |
| UserClaims | `principal.user.attributes.role.name` The `UserClaims` log field is mapped to the `principal.user.attributes.role.name` UDM field. |
| Version | `metadata.product_version` |
### Update-DistributionGroupMember
The following table lists the log fields and corresponding UDM mappings for the operation "Update-DistributionGroupMember" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is set to target.group.group_display_name security_result.summary is set to Group Members definition If ResultStatus is True then Action is set to ALLOW else Action is set to BLOCK |
| ClientVersion | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.group.group_display_name` and `about.user.user_display_name` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, `parameter.Value` is mapped to `target.group.group_display_name`. Else if `parameter.Name` is equal to `Members`, iterate through `members_list` and map `member` to `about.user.user_display_name`. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### SupervisoryReviewOLAudit
The following table lists the log fields and corresponding UDM mappings for the operation "SupervisoryReviewOLAudit" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_TRANSACTION extract auditscore form ResultStatus using ResultStatus .\*?Score:{auditScore} and map with security_result.confidenece_details is {auditScore} security_result.confidence will map based on auditScore |
| LogonType | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| InternalLogonType | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| MailboxOwnerUPN | target.user.email_addresses or target.user.userid |
| MailboxOwnerSid | `target.user.windows_sid` |
| MailboxOwnerMasterAccountSid | `additional.fields.key` and `additional.fields.value.string_value` |
| LogonUserSid | `principal.user.windows_sid` |
| LogonUserDisplayName | `principal.user.user_display_name` |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientInfoString | `network.http.user_agent` |
| ClientIPAddress | principal.ip and principal.port |
| ClientMachineName | `principal.hostname` |
| ClientProcessName | `principal.process.file.full_path` |
| ClientVersion | `metadata.product_version` |
| ExchangeDetails | network.direection network.email.from network.email.mail_id network.email.to network.email.subject If Directionality is Incoming then network.direction is mapped to INBOUND If Directionality is Outgoining then network.direction is mapped to OUTBOUND From is mapped to network.email.from InternetMessageId is mapped to network.email.mail_id Recipients is mapped to network.email.to Subject is mapped to network.email.subject |
| Version | `metadata.product_version` |
### CrmDefaultActivity
The following table lists the log fields and corresponding UDM mappings for the operation "CrmDefaultActivity" and workload "CRM":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_READ |
| CrmOrganizationUniqueName | `principal.resource.name` |
| InstanceUrl | `target.url` |
| ItemUrl | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| Fields | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityName | `additional.fields.key` and `additional.fields.value.string_value` |
| Message | `security_result.summary` |
| Query | `additional.fields[Query]`
If the `Workload` log field value is equal to `PowerBI` then, the `additional.fields.key` UDM field is set to `query` and the `Query` log field is mapped to the `additional.fields.value` UDM field. |
| PrimaryFieldValue | `additional.fields.key` and `additional.fields.value.string_value` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| QueryResults | `additional.fields.key` and `additional.fields.value.string_value` |
| ServiceContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ServiceContextIdType | `additional.fields.key` and `additional.fields.value.string_value` |
| ServiceName | `principal.application` |
| SystemUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### TIMailData
The following table lists the log fields and corresponding UDM mappings for the operation "TIMailData" and workload "ThreatIntelligence":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to EMAIL_UNCATEGORIZED ObjectId is set to metadata.product_log_id |
| AttachmentData | about.file.full_path about.file.mime_type about.file.sha256 security_result.category_details AttachmentData.FileName is mapped to about.file.full_path AttachmentData.FileType is mapped to about.file.mime_type AttachmentData.SHA256 is mapped to about.file.sha256 AttachmentData.FileVerdict is 0 then AttachmentData.MalwareFamily is mapped to security_result.category_details |
| DetectionType | `security_result.summary` |
| DetectionMethod | `security_result.description` |
| InternetMessageId | `additional.fields.key` and `additional.fields.value.string_value` |
| NetworkMessageId | `additional.fields.key` and `additional.fields.value.string_value` |
| P1Sender | `network.email.reply_to` `network.smtp.mail_from`
If the `Operation` log field value is one of the following: - `UserSubmission` - `UserSubmissionTriage` - `AirInvestigationData` then, the `P1Sender` log field is mapped to the `network.smtp.mail_from` UDM field. Else, the `P1Sender` log field is mapped to the `network.email.reply_to` UDM field. |
| P2Sender | `network.email.from` |
| Policy | `security_result.rule_name` |
| PolicyAction | security_result.action PolicyAction is Quarantine then action is set to QUARANTINE PolicyAction is MoveToJmf then action is set to ALLOW_WITH_MODIFICATION |
| Recipients | `network.email.to` |
| SenderIp | `principal.ip` |
| Subject | `network.email.subject` |
| Verdict | `security_result.category` |
| MessageTime | `target.resource.attribute.labels.key/value` |
| EventDeepLink | `metadata.url_back_to_product` |
| DeliveryAction | `additional.fields.key` and `additional.fields.value.string_value` |
| OriginalDeliveryLocation | `additional.fields.key` and `additional.fields.value.string_value` |
| LatestDeliveryLocation | `additional.fields.key` and `additional.fields.value.string_value` |
| Directionality | `network.direction` |
| ThreatsAndDetectionTech | `additional.fields.key` and `additional.fields.value.string_value` |
| AdditionalActionsAndResults | `additional.fields.key` and `additional.fields.value.string_value` |
| Connectors | `additional.fields.key` and `additional.fields.value.string_value` |
| AuthDetails | `additional.fields.key` and `additional.fields.value.string_value` |
| PhishConfidenceLevel | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### SearchMtpStatus
The following table lists the log fields and corresponding UDM mappings for the operation "SearchMtpStatus" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SYSTEM_AUDIT_LOG_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
### RemovedFromSiteCollection
The following table lists the log fields and corresponding UDM mappings for the operation "RemovedFromSiteCollection" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| TargetUserOrGroupType | target.group.group_display_name target.user.userid target.user.email_addresses |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ApplicationDisplayName | `target.application` |
### CommentsDisabled
The following table lists the log fields and corresponding UDM mappings for the operation "CommentsDisabled" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| CorrelationId | `security_result.detection_fields.key/value.` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| SourceRelativeUrl | if ObjectId field is not present in log then target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceFileName | if ObjectId field is not present in log then target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` |
### FileRecycled
The following table lists the log fields and corresponding UDM mappings for the operation "FileRecycled" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| SiteUrl | `target.url_metadata.url` |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceFileExtension | `target.file.mime_type` |
| UserSharedWith | `additional.fields.key` and `additional.fields.value.string_value` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| ItemPropertyBag.LastModifiedDate | `target.file.last_modification_time` |
### CommentsEnabled
The following table lists the log fields and corresponding UDM mappings for the operation "CommentsEnabled" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceFileExtension | `target.file.mime_type` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileName | if ObjectId field is not present in log then target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | if ObjectId field is not present in log then target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| ApplicationDisplayName | `target.application` |
### FolderRecycled
The following table lists the log fields and corresponding UDM mappings for the operation "FolderRecycled" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_DELETION ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` |
| SiteUrl | `target.url_metadata.url` |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} target.file.names |
| SourceFileExtension | `target.file.mime_type` |
| UserSharedWith | `additional.fields.key` and `additional.fields.value.string_value` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserType | `additional.fields.key` and `additional.fields.value.string_value` |
### FileTranscriptRequested
The following table lists the log fields and corresponding UDM mappings for the operation "FileTranscriptRequested" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` |
| SiteUrl | `target.url_metadata.url` |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceFileExtension | `target.file.mime_type` |
| UserSharedWith | `additional.fields.key` and `additional.fields.value.string_value` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### WACTokenShared
The following table lists the log fields and corresponding UDM mappings for the operation "WACTokenShared" and workload "SharePoint" or "OneDrive":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` |
| SiteUrl | `target.url_metadata.url` |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceFileExtension | `target.file.mime_type` |
| UserSharedWith | `additional.fields.key` and `additional.fields.value.string_value` |
| SharingType | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### Update label
The following table lists the log fields and corresponding UDM mappings for the operation "Update label." and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### SiteLocksChanged
The following table lists the log fields and corresponding UDM mappings for the operation "SiteLocksChanged" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
### SiteIBModeSet
The following table lists the log fields and corresponding UDM mappings for the operation "SiteIBModeSet" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_UNCATEGORIZED target.resource.resource_type is set to SETTING ObjectId is mapped to target.url If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
### SiteDesignInvoked
The following table lists the log fields and corresponding UDM mappings for the operation "SiteDesignInvoked" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| EventData | `target.resource.product_object_id` The extracted `site_design_id` from `EventData` is mapped to the `target.resource.product_object_id` UDM field. |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
### SiteContentTypeCreated
The following table lists the log fields and corresponding UDM mappings for the operation "SiteContentTypeCreated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
### SiteCollectionQuotaModified
The following table lists the log fields and corresponding UDM mappings for the operation "SiteCollectionQuotaModified" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
### ShortcutAdded
The following table lists the log fields and corresponding UDM mappings for the operation "ShortcutAdded" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_PERMISSIONS_CHANGE ObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceFileExtension | `target.file.mime_type` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
### SPOIBIsEnabled
The following table lists the log fields and corresponding UDM mappings for the operation "SPOIBIsEnabled" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
### WebAccessRequestApproverModified
The following table lists the log fields and corresponding UDM mappings for the operation "WebAccessRequestApproverModified" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `RequestAccessEmail`, then the `NewValue` log field value is mapped to the `target.user.email_addresses` or `target.user.userid` UDM fields. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
### Set-TransportConfig
The following table lists the log fields and corresponding UDM mappings for the operation "Set-TransportConfig" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields` Iterate through each `data` in `Parameters`: The `data.Value` is mapped to `additional.fields.value` and `additional.fields.key` is set to `%{data.Name}`. |
### Set-TenantObjectVersion
The following table lists the log fields and corresponding UDM mappings for the operation "Set-TenantObjectVersion" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### Set-RecipientEnforcementProvisioningPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Set-RecipientEnforcementProvisioningPolicy" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-PolicyConfig
The following table lists the log fields and corresponding UDM mappings for the operation "Set-PolicyConfig" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to ACCESS_POLICY |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-OwaMailboxPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Set-OwaMailboxPolicy" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-MailboxPlan
The following table lists the log fields and corresponding UDM mappings for the operation "Set-MailboxPlan" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-LabelProperties
The following table lists the log fields and corresponding UDM mappings for the operation "Set-LabelProperties" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
| SessionId | `network.session_id` |
### Set-Label
The following table lists the log fields and corresponding UDM mappings for the operation "Set-Label" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-ExchangeAssistanceConfig
The following table lists the log fields and corresponding UDM mappings for the operation "Set-ExchangeAssistanceConfig" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `about.url` Iterate through each `field` in `Parameters`: If `field.Name` is equal to `PrivacyStatementURL`, `field.Value` is mapped to `about.url`. |
### Set-ConditionalAccessPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Set-ConditionalAccessPolicy" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionID | `network.session_id` |
### New-ConditionalAccessPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "New-ConditionalAccessPolicy" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionID | `network.session_id` |
### RemovedSearchReport
The following table lists the log fields and corresponding UDM mappings for the operation "RemovedSearchReport" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION ObjectId is set to `target.resource.name ` UDM field. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `target.resource.product_object_id` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `CaseId`, then the `Value` log field value is mapped to the `target.resource.product_object_id` UDM field. Else, if the `Name` log field value is equal to `SearchIds`, then the `Value` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ObjectType | `security_result.summary` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### Get-PrivacyManagementPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Get-PrivacyManagementPolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[Parameters]` The `Parameters` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `Parameters`. |
### Set-RetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Set-RetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT target.resource.resource_type is set to SETTING If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[Parameters]` The `Parameters` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Parameters`. |
### SearchTrialOffer
The following table lists the log fields and corresponding UDM mappings for the operation "SearchTrialOffer" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchTIKustoClusterInformation
The following table lists the log fields and corresponding UDM mappings for the operation "SearchTIKustoClusterInformation" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchMtpRoleInfo
The following table lists the log fields and corresponding UDM mappings for the operation "SearchMtpRoleInfo" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchMailflowForwardingData
The following table lists the log fields and corresponding UDM mappings for the operation "SearchMailflowForwardingData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchDataInsightsSubscription
The following table lists the log fields and corresponding UDM mappings for the operation "SearchDataInsightsSubscription" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchCustomerInsight
The following table lists the log fields and corresponding UDM mappings for the operation "SearchCustomerInsight" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchConnectorReportData
The following table lists the log fields and corresponding UDM mappings for the operation "SearchConnectorReportData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchAlertAggregate
The following table lists the log fields and corresponding UDM mappings for the operation "SearchAlertAggregate" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchAlert
The following table lists the log fields and corresponding UDM mappings for the operation "SearchAlert" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### Enable-AddressListPaging
The following table lists the log fields and corresponding UDM mappings for the operation "Enable-AddressListPaging" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### Install-AdminAuditLogConfig
The following table lists the log fields and corresponding UDM mappings for the operation "Install-AdminAuditLogConfig" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### AccessedAggregates
The following table lists the log fields and corresponding UDM mappings for the operation "AccessedAggregates" and workload "Mip":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| DataType | `security_result.description` |
| version | `metadata.product_version` |
### AccessedSiteList
The following table lists the log fields and corresponding UDM mappings for the operation "AccessedSiteList" and workload "Mip":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| DataType | `security_result.description` |
| version | `metadata.product_version` |
### Install-DataClassificationConfig
The following table lists the log fields and corresponding UDM mappings for the operation "Install-DataClassificationConfig" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-UnifiedGroup
The following table lists the log fields and corresponding UDM mappings for the operation "Set-UnifiedGroup" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. if ResultStatus is TRUE then security_result.action is set to ALLOW else security_result.action is set to BLOCK |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.user.email_addresses` The extracted `email` from `email_addresses` is mapped to the `target.user.email_addresses` UDM field. The extracted `email_address` from `group_email_address` is mapped to the `target.user.email_addresses` UDM field. |
| SessionId | `network.session_id` |
### ApplicableAdaptivePolicyChange
The following table lists the log fields and corresponding UDM mappings for the operation "ApplicableAdaptivePolicyChange" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | security_result.detection_fields.key/value. target.resource.product_object_id if Name is CorrelationId then Name is mapped to security_result.detection_fields.key/value. if Name is AssociatedAdaptivePolicyIds then AssociatedAdaptivePolicyIds is mapped to target.resource.product_object_id |
| ObjectType | `security_result.summary` |
### Get-AppRetentionComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "Get-AppRetentionComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### New-AppRetentionComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "New-AppRetentionComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
### New-AppRetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "New-AppRetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
### Set-AppRetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Set-AppRetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
### Install-DefaultSharingPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Install-DefaultSharingPolicy" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SYSTEM_AUDIT_LOG_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### Install-ResourceConfig
The following table lists the log fields and corresponding UDM mappings for the operation "Install-ResourceConfig" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SYSTEM_AUDIT_LOG_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### New-Mailbox
The following table lists the log fields and corresponding UDM mappings for the operation "New-Mailbox" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZEDObjectId is mapped to target.url |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
### Add-MailboxFolderPermission
The following table lists the log fields and corresponding UDM mappings for the operation "Add-MailboxFolderPermission" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### New-LabelPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "New-LabelPolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION target.resource.resource_type is set to ACCESS_POLICY |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### New-Label
The following table lists the log fields and corresponding UDM mappings for the operation "New-Label" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-ActivityAlert
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ActivityAlert" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-ProtectionAlert
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ProtectionAlert" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchComplianceCase
The following table lists the log fields and corresponding UDM mappings for the operation "SearchComplianceCase" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-ComplianceTag
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-ComplianceTag" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_DELETION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-AppRetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-AppRetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION target.resource_resource_type is set to ACCESS_POLICY |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-RetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-RetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION target.resource_resource_type is set to ACCESS_POLICY |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### New-ComplianceTag
The following table lists the log fields and corresponding UDM mappings for the operation "New-ComplianceTag" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Enable-ComplianceTagStorage
The following table lists the log fields and corresponding UDM mappings for the operation "Enable-ComplianceTagStorage" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-ComplianceRetentionEventType
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ComplianceRetentionEventType" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### AggregateActivityData
The following table lists the log fields and corresponding UDM mappings for the operation "AggregateActivityData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-ComplianceTag
The following table lists the log fields and corresponding UDM mappings for the operation "Set-ComplianceTag" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-FilePlanPropertyStructure
The following table lists the log fields and corresponding UDM mappings for the operation "Get-FilePlanPropertyStructure" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### New-ComplianceRetentionEventType
The following table lists the log fields and corresponding UDM mappings for the operation "New-ComplianceRetentionEventType" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION target.resource.resource_type is mapped to ACCESS_POLICY |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-DlpSensitiveInformationTypeRulePackage
The following table lists the log fields and corresponding UDM mappings for the operation "Get-DlpSensitiveInformationTypeRulePackage" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-ComplianceRetentionEvent
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ComplianceRetentionEvent" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### ComplianceSecurityFilter
The following table lists the log fields and corresponding UDM mappings for the operation "ComplianceSecurityFilter" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-QuarantineMessage
The following table lists the log fields and corresponding UDM mappings for the operation "Get-QuarantineMessage" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### AggregateThreatProfileDetails
The following table lists the log fields and corresponding UDM mappings for the operation "AggregateThreatProfileDetails" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SYSTEM_AUDIT_LOG_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-DlpDetectionsReport
The following table lists the log fields and corresponding UDM mappings for the operation "Get-DlpDetectionsReport" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| Parameters | `security_result.detection_fields` `security_result.rule_name` If `Parameters` is not `empty`, the extracted `start_date` field is mapped to `security_result.detection_fields.value` with key `start_date`. The extracted `end_date` field is mapped to `security_result.detection_fields.value` with key `end_date`. The extracted `event_type` field is mapped to `security_result.detection_fields.value` with key `event_type`. The extracted `source` field is mapped to `security_result.detection_fields.value` with key `source`. The extracted `dlp_compliance_rule` field is mapped to `security_result.rule_name`. |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-AppRetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Get-AppRetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Add-RoleGroupMember
The following table lists the log fields and corresponding UDM mappings for the operation "Add-RoleGroupMember" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is set to target.group.group_display_name security_result.summary is set to Group Members definition If ResultStatus is True { Action is set to ALLOW } else { Action is set to BLOCK } |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| Parameters | `target.group.group_display_name` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the `parameter.Value` is mapped to the `target.group.group_display_name` UDM field. |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| SessionId | `network.session_id` |
### Update-RoleGroupMember
The following table lists the log fields and corresponding UDM mappings for the operation "Update-RoleGroupMember" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is set to target.group.group_display_name security_result.summary is set to Group Members definition If ResultStatus is True { Action is set to ALLOW } else { Action is set to BLOCK } |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientVersion | `metadata.product_version` |
| Parameters | `target.group.attribute.labels[identity]` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the `parameter.Value` is mapped to the UDM field `target.group.attribute.labels.value` and the UDM field `target.group.attribute.labels.key` is set to `Identity`. |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| SessionId | `network.session_id` |
### New-RoleGroup
The following table lists the log fields and corresponding UDM mappings for the operation "New-RoleGroup" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_UNCATEGORIZED ObjectId is set to target.group.group_display_name security_result.summary is set to Group Members definition If ResultStatus is True { Action is set to ALLOW } else { Action is set to BLOCK } |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| Parameters | `target.group.attribute.labels[identity]` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the `parameter.Value` is mapped to the UDM field `target.group.attribute.labels.value` and the UDM field `target.group.attribute.labels.key` is set to `Identity`. |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| SessionId | `network.session_id` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
### Provision-ComplianceMailboxFolder
The following table lists the log fields and corresponding UDM mappings for the operation "Provision-ComplianceMailboxFolder" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientVersion | `metadata.product_version` |
| version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### Remove-Mailbox
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-Mailbox" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientVersion | `metadata.product_version` |
| version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### New-QuarantinePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "New-QuarantinePolicy" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| ClientVersion | `metadata.product_version` |
| version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
### Get-RoleGroup
The following table lists the log fields and corresponding UDM mappings for the operation "Get-RoleGroup" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_UNCATEGORIZED ObjectId is set to target.group.group_display_name security_result.summary is set to Group Members definition If ResultStatus is True { Action is set to ALLOW } else { Action is set to BLOCK } |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchLabelAnalyticsActivityData
The following table lists the log fields and corresponding UDM mappings for the operation "SearchLabelAnalyticsActivityData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-DlpCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Get-DlpCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to ACCESS_POLICY |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchSecurityRedirection
The following table lists the log fields and corresponding UDM mappings for the operation "SearchSecurityRedirection" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-ComplianceCaseMember
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ComplianceCaseMember" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### HoldViewed
The following table lists the log fields and corresponding UDM mappings for the operation "HoldViewed" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.category_details` |
| ExtendedProperties | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field.Else, If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| ObjectType | `security_result.summary` |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### Get-eDiscoveryCaseAdmin
The following table lists the log fields and corresponding UDM mappings for the operation "Get-eDiscoveryCaseAdmin" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SYSTEM_AUDIT_LOG_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-RoleGroupMember
The following table lists the log fields and corresponding UDM mappings for the operation "Get-RoleGroupMember" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_UNCATEGORIZED |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-ManagementRole
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ManagementRole" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-RoleGroup
The following table lists the log fields and corresponding UDM mappings for the operation "Set-RoleGroup" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_UNCATEGORIZED |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| ResultCountSecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-SecurityPrincipal
The following table lists the log fields and corresponding UDM mappings for the operation "Get-SecurityPrincipal" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-CaseHoldRule
The following table lists the log fields and corresponding UDM mappings for the operation "Get-CaseHoldRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_product_object_id` field is mapped to `target.resource.product_object_id` and the extracted `target_resource_name` field is mapped to `target.resource.name`. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### ViewedSearchReport
The following table lists the log fields and corresponding UDM mappings for the operation "ViewedSearchReport" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | principal.process.command_line If Name is CmdletOptions then store value of Value in process_args variable. If Name is Cmdlet then store value of Value in process_value variable. then map principal.process.command_line is {process_value} {process_args} |
| Version | `metadata.product_version` |
| Case | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| ExchangeLocations | `security_result.summary` |
| ExtendedProperties | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}` Else, If `data.Name` is equal to `Search Id`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| ObjectType | `security_result.summary` |
| PublicFolderLocations | `security_result.category_details` |
| Query | `security_result.description` |
| SharepointLocations | `security_result.category_details` |
### Get-AdaptiveScope
The following table lists the log fields and corresponding UDM mappings for the operation "Get-AdaptiveScope" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-RetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Get-RetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS target.resource.resource_type is set to ACCESS_POLICY |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### New-RetentionCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation "New-RetentionCompliancePolicy" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION target.resource.resource_type is set to ACCESS_POLICY |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### New-RetentionComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "New-RetentionComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_CREATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-ComplianceTag
The following table lists the log fields and corresponding UDM mappings for the operation "Get-ComplianceTag" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-RetentionComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "Set-RetentionComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-RegulatoryComplianceUI
The following table lists the log fields and corresponding UDM mappings for the operation "Get-RegulatoryComplianceUI" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-RetentionComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "Get-RetentionComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### New-AdaptiveScope
The following table lists the log fields and corresponding UDM mappings for the operation "New-AdaptiveScope" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Enable-AdaptiveScopeStorage
The following table lists the log fields and corresponding UDM mappings for the operation "Enable-AdaptiveScopeStorage" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchCustomTag
The following table lists the log fields and corresponding UDM mappings for the operation "SearchCustomTag" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-RegulatoryComplianceUI
The following table lists the log fields and corresponding UDM mappings for the operation "Set-RegulatoryComplianceUI" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
### RemoveRetentionComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "RemoveRetentionComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_DELETION |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| ExtendedProperties | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| ObjectType | `security_result.summary` |
### NewAdaptiveScope
The following table lists the log fields and corresponding UDM mappings for the operation "NewAdaptiveScope" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| ObjectType | `security_result.summary` |
| ExtendedProperties | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
### CommentCreated
The following table lists the log fields and corresponding UDM mappings for the operation "CommentCreated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceFileExtension | `target.file.mime_type` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| CommentId | `additional.fields.key` and `additional.fields.value.string_value` |
### DeviceAccessPolicyChanged
The following table lists the log fields and corresponding UDM mappings for the operation "DeviceAccessPolicyChanged" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `metadata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value.` |
| ModifiedProperties | `additional.fields.key` and `additional.fields.value.struct_value.fields` |
### HeartBeat
The following table lists the log fields and corresponding UDM mappings for the operation "HeartBeat" and workload "Aip":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_HEARTBEAT |
| Common | principal.resource.product_object_id principal.resource.name principal.resource.attribute.labels principal.hostname metadata.product_version ApplicationId is mapped to principal.resource.product_object_id ApplicationName is mapped to principal.resource.name ProcessName is mapped to principal.resource.attribute.labels\[process_name\] DeviceName is mapped to principal.hostname and principal.asset.hostname ProductVersion is mapped to metadata.product_version if Version is empty else ProductVersion is mapped to additional.fields\[version\] |
| Version | `metadata.product_version` |
### MessageCreation
The following table lists the log fields and corresponding UDM mappings for the operation "MessageCreation" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| MessageID | `target.resource.product_object_id` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### ThreadViewed
The following table lists the log fields and corresponding UDM mappings for the operation "ThreadViewed" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS if ResultStatus is SUCCEEDED then action is set to ALLOW else action is set to BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ThreadID | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### StreamEditAdminGlobalRoleMembers
The following table lists the log fields and corresponding UDM mappings for the operation "StreamEditAdminGlobalRoleMembers" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSION if ResultStatus is SUCCEEDED then action is set to ALLOW else action is set to BLOCK |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `target.resource.attribute.labels` The `OperationDetails.SetTo.PrincipalIds` field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `PrincipalIds`. The `OperationDetails.ResourceType` field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `ResourceType` The `OperationDetails.SetTo.AllowEveryoneInOrganization` field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `AllowEveryoneInOrganization` The `OperationDetails.ResourceId` field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `ResourceId` The `OperationDetails.SetTo.Role` field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `Role` The `OperationDetails.Id` field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `OperationDetails_Id`. |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeGetTextTrack
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeGetTextTrack" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeChannelView
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeChannelView" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeVideoMakePublic
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeVideoMakePublic" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### StreamInvokeGroupView
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeGroupView" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `metadata.description` |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### Set-CsOnlineDirectoryTenant
The following table lists the log fields and corresponding UDM mappings for the operation "Set-CsOnlineDirectoryTenant" and workload "SkypeForBusiness":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| CmdletVersion | `metadata.product_version` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SkypeForBusinessEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| TenantName | `target.resource.product_object_id` |
| Version | `metadata.product_version` |
### Set-CsHostedVoicemailPolicy
The following table lists the log fields and corresponding UDM mappings for the operation "Set-CsHostedVoicemailPolicy" and workload "SkypeForBusiness":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| CmdletVersion | `metadata.product_version` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SkypeForBusinessEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| TenantName | `target.resource.product_object_id` |
| Version | `metadata.product_version` |
### Get-CSSimpleUrlConfiguration
The following table lists the log fields and corresponding UDM mappings for the operation "Get-CSSimpleUrlConfiguration" and workload "SkypeForBusiness":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| CmdletVersion | `metadata.product_version` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SkypeForBusinessEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| TenantName | `target.resource.product_object_id` |
| Version | `metadata.product_version` |
### New-ExchangeAssistanceConfig
The following table lists the log fields and corresponding UDM mappings for the operation "New-ExchangeAssistanceConfig" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### New-App
The following table lists the log fields and corresponding UDM mappings for the operation "New-App" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
### PublishToWebReport
The following table lists the log fields and corresponding UDM mappings for the operation "PublishToWebReport" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| ReportName | `target.resource.name` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| DatasetId | `target.resource.attribute.labels.key/value` |
| ReportId | `target.resource.product_object_id` |
| ReportType | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| UserAgent | `network.http.user_agent` |
| DistributionMethod | `additional.fields.key` and `additional.fields.value.string_value` |
### UpdateGateway
The following table lists the log fields and corresponding UDM mappings for the operation "UpdateGateway" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| GatewayId | `target.resource.product_object_id` |
### ShareDataset
The following table lists the log fields and corresponding UDM mappings for the operation "ShareDataset" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
| ArtifactId | `target.resource.product_object_id` |
| ArtifactName | `target.resource.name` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| UserAgent | `network.http.user_agent` |
| SharingAction | `additional.fields.key` and `additional.fields.value.string_value` |
### GetRefreshablesAsAdmin
The following table lists the log fields and corresponding UDM mappings for the operation "GetRefreshablesAsAdmin" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
### CreateTagJob
The following table lists the log fields and corresponding UDM mappings for the operation "CreateTagJob" and workload "Compliance":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| CaseID | `target.resource.product_object_id` |
| CaseName | `target.resource.name` |
| EndTime | `additional.fields[end_time]` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` |
| StartTime | `additional.fields[start_time]` |
### Add delegated permission grant
The following table lists the log fields and corresponding UDM mappings for the operation `Add delegated permission grant` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_PERMISSIONS` |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `target.resource.product_object_id` `target.resource.name` `security_result.summary` If `Name` is `ServicePrincipal.ObjectId` then `NewValue` is mapped to `target.resource.product_object_id` If `Name` is `ServicePrincipal.DisplayName` then `NewValue` is mapped to `target.resource.name` If `Name` is `Included Updated Properties` then `NewValue` is mapped to `security_result.summary` If `Name` is `DelegatedPermissionGrant.Scope` then `NewValue` and `OldValue` is mapped to `target.resource.attribute.labels.key/value` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `target.user.userid` or `target.user.email_addresses` `security_result.detection_fields.key/value` If `Type` is 5 then `ID` is mapped to `target.uset.userid` or `target.user.email_addresses` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add app role assignment to service principal
The following table lists the log fields and corresponding UDM mappings for the operation "Add app role assignment to service principal" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.product_object_id target.resource.name security_result.summary If Name is ServicePrincipal.ObjectId then NewValue is mapped to target.resource.product_object_id If Name is ServicePrincipal.DisplayName then NewValue is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Update to application
The following table lists the log fields and corresponding UDM mappings for the operation "Update to application" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | security_result.summary If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Update application -- Certificates and secrets management
The following table lists the log fields and corresponding UDM mappings for the operation `Update application -- Certificates and secrets management` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT` if `ObjectId` has unique field in the log then and then only it will be mapped. |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` If `Name` is `Included Updated Properties` then `NewValue` is mapped to `security_result.summary` If `Name` is `RequiredResourceAccess` then `New Value` and `Old Value` is mapped with `target.resource.attribute.labels.key/value` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `target.user.userid` or `target.user.email_addresses` `security_result.detection_fields.key/value` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add owner to application
The following table lists the log fields and corresponding UDM mappings for the operation "Add owner to application" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_CHANGE_PERMISSION |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.product_object_id target.resource.name security_result.summaryIf Name is Application.ObjectId then NewValue is mapped to target.resource.product_object_id If Name is Application.DisplayName then NewValue is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add to application
The following table lists the log fields and corresponding UDM mappings for the operation "Add to application" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.name security_result.summary If Name is DisplayName then NewValue is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add device configuration
The following table lists the log fields and corresponding UDM mappings for the operation "Add device configuration" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.name security_result.summary If Name is DisplayName then NewValue is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add unverified domain
The following table lists the log fields and corresponding UDM mappings for the operation "Add unverified domain" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.name security_result.summary If Name is Name then NewValue is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add policy
The following table lists the log fields and corresponding UDM mappings for the operation "Add policy" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| Version | `metadata.product_version` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.name security_result.summary If Name is DisplayName then NewValue is mapped to target.resource.name If Name is Included Updated Properties then NewValue is mapped to security_result.summary |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `security_result.detection_fields.key/value` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### CreateResponse
The following table lists the log fields and corresponding UDM mappings for the operation "CreateResponse" and workload "MicrosoftForms":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| FormsUserTypes | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application` |
| FormName | `target.resource.name` |
| FormId | `target.resource.product_object_id` |
### EditForm
The following table lists the log fields and corresponding UDM mappings for the operation "EditForm" and workload "MicrosoftForms":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| FormsUserTypes | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application` |
| FormName | `target.resource.name` |
| FormId | `target.resource.product_object_id` |
### SubmitResponse
The following table lists the log fields and corresponding UDM mappings for the operation "SubmitResponse" and workload "MicrosoftForms":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| FormsUserTypes | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application` |
| FormName | `target.resource.name` |
| FormId | `target.resource.product_object_id` |
### ViewResponses
The following table lists the log fields and corresponding UDM mappings for the operation "ViewResponses" and workload "MicrosoftForms":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| FormsUserTypes | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application` |
| FormName | `target.resource.name` |
| FormId | `target.resource.product_object_id` |
### ViewRuntimeForm
The following table lists the log fields and corresponding UDM mappings for the operation "ViewRuntimeForm" and workload "MicrosoftForms":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| FormsUserTypes | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application` |
| FormName | `target.resource.name` |
| FormId | `target.resource.product_object_id` |
### DeleteFlow
The following table lists the log fields and corresponding UDM mappings for the operation "DeleteFlow" and workload "MicrosoftForms":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_DELETION |
| FormsUserTypes | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application` |
| FormName | `about.resource.name` |
| FormId | `about.resource.product_object_id` |
### ListViewed
The following table lists the log fields and corresponding UDM mappings for the operation "ListViewed" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemCount | `additional.fields.key` and `additional.fields.value.string_value` |
| ListColor | `additional.fields.key` and `additional.fields.value.string_value` |
| ListIcon | `additional.fields.key` and `additional.fields.value.string_value` |
| TemplateTypeId | `additional.fields.key` and `additional.fields.value.string_value` |
### ListColumnUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "ListColumnUpdated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### ListContentTypeUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "ListContentTypeUpdated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### ListItemDeleted
The following table lists the log fields and corresponding UDM mappings for the operation "ListItemDeleted" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### ListUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "ListUpdated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListColor | `additional.fields.key` and `additional.fields.value.string_value` |
| ListIcon | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| TemplateTypeId | `additional.fields.key` and `additional.fields.value.string_value` |
| ApplicationDisplayName | `target.application` |
| ItemCount | `additional.fields.key` and `additional.fields.value.string_value` |
### ListItemCreated
The following table lists the log fields and corresponding UDM mappings for the operation "ListItemCreated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListColor | `additional.fields.key` and `additional.fields.value.string_value` |
| ListIcon | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| TemplateTypeId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemCount | `additional.fields.key` and `additional.fields.value.string_value` |
### ListColumnCreated
The following table lists the log fields and corresponding UDM mappings for the operation "ListColumnCreated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListColor | `additional.fields.key` and `additional.fields.value.string_value` |
| ListIcon | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| TemplateTypeId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SiteContentTypeUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "SiteContentTypeUpdated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### ListItemViewed
The following table lists the log fields and corresponding UDM mappings for the operation "ListItemViewed" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_READ ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemCount | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListColor | `additional.fields.key` and `additional.fields.value.string_value` |
| ListIcon | `additional.fields.key` and `additional.fields.value.string_value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
### ListItemUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "ListItemUpdated" and workload "SharePoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT ObjectId is mapped to target.url |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| EventSource | `target.application` |
| SourceName | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| MachineDomainInfo | `target.asset.attribute.labels.key/value` |
| MachineId | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| Version | `medata.product_version` |
| CorrelationId | `security_result.detection_fields.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| target.file.size | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListColor | `additional.fields.key` and `additional.fields.value.string_value` |
| ListIcon | `additional.fields.key` and `additional.fields.value.string_value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
### FileRenamed
The following table lists the log fields and corresponding UDM mappings for the operation "FileRenamed" and workload "Endpoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_MOVE |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| FileExtension | `target.file.mime_type` |
| FileType | `target.resource.attribute.labels.key/value` |
| PreviousFileName | `src.file.full_path` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetFilePath | `target.file.full_path` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### UpdatePowerApp
The following table lists the log fields and corresponding UDM mappings for the operation "UpdatePowerApp" and workload "PowerApps":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| Id | `metadata.product_log_id` |
### SubscribedToMessages
The following table lists the log fields and corresponding UDM mappings for the operation "SubscribedToMessages" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### MessageCreatedNotification
The following table lists the log fields and corresponding UDM mappings for the operation "MessageCreatedNotification" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| MessageId | `target.resource.product_object_id` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| MessageVersion | `target.resource.attribute.labels.key/value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| ChatThreadId | target.user.group_identifiers target.group.product_object_id |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### MessageUpdatedNotification
The following table lists the log fields and corresponding UDM mappings for the operation "MessageUpdatedNotification" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| MessageId | `target.resource.product_object_id` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| MessageVersion | `target.resource.attribute.labels.key/value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| ChatThreadId | target.user.group_identifiers target.group.product_object_id |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### MessageCreatedHasLink
The following table lists the log fields and corresponding UDM mappings for the operation "MessageCreatedHasLink" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| MessageId | `target.resource.product_object_id` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| ChatThreadId | target.user.group_identifiers target.group.product_object_id |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| MessageVersion | `target.resource.attribute.labels.key/value` |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### MessagesListed
The following table lists the log fields and corresponding UDM mappings for the operation "MessagesListed" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| ChannelGuid | `target.resource.product_object_id` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers and target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| Version | `metadata.product_version` |
### PerformedCardAction
The following table lists the log fields and corresponding UDM mappings for the operation "PerformedCardAction" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SYSTEM_AUDIT_LOG_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| AddOnGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnName | `additional.fields.key` and `additional.fields.value.string_value` |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelGuid | `target.resource.product_object_id` |
| ChannelName | `target.resource.name` |
| ChannelType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers and target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| Version | `metadata.product_version` |
### MessageEditedHasLink
The following table lists the log fields and corresponding UDM mappings for the operation "MessageEditedHasLink" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| MessageId | `target.resource.product_object_id` |
| MessageURLs | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| SubscriptionId | `target.resource.attribute.labels.key/value` |
| ChatThreadId | target.user.group_identifiers target.group.product_object_id |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| MessageVersion | `target.resource.attribute.labels.key/value` |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### MeetingParticipantDetail
The following table lists the log fields and corresponding UDM mappings for the operation "MeetingParticipantDetail" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Attendees | about.resource.product_object_id about.user.product_object_id about.user.attribute.roles.name OrganizationId is mapped to about.resource.product_object_id Role is mapped to about.user.attribute.roles.name UserObjectId is set to about.user.product_object_id |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| JoinTime | `target.resource.attribute.creation_time` |
| LeaveTime | `target.resource.attribute.last_update_time` |
| MeetingDetailId | `target.resource.product_object_id` |
| Version | `metadata.product_version` |
### MeetingDetail
The following table lists the log fields and corresponding UDM mappings for the operation "MeetingDetail" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| StartTime | `additional.fields[start_time]` |
| EndTime | `additional.fields[end_time]` |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| MeetingURL | `target.url` |
| MessageId | `target.resource.product_object_id` |
| ChatThreadId | target.user.group_identifiers target.group.product_object_id |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| Modalities | `ExtendedProperties.SubmissionSource` | `additional.fields[ExtendedProperties_SubmissionSource]` The `ExtendedProperties.SubmissionSource` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ExtendedProperties_SubmissionSource`. |
| Organizer | `principal.user.product_object_id` |
| Version | `metadata.product_version` |
### MessageUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "MessageUpdated" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT |
| ExtraProperties | `additional.fields.key` and `additional.fields.value.string_value` |
| MessageVersion | `target.resource.attribute.labels.key/value` |
| MessageId | `target.resource.product_object_id` |
| ChatThreadId | target.user.group_identifiers target.group.product_object_id |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### AggregateTransportQueueData
The following table lists the log fields and corresponding UDM mappings for the operation "AggregateTransportQueueData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### AuthorizeCustomerInsight
The following table lists the log fields and corresponding UDM mappings for the operation "AuthorizeCustomerInsight" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### AuthorizeConnectorReportData
The following table lists the log fields and corresponding UDM mappings for the operation "AuthorizeConnectorReportData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchAlertOverride
The following table lists the log fields and corresponding UDM mappings for the operation "SearchAlertOverride" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### AuthorizeMailflowForwardingData
The following table lists the log fields and corresponding UDM mappings for the operation "AuthorizeMailflowForwardingData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchDomainTrafficStatus
The following table lists the log fields and corresponding UDM mappings for the operation "SearchDomainTrafficStatus" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchAlertActivity
The following table lists the log fields and corresponding UDM mappings for the operation "SearchAlertActivity" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### AggregateMailmetadata
The following table lists the log fields and corresponding UDM mappings for the operation "AggregateMailmetadata" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### InsightGenerated
The following table lists the log fields and corresponding UDM mappings for the operation "InsightGenerated" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Category | `security_result.category_details` |
| Description | `security_result.description` |
| InsightId | `target.resource.product_object_id` |
| Name | `target.resource.name` |
| Version | `metadata.product_version` |
### UserSubmission
The following table lists the log fields and corresponding UDM mappings for the operation "UserSubmission" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|---|
| | metadata.event_type is mapped to SCAN_UNCATEGORIZED security_result.category is MAIL_SPAM |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| InternetMessageId | `network.email.mail_id` |
| KesMailId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtendedProperties | additional.fields | ExtendedProperties.SubmissionSource is mapped to additional.fields\[ExtendedProperties_SubmissionSource\] ExtendedProperties.SubmissionId is mapped to additional.fields\[ExtendedProperties_SubmissionId\] ExtendedProperties.SubmissionCategory is mapped to additional.fields\[ExtendedProperties_SubmissionCategory\] |
| P1SenderDomain | `network.dns_domain` |
| Recipients | `network.email.to` |
| SenderIP | `principal.ip` |
| Subject | `network.email.subject` |
| P2Sender | `network.email.from` |
| SubmissionState | `security_result.summary` |
| P1Sender | `network.smtp.mail_from` |
| Version | `metadata.product_version` |
### SaveRoleGroupMember
The following table lists the log fields and corresponding UDM mappings for the operation "SaveRoleGroupMember" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### AggregateCampaignIntelligenceData
The following table lists the log fields and corresponding UDM mappings for the operation "AggregateCampaignIntelligenceData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SYSTEM_AUDIT_LOG_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchEmailTimelineEvents
The following table lists the log fields and corresponding UDM mappings for the operation "SearchEmailTimelineEvents" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchAlertStory
The following table lists the log fields and corresponding UDM mappings for the operation "SearchAlertStory" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### AggregateThreatDetailsBulk
The following table lists the log fields and corresponding UDM mappings for the operation "AggregateThreatDetailsBulk" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-User
The following table lists the log fields and corresponding UDM mappings for the operation "Get-User" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_READ If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `target.user.email_addresses` If `Parameters` is not `empty`, the extracted `identity_email` field from `Parameters` is mapped to the `target.user.email_addresses` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### Get-DlpComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation "Get-DlpComplianceRule" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_READ If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
### AnalyzedByExternalApplication
The following table lists the log fields and corresponding UDM mappings for the operation "AnalyzedByExternalApplication" and workload "Power BI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to RESOURCE_READ |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.name` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | about.user.email_addresses about.user.user_display_name about.user.product_object_id about.user.attribute.permissions.name RecipientEmail is mapped to about.user.email_addresses RecipientName is mapped to about.user.user_display_name ObjectId is set to about.user.product_object_id ResharePermission is mapped to about.user.attribute.permissions.name |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| UserAgent | `network.http.user_agent` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
### New-MigrationBatch
The following table lists the log fields and corresponding UDM mappings for the operation "New-MigrationBatch" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields.key/value` Iterate through each `data` in `Parameters`: The `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| SessionId | `network.session_id` |
### UserSubmissionTriage
The following table lists the log fields and corresponding UDM mappings for the operation "UserSubmissionTriage" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|---|
| | metadata.event_type is mapped to SCAN_UNCATEGORIZED security_result.category is set to MAIL_SPAM |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| ExtendedProperties | additional.fields | ExtendedProperties.SubmissionSource is mapped to additional.fields\[ExtendedProperties_SubmissionSource\] ExtendedProperties.SubmissionId is mapped to additional.fields\[ExtendedProperties_SubmissionId\] ExtendedProperties.SubmissionCategory is mapped to additional.fields\[ExtendedProperties_SubmissionCategory\] |
| GradingResult | `security_result.category_details` |
| InternetMessageId | `network.email.mail_id` |
| KesMailId | `additional.fields.key` and `additional.fields.value.string_value` |
| P1Sender | `network.smtp.mail_from` |
| P1SenderDomain | `network.dns_domain` If `Workload` is equal to `P1SenderDomain`, the `P1SenderDomain` log field is mapped to the `network.dns_domain` UDM field. |
| P2Sender | `network.email.from` |
| Recipients | `network.email.to` |
| SenderIP | `principal.ip` |
| Subject | `network.email.subject` |
| SubmissionState | `security_result.summary` |
### FileArchived
The following table lists the log fields and corresponding UDM mappings for the operation "FileArchived" and workload "Endpoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| FileExtension | `target.file.mime_type` |
| FileSize | `target.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetFilePath | `target.file.full_path` |
| Version | `metadata.product_version` |
### FileCreatedOnNetworkShare
The following table lists the log fields and corresponding UDM mappings for the operation "FileCreatedOnNetworkShare" and workload "Endpoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_CREATION |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| FileExtension | `target.file.mime_type` |
| FileSize | `target.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetFilePath | `target.file.full_path` |
| Version | `metadata.product_version` |
### FileCreatedOnRemovableMedia
The following table lists the log fields and corresponding UDM mappings for the operation "FileCreatedOnRemovableMedia" and workload "Endpoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_CREATION |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| FileExtension | `target.file.mime_type` |
| FileSize | `target.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetFilePath | `target.file.full_path` |
| Version | `metadata.product_version` |
### SlimFilePrinted
The following table lists the log fields and corresponding UDM mappings for the operation "SlimFilePrinted" and workload "Endpoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE target.asset.type is PRINTER |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| DeviceName | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| FileType | `target.resource.attribute.labels.key/value` |
| TargetPrinterName | `target.asset.hostname` |
| Version | `metadata.product_version` |
### FilePrinted
The following table lists the log fields and corresponding UDM mappings for the operation "FilePrinted" and workload "Endpoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE target.asset.type is PRINTER |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| FileExtension | `target.file.mime_type` |
| FileSize | `target.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetPrinterName | `target.asset.hostname` |
| Version | `metadata.product_version` |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| FileExtension | `target.file.mime_type` |
| FileSize | `target.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| PreviousFileName | `src.file.full_path` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetFilePath | `target.file.full_path` |
| Version | `metadata.product_version` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### ArchiveCreated
The following table lists the log fields and corresponding UDM mappings for the operation "ArchiveCreated" and workload "Endpoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| FileExtension | `target.file.mime_type` |
| FileSize | `target.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetFilePath | `target.file.full_path` |
| Version | `metadata.product_version` |
### FileDownloadedFromBrowser
The following table lists the log fields and corresponding UDM mappings for the operation "FileDownloadedFromBrowser" and workload "Endpoint":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED |
| Application | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| FileExtension | `target.file.mime_type` |
| FileSize | `target.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetFilePath | `target.file.full_path` |
| Version | `metadata.product_version` |
### Create application password for user
The following table lists the log fields and corresponding UDM mappings for the operation "Create application password for user" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses security_result.detection_fields.key/value If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### SearchNdrDetailData
The following table lists the log fields and corresponding UDM mappings for the operation "SearchNdrDetailData" and workload "SecurityComplianceCenter":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GENERIC_EVENT |
| StartTime | `additional.fields[start_time]` |
| ClientRequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| ClientApplication | `principal.application` |
| Version | `metadata.product_version` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DatabaseType | `target.resource.attribute.labels.key/value` |
| DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### MessageUpdated
The following table lists the log fields and corresponding UDM mappings for the operation "MessageUpdated" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_CONTENT If ResultStatus is TRUE then action is ALLOW else action is BLOCK |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | `security_result.description` |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### Access
The following table lists the log fields and corresponding UDM mappings for the operation "Access" and workload "Aip":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS ObjectId is set to target.file.full_path |
| Common | target.resource.product_object_id target.resource.name target.process.command_line target.hostname metadata.product_version ApplicationId is mapped to target.resource.product_object_id ApplicationName is mapped to target.resource.name ProcessName is mapped to target.process.command_line DeviceName is mapped to target.hostname ProductVersion is mapped to metadata.product_version |
| DataState | `security_result.summary` |
| Version | `metadata.product_version` |
### Discover
The following table lists the log fields and corresponding UDM mappings for the operation "Discover" and workload "Aip":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS ObjectId is set to target.file.full_path |
| Common | target.resource.product_object_id target.resource.name target.process.command_line target.hostname metadata.product_version ApplicationId is mapped to target.resource.product_object_id ApplicationName is mapped to target.resource.name ProcessName is mapped to target.process.command_line DeviceName is mapped to target.hostname ProductVersion is mapped to metadata.product_version |
| DataState | `security_result.summary` |
| Version | `metadata.product_version` |
| Common.Location | `target.location.name` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### TIUrlClickData
The following table lists the log fields and corresponding UDM mappings for the operation "TIUrlClickData" and workload "ThreatIntelligence":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| AppName | `target.application` |
| AppVersion | `metadata.product_version` |
| EventDeepLink | `metadata.url_back_to_product` |
| SourceId | AppName is Mail then SourceId is mapped to network.email.id |
| Url | `target.url` |
| UserIp | `principal.ip` |
| Version | `metadata.product_version` |
| UrlClickAction | `security_result.detection_fields.key/value` |
### Device no longer managed
The following table lists the log fields and corresponding UDM mappings for the operation "Device no longer managed" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE target.resource.resource_type is set to DEVICE |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.asset.product_object_id target.platform If Name is TargetId.DeviceId then NewValue is mapped to target.asset.product_object_id If Name is TargetId.DeviceOSType then NewValue is mapped to target.platform |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### AirInvestigationData
The following table lists the log fields and corresponding UDM mappings for the operation "AirInvestigationData" and workload "AirInvestigation":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SYSTEM_AUDIT_LOG_UNCATEGORIZED If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| LastUpdateTimeUtc | `target.resource.attribute.last_update_time` |
| Status | `additional.fields[status]` The `Status` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `status`. |
| InvestigationId | `target.resource.product_object_id` |
| InvestigationType | `target.resource.attribute.labels.key/value` |
| Data | security_result.description security_result.category_details network.email.to network.email.from network.email.mail_id network.email.subject network.direction principal.ip principal.administrative_domain principal.user.email_addresses Data.Description is mapped to security_result.description Data.Category is mapped to security_result.category_details Data.Entities.1.Recipient is mapped to network.email.to Data.Entities.1.Sender is mapped to network.email.from Data.Entities.1.InternetMessageId is mapped to network.email.mail_id Data.Entities.1.Subject is mapped to network.email.subject Data.Entities.1.AntispamDirection is mapped to network.direction Data.Entities.1.SenderIP is mapped to principal.ip Data.Entities.1.P1SenderDomain is mapped to principal.administrative_domain Data.Entities.1.P1Sender is mapped to principal.user.email_addresses |
| InvestigationName | `security_result.summary` |
| StartTimeUtc | `target.resource.attribute.creation_time` |
| Version | `metadata.product_versionn` |
| DeepLinkUrl | `metadata.url_back_to_product` |
### Set-MailboxJunkEmailConfiguration
The following table lists the log fields and corresponding UDM mappings for the operation "Set-MailboxJunkEmailConfiguration" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| OriginatingServer | `principal.hostname` |
| OrganizationName | `target.administrative_domain` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| Parameters | `about.user.email_addresses` Iterate through `Parameters`: If `field.Name` is equal to `BlockedSendersAndDomains` and `field.Value` is not `empty`, iterate through each `email` in `field.Value`. If `email` matches the regular expression pattern `(^.+@.+$)`, the `email` is mapped to the `about.user.email_addresses` UDM field. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
### New-DistributionGroup
The following table lists the log fields and corresponding UDM mappings for the operation "New-DistributionGroup" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_CREATION ObjectId is set to target.group.group_display_name security_result.summary is set to Group Members definition If ResultStatus is True then Action is set to ALLOW else Action is set to BLOCK |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `target.group.group_display_name`, `about.user.attribute.labels`, `about.user.user_display_name` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Name`, the `parameter.Value` is mapped to the `target.group.group_display_name` UDM field. Else if `parameter.Name` is equal to `ManagedBy`, the `parameter.Value` is mapped to `about.user.attribute.labels.value` and `about.user.attribute.labels.key` is set to `managed_by`. Else if `parameter.Name` is equal to `Members`, the `parameter.Value` is mapped to the `about.user.user_display_name` UDM field. |
| SessionId | `network.session_id` |
### Add-DistributionGroupMember
The following table lists the log fields and corresponding UDM mappings for the operation "Add-DistributionGroupMember" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION ObjectId is set to target.group.group_display_name security_result.summary is set to Group Members definition If ResultStatus is True then Action is set to ALLOW else Action is set to BLOCK |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
### Remove-InboxRule
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-InboxRule" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_DELETION target.resource.resource_type is set to SETTING ObjectId is set to target.group.product_object_id |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
### Enable-Mailbox
The following table lists the log fields and corresponding UDM mappings for the operation "Enable-Mailbox" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_CREATION |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
### Import
The following table lists the log fields and corresponding UDM mappings for the operation "Import" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to FILE_UNCATEGORIZED |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | target.user.email_addresses target.user.attribute.permission.name We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | `target.user.user_display_name` `target.user.product_object_id` `target.user.email_addresses` `target.user.attribute.permissions.name`
Iterate for each element `info` in the `SharingInformation` log field array, then The `info.RecipientName` log field is mapped to the `target.user.user_display_name` UDM field. The `info.ObjectId` log field is mapped to the `target.user.product_object_id` UDM field. The `info.RecipientEmail` log field is mapped to the `target.user.email_addresses` UDM field. If the `info.ResharePermission` value is not `empty` then, the `info.ResharePermission` log field is mapped to the `target.user.attribute.permissions.name` UDM field. |
| WorkSpaceName | `target.resource.name` |
| WorkspaceId | `target.resource.product_object_id` |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| ImportSource | `additional.fields.key` and `additional.fields.value.string_value` |
| ImportType | `target.file.mime_type` |
| ImportDisplayName | `target.file.full_path` |
### Device no longer compliant
The following table lists the log fields and corresponding UDM mappings for the operation "Device no longer compliant" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE target.resource.resource_type is set to DEVICE |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.platform target.resource.product_object_id If Name is TargetId.DeviceId then NewValue is mapped to target.resource.product_object_id If Name is TargetId.DeviceOSType then NewValue is mapped to target.platform |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Enable account
The following table lists the log fields and corresponding UDM mappings for the operation `Enable account` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_CHANGE_PERMISSIONS` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `target.resource.name` If `Name` is `Included Updated Properties` then `NewValue` is mapped to `security_result.summary` If `Name` is `Action Client Name` then `NewValue` is mapped to `target.resource.name` If `Name` is `HardDeleted` then `NewValue` and `OldValue` is mapped to `security_result.detection_fields.key/value` If `Name` is `GivenName` then `NewValue` and `OldValue` is mapped to `target.user.attribute.labels.key/value` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | `principal.ip and principal.port` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `target.user.userid or target.user.email_addresses` If `Type` is 5 then `ID` is mapped to `target.user.userid` or `target.user.email_addresses` else `security_result.detection_fields.key/value` |
| Target.1.ID | `target.user.product_object_id` |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add service principal credentials
The following table lists the log fields and corresponding UDM mappings for the operation "Add service principal credentials" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-SyncUser
The following table lists the log fields and corresponding UDM mappings for the operation "Set-SyncUser" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
### MessageSent
The following table lists the log fields and corresponding UDM mappings for the operation "MessageSent" and workload "MicrosoftTeams":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE If ClientIP field is absent then metadata.event_type is mapped to GENERIC_EVENT. |
| MessageSizeInBytes | `target.resource.attribute.labels.key/value` |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | target.user.group_identifiers target.group.product_object_id |
| TeamName | `target.group.group_display_name` |
| AADGroupId | `additional.fields.key` and `additional.fields.value.string_value` |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| MessageId | `target.resource.product_object_id` |
| Version | `metadata.product_version` |
| MessageVersion | `target.resource.attribute.labels.key/value` |
### Remove service principal credentials
The following table lists the log fields and corresponding UDM mappings for the operation "Remove service principal credentials" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `Included Updated Properties`, then the `NewValue` log field value is mapped to the `security_result.summary` UDM field. Else, the `NewValue` log field value is mapped to the , `additional.fields.key` and `additional.fields.value.struct_value.fields` UDM fields. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Remove-MoveRequest
The following table lists the log fields and corresponding UDM mappings for the operation "Remove-MoveRequest" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### StreamInvokeGetTranscript
The following table lists the log fields and corresponding UDM mappings for the operation "StreamInvokeGetTranscript" and workload "MicrosoftStream":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_COMMUNICATION |
| ClientApplicationId | `additional.fields.key` and `additional.fields.value.string_value` |
| EntityPath | `additional.fields[entity_path]` |
| OperationDetails | `additional.fields[operation_details]` The `OperationDetails` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `operation_details`. |
| ResourceTitle | `target.resource.name` |
| ResourceUrl | `target.url` |
| Version | `metadata.product_version` |
### Remove owner from group
The following table lists the log fields and corresponding UDM mappings for the operation "Remove owner from group" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to GROUP_MODIFICATION |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.group.product_object_id target.group.group_display_nameIf Name is Group.ObjectID then NewValue is mapped to target.group.product_object_id If Name is Group.DisplayName then NewValue is mapped to target.group.group_display_name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Add app role assignment to group
The following table lists the log fields and corresponding UDM mappings for the operation "Add app role assignment to group" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | target.resource.product_object_id target.resource.name target.group.group_display_name If Name is AppRole.Id then NewValue is mapped to target.resource.product_object_id If Name is AppRole.DisplayName then NewValue is mapped to target.resource.name If Name is Group.DisplayName then NewValue is mapped to target.group.group_display_name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### Disable-MailUser
The following table lists the log fields and corresponding UDM mappings for the operation "Disable-MailUser" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_UNCATEGORIZED ResultStatus is True Action is set to BLOCK |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### New-FolderMoveRequest
The following table lists the log fields and corresponding UDM mappings for the operation "New-FolderMoveRequest" and workload "Exchange":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to STATUS_UPDATE |
| Version | `metadata.product_version` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### Add owner to policy
The following table lists the log fields and corresponding UDM mappings for the operation "Add owner to policy" and workload "AzureActiveDirectory":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_UPDATE_PERMISSIONS |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | If Name is Policy.ObjectID then NewValue is mapped to target.resource.product_object_id If Name is Policy.DisplayName then NewValue is mapped to target.resource.name |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ActorIpAddress | principal.ip and principal.port |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | target.user.userid or target.user.email_addresses If Type is 5 then ID is mapped to target.user.userid or target.user.email_addresses else security_result.detection_fields.key/value |
| version | `metadata.product_version` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
### EditContentProviderProperties
The following table lists the log fields and corresponding UDM mappings for the operation "EditContentProviderProperties" and workload "PowerBI":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to SETTING_MODIFICATION target.resource.resource_type is set to SETTING |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| DataClassification | `additional.fields.key` and `additional.fields.value.string_value` |
| DatasetName | `target.resource.attribute.labels.key/value` |
| OrgAppPermission | We map this field based on value of UpdateApp Operation value. recipients is mapped to target.user.email_addresses permissions is mapped to target.user.attribute.permissions.name |
| ReportName | `target.resource.attribute.labels.key/value` |
| SharingInformation | `target.user.user_display_name` `target.user.product_object_id` `target.user.email_addresses` `target.user.attribute.permissions.name`
Iterate for each element `info` in the `SharingInformation` log field array, then The `info.RecipientName` log field is mapped to the `target.user.user_display_name` UDM field. The `info.ObjectId` log field is mapped to the `target.user.product_object_id` UDM field. The `info.RecipientEmail` log field is mapped to the `target.user.email_addresses` UDM field. If the `info.ResharePermission` value is not `empty` then, the `info.ResharePermission` log field is mapped to the `target.user.attribute.permissions.name` UDM field. |
| WorkSpaceName | `target.resource.name` |
| WorkspaceId | `target.resource.product_object_id` |
| SwitchState | `additional.fields.key` and `additional.fields.value.string_value` |
| ContentProviderCertificationStage | `security_result.summary` |
| AppId | `additional.fields.key` and `additional.fields.value.string_value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
### ReportingAccessed
The following table lists the log fields and corresponding UDM mappings for the operation "ReportingAccessed" and workload "Project":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| ItemType | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Entity | `metadata.product_name` |
| Version | `metadata.product_version` |
| Action | `security_result.action_details` |
| OnBehalfOfResId | `additional.fields.key` and `additional.fields.value.string_value` |
### GroupAccessFailure
The following table lists the log fields and corresponding UDM mappings for the operation "GroupAccessFailure" and workload "Yammer":
| Log field | UDM mapping |
|---|---|
| | metadata.event_type is mapped to USER_RESOURCE_ACCESS |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataExportType | `target.resource.attribute.labels.key/value` |
| FileId | `target.resource.product_object_id` |
| FileName | `target.file.full_path` |
| GroupName | `target.group.group_display_name` |
| IsSoftDelete | security_result.description is set to IsSoftDelete - {IsSoftDelete} |
| MessageId | `target.resource.product_object_id` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetUserId | `target.user.email_addresses` |
| TargetYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| VersionId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### FileSensitivityLabelChanged
The following table lists the log fields and corresponding UDM mappings for the operation `FileSensitivityLabelChanged` and workload `SharePoint` or `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_UNCATEGORIZED` `ObjectId` is mapped to `target.file.full_path` |
| AppAccessContext.CorrelationId | `security_result.detection_fields.key/value` |
| CorrelationId | `security_result.detection_fields.key/value` |
| DestinationFileExtension | `target.file.mime_type` |
| DestinationFileName | `target.file.full_path` is set to `{DestinationRelativeUrl}/{DestinationFileName}` |
| DestinationRelativeUrl | `target.file.full_path` is set to `{DestinationRelativeUrl}/{DestinationFileName}` |
| DestinationLabel | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| HighPriorityMediaProcessing | `additional.fields.key` and `additional.fields.value.string_value` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListServerTemplate | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.ActionSource | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelEventData.LabelEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelEventData.OldSensitivityLabelId | `target.resource.product_object_id` |
| SensitivityLabelEventData.OldSensitivityLabelOwnerEmail | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.SensitivityLabelId | `security_result.detection_fields.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | `src.file.full_path = %{SourceRelativeUrl}/%{SourceFileName}` |
| SourceRelativeUrl | `src.file.full_path = %{SourceRelativeUrl}/%{SourceFileName}` |
| SourceLabel | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### FileRead
The following table lists the log fields and corresponding UDM mappings for the operation `FileRead` and workload `Endpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_READ` `ObjectId` is mapped to `target.url` |
| Application | `principal.application` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| DlpAuditEventMetadata.DlpPolicyMatchId | `security_result.detection_fields.key/value` |
| DlpAuditEventMetadata.EvaluationTime | `security_result.detection_fields.key/value` |
| EnforcementMode | `additional.fields.key` and `additional.fields.value.string_value` |
| FileExtension | `target.file.mime_type` |
| FileSize | `target.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Hidden | `security_result.detection_fields.key/value` |
| JitTriggered | `security_result.detection_fields.key/value` |
| MDATPDeviceId | `security_result.detection_fields.key/value` |
| PolicyMatchInfo | `target.resource.product_object_id` `security_result.summary` `security_result.rule_id` `security_result.rule_name` `PolicyId` is mapped to `target.resource.product_object_id` `PolicyName` is mapped to `security_result.summary` `RuleId` is mapped to `security_result.rule_id` `RuleName` is mapped to `security_result.rule_name` |
| RMSEncrypted | `security_result.detection_fields.key/value` |
| SensitiveInfoTypeData | `security_result.detection_fields.key/value` `security_result.confidence_details` |
| SensitivityLabelEventData.SensitivityLabelId | `security_result.detection_fields.key/value` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### MessageReadReceiptReceived
The following table lists the log fields and corresponding UDM mappings for the operation `MessageReadReceiptReceived` and workload `MicrosoftTeams`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE` |
| ChatThreadId | `target.user.group_identifiers` `target.group.product_object_id` |
| CommunicationType | `additional.fields.key` and `additional.fields.value.string_value` |
| MessageId | `target.resource.product_object_id` |
| MessageVersion | `target.resource.attribute.labels.key/value` |
| MessageVisibilityTime | `target.resource.attribute.labels.key/value` |
| ParticipantInfo.HasForeignTenantUsers | `security_result.detection_fields.key/value` |
| ParticipantInfo.HasGuestUsers | `security_result.detection_fields.key/value` |
| ParticipantInfo.HasOtherGuestUsers | `security_result.detection_fields.key/value` |
| ParticipantInfo.HasUnauthenticatedUsers | `security_result.detection_fields.key/value` |
| ParticipantInfo.ParticipatingTenantIds | `security_result.detection_fields.key/value` |
### Search
The following table lists the log fields and corresponding UDM mappings for the operation `Search` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UNCATEGORIZED` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| DataType | `security_result.description` |
### TaskDeleted
The following table lists the log fields and corresponding UDM mappings for the operation `TaskDeleted` and workload `MicrosoftTodo`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_DELETION` `target.resource.resource_type` is set to `TASK` |
| ActorAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemId | `security_result.detection_fields.key/value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| TargetActorId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetActorTenantId | `additional.fields.key` and `additional.fields.value.string_value` |
### TaskUpdated
The following table lists the log fields and corresponding UDM mappings for the operation `TaskUpdated` and workload `MicrosoftTodo`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_WRITTEN` `target.resource.resource_type` is set to `TASK` |
| ActorAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemId | `security_result.detection_fields.key/value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| TargetActorId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetActorTenantId | `additional.fields.key` and `additional.fields.value.string_value` |
### TaskCreation
The following table lists the log fields and corresponding UDM mappings for the operation `TaskCreation` and workload `MicrosoftTodo`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_CREATION` `target.resource.resource_type` is set to `TASK` |
| ActorAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemId | `security_result.detection_fields.key/value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| TargetActorId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetActorTenantId | `additional.fields.key` and `additional.fields.value.string_value` |
### SecurityGroupModified
The following table lists the log fields and corresponding UDM mappings for the operation `SecurityGroupModified` and workload `Project`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `GROUP_MODIFICATION` |
| CorrelationId | `security_result.detection_fields.key/value` |
| Entity | `metadata.product_name` |
| EventSource | `target.application` |
| ItemType | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| AppAccessContext.UniqueTokenId | `additional.fields.key` and `additional.fields.value.string_value` |
| AppAccessContext.CorrelationId | `security_result.detection_fields.key/value` |
### LaunchPowerApp
The following table lists the log fields and corresponding UDM mappings for the operation `LaunchPowerApp` and workload `PowerApps`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `GENERIC_EVENT` |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### DeleteDatasetRows
The following table lists the log fields and corresponding UDM mappings for the operation `DeleteDatasetRows` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_DELETION`. If `ResultStatus` is TRUE then `Action` is set to `ALLOW` and `security_result.summary` is set to `DataSetRow deletion successful` else `Action` is set to `BLOCK` and `security_result.summary` is set to `DataSetRow deletion failed`. |
| UserAgent | `network.http.user_agent ` |
| WorkSpaceName | `target.resource.attribute.labels.key/value ` |
| DatasetName | `target.resource.attribute.labels.key/value ` |
| WorkspaceId | `target.resource.attribute.labels.key/value ` |
| DatasetId | `target.resource.product_object_id ` |
| DataConnectivityMode | `target.resource.attribute.labels.key/value ` |
| ArtifactId | `target.resource.attribute.labels.key/value ` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value ` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| TableName | `target.resource.attribute.labels.key/value ` |
| LastRefreshTime | `additional.fields.key` and `additional.fields.value.string_value ` |
| ArtifactKind | `target.resource.attribute.labels.key/value ` |
### New-DlpCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation `New-DlpCompliancePolicy` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_CREATION`. `target.resource.resource_type` is set to `ACCESS_POLICY`. |
| ClientApplication | `additional.fields.key` and `additional.fields.value.string_value ` |
| CmdletVersion | `metadata.product_version ` |
| EffectiveOrganization | `target.administrative_domain ` |
| ObjectId | `target.resource.product_object_id ` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value ` |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value ` |
| StartTime | `additional.fields[start_time] ` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value ` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value ` |
| Version | `metadata.product_version ` |
### New-DlpComplianceRule
The following table lists the log fields and corresponding UDM mappings for the operation `New-DlpComplianceRule` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_CREATION`. `target.resource.resource_type` is set to `ACCESS_POLICY`. |
| ClientApplication | `additional.fields.key` and `additional.fields.value.string_value ` |
| CmdletVersion | `metadata.product_version ` |
| EffectiveOrganization | `target.administrative_domain ` |
| ObjectId | `target.resource.product_object_id ` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value ` |
| StartTime | `additional.fields[start_time] ` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value ` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value ` |
| Version | `metadata.product_version ` |
### Get-InsiderRiskPolicy
The following table lists the log fields and corresponding UDM mappings for the operation `Get-InsiderRiskPolicy` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_CREATION`. |
| ClientApplication | `additional.fields.key` and `additional.fields.value.string_value ` |
| CmdletVersion | `metadata.product_version ` |
| EffectiveOrganization | `target.administrative_domain ` |
| ObjectId | `target.resource.product_object_id ` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value ` |
| StartTime | `additional.fields[start_time] ` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value ` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value ` |
| Version | `metadata.product_version ` |
### Set-HostedContentFilterPolicy
The following table lists the log fields and corresponding UDM mappings for the operation `Set-HostedContentFilterPolicy` and workload `Exchange`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_CREATION`. `target.resource.resource_type` is set to `SETTING`. If `ResultStatus` is TRUE then `Action` is set to `ALLOW` else `Action` is set to `BLOCK`. |
| ExternalAccess | `additional.fields.key` and `additional.fields.value.string_value ` |
| ObjectId | `target.resource.product_object_id ` |
| Version | `metadata.product_version ` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value ` |
### Enable Strong Authentication.
The following table lists the log fields and corresponding UDM mappings for the operation `Enable Strong Authentication.` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `SETTING_MODIFICATION`. |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `target.resource.attribute.labels[Action Client Name]`
Iterate for each element `field` in the `ModifiedProperties` log field array, then If the `field.Name` value is equal to `Action Client Name` then, the `target.resource.attribute.labels.key` UDM field is set to `Action Client Name` and the `field.NewValue` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
### ReactedToMessage
The following table lists the log fields and corresponding UDM mappings for the operation `ReactedToMessage` and workload `MicrosoftTeams`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_COMMUNICATION`. |
| AppAccessContext.IssuedAtTime | `additional.fields.key` and `additional.fields.value.string_value` |
| AppAccessContext.UniqueTokenId | `additional.fields.key` and `additional.fields.value.string_value` |
| ChatThreadId | `target.user.group_identifiers ` |
| ChatThreadId | `target.group.product_object_id ` |
| MessageReactionType | `target.resource.attribute.labels.key/value ` |
| ChatName | `target.group.group_display_name ` |
| MessageId | `target.resource.product_object_id ` |
| ParticipantInfo.HasForeignTenantUsers | `security_result.detection_fields.key/value ` |
| ParticipantInfo.HasGuestUsers | `security_result.detection_fields.key/value ` |
| ParticipantInfo.HasOtherGuestUsers | `security_result.detection_fields.key/value ` |
| ParticipantInfo.HasUnauthenticatedUsers | `security_result.detection_fields.key/value ` |
| ParticipantInfo.ParticipatingTenantIds | `security_result.detection_fields.key/value ` |
### RemovableMediaUnmount
The following table lists the log fields and corresponding UDM mappings for the operation `RemovableMediaUnmount` and workload `Endpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. |
| MDATPDeviceId | `principal.asset.asset_id` |
| Platform | `additional.fields.key` and `additional.fields.value.string_value` |
| Scope | `additional.fields.key` and `additional.fields.value.string_value` |
| RemovableMediaDeviceAttributes.Manufacturer | `target.asset.hardware.manufacturer ` |
| RemovableMediaDeviceAttributes.Model | `target.asset.hardware.model ` |
| RemovableMediaDeviceAttributes.SerialNumber | `target.asset.hardware.serial_number ` |
### FileUploadedToCloud
The following table lists the log fields and corresponding UDM mappings for the operation `FileUploadedToCloud` and workload `Endpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_UNCATEGORIZED`. |
| DlpAuditEventMetadata.DlpPolicyMatchId | `security_result.detection_fields.key/value ` |
| DlpAuditEventMetadata.EvaluationTime | `security_result.detection_fields.key/value ` |
| EnforcementMode | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.FullUrl | `target.file.full_path ` |
| EvidenceFile.StorageName | `target.file.names ` |
| Hidden | `security_result.detection_fields.key/value ` |
| JitTriggered | `security_result.detection_fields.key/value ` |
| MDATPDeviceId | `principal.asset.asset_id` |
| ObjectId | `target.file.full_path` |
| SensitiveInfoTypeData.Count | `security_result.detection_fields.key/value ` |
| SensitiveInfoTypeData.Confidence | `security_result.detection_fields.key/value ` |
| SensitiveInfoTypeData.SensitiveInfoTypeName | `security_result.detection_fields.key/value ` |
| TargetPrinterName | `target.asset.hostname ` |
| | `target.asset.type` is set to `PRINTER` |
| TargetDomain | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### GenerateDataflowSasToken
The following table lists the log fields and corresponding UDM mappings for the operation `GenerateDataflowSasToken` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_ACCESS`. |
| DataflowAccessTokenRequestParameters.entityName | `additional.fields.key` and `additional.fields.value.string_value` |
| DataflowAccessTokenRequestParameters.partitionUri | `additional.fields.key` and `additional.fields.value.string_value` |
| DataflowAccessTokenRequestParameters.permissions | `additional.fields.key` and `additional.fields.value.string_value` |
| DataflowAccessTokenRequestParameters.tokenLifetimeInMinutes | `additional.fields.key` and `additional.fields.value.string_value` |
| DataflowId | `target.resource.product_object_id ` |
| DataflowName | `target.resource.name ` |
| IsSuccess | If `IsSuccess` is TRUE then `Action` is set to `ALLOW` else `Action` is set to `BLOCK`. |
| ItemName | `additional.fields.key` and `additional.fields.value.string_value` |
### GenerateScreenshot
The following table lists the log fields and corresponding UDM mappings for the operation `GenerateScreenshot` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_CREATION`. |
### MDCAssessments
The following table lists the log fields and corresponding UDM mappings for the operation `MDCAssessments` and workload `CompliancePostureManagement`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `SCAN_UNCATEGORIZED`. |
| PropertyBag.AssessmentStatusPerInitiative.ArnEventId | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.CloudProvider | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.CustomerResourceId | `about.resource.product_object_id ` |
| PropertyBag.AssessmentStatusPerInitiative.EventType | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.PolicyInitiativeId | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.PolicyInitiativeName | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.ResourceName | `about.resource.name ` |
| PropertyBag.AssessmentStatusPerInitiative.ResourceType | `about.resource.resource_subtype ` |
| PropertyBag.AssessmentStatusPerInitiative.SecurityAssessmentId | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.StatusChangeDate | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.StatusCode | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.StatusFirstEvaluationDate | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.SubscriptionId | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.AssessmentStatusPerInitiative.SubscriptionName | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.DataType | `additional.fields.key` and `additional.fields.value.string_value` |
### RemovableMediaMount
The following table lists the log fields and corresponding UDM mappings for the operation `RemovableMediaMount` and workload `Endpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
| MDATPDeviceId | `target.asset.asset_id ` |
| Platform | `additional.fields.key` and `additional.fields.value.string_value` |
| Scope | `additional.fields.key` and `additional.fields.value.string_value` |
| RemovableMediaDeviceAttributes.Manufacturer | `target.asset.hardware.manufacturer ` |
| RemovableMediaDeviceAttributes.Model | `target.asset.hardware.model ` |
| RemovableMediaDeviceAttributes.SerialNumber | `target.asset.hardware.serial_number ` |
### SignInEvent
The following table lists the log fields and corresponding UDM mappings for the operation `SignInEvent` and workload `SharePoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_LOGIN`. |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
### ApprovedRequest
The following table lists the log fields and corresponding UDM mappings for the operation `ApprovedRequest` and workload `MicrosoftTeams`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_PERMISSIONS`. |
| ItemName | `additional.fields.key` and `additional.fields.value.string_value` |
### CreateForm
The following table lists the log fields and corresponding UDM mappings for the operation `CreateForm` and workload `MicrosoftForms`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_CREATION`. |
| FormsUserType | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application ` |
### ListForms
The following table lists the log fields and corresponding UDM mappings for the operation `ListForms` and workload `MicrosoftForms`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
### MDCRegulatoryComplianceAssessments
The following table lists the log fields and corresponding UDM mappings for the operation `MDCRegulatoryComplianceAssessments` and workload `CompliancePostureManagement`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `SCAN_UNCATEGORIZED`. |
| PropertyBag.DataType | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.Policy.ArnEventId | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.Policy.Description | `metadata.description ` |
| PropertyBag.Policy.Description | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.Policy.DetailsLink | `security_result.url_back_to_products ` |
| PropertyBag.Policy.DetailsLink | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.Policy.EventTime | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.Policy.EventType | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.Policy.PolicyInitiativeId | `security_result.rule_labels[policy_initiative_id] ` |
| PropertyBag.Policy.PolicyInitiativeId | `additional.fields.key` and `additional.fields.value.string_value` |
| PropertyBag.Policy.PolicyInitiativeName | `security_result.rule_labels` The `PropertyBag.Policy.PolicyInitiativeName` log field is mapped to the UDM field `security_result.rule_labels.value` and the UDM field `security_result.rule_labels.key` is set to `policy_initiative_name`. |
| PropertyBag.Policy.PolicyInitiativeName | `additional.fields.key` and `additional.fields.value.string_value` |
### PreviewForm
The following table lists the log fields and corresponding UDM mappings for the operation `PreviewForm` and workload `MicrosoftForms`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_ACCESS`. |
### ViewedApprovalRequest
The following table lists the log fields and corresponding UDM mappings for the operation `ViewedApprovalRequest` and workload `MicrosoftTeams`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_ACCESS`. |
| ItemName | `additional.fields.key` and `additional.fields.value.string_value` |
### ListCreated
The following table lists the log fields and corresponding UDM mappings for the operation `ListCreated` and workload `SharePoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_CREATION`. |
| AppAccessContext.UniqueTokenId | `additional.fields.key` and `additional.fields.value.string_value` |
| ListColor | `additional.fields.key` and `additional.fields.value.string_value` |
| ListIcon | `additional.fields.key` and `additional.fields.value.string_value` |
### SiteColumnCreated
The following table lists the log fields and corresponding UDM mappings for the operation `SiteColumnCreated` and workload `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. |
| ObjectId | `target.resource.product_object_id ` |
### ListViewUpdated
The following table lists the log fields and corresponding UDM mappings for the operation `ListViewUpdated` and workload `SharePoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. |
| AppAccessContext.UniqueTokenId | `additional.fields.key` and `additional.fields.value.string_value` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| CustomizedDoclib | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `principal.ip` The `DeviceDisplayName` log field is mapped to the `principal.ip` UDM field. |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| FromApp | `additional.fields.key` and `additional.fields.value.string_value` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemCount | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListColor | `additional.fields.key` and `additional.fields.value.string_value` |
| ListIcon | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `target.resource.attribute.labels[ListId]` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `target.url` |
| Platform | `additional.fields.key` and `additional.fields.value.string_value` |
| RecordType | `security_result.detection_fields.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| Source | `security_result.description` |
| TemplateTypeId | `additional.fields.key` and `additional.fields.value.string_value` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### TeamsUserSignedOut
The following table lists the log fields and corresponding UDM mappings for the operation `TeamsUserSignedOut` and workload `MicrosoftTeams`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_LOGOUT`. |
| | `extension.auth.auth_type` is mapped to `SSO`. |
| ChannelGuid | `additional.fields.key` and `additional.fields.value.string_value` |
| ChannelName | `additional.fields.key` and `additional.fields.value.string_value` |
| ChatName | `target.group.group_display_name` |
| ChatThreadId | `target.user.group_identifiers` |
| DeviceInformation | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemName | `additional.fields.key` and `additional.fields.value.string_value` |
| MessageId | `additional.fields.key` and `additional.fields.value.string_value` |
| MessageVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| TeamGuid | `target.group.product_object_id` |
| TeamName | `target.group.group_display_name` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| UserType | `target.user.attribute.roles` |
| Version | `metadata.product_version` |
### GetWorkspaces
The following table lists the log fields and corresponding UDM mappings for the operation `GetWorkspaces` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
| Activity | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| AggregatedWorkspaceInformation.WorkspaceCount | `additional.fields.key` and `additional.fields.value.string_value` |
| AggregatedWorkspaceInformation.WorkspacesByCapacitySku | `additional.fields.key` and `additional.fields.value.string_value` |
| AggregatedWorkspaceInformation.WorkspacesByType | `additional.fields.key` and `additional.fields.value.string_value` |
| IsSuccess | `security_result.action` |
| UserAgent | `network.http.user_agent` |
### ConnectFromExternalApplication
The following table lists the log fields and corresponding UDM mappings for the operation `ConnectFromExternalApplication` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| Activity | `additional.fields.key` and `additional.fields.value.string_value` |
| CustomData | `additional.fields.key` and `additional.fields.value.string_value` |
### TaskListRead
The following table lists the log fields and corresponding UDM mappings for the operation `TaskListRead` and workload `Planner`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| TaskList | `additional.fields.key` and `additional.fields.value.string_value` |
### PutConnection
The following table lists the log fields and corresponding UDM mappings for the operation `PutConnection` and workload `PowerApps`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| AdditionalInfo.actionName | `security_result.action_details` The `AdditionalInfo.actionName` log field is mapped to the `security_result.action_details` UDM field. |
| ResourceId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserKey | `target.label.key/value` |
| AdditionalInfo.environmentName | `additional.fields.key` and `additional.fields.value.string_value` |
### AdminSubmissionTablAllow
The following table lists the log fields and corresponding UDM mappings for the operation `AdminSubmissionTablAllow` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `GENERIC_EVENT`. |
| SubmissionContent | `security_result.detection_fields.key/value` |
| SubmissionContentType | `security_result.detection_fields.key/value` |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| Recipients | `network.email.to` |
| SubmissionState | `security_result.summary` |
| SubmissionId | `security_result.detection_fields.key/value` |
| ExtendedProperties | If the `Name` log field value is equal to `AdminReviewTime` or `AdminReviewResult`, then the `Value` is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| SubmissionConfidenceLevel | `security_result.confidence_details` The `SubmissionConfidenceLevel` log field is mapped to the `security_result.confidence_details` UDM field. |
| SubmissionType | `security_result.detection_fields.key/value` |
| MessageDate | `additional.fields.key` and `additional.fields.value.string_value` |
| P1SenderDomain | `network.dns_domain` |
| UserKey | `target.label.key/value` |
| P2SenderDomain | `about.administrative_domain` |
| Subject | `network.email.subject` |
| Version | `metadata.product_version` |
### Add contact.
The following table lists the log fields and corresponding UDM mappings for the operation `Add contact.` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_CREATION`. `target.resource.resource_subtype` is set to `Contact`. |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserKey | `target.label.key/value` |
| Target | `security_result.detection_fields.key/value` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| Version | `metadata.product_version` |
| ExtendedProperties | `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the , `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `target.resource.name` `target.resource.attribute.labels.key/value` `security_result.detection_fields.key/value` `security_result.summary` If `Name` is `Included Updated Properties` then `NewValue` is mapped to `security_result.summary` and `OldValue` is mapped to `security_result.detection_field.key/value`. Else if `Name` is `DisplayName` then `NewValue` is mapped to `target.resource.name` and `OldValue` is mapped to `target.resource.attribute.key/value`. Else `target.resource.attribute.labels.key/value`. |
### WorkspacePortalUrlReceived
The following table lists the log fields and corresponding UDM mappings for the operation `WorkspacePortalUrlReceived` and workload `MicrosoftDefenderForIdentity`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| ResultDescription | `security_result.detection_fields.key.value` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
### PutConnectionPermission
The following table lists the log fields and corresponding UDM mappings for the operation `PutConnectionPermission` and workload `PowerApps`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_PERMISSIONS_CHANGE`. `target.resource.resource_type` is set to `SETTING`. |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| AdditionalInfo.actionName | `security_result.action_details` The `AdditionalInfo.actionName` log field is mapped to the `security_result.action_details` UDM field. |
| ResourceId | `target.resource.attribute.labels.key/value` |
| UserKey | `target.label.key/value` |
| AdditionalInfo.environmentName | `target.resource.attribute.labels.key/value` |
| AdditionalInfo.targetObjectId | `target.resource.product_object_id` |
### SensitivityLabeledFileOpened
The following table lists the log fields and corresponding UDM mappings for the operation `SensitivityLabeledFileOpened` and workload `PublicEndpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_OPEN`. |
| PreviousProtectionType.protectionType | `security_result.detection_fields.key/value` |
| CurrentProtectionType.protectionType | `security_result.detection_fields.key/value` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| CurrentProtectionType.documentEncrypted | `security_result.detection_fields.key/value` |
| CurrentProtectionType.owner | `security_result.about.email_addresses` |
| TargetLocation | `additional.fields.key` and `additional.fields.value.string_value` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| LabelId | `additional.fields.key` and `additional.fields.value.string_value` |
| CurrentProtectionType.templateId | `security_result.detection_fields.key/value` |
| ProtectionEventType | `security_result.detection_fields.key/value` |
| ContentType | `additional.fields.key` and `additional.fields.value.string_value` |
| Platform | `target.platform` |
| UserSku | `additional.fields.key` and `additional.fields.value.string_value` |
| PreviousProtectionType.documentEncrypted | `security_result.detection_fields.key/value` |
| ObjectId | `target.url` |
| PreviousProtectionType.owner | `security_result.about.email_addresses` |
| Application | `principal.application` |
| PreviousProtectionType.templateId | `security_result.detection_fields.key/value` |
### Validate
The following table lists the log fields and corresponding UDM mappings for the operation `Validate` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `security_result.description` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| RelativeUrl | `target.url` |
### SensitivityLabeledFileRenamed
The following table lists the log fields and corresponding UDM mappings for the operation `SensitivityLabeledFileRenamed` and workload `PublicEndpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_MOVE`. |
| PreviousProtectionType.protectionType | `security_result.detection_fields.key/value` |
| CurrentProtectionType.protectionType | `security_result.detection_fields.key/value` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| CurrentProtectionType.documentEncrypted | `security_result.detection_fields.key/value` |
| CurrentProtectionType.owner | `security_result.about.email_addresses` |
| TargetLocation | `additional.fields.key` and `additional.fields.value.string_value` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| LabelId | `additional.fields.key` and `additional.fields.value.string_value` |
| CurrentProtectionType.templateId | `security_result.detection_fields.key/value` |
| ProtectionEventType | `security_result.detection_fields.key/value` |
| ContentType | `additional.fields.key` and `additional.fields.value.string_value` |
| Platform | `target.platform` |
| UserSku | `additional.fields.key` and `additional.fields.value.string_value` |
| PreviousProtectionType.documentEncrypted | `security_result.detection_fields.key/value` |
| ObjectId | `target.url` |
| PreviousProtectionType.owner | `security_result.about.email_addresses` |
| Application | `principal.application` |
| PreviousProtectionType.templateId | `security_result.detection_fields.key/value` |
| PreviousTarget | `src.url` |
### TaskModified
The following table lists the log fields and corresponding UDM mappings for the operation `TaskModified` and workload `Planner`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_WRITTEN`. `target.resource.resource_type` is set to `TASK`. |
| PlanId | `target.resource.attribute.labels.key/value` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `target.resource.product_object_id` |
### DeleteTile
The following table lists the log fields and corresponding UDM mappings for the operation `TaskModified` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_DELETION`. |
| WorkspaceId | `target.resource.product_object_id` |
| WorkSpaceName | `target.resource.name` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| RefreshEnforcementPolicy | `security_result.detection_fields.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| IsSuccess | `security_result.action` |
| UserAgent | `network.http.user_agent` |
| ObjectId | `target.resource.attribute.labels.key/value` |
### QuarantineReleaseMessage
The following table lists the log fields and corresponding UDM mappings for the operation `QuarantineReleaseMessage` and workload `Quarantine`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| NetworkMessageId | `security_result.detection_fields.key/value` |
| ReleaseTo | `security_result.detection_fields.key/value` |
| RequestType | `security_result.detection_fields.key/value` |
| RequestSource | `security_result.detection_fields.key/value` |
### WorkspaceStatusReceived
The following table lists the log fields and corresponding UDM mappings for the operation `WorkspaceStatusReceived` and workload `MicrosoftDefenderForIdentity`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| ResultDescription | `security_result.detection_fields.key/value` |
### LinkedEntityUpdated
The following table lists the log fields and corresponding UDM mappings for the operation `LinkedEntityUpdated` and workload `MicrosoftTodo`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_WRITTEN`. `target.resource.resource_type` is set to `TASK`. |
| ActorAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemId | `security_result.detection_fields.key/value` and `target.resource.product_object_id` |
| ItemType | `target.resource.attribute.labels.key/value` |
| TargetActorId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetActorTenantId | `additional.fields.key` and `additional.fields.value.string_value` |
### ViewResponse
The following table lists the log fields and corresponding UDM mappings for the operation `ViewResponse` and workload `MicrosoftForms`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
| FormsUserTypes | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application` |
| FormName | `target.resource.name` |
| FormId | `target.resource.product_object_id` |
### PlanListRead
The following table lists the log fields and corresponding UDM mappings for the operation `PlanListRead` and workload `Planner`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. `target.resource.resource_subtype` is set to `Plan`. |
| PlanList | `target.resource.product_object_id` |
| ObjectId | `target.resource.attribute.labels.key/value` |
### O365SyncAdminUserPromotion
The following table lists the log fields and corresponding UDM mappings for the operation `O365SyncAdminUserPromotion` and workload `Yammer`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| ActorUserId | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| ActorYammerUserId | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
| YammerNetworkId | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### FileCopiedToClipboard
The following table lists the log fields and corresponding UDM mappings for the operation `FileCopiedToClipboard` and workload `Endpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_UNCATEGORIZED`. |
| Application | `principal.application` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| DlpAuditEventMetadata.DlpPolicyMatchId | `security_result.detection_fields.key/value` |
| DlpAuditEventMetadata.EvaluationTime | `security_result.detection_fields.key/value` |
| EnforcementMode | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.FullUrl | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.StorageName | `additional.fields.key` and `additional.fields.value.string_value` |
| FileExtension | `target.file.mime_type` |
| FileType | `target.resource.attribute.labels.key/value` |
| FileSizeBytes | `target.file.size` |
| Hidden | `security_result.detection_fields.key/value` |
| JitTriggered | `security_result.detection_fields.key/value` |
| MDATPDeviceId | `security_result.detection_fields.key/value` |
| ObjectId | `target.file.full_path` |
| Platform | `additional.fields.key` and `additional.fields.value.string_value` |
| PolicyMatchInfo | `target.resource.product_object_id` `security_result.summary` `security_result.rule_id` `security_result.rule_name` `PolicyId` is mapped to `target.resource.product_object_id` `PolicyName` is mapped to `security_result.summary` `RuleId` is mapped to `security_result.rule_id` `RuleName` is mapped to `security_result.rule_name` |
| SensitiveInfoTypeData | `security_result.detection_fields.key/value` `security_result.confidence_details` |
| Scope | `additional.fields.key` and `additional.fields.value.string_value` |
| RMSEncrypted | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.SensitivityLabelId | `security_result.detection_fields.key/value` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetDomain | `target.domain.name` |
| TargetFilePath | `additional.fields.key` and `additional.fields.value.string_value` |
| OriginatingDomain | `principal.domain.name` |
### FileTranscriptContentAccessed
The following table lists the log fields and corresponding UDM mappings for the operation `FileTranscriptContentAccessed` and workload `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_READ`. |
| AlternateStreamId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `target.application` and `target.resource.name` |
| ApplicationId | `additional.fields[ApplicationId]` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| AppAccessContext.UniqueTokenId | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| HighPriorityMediaProcessing | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListServerTemplate | `security_result.detection_fields.key/value` |
| ObjectId | `target.url` |
| Platform | `additional.fields.key` and `additional.fields.value.string_value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` is mapped to `SourceRelativeUrl`/`SourceFileName`. |
| SourceRelativeUrl | `target.file.full_path` is mapped to `SourceRelativeUrl`/`SourceFileName`. |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### Set-DlpCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation `Set-DlpCompliancePolicy` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. `target.resource.resource_type` is set to `ACCESS_POLICY`. |
| ClientApplication | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| ObjectId | `target.resource.product_object_id` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| StartTime | `additional.fields[start_time]` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Remove-DlpCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation `Remove-DlpCompliancePolicy` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_DELETION`. `target.resource.resource_type` is set to `ACCESS_POLICY`. |
| ClientApplication | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| ObjectId | `target.resource.product_object_id` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| StartTime | `additional.fields[start_time]` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Remove-DlpCompliancePolicy
The following table lists the log fields and corresponding UDM mappings for the operation `Remove-DlpCompliancePolicy` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_DELETION`. `target.resource.resource_type` is set to `ACCESS_POLICY`. |
| ClientApplication | `additional.fields.key` and `additional.fields.value.string_value` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| ObjectId | `target.resource.product_object_id` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| StartTime | `additional.fields[start_time]` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
### Add-MailboxLocation
The following table lists the log fields and corresponding UDM mappings for the operation `Add-MailboxLocation` and workload `Exchange`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. |
| AppAccessContext.UniqueTokenId | `additional.fields.key` and `additional.fields.value.string_value` |
| AppId | `target.resource.attribute.labels.key/value` |
| ClientAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `target.resource.product_object_id` |
| OrganizationName | `target.administrative_domain` |
| OriginatingServer | `principal.hostname` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SessionId | `network.session_id` |
| Version | `metadata.product_version` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
### Release-QuarantineMessage
The following table lists the log fields and corresponding UDM mappings for the operation `Release-QuarantineMessage` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| ObjectId | `target.resource.product_object_id` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key` and `additional.fields.value.string_value` |
### SensitivityLabelApplied
The following table lists the log fields and corresponding UDM mappings for the operation `SensitivityLabelApplied` and workload `PublicEndpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. `target.resource.resource_type` is set to `SETTING`. |
| Application | `principal.application` |
| ContentType | `additional.fields.key` and `additional.fields.value.string_value` |
| CurrentProtectionType.protectionType | `target.resource.attribute.labels.key/value` |
| CurrentProtectionType.documentEncrypted | `target.resource.attribute.labels.key/value` |
| CurrentProtectionType.owner | `target.resource.attribute.labels.key/value` |
| CurrentProtectionType.templateId | `target.resource.attribute.labels.key/value` |
| DeviceName | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| EmailInfo.cc | `network.email.cc` |
| EmailInfo.bcc | `network.email.bcc` |
| EmailInfo.from | `network.email.from` |
| EmailInfo.subject | `network.email.subject` |
| EmailInfo.to | `network.email.to` |
| Platform | `target.platform` |
| PreviousProtectionType.protectionType | `target.resource.attribute.labels.key/value` |
| PreviousProtectionType.documentEncrypted | `target.resource.attribute.labels.key/value` |
| PreviousProtectionType.owner | `target.resource.attribute.labels.key/value` |
| PreviousProtectionType.templateId | `target.resource.attribute.labels.key/value` |
| ProtectionEventType | `security_result.detection_fields.key/value` |
| TargetLocation | `additional.fields.key` and `additional.fields.value.string_value` |
| UserSku | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelEventData.ActionSource | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.ActionSourceDetail | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.LabelEventType | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.SensitivityLabelId | `target.resource.product_object_id` |
| Common.Location | `target.location.name` |
### SharingLinkCreated
The following table lists the log fields and corresponding UDM mappings for the operation `SharingLinkCreated` and workload `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_PERMISSIONS_CHANGE`. `target.resource.resource_subtype` is set to `Link`. |
| ApplicationDisplayName | `target.application` and `target.resource.name` |
| ApplicationId | `additional.fields[ApplicationId]` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ObjectId | `target.url` |
| Permission | `target.resource.attribute.permissions.name` |
| Platform | `target.platform` |
| SharingLinkScope | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### TimesheetSaved
The following table lists the log fields and corresponding UDM mappings for the operation `TimesheetSaved` and workload `Project`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_WRITTEN`. `target.resource.resource_subtype` is set to `Timesheet`. |
| Action | `security_result.action_details` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| Entity | `metadata.product_name` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Platform | `target.platform` |
| UserAgent | `network.http.user_agent` |
### ResourceCheckedOut
The following table lists the log fields and corresponding UDM mappings for the operation `ResourceCheckedOut` and workload `Project`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
| Action | `security_result.action_details` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| Entity | `metadata.product_name` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Platform | `target.platform` |
| UserAgent | `network.http.user_agent` |
### TimesheetAccessed
The following table lists the log fields and corresponding UDM mappings for the operation `TimesheetAccessed` and workload `Project`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. `target.resource.resource_subtype` is set to `Timesheet`. |
| Action | `security_resultaction_details` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| Entity | `metadata.product_name` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Platform | `target.platform` |
| UserAgent | `network.http.user_agent` |
### ListItemRecycled
The following table lists the log fields and corresponding UDM mappings for the operation `ListItemRecycled` and workload `SharePoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| ApplicationDisplayName | `principal.application` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListBaseTemplateType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListTitle | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `target.url` |
| Platform | `target.platform` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### SensitivityLabelUpdated
The following table lists the log fields and corresponding UDM mappings for the operation `SensitivityLabelUpdated` and workload `PowerPoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| Application | `principal.application` |
| ContentType | `additional.fields.key` and `additional.fields.value.string_value` |
| CurrentProtectionType.documentEncrypted | `security_result.detection_fields.key/value` |
| CurrentProtectionType.owner | `security_result.about.user.email_addresses` |
| CurrentProtectionType.protectionType | `security_result.detection_fields.key/value` |
| CurrentProtectionType.templateId | `security_result.detection_fields.key/value` |
| DeviceName | `principal.hostname & principal.asset.hostname` |
| ObjectId | `target.url` |
| Platform | `target.platform` |
| PreviousProtectionType.documentEncrypted | `security_result.detection_fields.key/value` |
| PreviousProtectionType.owner | `security_result.about.user.email_addresses` |
| PreviousProtectionType.protectionType | `security_result.detection_fields.key/value` |
| PreviousProtectionType.templateId | `security_result.detection_fields.key/value` |
| ProtectionEventType | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.ActionSource | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelEventData.LabelEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelEventData.OldSensitivityLabelId | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.SensitivityLabelId | `target.resource.product_object_id` |
| TargetLocation | `additional.fields.key` and `additional.fields.value.string_value` |
| UserSku | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelEventData.JustificationText | `security_result.detection_fields.key/value` |
| Common.Location | `target.location.name` |
### GetGroupUsers
The following table lists the log fields and corresponding UDM mappings for the operation `GetGroupUsers` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
| Activity | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| CapacityId | `additional.fields.key` and `additional.fields.value.string_value` |
| IsSuccess | `security_result.action` |
| ObjectId | `target.resource.name` |
| RefreshEnforcementPolicy | `security_result.detection_fields.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WorkspaceId | `target.resource.product_object_id` |
### SubTaskCreated
The following table lists the log fields and corresponding UDM mappings for the operation `SubTaskCreated` and workload `MicrosoftTodo`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_CREATION`. `target.resource.resource_type` is set to `TASK`. |
| ActorAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemId | `target.resource.product_object_id` |
| ItemType | `target.resource.attribute.labels.key/value` |
| TargetActorId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetActorTenantId | `additional.fields.key` and `additional.fields.value.string_value` |
### TaskRead
The following table lists the log fields and corresponding UDM mappings for the operation `TaskRead` and workload `MicrosoftTodo`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. `target.resource.resource_type` is set to `TASK`. |
| ActorAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemId | `target.resource.product_object_id` |
| ItemType | `target.resource.attribute.labels.key/value` |
| TargetActorId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetActorTenantId | `additional.fields.key` and `additional.fields.value.string_value` |
### SubTaskUpdated
The following table lists the log fields and corresponding UDM mappings for the operation `SubTaskUpdated` and workload `MicrosoftTodo`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_WRITTEN`. `target.resource.resource_type` is set to `TASK`. |
| ActorAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemId | `target.resource.product_object_id` |
| ItemType | `target.resource.attribute.labels.key/value` |
| TargetActorId | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetActorTenantId | `additional.fields.key` and `additional.fields.value.string_value` |
### SharingLinkUpdated
The following table lists the log fields and corresponding UDM mappings for the operation `SharingLinkUpdated` and workload `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_PERMISSIONS_CHANGE`. `target.resource.resource_subtype` is set to `Link`. |
| ApplicationDisplayName | `target.application` and `target.resource.name` |
| ApplicationId | `additional.fields[ApplicationId]` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ObjectId | `target.url` |
| Permission | `target.resource.attribute.permissions.name` |
| Platform | `target.platform` |
| SharingLinkScope | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### Authorize
The following table lists the log fields and corresponding UDM mappings for the operation `Authorize` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| AadAppId | `additional.fields.key` and `additional.fields.value.string_value` |
| DataType | `security_result.description` |
| RelativeUrl | `target.url` |
| ResultCount | `additional.fields.key` and `additional.fields.value.string_value` |
### AddedToSharingLink
The following table lists the log fields and corresponding UDM mappings for the operation `AddedToSharingLink` and workload `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_PERMISSIONS_CHANGE`.
|
| ApplicationDisplayName | `target.application` and `target.resource.name` |
| ApplicationId | `additional.fields[ApplicationId]` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ObjectId | `target.url` |
| Permission | `target.resource.attribute.permissions.name` |
| Platform | `target.platform` |
| SharingLinkScope | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
| `TargetUserOrGroupName` | If the `TargetUserOrGroupType` log field value contain one of the following values, then the `TargetUserOrGroupName` field is mapped to the `target.group.group_display_name` UDM field: - `SecurityGroup` - `SharePointGroup`
Else, if the `TargetUserOrGroupType` log field value contain one of the following values, then the `TargetUserOrGroupName` field is mapped to the `target.user.email_addresses` UDM field: - `Member` - `Guest` |
### SharingLinkUsed
The following table lists the log fields and corresponding UDM mappings for the operation `SharingLinkUsed` and workload `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. `target.resource.resource_subtype` is set to `Link`. |
| ApplicationDisplayName | `target.application` and `target.resource.name` |
| ApplicationId | `additional.fields[ApplicationId]` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ObjectId | `target.url` |
| Permission | `target.resource.attribute.permissions.name` |
| Platform | `target.platform` |
| SharingLinkScope | `target.resource.attribute.labels.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| UniqueSharingId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelId | `security_result.detection_fields.key/value` |
### Update policy.
The following table lists the log fields and corresponding UDM mappings for the operation `Update policy.` and workload `AzureActiveDirectory`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, the `Value` log field is mapped to the `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.summary` `target.resource.name` If the `Name` log field value is equal to `DisplayName`, then `NewValue` log field is mapped to the `target.resource.name` UDM field. If the `Name` log field value is equal to `Updated Properties`, then `NewValue` log field is mapped to the `security_result.summary` UDM field. |
| `Actor` | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `security_result.detection_fields.key/value` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `target.resource.product_object_id` |
### FileSensitivityLabelApplied
The following table lists the log fields and corresponding UDM mappings for the operation `FileSensitivityLabelApplied` and workload `SharePoint` or `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_UNCATEGORIZED`. |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DestinationFileExtension | `target.file.mime_type` |
| DestinationFileName | `target.file.full_path` |
| DestinationRelativeUrl | `target.file.full_path` |
| DestinationLabel | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| HighPriorityMediaProcessing | `additional.fields.key` and `additional.fields.value.string_value` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListServerTemplate | `security_result.detection_fields.key/value` |
| ObjectId | `target.url` |
| Platform | `target.platform` |
| SensitivityLabelEventData.LabelEventType | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitivityLabelEventData.SensitivityLabelId | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.SensitivityLabelOwnerEmail | `security_result.about.user.email_addresses` |
| SensitivityLabelJustificationText | `security_result.detection_fields.key/value` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `src.file.mime_type` |
| SourceFileName | `src.file.full_path` |
| SourceRelativeUrl | `src.file.full_path` |
| SourceLabel | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| Version | `metadata.product_version` |
| WebId | `additional.fields.key` and `additional.fields.value.string_value` |
### QuarantineDenyReleaseMessage
The following table lists the log fields and corresponding UDM mappings for the operation `QuarantineDenyReleaseMessage` and workload `Quarantine`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| Identity | `additional.fields.key` and `additional.fields.value.string_value` |
| NetworkMessageId | `security_result.detection_fields.key/value` |
| QuarantinePolicy | `security_result.rule_name` The `QuarantinePolicy` log field is mapped to the `security_result.rule_name` UDM field. |
| QuarantineType | `security_result.detection_fields.key/value` |
| RecipientTags | `security_result.detection_fields.key/value` |
| RequestSource | `security_result.detection_fields.key/value` |
| RequestType | `security_result.detection_fields.key/value` |
### QuarantineApproveReleaseMessage
The following table lists the log fields and corresponding UDM mappings for the operation `QuarantineApproveReleaseMessage` and workload `Quarantine`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| Identity | `additional.fields.key` and `additional.fields.value.string_value` |
| NetworkMessageId | `security_result.detection_fields.key/value` |
| QuarantinePolicy | `security_result.rule_name` The `QuarantinePolicy` log field is mapped to the `security_result.rule_name` UDM field. |
| QuarantineType | `security_result.detection_fields.key/value` |
| RecipientTags | `security_result.detection_fields.key/value` |
| RequestSource | `security_result.detection_fields.key/value` |
| RequestType | `security_result.detection_fields.key/value` |
### CopilotInteraction
The following table lists the log fields and corresponding UDM mappings for the operation `CopilotInteraction` and workload `Copilot`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. `target.resource.resource_sub_type` is set to `Copilot Chat`. |
| CopilotEventData.AppHost | `additional.fields[CopilotEventDataAppHost]` |
| CopilotEventData.ThreadId | `target.resource.product_object_id` |
| CopilotEventData.AccessedResources | `target.resource.attribute.labels.key/value` |
| CopilotEventData.Contexts | `target.resource.attribute.labels.key/value` |
| CopilotEventData.MessageIds | `target.resource.attribute.labels.key/value` |
| ApplicationName | `target.application` |
| ConversationId | `network.session_id` |
| CopilotEventData.ConversationId | `security_result.detection_fields[ConversationId]` |
| CopilotEventData.CorrelationId | `additional.fields[CorrelationId]` |
| CopilotEventData.SensitivityLabelId | `target.resource.attribute.labels[SensitivityLabelId]` |
| CopilotEventData.AccessedResources.listItemUniqueId | `about.resource.product_object_id` |
| CopilotEventData.AccessedResources.PolicyDetails.PolicyType | `security_result.rule_type` |
| CopilotEventData.AccessedResources.PolicyDetails.PolicyOutcomes | `security_result.action_details` |
| CopilotEventData.Messages.Id | `about.resource.product_object_id` |
| CopilotEventData.Messages.isPrompt | `security_result.detection_fields[isPrompt]` |
| CopilotEventData.Messages.JailbreakDetected | `security_result.detection_fields[JailbreakDetected]` |
| CopilotEventData.AISystemPlugin.Id | `about.resource.product_object_id` |
| CopilotEventData.AISystemPlugin.Name | `about.resource.name` |
| CopilotEventData.ParticipatingAgents.AgentId | `about.resource.product_object_id` |
| CopilotEventData.ParticipatingAgents.AgentName | `about.resource.name` |
| Workload | `additional.fields[Workload]` |
### Remove delegated permission grant.
The following table lists the log fields and corresponding UDM mappings for the operation `Remove delegated permission grant.` and workload `Copilot`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_PERMISSIONS_CHANGE`. |
| Actor | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| ActorContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| AzureActiveDirectoryEventType | `target.resource.attribute.labels.key/value` |
| InterSystemsId | `target.resource.attribute.labels.key/value` |
| IntraSystemId | `target.resource.attribute.labels.key/value` |
| ObjectId | `target.resource.product_object_id` |
| SupportTicketId | `additional.fields.key` and `additional.fields.value.string_value` |
| Target | `security_result.detection_fields.key/value` |
| TargetContextId | `additional.fields.key` and `additional.fields.value.string_value` |
| ExtendedProperties | `network.http.user_agent` `target.resource.attribute.labels.key/value` `additional.fields.key` and `additional.fields.value.string_value` If the `Name` log field value is equal to `additionalDetails`, then `User-Agent` is extracted from the `Value` log field using the Grok pattern and mapped to the `network.http.user_agent` UDM field. Else, if the `Name` log field value is equal to `extendedAuditEventCategory`, then the `Value` log field is mapped to the `target.resource.attribute.labels.key/value` UDM field. Else, the `Value` log field is mapped to the `additional.fields.key` and `additional.fields.value.string_value` UDM fields. |
| ModifiedProperties | `security_result.detection_fields.key/value` |
### FileCopiedToRemovableMedia
The following table lists the log fields and corresponding UDM mappings for the operation `FileCopiedToRemovableMedia` and workload `Endpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_COPY`. |
| Application | `principal.application` |
| DestinationLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceName | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| DlpAuditEventMetadata.DlpPolicyMatchId | `security_result.detection_fields.key/value` |
| DlpAuditEventMetadata.EvaluationTime | `security_result.detection_fields.key/value` |
| EnforcementMode | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.FullUrl | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.StorageName | `additional.fields.key` and `additional.fields.value.string_value` |
| FileExtension | `src.file.mime_type` |
| FileSize | `src.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Hidden | `security_result.detection_fields.key/value` |
| JitTriggered | `security_result.detection_fields.key/value` |
| MDATPDeviceId | `security_result.detection_fields.key/value` |
| MatchedPolicies.PolicyId | `security_result.detection_fields.key/value` |
| MatchedPolicies.PolicyName | `security_result.detection_fields.key/value` |
| MatchedPolicies.RuleId | `security_result.rule_id` |
| MatchedPolicies.RuleName | `security_result.rule_name` |
| ObjectId | `src.file.full_path` |
| OriginatingDomain | `principal.domain.name` |
| Platform | `target.platform` |
| PolicyMatchInfo.PolicyId | `target.resource.product_object_id` |
| PolicyMatchInfo.PolicyName | `security_result.summary` |
| PolicyMatchInfo.RuleId | `security_result.rule_id` |
| PolicyMatchInfo.RuleName | `security_result.rule_name` |
| PreviousFileName | `src.file.names` |
| RMSEncrypted | `security_result.detection_fields.key/value` |
| RemovableMediaDeviceAttributes.Manufacturer | `target.asset.hardware.manufacturer` |
| RemovableMediaDeviceAttributes.Model | `target.asset.hardware.model` |
| RemovableMediaDeviceAttributes.SerialNumber | `target.asset.hardware.serial_number` |
| Scope | `additional.fields.key` and `additional.fields.value.string_value` |
| SensitiveInfoTypeData.Confidence | `security_result.confidence_details` |
| SensitiveInfoTypeData.Count | `security_result.detection_fields.key/value` |
| SensitiveInfoTypeData.SensitiveInfoTypeId | `security_result.detection_fields.key/value` |
| SensitiveInfoTypeData.SensitiveInfoTypeName | `security_result.detection_fields.key/value` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields.key/value` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields.key/value` |
| SensitivityLabelEventData.SensitivityLabelId | `security_result.detection_fields.key/value` |
| Sha1 | `src.file.sha1` |
| Sha256 | `src.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetDomain | `target.domain.name` |
| TargetFilePath | `target.file.full_path` |
| TargetPrinterName | `target.asset.hostname` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### TaskStatusSubmitted
The following table lists the log fields and corresponding UDM mappings for the operation `TaskStatusSubmitted` and workload `Project`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_WRITTEN`. `target.resource.resource_type` is set to `TASK`. |
| ApplicationDisplayName | `principal.application` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| Entity | `metadata.product_name` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Platform | `target.platform` |
| UserAgent | `network.http.user_agent` |
### ViewTile
The following table lists the log fields and corresponding UDM mappings for the operation `ViewTile` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. `target.resource.resource_sub_type` is set to `Tile`. |
| Activity | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| ConsumptionMethod | `additional.fields.key` and `additional.fields.key/value` |
| DashboardId | `target.resource.attribute.labels.key/value` |
| DashboardName | `target.resource.attribute.labels.key/value` |
| IsSuccess | `security_result.action` |
| ObjectId | `target.resource.name` |
| RefreshEnforcementPolicy | `security_result.detection_fields.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| TileText | `target.resource.attribute.labels.key/value` |
| UserAgent | `network.http.user_agent` |
| WorkSpaceName | `target.resource.attribute.labels.key/value` |
| WorkspaceId | `target.resource.attribute.labels.key/value` |
### AppDlpEvaluationResultChange
The following table lists the log fields and corresponding UDM mappings for the operation `AppDlpEvaluationResultChange` and workload `PowerApps`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| AdditionalInfo | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
### ExportForm
The following table lists the log fields and corresponding UDM mappings for the operation `ExportForm` and workload `MicrosoftForms`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `GENERIC_EVENT`. |
| ActivityParameters.ExportFormat | `target.file.mime_type` |
| FormId | `target.resource.product_object_id` |
| FormName | `target.resource.name` |
| FormsUserType | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `target.resource.product_object_id` |
| SourceApp | `principal.application` |
### AppCleanedUpAfterExpiration
The following table lists the log fields and corresponding UDM mappings for the operation `AppCleanedUpAfterExpiration` and workload `MicrosoftTeams`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| AddOnGuid | `target.resource.product_object_id` The `AddOnGuid` log field is mapped to the `target.resource.product_object_id` UDM field. |
| AddOnType | `additional.fields.key` and `additional.fields.value.string_value` |
| AppAccessContext.IssuedAtTime | `additional.fields.key` and `additional.fields.value.string_value` |
| AppAccessContext.UniqueTokenId | `additional.fields.key` and `additional.fields.value.string_value` |
| ChatThreadId | `target.user.group_identifiers` |
| ChatThreadId | `target.group.product_object_id` |
| OperationScope | `additional.fields.key` and `additional.fields.value.string_value` |
### PlanRead
The following table lists the log fields and corresponding UDM mappings for the operation `PlanRead` and workload `Planner`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
| ContainerId | `target.resource.attribute.labels.key/value` |
| ContainerType | `target.resource.attribute.labels.key/value` |
| ObjectId | `target.resource.product_object_id` |
### FileTimelineMetadataAccessed
The following table lists the log fields and corresponding UDM mappings for the operation `FileTimelineMetadataAccessed` and workload `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_UNCATEGORIZED`. |
| AlternateStreamId | `security_result.detection_fields.key/value` |
| ApplicationDisplayName | `principal.application` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| EventSource | `target.application` |
| HighPriorityMediaProcessing | `additional.fields.key` and `additional.fields.value.string_value` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| ListBaseType | `additional.fields.key` and `additional.fields.value.string_value` |
| ListId | `security_result.detection_fields.key/value` |
| ListItemUniqueId | `target.resource.attribute.labels[list_item_unique_id]` |
| ListServerTemplate | `security_result.detection_fields.key/value` |
| ObjectId | `target.url` |
| Platform | `target.platform` |
| Site | `additional.fields.key` and `additional.fields.value.string_value` |
| SiteUrl | `target.url_metadata.url` |
| SourceFileExtension | `target.file.mime_type` |
| SourceFileName | `target.file.full_path` |
| SourceRelativeUrl | `target.file.full_path` |
| UserAgent | `network.http.user_agent` |
### TimesheetSubmitted
The following table lists the log fields and corresponding UDM mappings for the operation `TimesheetSubmitted` and workload `Project`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_UNCATEGORIZED`. `target.resource.resource_subtype` is set to `Timesheet`. |
| ApplicationDisplayName | `principal.application` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| Entity | `metadata.product_name` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Platform | `target.platform` |
| UserAgent | `network.http.user_agent` |
### ViewForm
The following table lists the log fields and corresponding UDM mappings for the operation `ViewForm` and workload `MicrosoftForms`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_ACCESS`. |
| FormId | `target.resource.product_object_id` |
| FormName | `target.resource.name` |
| FormsUserType | `additional.fields.key` and `additional.fields.value.string_value` |
| SourceApp | `principal.application` |
### TaskStatusSaved
The following table lists the log fields and corresponding UDM mappings for the operation `TaskStatusSaved` and workload `Project`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `GENERIC_EVENT`. |
| ApplicationDisplayName | `principal.application` |
| AuthenticationType | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserName | `additional.fields.key` and `additional.fields.value.string_value` |
| BrowserVersion | `additional.fields.key` and `additional.fields.value.string_value` |
| DeviceDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| Entity | `metadata.product_name` |
| EventSource | `target.application` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemType | `target.resource.attribute.labels.key/value` |
| Platform | `target.platform` |
| UserAgent | `network.http.user_agent` |
### RecordScopesConsent
The following table lists the log fields and corresponding UDM mappings for the operation `RecordScopesConsent` and workload `PowerApps`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| AppName | `additional.fields.key` and `additional.fields.value.string_value` |
| ObjectId | `additional.fields.key` and `additional.fields.value.string_value` |
### EditFlow
The following table lists the log fields and corresponding UDM mappings for the operation `EditFlow` and workload `MicrosoftFlow`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. |
| FlowConnectorNames | `target.resource.name` |
| FlowDetailsUrl | `target.url` |
| ObjectId | `target.resource.product_object_id` |
| LicenseDisplayName | `additional.fields.key` and `additional.fields.value.string_value` |
| SharingPermission | `target.resource.attribute.labels.key/value` |
| UserTypeInitiated | `principal.user.attribute.labels.key/value` |
| UserUPN | `principal.user.attribute.labels.key/value` |
### AttackSimulationEvent
The following table lists the log fields and corresponding UDM mappings for the operation `AttackSimulationEvent` and workload `AttackSimulation`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| AttackSimEvent | `security_result.detection_fields.key/value` |
| AttackTechnique | `security_result.attack_details.technique.name` |
| BatchId | `security_result.detection_fields.key/value` |
| CampaignId | `security_result.detection_fields.key/value` |
| EndTimeData | `security_result.detection_fields.key/value` |
| TimeData | `security_result.detection_fields.key/value` |
| UserDisplayName | `principal.user.user_display_name` |
### TaskAssigned
The following table lists the log fields and corresponding UDM mappings for the operation `TaskAssigned` and workload `Planner`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| ObjectId | `target.resource.product_object_id` |
| PlanId | `target.resource.attribute.labels.key/value` |
### FileTransferredByBluetooth
The following table lists the log fields and corresponding UDM mappings for the operation `FileTransferredByBluetooth` and workload `Endpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_MOVE`. |
| Application | `principal.application` |
| DeviceName | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| DlpAuditEventMetadata.DlpPolicyMatchId | `security_result.detection_fields.key/value` |
| DlpAuditEventMetadata.EvaluationTime | `security_result.detection_fields.key/value` |
| EnforcementMode | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.FullUrl | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.StorageName | `additional.fields.key` and `additional.fields.value.string_value` |
| FileExtension | `src.file.mime_type` |
| FileSize | `src.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Hidden | `security_result.detection_fields.key/value` |
| JitTriggered | `security_result.detection_fields.key/value` |
| MDATPDeviceId | `security_result.detection_fields.key/value` |
| ObjectId | `src.file.full_path` |
| Platform | `additional.fields.key` and `additional.fields.value.string_value` |
| RMSEncrypted | `security_result.detection_fields.key/value` |
| Scope | `additional.fields.key` and `additional.fields.value.string_value` |
| Sha1 | `src.file.sha1` |
| Sha256 | `src.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetDomain | `target.domain.name` |
| TargetFilePath | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetPrinterName | `target.asset.hostname` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### FileCopiedToRemoteDesktopSession
The following table lists the log fields and corresponding UDM mappings for the operation `FileCopiedToRemoteDesktopSession` and workload `Endpoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_COPY`. |
| Application | `principal.application` |
| DeviceName | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| DlpAuditEventMetadata.DlpPolicyMatchId | `security_result.detection_fields.key/value` |
| DlpAuditEventMetadata.EvaluationTime | `security_result.detection_fields.key/value` |
| EnforcementMode | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.FullUrl | `additional.fields.key` and `additional.fields.value.string_value` |
| EvidenceFile.StorageName | `additional.fields.key` and `additional.fields.value.string_value` |
| FileExtension | `src.file.mime_type` |
| FileSize | `src.file.size` |
| FileType | `target.resource.attribute.labels.key/value` |
| Hidden | `security_result.detection_fields.key/value` |
| JitTriggered | `security_result.detection_fields.key/value` |
| MDATPDeviceId | `security_result.detection_fields.key/value` |
| ObjectId | `src.file.full_path` |
| Platform | `additional.fields.key` and `additional.fields.value.string_value` |
| RMSEncrypted | `security_result.detection_fields.key/value` |
| Scope | `additional.fields.key` and `additional.fields.value.string_value` |
| Sha1 | `target.file.sha1` |
| Sha256 | `target.file.sha256` |
| SourceLocationType | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetDomain | `target.domain.name` |
| TargetFilePath | `additional.fields.key` and `additional.fields.value.string_value` |
| TargetPrinterName | `target.asset.hostname` |
### New-InsiderRiskPolicy
The following table lists the log fields and corresponding UDM mappings for the operation `New-InsiderRiskPolicy` and workload `SecurityComplianceCenter`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_CREATION`. |
| ClientApplication | `principal.application` |
| CmdletVersion | `metadata.product_version` |
| EffectiveOrganization | `target.administrative_domain` |
| ObjectId | `target.resource.product_object_id` |
| Parameters | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| SecurityComplianceCenterEventType | `additional.fields.key/value.string_value` |
| StartTime | `additional.fields[start_time]` |
| UserServicePlan | `additional.fields.key/value.string_value` |
### AutoSensitivityLabelRuleMatch
The following table lists the log fields and corresponding UDM mappings for the operation `AutoSensitivityLabelRuleMatch` and workload `Exchange`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| ConditionMatch.SensitiveInformation.ClassifierType | `security_result.detection_fields.key/value` |
| ConditionMatch.SensitiveInformation.Confidence | `security_result.confidence_details` |
| ConditionMatch.SensitiveInformation.Count | `security_result.detection_fields.key/value` |
| ConditionMatch.SensitiveInformation.Id | `security_result.detection_fields.key/value` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields.key/value` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields.key/value` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields.key/value` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields.key/value` |
| ConditionMatch.SensitiveInformation.UniqueCount | `security_result.detection_fields.key/value` |
| ExchangeMetaData.From | `network.email.from` |
| ExchangeMetaData.MessageID | `network.email.mail_id` The `ExchangeMetaData.MessageID` log field is mapped to the `network.email.mail_id` UDM field. |
| ExchangeMetaData.RecipientCount | `additional.fields.key` and `additional.fields.value.string_value` |
| ExchangeMetaData.Sent | `additional.fields.key` and `additional.fields.value.string_value` |
| ExchangeMetaData.To | `network.email.to` |
| ExecutionRuleId | `security_result.rule_id` |
| ExecutionRuleName | `security_result.rule_name` |
| ExecutionRuleVersion | `security_result.rule_version` |
| IsViewableByExternalUsers | `additional.fields.key` and `additional.fields.value.string_value` |
| ItemCreationTime | `target.resource.attribute.labels.key/value` |
| ItemLastModifiedTime | `target.resource.attribute.labels.key/value` |
| ItemSize | `target.resource.attribute.labels.key/value` |
| LabelId | `target.resource.attribute.labels.key/value` |
| LabelName | `target.resource.attribute.labels.key/value` |
| ItemName | `target.resource.name` |
| MachineName | `principal.hostname` |
| MgtRuleId | `security_result.detection_fields.key/value` |
| OverRideReason | `security_result.detection_fields.key/value` |
| OverRideType | `security_result.detection_fields.key/value` |
| PolicyId | `security_result.detection_fields.key/value` |
| PolicyName | `security_result.detection_fields.key/value` |
| PolicyVersion | `security_result.detection_fields.key/value` |
| RuleMode | `security_result.detection_fields.key/value` |
| ScopedLocationId | `security_result.detection_fields.key/value` |
| SensitiveInfoDetectionIsIncluded | `security_result.detection_fields.key/value` |
| WorkLoadItemId | `additional.fields.key` and `additional.fields.value.string_value` |
| Severity | `security_result.severity` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### GetRefreshablesForCapacityAsAdmin
The following table lists the log fields and corresponding UDM mappings for the operation `GetRefreshablesForCapacityAsAdmin` and workload `PowerBI`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `STATUS_UPDATE`. |
| Activity | `additional.fields.key` and `additional.fields.value.string_value` |
| ActivityId | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| IsSuccess | `security_result.action` |
| RefreshEnforcementPolicy | `security_result.detection_fields.key/value` |
| RequestId | `additional.fields.key` and `additional.fields.value.string_value` |
| UserAgent | `network.http.user_agent` |
### WriteUserObjPreference
The following table lists the log fields and corresponding UDM mappings for the operation `WriteUserObjPreference` and workload `MicrosoftTeams`:
| Log field | UDM mapping |
|---|---|
| UserKey | `additional.fields.key` and `additional.fields.value.string_value` |
| RecordType | `security_result.detection_fields.key/value` |
| UserClaims | `security_result.description` |
### Set-TransportRule
The following table lists the log fields and corresponding UDM mappings for the operation `Set-TransportRule` and workload `Exchange`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_CONTENT`. |
| | `target.resource.resource_type` is mapped to `ACCESS_POLICY`. |
| ExternalAccess | `principal.user.attributes.labels[external_access]` |
| ObjectId | `target.resource.name` |
| Parameters.ExceptIfSentTo | `additional.fields[ExceptIfSentTo]` |
| Parameters.FromScope | `additional.fields[FromScope]` |
| Parameters.Identity | `target.resource.product_object_id` |
| Parameters.Name | `target.resource.attribute.labels[parameters_name]` |
| Parameters.RedirectMessageTo | `additional.fields[RedirectMessageTo]` |
| Parameters.SentToScope | `additional.fields[SentToScope]` |
| Parameters.SubjectOrBodyContainsWords | `additional.fields[SubjectOrBodyContainsWords]` |
| ResultStatus | If the `ResultStatus` log field value is equal to `True` then, the `security_result.action` UDM field is set to `ALLOW`. Else, if `ResultStatus` log field value is equal to `False` then, the `security_result.action` UDM field is set to `BLOCK`. |
### AtpDetection
The following table lists the log fields and corresponding UDM mappings for the operation `AtpDetection` and workload `ThreatIntelligence`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `SCAN_FILE`. |
| DetectionMethod | `security_result.detection_fields[detection_method]` |
| LastModifiedBy | `about.user.userid` |
| SourceWorkload | `src.application`
If the `Operation` log field is equal to `AtpDetection`: - If the `SourceWorkload` log field is equal to `1`, then the UDM field `src.application` is set to `OneDrive`. - If the `SourceWorkload` log field is equal to `0`, then the UDM field `src.application` is set to `SharePoint`. - If the `SourceWorkload` log field is equal to `2`, then the UDM field `src.application` is set to `Microsoft Teams`. |
### Set-OrganizationConfig
The following table lists the log fields and corresponding UDM mappings for the operation `Set-OrganizationConfig` and workload `Exchange`:
| Log field | UDM mapping | Logic |
|---|---|---|
| | `metadata.event_type` is mapped to `SETTING_MODIFICATION` `target.resource.resource_type` is set to `SETTING` `ObjectId` is mapped to `target.resource.name` | |
| `ExternalAccess` | `principal.user.attribute.labels[ExternalAccess]` | |
| `Parameters` | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
### PlanSharedWithContainerAdded
The following table lists the log fields and corresponding UDM mappings for the operation `PlanSharedWithContainerAdded` and workload `Planner`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_RESOURCE_UPDATE_PERMISSIONS`. |
| ContainerId | `target.resource.attribute.labels[container_id]` |
| ContainerType | If the `ContainerType` log field value is equal to `0` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `Invalid`. Else, if `ContainerType` log field value is equal to `2` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `Group`. Else, if `ContainerType` log field value is equal to `3` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `TeamsConversation`. Else, if `ContainerType` log field value is equal to `4` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `OfficeDocument`. Else, if `ContainerType` log field value is equal to `5` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `Roster`. Else, if `ContainerType` log field value is equal to `6` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `Project`. Else, if `ContainerType` log field value is equal to `7` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `User`. Else, if `ContainerType` log field value is equal to `8` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `TeamsChannel`. Else, if `ContainerType` log field value is equal to `10` then, the `target.resource.attribute.labels.key` UDM field is set to `container_type` and the `target.resource.attribute.labels.value` UDM field is set to `PlannerTask`. |
| ObjectId | `target.resource.product_object_id`. |
### UnifiedSimulationRuleMatch
The following table lists the log fields and corresponding UDM mappings for the operation `UnifiedSimulationRuleMatch` and workload `OneDriveForBusiness`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `SCAN_UNCATEGORIZED` |
| ExecutionRuleId | `security_result.rule_id` |
| ObjectId | `target.resource.product_object_id` |
| ExecutionRuleName | `security_result.rule_name` |
| ExecutionRuleVersion | `security_result.rule_version` |
| LabelId | `target.resource.attribute.labels[LabelId]` |
| LabelName | `target.resource.attribute.labels[LabelName]` |
| MachineName | `principal.hostname` |
| PolicyName | `security_result.rule_set` |
| PolicyVersion | `security_result.detection_fields[PolicyVersion]` |
| RuleMode | `security_result.detection_fields[RuleMode]` |
| Severity | `security_result.severity` |
| ScopedLocationId | `additional.fields[ScopedLocationId]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Confidence | `security_result.detection_fields[Confidence]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.Count | `security_result.detection_fields[Count]` |
| SensitiveInfoTypeData.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| ConditionMatch.OtherConditions | `security_result.detection_fields[%{Name}]` |
| ConditionMatch.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| ConditionMatch.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.Actions | `security_result.action_details` |
| PolicyDetails.Rules.OverriddenActions | `security_result.action_details` |
| PolicyDetails.Rules.ConditionsMatched.OtherConditions | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveType | `security_result.detection_fields[SensitiveType]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.Location | `security_result.detection_fields[SensitiveInfoLocation]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetailedClassificationAttributes.IsMatch | `security_result.detection_fields[IsMatch]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.DetectedValues | `security_result.detection_fields[%{Name}]` |
| PolicyDetails.Rules.ConditionsMatched.SensitiveInformation.SensitiveInformationDetections.ResultsTruncated | `security_result.detection_fields[ResultsTruncated]` |
### IDCRLBlockedDueToSoftEnforcement
The following table lists the log fields and corresponding UDM mappings for the operation `IDCRLBlockedDueToSoftEnforcement` and workload `SharePoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `USER_LOGIN` |
| IsManagedDevice | `additional.fields.key` and `additional.fields.value.string_value` |
| | `extensions.auth.type` is mapped to `SSO` |
### FileVersionDeleted
The following table lists the log fields and corresponding UDM mappings for the operation `FileVersionDeleted` and workload `OneDrive`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_DELETION` ObjectId is mapped to target.url |
| SourceFileName | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | target.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
### FilePreserved
The following table lists the log fields and corresponding UDM mappings for the operation `FilePreserved` and workload `SharePoint`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `FILE_UNCATEGORIZED` ObjectId is mapped to target.url |
| SourceFileExtension | `src.file.mime_type` |
| DestinationFileExtension | `target.file.mime_type` |
| SourceFileName | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| SourceRelativeUrl | src.file.full_path is set to {SourceRelativeUrl}/{SourceFileName} |
| DestinationRelativeUrl | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| DestinationFileName | target.file.full_path is set to {DestinationRelativeUrl}/{DestinationFileName} |
| FileSizeBytes | `target.file.size` |
### RecipientChange
The following table lists the log fields and corresponding UDM mappings for the operation `RecipientChange` and workload `Exchange`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `EMAIL_UNCATEGORIZED` |
### GroupMemberRoleAdded
The following table lists the log fields and corresponding UDM mappings for the operation `GroupMemberRoleAdded` and workload `Yammer`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `GROUP_MODIFICATION` ObjectId is mapped to target.group.product_object_id If ResultStatus is TRUE then action is ALLOW Otherwise action is BLOCK |
| ActorUserId | `principal.user.email_addresses` |
| IsSoftDelete | `security_result.description` security_result.description is set to IsSoftDelete - %{IsSoftDelete} |
| DataExportType | `target.resource.attribute.labels.key/value` |
| TargetYammerUserId | `target.user.userid` |
| ObjectId | `about.resource.product_object_id` |
| ThreadId | `target.resource.product_object_id` |
### ConnectedAIAppInteraction
The following table lists the log fields and corresponding UDM mappings for the operation `ConnectedAIAppInteraction` and workload `ConnectedAIApp` or `Copilot`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
| ApplicationName | `target.application` |
| ConversationId | `network.session_id` |
| CopilotEventData.ConversationId | `security_result.detection_fields[ConversationId]` |
| CopilotEventData.CorrelationId | `additional.fields[CorrelationId]` |
| CopilotEventData.SensitivityLabelId | `target.resource.attribute.labels[SensitivityLabelId]` |
| CopilotEventData.AccessedResources.listItemUniqueId | `about.resource.product_object_id` |
| CopilotEventData.AccessedResources.PolicyDetails.PolicyType | `security_result.rule_type` |
| CopilotEventData.AccessedResources.PolicyDetails.PolicyOutcomes | `security_result.action_details` |
| CopilotEventData.Messages.Id | `about.resource.product_object_id` |
| CopilotEventData.Messages.isPrompt | `security_result.detection_fields[isPrompt]` |
| CopilotEventData.Messages.JailbreakDetected | `security_result.detection_fields[JailbreakDetected]` |
| CopilotEventData.AISystemPlugin.Id | `about.resource.product_object_id` |
| CopilotEventData.AISystemPlugin.Name | `about.resource.name` |
| CopilotEventData.ParticipatingAgents.AgentId | `about.resource.product_object_id` |
| CopilotEventData.ParticipatingAgents.AgentName | `about.resource.name` |
| Workload | `additional.fields[Workload]` |
### MessageRead
The following table lists the log fields and corresponding UDM mappings for the operation `MessageRead` and workload `MicrosoftTeams`:
| Log field | UDM mapping |
|---|---|
| | `metadata.event_type` is mapped to `RESOURCE_READ`. |
| MessageId | `target.resource.product_object_id` |
### ProtectionApplied
The following table lists the log fields and corresponding UDM mappings for the operation `ProtectionApplied` and workload `Aip`:
| Log field | UDM mapping |
|---|---|
| Common.Location | `target.location.name` |
## UDM Mapping Delta
> [!NOTE]
> **Note:** In this delta, "Old UDM Mapping" refer to releases before April 9th, 2026. Versions released after April 9th, 2026 include the following "New UDM Mapping".
### UDM Event Type Mapping Delta
The following table lists the delta between the old UDM Mapping of `Microsoft Office 365` and the new UDM Mapping of `Microsoft Office 365`.
#### UDM Event Type Delta
| **Operation** | **Old UDM Event Type** | **New UDM Event Type** |
|---|---|---|
| FileDownloaded | USER_RESOURCE_UPDATE_CONTENT | FILE_UNCATEGORIZED |
| FileUploaded | FILE_SYNC | FILE_UNCATEGORIZED |
| FileCheckedIn | USER_RESOURCE_UPDATE_CONTENT | FILE_MODIFICATION |
| FileCheckedOut | USER_RESOURCE_ACCESS | FILE_UNCATEGORIZED |
| LockRecord | USER_CHANGE_PERMISSIONS | RESOURCE_PERMISSIONS_CHANGE |
| UnlockRecord | USER_CHANGE_PERMISSIONS | RESOURCE_PERMISSIONS_CHANGE |
| FileCheckOutDiscarded | USER_RESOURCE_UPDATE_CONTENT | FILE_UNCATEGORIZED |
| FileRestored | FILE_UNCATEGORIZED | FILE_MOVE |
| FileMalwareDetected | GENERIC_EVENT | SCAN_UNCATEGORIZED |
| PageViewed | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_ACCESS |
| PagePrefetched | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_ACCESS |
| ClientViewSignaled | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_ACCESS |
| PageViewedExtended | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_ACCESS |
| FolderDeleted | FILE_DELETION | USER_RESOURCE_DELETION |
| FileSyncDownloadedFull | USER_RESOURCE_UPDATE_CONTENT | FILE_UNCATEGORIZED |
| FileSyncDownloadedPartial | USER_RESOURCE_UPDATE_CONTENT | FILE_UNCATEGORIZED |
| FileSyncUploadedFull | FILE_SYNC | FILE_UNCATEGORIZED |
| FileSyncUploadedPartial | FILE_SYNC | FILE_UNCATEGORIZED |
| ManagedSyncClientAllowed | RESOURCE_WRITTEN | STATUS_UNCATEGORIZED |
| UnmanagedSyncClientBlocked | USER_RESOURCE_UPDATE_PERMISSIONS | STATUS_UNCATEGORIZED |
| CompanyLinkCreated | USER_RESOURCE_CREATION | RESOURCE_PERMISSIONS_CHANGE |
| SecureLinkCreated | USER_RESOURCE_CREATION | RESOURCE_PERMISSIONS_CHANGE |
| SharingInvitationCreated | USER_RESOURCE_ACCESS | RESOURCE_PERMISSIONS_CHANGE |
| SecureLinkDeleted | USER_RESOURCE_DELETION | RESOURCE_PERMISSIONS_CHANGE |
| SecureLinkUpdated | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_PERMISSIONS_CHANGE |
| SharingSet | FILE_SYNC | USER_RESOURCE_UPDATE_PERMISSIONS |
| PermissionLevelAdded | USER_CHANGE_PERMISSIONS | USER_RESOURCE_UPDATE_PERMISSIONS |
| SharingInvitationBlocked | USER_UNCATEGORIZED | RESOURCE_PERMISSIONS_CHANGE |
| AccessRequestCreated | USER_RESOURCE_ACCESS | RESOURCE_PERMISSIONS_CHANGE |
| AnonymousLinkCreated | USER_RESOURCE_CREATION | RESOURCE_PERMISSIONS_CHANGE |
| AccessRequestUpdated | STATUS_UPDATE | RESOURCE_PERMISSIONS_CHANGE |
| CompanyLinkRemoved | USER_RESOURCE_DELETION | RESOURCE_PERMISSIONS_CHANGE |
| AnonymousLinkRemoved | USER_RESOURCE_DELETION | RESOURCE_PERMISSIONS_CHANGE |
| SharingInvitationUpdated | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_PERMISSIONS_CHANGE |
| Change user license | USER_RESOURCE_UPDATE_PERMISSIONS | USER_CHANGE_PERMISSIONS |
| Disable account | USER_RESOURCE_DELETION | USER_CHANGE_PERMISSIONS |
| Add owner to group | USER_CHANGE_PERMISSIONS | GROUP_MODIFICATION |
| Add OAuth2PermissionGrant | USER_CHANGE_PERMISSIONS | RESOURCE_PERMISSIONS_CHANGE |
| Add device | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_CREATION |
| Consent to application | USER_RESOURCE_ACCESS | RESOURCE_PERMISSIONS_CHANGE |
| Update service principal | USER_RESOURCE_UPDATE_CONTENT | STATUS_UPDATE |
| Remove service principal | USER_RESOURCE_DELETION | STATUS_UPDATE |
| Add member to role | USER_UNCATEGORIZED | USER_CHANGE_PERMISSIONS |
| Remove member from role | USER_UNCATEGORIZED | USER_CHANGE_PERMISSIONS |
| ClockedIn | USER_RESOURCE_UPDATE_CONTENT | STATUS_UPDATE |
| BreakStarted | USER_RESOURCE_UPDATE_CONTENT | STATUS_UPDATE |
| BreakEnded | USER_RESOURCE_UPDATE_CONTENT | STATUS_UPDATE |
| ClockedOut | USER_CHANGE_PERMISSIONS | STATUS_UPDATE |
| BotAddedToTeam | GROUP_MODIFICATION | USER_RESOURCE_CREATION |
| BotRemovedFromTeam | GROUP_MODIFICATION | USER_RESOURCE_DELETION |
| SendOnBehalf | EMAIL_UNCATEGORIZED | EMAIL_TRANSACTION |
| SendAs | EMAIL_UNCATEGORIZED | EMAIL_TRANSACTION |
| Send | EMAIL_UNCATEGORIZED | EMAIL_TRANSACTION |
| MoveToDeletedItems | USER_RESOURCE_UPDATE_CONTENT | EMAIL_UNCATEGORIZED |
| Move | USER_RESOURCE_UPDATE_CONTENT | EMAIL_UNCATEGORIZED |
| RemoveFolderPermissions | USER_CHANGE_PERMISSIONS | RESOURCE_PERMISSIONS_CHANGE |
| ModifyFolderPermissions | USER_CHANGE_PERMISSIONS | RESOURCE_PERMISSIONS_CHANGE |
| AddFolderPermissions | USER_CHANGE_PERMISSIONS | RESOURCE_PERMISSIONS_CHANGE |
| UpdateInboxRules | USER_RESOURCE_UPDATE_CONTENT | SETTING_MODIFICATION |
| UpdateCalendarDelegation | USER_RESOURCE_UPDATE_CONTENT | USER_CHANGE_PERMISSIONS |
| Set-User | USER_CREATION | USER_UNCATEGORIZED |
| GenerateEmbedToken | USER_CHANGE_PERMISSIONS | GENERIC_EVENT |
| ChangeGatewayAdministrators | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_PERMISSIONS_CHANGE |
| InsertOrganizationalGalleryItem | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_CREATION |
| DeleteComment | USER_RESOURCE_DELETION | GENERIC_EVENT |
| DownloadReport | USER_RESOURCE_ACCESS | FILE_UNCATEGORIZED |
| ExportDataflow | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| ExportReport | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| InstallApp | USER_RESOURCE_ACCESS | USER_RESOURCE_CREATION |
| InstallTemplateApp | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_CREATION |
| PostComment | SYSTEM_AUDIT_LOG_UNCATEGORIZED | USER_RESOURCE_UPDATE_CONTENT |
| PrintDashboard | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| PrintReport | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| RequestDataflowRefresh | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| RefreshDataset | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| SensitivityLabelApplied | SETTING_CREATION | STATUS_UPDATE |
| SensitivityLabelRemoved | SETTING_DELETION | STATUS_UPDATE |
| ShareDashboard | USER_UNCATEGORIZED | USER_RESOURCE_UPDATE_PERMISSIONS |
| ShareReport | USER_UNCATEGORIZED | USER_RESOURCE_UPDATE_PERMISSIONS |
| OptInForProTrial | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| UpdateAlmPipelineAccess | SYSTEM_AUDIT_LOG_UNCATEGORIZED | RESOURCE_PERMISSIONS_CHANGE |
| RunEmailSubscription | SCHEDULED_TASK_CREATION | SCHEDULED_TASK_UNCATEGORIZED |
| Set-MailUser | EMAIL_UNCATEGORIZED | USER_UNCATEGORIZED |
| Set-CASMailbox | EMAIL_UNCATEGORIZED | SETTING_MODIFICATION |
| Remove-MigrationUser | USER_DELETION | USER_UNCATEGORIZED |
| AnnotateDocument | USER_RESOURCE_ACCESS | USER_RESOURCE_UPDATE_CONTENT |
| TagFiles | USER_UNCATEGORIZED | USER_RESOURCE_UPDATE_CONTENT |
| CaseMemberAdded | USER_CREATION | RESOURCE_PERMISSIONS_CHANGE |
| SearchUpdated | USER_RESOURCE_ACCESS | USER_RESOURCE_UPDATE_CONTENT |
| CaseAdminUpdated | GROUP_MODIFICATION | RESOURCE_PERMISSIONS_CHANGE |
| CaseMemberUpdated | GROUP_MODIFICATION | RESOURCE_PERMISSIONS_CHANGE |
| SearchRemoved | USER_UNCATEGORIZED | RESOURCE_DELETION |
| CaseAdminRemoved | USER_DELETION | RESOURCE_PERMISSIONS_CHANGE |
| SearchPermissionRemoved | USER_UNCATEGORIZED | RESOURCE_PERMISSIONS_CHANGE |
| SearchCreated | USER_RESOURCE_ACCESS | USER_RESOURCE_CREATION |
| CaseAdminAdded | USER_CREATION | RESOURCE_PERMISSIONS_CHANGE |
| SearchStopped | USER_UNCATEGORIZED | STATUS_UPDATE |
| CaseMemberRemoved | USER_DELETION | RESOURCE_PERMISSIONS_CHANGE |
| SearchPermissionCreated | USER_UNCATEGORIZED | RESOURCE_CREATION |
| DataExport | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_ACCESS |
| StreamInvokeVideoView | USER_COMMUNICATION | USER_RESOURCE_ACCESS |
| StreamInvokeVideoDownload | USER_COMMUNICATION | USER_RESOURCE_ACCESS |
| StreamInvokeVideoSetLink | USER_COMMUNICATION | RESOURCE_PERMISSIONS_CHANGE |
| StreamEditVideoPermissions | USER_COMMUNICATION | RESOURCE_PERMISSIONS_CHANGE |
| StreamEditVideo | USER_COMMUNICATION | USER_RESOURCE_UPDATE_CONTENT |
| StreamDeleteVideo | USER_COMMUNICATION | USER_RESOURCE_DELETION |
| StreamEditUserSettings | USER_COMMUNICATION | SETTING_MODIFICATION |
| StreamInvokeVideoThumbnailUpload | USER_COMMUNICATION | USER_RESOURCE_UPDATE_CONTENT |
| StreamCreateVideo | USER_COMMUNICATION | USER_RESOURCE_CREATION |
| DlpRuleMatch | EMAIL_TRANSACTION | For Workload Onedrive/Sharepoint -\> SCAN_FILE For Workload Exchange -\> EMAIL_UNCATEGORIZED |
| DlpRuleUndo | EMAIL_TRANSACTION | STATUS_UPDATE |
| DlpInfo | EMAIL_TRANSACTION | For Workload Onedrive/Sharepoint -\> SCAN_FILE For Workload Exchange -\> EMAIL_UNCATEGORIZED |
| SharingPolicyChanged | USER_RESOURCE_UPDATE_PERMISSIONS | SETTING_MODIFICATION |
| NetworkAccessPolicyChanged | USER_RESOURCE_UPDATE_PERMISSIONS | SETTING_MODIFICATION |
| Get-CaseHoldPolicy | SETTING_UNCATEGORIZED | USER_RESOURCE_ACCESS |
| Remove-CaseHoldPolicy | SETTING_DELETION | USER_RESOURCE_DELETION |
| Set-CaseHoldPolicy | SETTING_MODIFICATION | USER_RESOURCE_UPDATE_CONTENT |
| New-ComplianceCase | SETTING_CREATION | USER_RESOURCE_CREATION |
| Set-ComplianceCase | SETTING_MODIFICATION | RESOURCE_WRITTEN |
| Add-ComplianceCaseMember | USER_CREATION | RESOURCE_PERMISSIONS_CHANGE |
| Remove-ComplianceCaseMember | USER_DELETION | RESOURCE_PERMISSIONS_CHANGE |
| Update-ComplianceCaseMember | GROUP_MODIFICATION | RESOURCE_PERMISSIONS_CHANGE |
| New-ComplianceSearch | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| Remove-ComplianceSearch | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| Set-ComplianceSearch | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| Start-ComplianceSearch | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| Stop-ComplianceSearch | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| New-ComplianceSearchAction | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| Remove-ComplianceSearchAction | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| New-ComplianceSecurityFilter | USER_UNCATEGORIZED | USER_RESOURCE_CREATION |
| Remove-ComplianceSecurityFilter | USER_UNCATEGORIZED | USER_RESOURCE_DELETION |
| Set-ComplianceSecurityFilter | USER_UNCATEGORIZED | USER_RESOURCE_UPDATE_CONTENT |
| Add-eDiscoveryCaseAdmin | USER_CREATION | USER_CHANGE_PERMISSION |
| Remove-eDiscoveryCaseAdmin | USER_DELETION | USER_CHANGE_PERMISSION |
| New-CaseHoldPolicy | SETTING_CREATION | USER_RESOURCE_CREATION |
| Get-AutoSensitivityLabelPolicy | STATUS_UNCATEGORIZED | GENERIC_EVENT |
| Get-DlpSensitiveInformationType | STATUS_UNCATEGORIZED | GENERIC_EVENT |
| Get-Label | STATUS_UNCATEGORIZED | GENERIC_EVENT |
| Get-LabelPolicy | STATUS_UNCATEGORIZED | GENERIC_EVENT |
| Get-PolicyConfig | STATUS_UNCATEGORIZED | GENERIC_EVENT |
| ApplicableAdaptiveScopeChange | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| NewRetentionCompliancePolicy | SETTING_CREATION | USER_RESOURCE_CREATION |
| Get-ComplianceTag | USER_RESOURCE_ACCESS | GENERIC_EVENT |
| NewComplianceTag | USER_RESOURCE_CREATION | SETTING_CREATION |
| SetComplianceTag | USER_RESOURCE_UPDATE_CONTENT | SETTING_MODIFICATION |
| Remove-ComplianceTag | USER_RESOURCE_DELETION | SETTING_DELETION |
| RemoveRetentionCompliancePolicy | SETTING_DELETION | USER_RESOURCE_DELETION |
| SetRetentionCompliancePolicy | SETTING_MODIFICATION | USER_RESOURCE_UPDATE_CONTENT |
| Get-CsTeamsUpgradeOverridePolicy | USER_COMMUNICATION | USER_RESOURCE_ACCESS |
| TeamsAdminAction | USER_CHANGE_PERMISSIONS | USER_UNCATEGORIZED |
| TIMailData | EMAIL_TRANSACTION | EMAIL_UNCATEGORIZED |
| Update label | USER_RESOURCE_UPDATE_CONTENT | STATUS_UPDATE |
| SiteLocksChanged | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_PERMISSIONS_CHANGE |
| ShortcutAdded | USER_RESOURCE_CREATION | RESOURCE_PERMISSIONS_CHANGE |
| Set-PolicyConfig | USER_RESOURCE_UPDATE_CONTENT | SETTING_MODIFICATION |
| New-ConditionalAccessPolicy | USER_UNCATEGORIZED | USER_RESOURCE_CREATION |
| Set-RetentionCompliancePolicy | SETTING_MODIFICATION | USER_RESOURCE_UPDATE_CONTENT |
| Enable-AddressListPaging | RESOURCE_READ | SETTING_MODIFICATION |
| Install-DataClassificationConfig | SYSTEM_AUDIT_LOG_UNCATEGORIZED | SETTING_MODIFICATION |
| New-RetentionComplianceRule | USER_RESOURCE_CREATION | SETTING_CREATION |
| New-AppRetentionComplianceRule | GENERIC_EVENT | SETTING_CREATION |
| New-AppRetentionCompliancePolicy | GENERIC_EVENT | USER_RESOURCE_CREATION |
| Set-AppRetentionCompliancePolicy | GENERIC_EVENT | USER_RESOURCE_UPDATE_CONTENT |
| New-ComplianceTag | USER_UNCATEGORIZED | SETTING_CREATION |
| Set-ComplianceTag | GENERIC_EVENT | SETTING_MODIFICATION |
| Get-AppRetentionCompliancePolicy | GENERIC_EVENT | USER_RESOURCE_ACCESS |
| Get-CaseHoldRule | SETTING_UNCATEGORIZED | GENERIC_EVENT |
| Get-RetentionComplianceRule | USER_RESOURCE_ACCESS | GENERIC_EVENT |
| Set-RetentionComplianceRule | USER_UNCATEGORIZED | SETTING_MODIFICATION |
| New-RetentionComplianceRule | USER_RESOURCE_CREATION | SETTING_CREATION |
| RemoveRetentionComplianceRule | USER_RESOURCE_DELETION | SETTING_DELETION |
| CommentCreated | USER_UNCATEGORIZED | GENERIC_EVENT |
| HeartBeat | USER_RESOURCE_CREATION | STATUS_HEARTBEAT |
| StreamEditAdminGlobalRoleMembers | USER_COMMUNICATION | USER_CHANGE_PERMISSION |
| New-App | STATUS_UNCATEGORIZED | GENERIC_EVENT |
| PublishToWebReport | SYSTEM_AUDIT_LOG_UNCATEGORIZED | GENERIC_EVENT |
| ShareDataset | USER_UNCATEGORIZED | USER_RESOURCE_UPDATE_PERMISSIONS |
| GetRefreshablesAsAdmin | USER_RESOURCE_ACCESS | GENERIC_EVENT |
| Add owner to application | USER_UNCATEGORIZED | USER_CHANGE_PERMISSION |
| Add policy | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_CREATION |
| SubmitResponse | USER_RESOURCE_CREATION | USER_RESOURCE_UPDATE_CONTENT |
| ViewResponses | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_ACCESS |
| ViewRuntimeForm | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_ACCESS |
| ListViewed | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_ACCESS |
| MessageCreatedHasLink | USER_RESOURCE_CREATION | USER_UNCATEGORIZED |
| InsightGenerated | USER_RESOURCE_CREATION | GENERIC_EVENT |
| UserSubmission | EMAIL_UNCATEGORIZED | SCAN_UNCATEGORIZED |
| SaveRoleGroupMember | STATUS_UNCATEGORIZED | USER_RESOURCE_UPDATE_PERMISSIONS |
| AggregateCampaignIntelligenceData | STATUS_UNCATEGORIZED | SYSTEM_AUDIT_LOG_UNCATEGORIZED |
| Get-User | STATUS_UNCATEGORIZED | RESOURCE_READ |
| Get-DlpComplianceRule | STATUS_UNCATEGORIZED | RESOURCE_READ |
| FileDownloadedFromBrowser | USER_RESOURCE_UPDATE_CONTENT | FILE_UNCATEGORIZED |
| Device no longer managed | USER_RESOURCE_DELETION | STATUS_UPDATE |
| Device no longer compliant | USER_RESOURCE_UPDATE_PERMISSIONS | STATUS_UPDATE |
| Enable account | USER_RESOURCE_UPDATE_PERMISSIONS | USER_CHANGE_PERMISSIONS |
| Add app role assignment to group | GROUP_UNCATEGORIZED | USER_RESOURCE_UPDATE_PERMISSIONS |
| GroupAccessFailure | GROUP_UNCATEGORIZED | USER_RESOURCE_ACCESS |
| Enable Strong Authentication | USER_RESOURCE_UPDATE_PERMISSIONS | SETTING_MODIFICATION |
| ReactedToMessage | USER_RESOURCE_UPDATE_CONTENT | USER_COMMUNICATION |
| RemovableMediaUnmount | USER_UNCATEGORIZED | USER_RESOURCE_UPDATE_CONTENT |
| FileUploadedToCloud | FILE_SYNC | FILE_UNCATEGORIZED |
| GenerateDataflowSasToken | USER_CHANGE_PERMISSIONS | USER_RESOURCE_ACCESS |
| RemovableMediaMount | USER_UNCATEGORIZED | RESOURCE_READ |
| SignInEvent | USER_UNCATEGORIZED | USER_LOGIN |
| ListForms | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_READ |
| ListCreated | USER_RESOURCE_UPDATE_CONTENT | USER_RESOURCE_CREATION |
| GetWorkspaces | STATUS_UPDATE | RESOURCE_READ |
| ViewResponse | USER_RESOURCE_UPDATE_CONTENT | RESOURCE_READ |
| PublicEndpoint | GENERIC_EVENT | STATUS_UPDATE |
| SharingLinkCreated | RESOURCE_CREATION | RESOURCE_PERMISSIONS_CHANGE |
| TimesheetSaved | RESOURCE_READ | RESOURCE_WRITTEN |
| SharingLinkUpdated | RESOURCE_WRITTEN | RESOURCE_PERMISSIONS_CHANGE |
| AddedToSharingLink | RESOURCE_WRITTEN | RESOURCE_PERMISSIONS_CHANGE |
| ExportForm | USER_UNCATEGORIZED | GENERIC_EVENT |
| TaskStatusSaved | USER_UNCATEGORIZED | GENERIC_EVENT |
| EditFlow | USER_UNCATEGORIZED | USER_RESOURCE_UPDATE_CONTENT |
| TaskAssigned | USER_UNCATEGORIZED | STATUS_UPDATE |
| FileTransferredByBluetooth | FILE_UNCATEGORIZED | FILE_MOVE |
| FileCopiedToRemoteDesktopSession | FILE_UNCATEGORIZED | FILE_COPY |
| New-InsiderRiskPolicy | STATUS_UPDATE | RESOURCE_CREATION |
### Common fields Mapping Delta
The following table lists the common log fields delta between old UDM mapping of `OFFICE_365` and new UDM mapping of `OFFICE_365`.
| Log Field | Old UDM Mapping | New UDM Mapping |
|---|---|---|
| `StartTime` | `target.resource.attribute.creation_time` | `additional.fields[start_time]` |
| `EndTime` | `target.resource.attribute.last_update_time` | `additional.fields[end_time]` |
| `EventSource` | `principal.application` | `target.application` |
| `SiteUrl` | `network.http.referral_url` | `target.url_metadata.url` |
| `ListId` | `security_result.detection_fields[ListId]` | `target.resource.attribute.labels[ListId]` |
| `ListItemUniqueId` | `principal.asset_id` | `target.resource.attribute.labels[list_item_unique_id]` |
| `SensitivityLabelOwnerEmail` | `security_result.detection_fields[SensitivityLabelOwnerEmail]` | `about.user.email_addresses` |
| `ActorYammerUserId` | `principal.labels[ActorYammerUserId]` `additional.fields[ActorYammerUserId]` | `principal.user.userid` |
| `TargetYammerUserId` | `target.labels[TargetYammerUserId]` `additional.fields[TargetYammerUserId]` | `target.user.userid` |
| `ApplicationDisplayName` | `target.application` `target.resource.name` | `principal.application` |
| `ApplicationId` | `target.resource.product_object_id` | `additional.fields[ApplicationId]` |
| `SourceFileUrl` | `src.file.full_path` | `src.url` |
| `TargetFileUrl` | `target.file.full_path` | `target.url` |
| `ActorContextId` | `principal.labels[ActorContextId]` `additional.fields[ActorContextId]` | `additional.fields[ActorContextId]` |
| `PolicyDetails.PolicyName` | `security_result.summary` | `security_result.rule_set` |
| `PolicyDetails.PolicId` | `target.resource.product_object_id` | `security_result.rule_labels` |
| `FileType` | `target.resource.attribute.labels[FileType]` | `about.file.mime_type` |
| `Action` | `security_result.description` | `security_resultaction_details` |
| `DevicePhysicalIds` | `security_result.description` | `target.resource.attribute.labels[device_physical_ids]` |
| `Item.Attachments` | `target.file.names` | `about.file.names` |
| `Item.ParentFolder.Path` | `target.resource.name` | `target.file.full_path` |
| `Item.Id` | `target.resource.product_object_id` | `additional.fields[item_id]` |
| `GatewayType` | `target.labels[GatewayType]` | `target.resource.attribute.labels[GatewayType]` |
| `EntityPath` | `metadata.url.back_to_product` | `additional.fields[entity_path]` |
| `ExchangeMetaData.MessageID` | `additional.fields[ExchangeMetaData_MessageID]` | `network.email.mail_id` |
| `P1SenderDomain` | `principal.administrative_domain` | `network.dns_domain` |
| `ActorUserId` | `principal.user.email_addresses` `principal.user.userid` `principal.labels[userid]` `additional.fields[userid]`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` and the `ActorUserId` log field value is not `empty` and not equal to `NOT-FOUND` then, If the `ActorUserId` value matches the regular expression pattern `(^.+@.+$)` and matches the regular expression pattern `(^.{0,256}$)` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field and the `ActorUserId` log field is mapped to the `principal.user.userid` UDM field. Else, if the `ActorUserId` value matches the regular expression pattern `(^.{0,256}$)` then, the `ActorUserId` log field is mapped to the `principal.user.userid` UDM field. Else, the `principal.labels.key` UDM field is set to `userid`, the `ActorUserId` log field is mapped to the `principal.labels.value` UDM field, the `additional.fields.key` UDM field is set to `userid`, and the `ActorUserId` log field is mapped to the `additional.fields.value` UDM field. | `principal.user.email_addresses`
If the `Workload` log field value is equal to `Yammer` and the `Operation` log field value is one of the following: - `GroupCreation` - `GroupDeletion` - `FileVisited` - `FileCreated` - `MessageDeleted` - `NetworkSecurityConfigurationUpdated` - `NetworkConfigurationUpdated` - `DataExport` - `MessageCreation` - `ThreadViewed` - `ProcessProfileFields` - `SupervisorAdminToggled` - `MessageUpdated` - `GroupAccessFailure` - `O365SyncAdminUserPromotion` then, the `ActorUserId` log field is mapped to the `principal.user.email_addresses` UDM field. |
| `Target` | `target.group.group_display_name` `target.resource.name` `target.user.email_addresses` `target.user.userid` `target.labels` `additional.fields` `security_result.detection_fields`
Iterate for each element `field` in the `Target` log field array, then If the `Operation` log field value is one of the following: - `Delete group.` - `Add group.` - `Update group.` and the `field.Type` value is equal to `1` then, the `field.ID` log field is mapped to the `target.group.group_display_name` UDM field. Else, if the `Operation` log field value is one of the following: - `Set federation settings on domain.` - `Set Company Information.` - `Consent to application.` - `Verify domain.` - `Update device.` - `Delete device.` - `Add device.` and the `field.Type` value is equal to `1` then, the `field.ID` log field is mapped to the `target.resource.name` UDM field. Else, if the `field.Type` value is equal to `5` then, If the `field.ID` value is not `empty` then, If the `field.ID` value matches the regular expression pattern `(^.+@.+$)` and matches the regular expression pattern `(^.{0,256}$)` then, the `field.ID` log field is mapped to the `target.user.email_addresses` UDM field and the `field.ID` log field is mapped to the `target.user.userid` UDM field. Else, if the `field.ID` value matches the regular expression pattern `(^.{0,256}$)` then, the `field.ID` log field is mapped to the `target.user.userid` UDM field. Else, the `target.labels.key` UDM field is set to `userid`, the `field.ID` log field is mapped to the `target.labels.value` UDM field, the `additional.fields.key` UDM field is set to `userid`, and the `field.ID` log field is mapped to the `additional.fields.value` UDM field. Else, if the `field.ID` value is not `empty` then, the `security_result.detection_fields.key` UDM field is set to `target_%{field.Type}` and the `field.ID` log field is mapped to the `security_result.detection_fields.value` UDM field. | `target.group.group_display_name` `target.user.email_addresses` `target.user.userid` `target.resource.name` `target.resource.attribute.labels` `security_result.detection_fields` `additional.fields`
Iterate for each element `field` with index `ind` in the `Target` log field array, then If the `Operation` log field value is equal to `Add group.` then, If the `field.Type` value is equal to `1` then, the `field.ID` log field is mapped to the `target.group.group_display_name` UDM field. Else, if the `field.Type` value is equal to `5` and the `field.ID` value is not `empty` then, If the `field.ID` value matches the regular expression pattern `(^.+@.+$)` and matches the regular expression pattern `(^.{0,256}$)` then, the `field.ID` log field is mapped to the `target.user.email_addresses` UDM field and the `field.ID` log field is mapped to the `target.user.userid` UDM field. Else, if the `field.ID` value matches the regular expression pattern `(^.{0,256}$)` then, the `field.ID` log field is mapped to the `target.user.userid` UDM field. Else, the `additional.fields.key` UDM field is set to `userid`, and the `field.ID` log field is mapped to the `additional.fields.value` UDM field. Else, if the `field.ID` value is not `empty` then, the `additional.fields.key` UDM field is set to `target_%{ind}_%{field.Type}` and the `field.ID` log field is mapped to the `additional.fields.value` UDM field. If the `Operation` log field value is equal to `Update device.` and the `field.Type` value is equal to `1` then, the `target.resource.attribute.labels.key` UDM field is set to `id` and the `field.ID` log field is mapped to the `target.resource.attribute.labels.value` UDM field. If the `Operation` log field value is one of the following: - `Delete group.` - `Update group.` and the `field.Type` value is equal to `1` then, the `field.ID` log field is mapped to the `target.group.group_display_name` UDM field. Else, if the `Operation` log field value is one of the following: - `Set federation settings on domain.` - `Set Company Information.` - `Consent to application.` - `Verify domain.` - `Delete device.` - `Add device.` and the `field.Type` value is equal to `1` then, the `field.ID` log field is mapped to the `target.resource.name` UDM field. Else, if the `field.Type` value is equal to `5` and the `field.ID` value is not `empty` then, If the `field.ID` value matches the regular expression pattern `(^.+@.+$)` and matches the regular expression pattern `(^.{0,256}$)` then, the `field.ID` log field is mapped to the `target.user.email_addresses` UDM field and the `field.ID` log field is mapped to the `target.user.userid` UDM field. Else, if the `field.ID` value matches the regular expression pattern `(^.{0,256}$)` then, the `field.ID` log field is mapped to the `target.user.userid` UDM field. Else, the `additional.fields.key` UDM field is set to `userid`, and the `field.ID` log field is mapped to the `additional.fields.value` UDM field. Else, if the `field.ID` value is not `empty` then, the `security_result.detection_fields.key` UDM field is set to `target_%{ind}_%{field.Type}` and the `field.ID` log field is mapped to the `security_result.detection_fields.value` UDM field. Else, the `additional.fields.key` UDM field is set to `Target` and the `Target` log field is mapped to the `additional.fields.value` UDM field. |
| `ModifiedProperties` | `security_result.summary`
Iterate for each element `field` in the `ModifiedProperties` log field array, then If the `field.Name` value is equal to `Included Updated Properties` then, the `field.NewValue` log field is mapped to the `security_result.summary` UDM field. | `additional.fields[Included Updated Properties]`
Iterate for each element `field` in the `ModifiedProperties` log field array, then If the `field.Name` value is equal to `Included Updated Properties` then, the `additional.fields.key` UDM field is set to `Included Updated Properties` and the `field.NewValue` log field is mapped to the `additional.fields.value` UDM field. |
| `ModifiedProperties` | `target.resource.name`
Iterate for each element `field` in the `ModifiedProperties` log field array, then If the `field.Name` value is equal to `Action Client Name` then, the `field.NewValue` log field is mapped to the `target.resource.name` UDM field. | `target.resource.attribute.labels[Action Client Name]`
Iterate for each element `field` in the `ModifiedProperties` log field array, then If the `field.Name` value is equal to `Action Client Name` then, the `target.resource.attribute.labels.key` UDM field is set to `Action Client Name` and the `field.NewValue` log field is mapped to the `target.resource.attribute.labels.value` UDM field. |
| `Parameters` | `target.administrative_domain`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `data.Value` log field is mapped to the `target.administrative_domain` UDM field. | `additional.fields[domain_controller]`
Iterate for each element `data` in the `Parameters` log field array, then If the `data.Name` value is equal to `DomainController` then, the `additional.fields.key` UDM field is set to `domain_controller` and the `data.Value` log field is mapped to the `additional.fields.value` UDM field. |
| `SharingInformation` | `about.user.user_display_name` `about.user.product_object_id` `about.user.email_addresses` `about.user.attribute.permissions.name`
Iterate for each element `info` in the `SharingInformation` log field array, then The `info.RecipientName` log field is mapped to the `about.user.user_display_name` UDM field. The `info.ObjectId` log field is mapped to the `about.user.product_object_id` UDM field. The `info.RecipientEmail` log field is mapped to the `about.user.email_addresses` UDM field. If the `info.ResharePermission` value is not `empty` then, the `info.ResharePermission` log field is mapped to the `about.user.attribute.permissions.name` UDM field. | `target.user.user_display_name` `target.user.product_object_id` `target.user.email_addresses` `target.user.attribute.permissions.name`
Iterate for each element `info` in the `SharingInformation` log field array, then The `info.RecipientName` log field is mapped to the `target.user.user_display_name` UDM field. The `info.ObjectId` log field is mapped to the `target.user.product_object_id` UDM field. The `info.RecipientEmail` log field is mapped to the `target.user.email_addresses` UDM field. If the `info.ResharePermission` value is not `empty` then, the `info.ResharePermission` log field is mapped to the `target.user.attribute.permissions.name` UDM field. |
| `Actor` | `security_result.detection_fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `security_result.detection_fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `security_result.detection_fields.value` UDM field. | `additional.fields`
Iterate for each element `actor` with index `ind` in the `Actor` log field array, then The `additional.fields.key` UDM field is set to `actor_%{ind}_%{actor.Type}` and the `actor.ID` log field is mapped to the `additional.fields.value` UDM field. |
| `ExchangeLocations` | `security_result.category_details`
If the `Operation` log field value is one of the following: - `ViewedSearchExported` - `SearchViewed` - `SearchUpdated` - `SearchStarted` - `SearchExportDownloaded` - `CaseAdded` - `SetRetentionCompliancePolicy` - `NewRetentionCompliancePolicy` - `CaseUpdated` - `CaseMemberUpdated` - `CaseViewed` - `SearchCreated` - `SearchReport` - `RemoveComplianceTag` - `RemoveRetentionCompliancePolicy` - `SetRetentionComplianceRule` - `CaseAdminUpdated` - `HoldUpdated` - `HoldCreated` - `HoldRemoved` - `SearchRemoved` - `Update-eDiscoveryCaseAdmin` - `NewRetentionComplianceRule` - `ApplicableAdaptiveScopeChange` - `NewComplianceTag` - `SetComplianceTag` - `CaseMemberAdded` - `CaseMemberRemoved` - `CaseAdminAdded` - `CaseAdminRemoved` - `SearchPermissionUpdated` - `SearchPermissionCreated` - `SearchPermissionRemoved` - `SearchStopped` - `ApplicableAdaptivePolicyChange` - `HoldViewed` - `ViewedSearchReport` - `NewAdaptiveScope` - `RemoveRetentionComplianceRule` - `RemovedSearchReport` - `CaseRemoved` then, the `ExchangeLocations` log field is mapped to the `security_result.category_details` UDM field. | `additional.fields[exchange_locations]`
If the `Workload` log field value is equal to `PowerBI` then, the `additional.fields.key` UDM field is set to `exchange_locations` and the `ExchangeLocations` log field is mapped to the `additional.fields.value` UDM field. |
| `PublicFolderLocations` | `security_result.category_details`
If the `Operation` log field value is one of the following: - `ViewedSearchExported` - `SearchViewed` - `SearchUpdated` - `SearchStarted` - `SearchExportDownloaded` - `CaseAdded` - `SetRetentionCompliancePolicy` - `NewRetentionCompliancePolicy` - `CaseUpdated` - `CaseMemberUpdated` - `CaseViewed` - `SearchCreated` - `SearchReport` - `RemoveComplianceTag` - `RemoveRetentionCompliancePolicy` - `SetRetentionComplianceRule` - `CaseAdminUpdated` - `HoldUpdated` - `HoldCreated` - `HoldRemoved` - `SearchRemoved` - `Update-eDiscoveryCaseAdmin` - `NewRetentionComplianceRule` - `ApplicableAdaptiveScopeChange` - `NewComplianceTag` - `SetComplianceTag` - `CaseMemberAdded` - `CaseMemberRemoved` - `CaseAdminAdded` - `CaseAdminRemoved` - `SearchPermissionUpdated` - `SearchPermissionCreated` - `SearchPermissionRemoved` - `SearchStopped` - `ApplicableAdaptivePolicyChange` - `HoldViewed` - `ViewedSearchReport` - `NewAdaptiveScope` - `RemoveRetentionComplianceRule` - `RemovedSearchReport` - `CaseRemoved` then, the `PublicFolderLocations` log field is mapped to the `security_result.category_details` UDM field. | `additional.fields[public_folder_locations]`
If the `Workload` log field value is equal to `PowerBI` then, the `additional.fields.key` UDM field is set to `public_folder_locations` and the `PublicFolderLocations` log field is mapped to the `additional.fields.value` UDM field. |
| `SharepointLocations` | `security_result.category_details`
If the `Operation` log field value is one of the following: - `ViewedSearchExported` - `SearchViewed` - `SearchUpdated` - `SearchStarted` - `SearchExportDownloaded` - `CaseAdded` - `SetRetentionCompliancePolicy` - `NewRetentionCompliancePolicy` - `CaseUpdated` - `CaseMemberUpdated` - `CaseViewed` - `SearchCreated` - `SearchReport` - `RemoveComplianceTag` - `RemoveRetentionCompliancePolicy` - `SetRetentionComplianceRule` - `CaseAdminUpdated` - `HoldUpdated` - `HoldCreated` - `HoldRemoved` - `SearchRemoved` - `Update-eDiscoveryCaseAdmin` - `NewRetentionComplianceRule` - `ApplicableAdaptiveScopeChange` - `NewComplianceTag` - `SetComplianceTag` - `CaseMemberAdded` - `CaseMemberRemoved` - `CaseAdminAdded` - `CaseAdminRemoved` - `SearchPermissionUpdated` - `SearchPermissionCreated` - `SearchPermissionRemoved` - `SearchStopped` - `ApplicableAdaptivePolicyChange` - `HoldViewed` - `ViewedSearchReport` - `NewAdaptiveScope` - `RemoveRetentionComplianceRule` - `RemovedSearchReport` - `CaseRemoved` then, the `SharepointLocations` log field is mapped to the `security_result.category_details` UDM field. | `additional.fields[sharepoint_locations]`
If the `Workload` log field value is equal to `PowerBI` then, the `additional.fields.key` UDM field is set to `sharepoint_locations` and the `SharepointLocations` log field is mapped to the `additional.fields.value` UDM field. |
| `Query` | `security_result.description`
If the `Operation` log field value is one of the following: - `ViewedSearchExported` - `SearchViewed` - `SearchUpdated` - `SearchStarted` - `SearchExportDownloaded` - `CaseAdded` - `SetRetentionCompliancePolicy` - `NewRetentionCompliancePolicy` - `CaseUpdated` - `CaseMemberUpdated` - `CaseViewed` - `SearchCreated` - `SearchReport` - `RemoveComplianceTag` - `RemoveRetentionCompliancePolicy` - `SetRetentionComplianceRule` - `CaseAdminUpdated` - `HoldUpdated` - `HoldCreated` - `HoldRemoved` - `SearchRemoved` - `Update-eDiscoveryCaseAdmin` - `NewRetentionComplianceRule` - `ApplicableAdaptiveScopeChange` - `NewComplianceTag` - `SetComplianceTag` - `CaseMemberAdded` - `CaseMemberRemoved` - `CaseAdminAdded` - `CaseAdminRemoved` - `SearchPermissionUpdated` - `SearchPermissionCreated` - `SearchPermissionRemoved` - `SearchStopped` - `ApplicableAdaptivePolicyChange` - `HoldViewed` - `ViewedSearchReport` - `NewAdaptiveScope` - `RemoveRetentionComplianceRule` - `RemovedSearchReport` - `CaseRemoved` then, the `Query` log field is mapped to the `security_result.description` UDM field. | `additional.fields[Query]`
If the `Workload` log field value is equal to `PowerBI` then, the `additional.fields.key` UDM field is set to `query` and the `Query` log field is mapped to the `additional.fields.value` UDM field. |
| `MachineId` | `target.asset.product_object_id` | `principal.asset.product_object_id`
If the `Operation` log field value is one of the following: - `FileSyncUploadedFull` - `FileSyncUploadedPartial` - `ManagedSyncClientAllowed` - `UnmanagedSyncClientBlocked` then, the `MachineId` log field is mapped to the `principal.asset.product_object_id` UDM field. |
| `DeviceName` | `target.hostname` | `principal.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.hostname` UDM field. |
| `DeviceName` | `target.asset.hostname` | `principal.asset.hostname`
If the `Operation` log field value is equal to `SensitivityLabelUpdated` or the `Workload` log field value is one of the following: - `Endpoint` - `ThreatIntelligence` then, the `DeviceName` log field is mapped to the `principal.asset.hostname` UDM field. |
| `ActivityId` | `about.labels[ActivityId]` `additional.fields[ActivityId]` | `metadata.product_log_id`
If the `Workload` log field value is equal to `Activity` then, the `ActivityId` log field is mapped to the `metadata.product_log_id` UDM field. |
| `AffectedItems.Attachments` | `about.file.full_path` `about.file.size` | `about.file.names` `target.file.names`
If the `Operation` log field value is one of the following: - `Move` - `MoveToDeletedItems` then, the `AffectedItems.Attachments` log field is mapped to the `about.file.names` UDM field. Else, if the `Operation` log field value is one of the following: - `SoftDelete` - `HardDelete` then, the `AffectedItems.Attachments` log field is mapped to the `target.file.names` UDM field. |
| `Case` | `metadata.description` | `about.resource.product_object_id`
If the `Workload` log field value is equal to `SecurityComplianceCenter` then, the `Case` log field is mapped to the `about.resource.product_object_id` UDM field. |
| `MessageURLs` | `target.resource.attribute.labels`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `target.resource.attribute.labels.key` UDM field is set to `Url_%{index}` and the `url` log field is mapped to the `target.resource.attribute.labels.value` UDM field. | `about.url`
Iterate for each element `url` with index `index` in the `MessageURLs` log field array, then The `url` log field is mapped to the `about.url` UDM field. |
| `LogonType` | `extensions.auth.mechanism`
If the `LogonType` log field value is not `empty` then, If the `LogonType` log field value is equal to `2` then, the `extensions.auth.mechanism` UDM field is set to `INTERACTIVE`. Else, if the `LogonType` log field value is equal to `3` or the `LogonType` log field value is equal to `8` then, the `extensions.auth.mechanism` UDM field is set to `NETWORK`. Else, if the `LogonType` log field value is equal to `4` then, the `extensions.auth.mechanism` UDM field is set to `BATCH`. Else, if the `LogonType` log field value is equal to `5` then, the `extensions.auth.mechanism` UDM field is set to `SERVICE`. Else, if the `LogonType` log field value is equal to `7` then, the `extensions.auth.mechanism` UDM field is set to `UNLOCK`. Else, if the `LogonType` log field value is equal to `9` then, the `extensions.auth.mechanism` UDM field is set to `NEW_CREDENTIALS`. Else, if the `LogonType` log field value is equal to `10` then, the `extensions.auth.mechanism` UDM field is set to `REMOTE_INTERACTIVE`. Else, if the `LogonType` log field value is equal to `11` then, the `extensions.auth.mechanism` UDM field is set to `CACHED_INTERACTIVE`. Else, the `extensions.auth.mechanism` UDM field is set to `MECHANISM_UNSPECIFIED`. | `principal.user.attribute.labels[logon_type]`
If the `LogonType` log field value is not `empty` then, the `principal.user.attribute.labels.key` UDM field is set to `logon_type` and If the `LogonType` log field value is equal to `0` then, the `principal.user.attribute.labels.value` UDM field is set to `Owner`. Else, if the `LogonType` log field value is equal to `1` then, the `principal.user.attribute.labels.value` UDM field is set to `Admin`. Else, if the `LogonType` log field value is equal to `2` then, the `principal.user.attribute.labels.value` UDM field is set to `Delegated`. Else, if the `LogonType` log field value is equal to `3` then, the `principal.user.attribute.labels.value` UDM field is set to `Transport`. Else, if the `LogonType` log field value is equal to `4` then, the `principal.user.attribute.labels.value` UDM field is set to `SystemService`. Else, if the `LogonType` log field value is equal to `5` then, the `principal.user.attribute.labels.value` UDM field is set to `BestAccess`. Else, if the `LogonType` log field value is equal to `6` then, the `principal.user.attribute.labels.value` UDM field is set to `DelegatedAdmin`. |
| `P1Sender` | `principal.user.email_addresses` | `network.email.reply_to` `network.smtp.mail_from`
If the `Operation` log field value is one of the following: - `UserSubmission` - `UserSubmissionTriage` - `AirInvestigationData` then, the `P1Sender` log field is mapped to the `network.smtp.mail_from` UDM field. Else, the `P1Sender` log field is mapped to the `network.email.reply_to` UDM field. |
| `Workload` | `target.application`
`intermediary.application`
If the log fields `Workload` is not `empty`, then the log field `Workload` is mapped to the `intermediary.application` UDM field. | `target.application`
`additional.fields[workload]`
If the log fields `EventSource` and `Workload` are not `empty` and equal, then the log field `EventSource` is mapped to the `target.application` UDM field.
Else If, the log fields `EventSource` and `Workload` are not `empty` and not equal, then the log field `EventSource` is mapped to the `target.application` UDM field and the `Workload` field is mapped to `additional.fields.value` UDM field and the `additional.fields.key` UDM field is set to `workload`.
Else If, the log field `EventSource` is not `empty`, then the log field `EventSource` is mapped to the `target.application` UDM field.
Else If, the log field `Workload` is not `empty`, then the log field `Workload` is mapped to the `target.application` UDM field. |
| `AlertCategory` | `additional.fields[AlertCategory]` | `security_result.category_details` |
| `AlertDescription` | `additional.fields[AlertDescription]` | `security_result.summary` |
| `Justification` | `principal.user.attribute.labels[justification]` | `security_result.detection_fields[justification]` |
| `Applications.0.Name` | `target.application`. | `additional.fields[ApplicationsName]` |
| `AggregatedWorkspaceInformation.WorkspaceCount` | `target.labels[workspace_count]` `additional.fields[workspace_count]` | `additional.fields[workspace_count]` |
| `AggregatedWorkspaceInformation.WorkspacesByCapacitySku` | `target.labels[workspaces_by_capacity_sku]` `additional.fields[workspaces_by_capacity_sku]` | `additional.fields[workspaces_by_capacity_sku]` |
| `AggregatedWorkspaceInformation.WorkspacesByType` | `target.labels[workspaces_type]` `additional.fields[workspaces_type]` | `additional.fields[workspaces_type]` |
| `SensitivityLabelEventData.ActionSource` | `principal.labels[SensitivityLabelEventData_ActionSource]` `additional.fields[SensitivityLabelEventData_ActionSource]` | `additional.fields[SensitivityLabelEventData_ActionSource]` |
| `SensitivityLabelEventData.LabelEventType` | `target.labels[SensitivityLabelEventData_LabelEventType]` `additional.fields[SensitivityLabelEventData_LabelEventType]` | `additional.fields[SensitivityLabelEventData_LabelEventType]` |
| `EvidenceFile.FullUrl` | `target.labels[evidence_file_full_url]` `additional.fields[evidence_file_full_url]` | `additional.fields[evidence_file_full_url]` |
| `PropertyBag.AssessmentStatusPerInitiative.ArnEventId` | `about.labels[ArnEventId]` `additional.fields[ArnEventId]` | `additional.fields[ArnEventId]` |
| `PropertyBag.AssessmentStatusPerInitiative.CloudProvider` | `about.labels[Cloud_provider]` `additional.fields[Cloud_provider]` | `additional.fields[Cloud_provider]` |
| `PropertyBag.AssessmentStatusPerInitiative.EventType` | `about.labels[EventType]` `additional.fields[EventType]` | `additional.fields[EventType]` |
| `PropertyBag.AssessmentStatusPerInitiative.PolicyInitiativeId` | `about.labels[PolicyInitiativeId]` `additional.fields[PolicyInitiativeId]` | `additional.fields[PolicyInitiativeId]` |
| `PropertyBag.AssessmentStatusPerInitiative.PolicyInitiativeName` | `about.labels[PolicyInitiativeName]` `additional.fields[PolicyInitiativeName]` | `additional.fields[PolicyInitiativeName]` |
| `PropertyBag.AssessmentStatusPerInitiative.SecurityAssessmentId` | `about.labels[SecurityAssessmentId]` `additional.fields[SecurityAssessmentId]` | `additional.fields[SecurityAssessmentId]` |
| `PropertyBag.AssessmentStatusPerInitiative.StatusChangeDate` | `about.labels[StatusChangeDate]` `additional.fields[StatusChangeDate]` | `additional.fields[StatusChangeDate]` |
| `PropertyBag.AssessmentStatusPerInitiative.StatusCode` | `about.labels[StatusCode]` `additional.fields[StatusCode]` | `additional.fields[StatusCode]` |
| `PropertyBag.AssessmentStatusPerInitiative.StatusFirstEvaluationDate` | `about.labels[StatusFirstEvaluationDate]` `additional.fields[StatusFirstEvaluationDate]` | `additional.fields[StatusFirstEvaluationDate]` |
| `PropertyBag.AssessmentStatusPerInitiative.SubscriptionId` | `about.labels[SubscriptionId]` `additional.fields[SubscriptionId]` | `additional.fields[SubscriptionId]` |
| `PropertyBag.AssessmentStatusPerInitiative.SubscriptionName` | `about.labels[SubscriptionName]` `additional.fields[SubscriptionName]` | `additional.fields[SubscriptionName]` |
| `PropertyBag.DataType` | `about.labels[PropertyBag Datatype]` `additional.fields[PropertyBag Datatype]` | `additional.fields[PropertyBag Datatype]` |
| `PropertyBag.Policy.ArnEventId` | `about.labels[policy_arn_event_id]` `additional.fields[policy_arn_event_id]` | `additional.fields[policy_arn_event_id]` |
| `PropertyBag.Policy.Description` | `about.labels[policy_description]` `additional.fields[policy_description]` | `additional.fields[policy_description]` |
| `PropertyBag.Policy.DetailsLink` | `about.labels[policy_details_link]` `additional.fields[policy_details_link]` | `additional.fields[policy_details_link]` |
| `PropertyBag.Policy.EventTime` | `about.labels[policy_event_time]` `additional.fields[policy_event_time]` | `additional.fields[policy_event_time]` |
| `PropertyBag.Policy.EventType` | `about.labels[policy_event_type]` `additional.fields[policy_event_type]` | `additional.fields[policy_event_type]` |
| `PropertyBag.Policy.PolicyInitiativeId` | `about.labels[policy_initiative_id]` `additional.fields[policy_initiative_id]` | `additional.fields[policy_initiative_id]` |
| `PropertyBag.Policy.PolicyInitiativeName` | `about.labels[policy_initiative_name]` `additional.fields[policy_initiative_name]` | `additional.fields[policy_initiative_name]` |
| `AdditionalInfo.environmentName` | `target.labels[environment_name]` `additional.fields[environment_name]` | `additional.fields[environment_name]` |
| `DataflowAccessTokenRequestParameters.entityName` | `principal.labels[Entity_name]` `additional.fields[Entity_name]` | `additional.fields[Entity_name]` |
| `DataflowAccessTokenRequestParameters.partitionUri` | `principal.labels[Partition URI]` `additional.fields[Partition URI]` | `additional.fields[Partition URI]` |
| `DataflowAccessTokenRequestParameters.permissions` | `principal.labels[Token Permission]` `additional.fields[Token Permission]` | `additional.fields[Token Permission]` |
| `DataflowAccessTokenRequestParameters.tokenLifetimeInMinutes` | `principal.labels[TokenLifetimeInMinutes]` `additional.fields[TokenLifetimeInMinutes]` | `additional.fields[TokenLifetimeInMinutes]` |
| `ModifiedProperties` | `target.labels[Expire date]` `additional.fields[Expire date]` | `additional.fields[Expire date]` |
| `ModifiedProperties` | `target.labels[%{field.Name}]` `additional.fields[%{field.Name}]` | `additional.fields[%{field.Name}]` |
| `ItemName` | `target.labels[ItemName]` `additional.fields[ItemName]` | `additional.fields[ItemName]` |
| `UserId` | `principal.labels[userid]` `additional.fields[userid]` | `additional.fields[userid]` |
| `ObjectId` | `target.labels[userid]` `additional.fields[userid]` | `additional.fields[userid]` |
| `Platform` | `target.labels[Platform]` `additional.fields[Platform]` | `additional.fields[Platform]` |
| `ContentType` | `target.labels[content_type]` `additional.fields[content_type]` | `additional.fields[content_type]` |
| `ActionSource` | `principal.labels[ActionSource]` `additional.fields[ActionSource]` | `additional.fields[ActionSource]` |
| `ActionSourceDetail` | `principal.labels[ActionSourceDetail]` `additional.fields[ActionSourceDetail]` | `additional.fields[ActionSourceDetail]` |
| `ClientRequestId` | `principal.labels[ClientRequestId]` `additional.fields[ClientRequestId]` | `additional.fields[ClientRequestId]` |
| `UserServicePlan` | `principal.labels[UserServicePlan]` `additional.fields[UserServicePlan]` | `additional.fields[UserServicePlan]` |
| `EntityId` | `principal.labels[EntityId]` `additional.fields[EntityId]` | `additional.fields[EntityId]` |
| `LabelAppliedDateTime` | `principal.labels[LabelAppliedDateTime]` `additional.fields[LabelAppliedDateTime]` | `additional.fields[LabelAppliedDateTime]` |
| `Activity` | `principal.labels[activity]` `additional.fields[activity]` | `additional.fields[activity]` |
| `ActivityId` | `principal.labels[ActivityId]` `additional.fields[ActivityId]` | `additional.fields[ActivityId]` |
| `SourceName` | `principal.labels[SourceName]` `additional.fields[SourceName]` | `additional.fields[SourceName]` |
| `ClientApplicationId` | `principal.labels[ClientApplicationId]` `additional.fields[ClientApplicationId]` | `additional.fields[ClientApplicationId]` |
| `EntityName` | `principal.labels[EntityName]` `additional.fields[EntityName]` | `additional.fields[EntityName]` |
| `ActorYammerUserId` | `principal.labels[ActorYammerUserId]` `additional.fields[ActorYammerUserId]` | `additional.fields[ActorYammerUserId]` |
| `ItemUrl` | `principal.labels[ItemUrl]` `additional.fields[ItemUrl]` | `additional.fields[ItemUrl]` |
| `SystemUserId` | `principal.labels[SystemUserId]` `additional.fields[SystemUserId]` | `additional.fields[SystemUserId]` |
| `YammerNetworkId` | `principal.labels[YammerNetworkId]` `additional.fields[YammerNetworkId]` | `additional.fields[YammerNetworkId]` |
| `AlertLinks` | `principal.labels[AlertLinks]` `additional.fields[AlertLinks]` | `additional.fields[AlertLinks]` |
| `ServiceContextId` | `principal.labels[ServiceContextId]` `additional.fields[ServiceContextId]` | `additional.fields[ServiceContextId]` |
| `SourceLocationType` | `principal.labels[SourceLocationType]` `additional.fields[SourceLocationType]` | `additional.fields[SourceLocationType]` |
| `AddOnType` | `target.labels[AddOnType]` `additional.fields[AddOnType]` | `additional.fields[AddOnType]` |
| `LabelEventType` | `target.labels[LabelEventType]` `additional.fields[LabelEventType]` | `additional.fields[LabelEventType]` |
| `AadAppId` | `target.labels[AadAppId]` `additional.fields[AadAppId]` | `additional.fields[AadAppId]` |
| `MailboxGuid` | `target.labels[MailboxGuid]` `additional.fields[MailboxGuid]` | `additional.fields[MailboxGuid]` |
| `ConsumptionMethod` | `target.labels[ConsumptionMethod]` `additional.fields[ConsumptionMethod]` | `additional.fields[ConsumptionMethod]` |
| `UserSharedWith` | `target.labels[UserSharedWith]` `additional.fields[UserSharedWith]` | `additional.fields[UserSharedWith]` |
| `RefreshType` | `target.labels[RefreshType]` `additional.fields[RefreshType]` | `additional.fields[RefreshType]` |
| `AppName` | `target.labels[AppName]` `additional.fields[AppName]` | `additional.fields[AppName]` |
| `SharingType` | `target.labels[SharingType]` `additional.fields[SharingType]` | `additional.fields[SharingType]` |
| `MailboxOwnerMasterAccountSid` | `target.labels[MailboxOwnerMasterAccountSid]` `additional.fields[MailboxOwnerMasterAccountSid]` | `additional.fields[MailboxOwnerMasterAccountSid]` |
| `PolicyId` | `target.labels[PolicyId]` `additional.fields[PolicyId]` | `additional.fields[PolicyId]` |
| `DataType` | `target.labels[DataType]` `additional.fields[DataType]` | `additional.fields[DataType]` |
| `DeploymentPipelineId` | `target.labels[DeploymentPipelineId]` `additional.fields[DeploymentPipelineId]` | `additional.fields[DeploymentPipelineId]` |
| `DeploymentPipelineStageOrder` | `target.labels[DeploymentPipelineStageOrder]` `additional.fields[DeploymentPipelineStageOrder]` | `additional.fields[DeploymentPipelineStageOrder]` |
| `ResultCount` | `target.labels[ResultCount]` `additional.fields[ResultCount]` | `additional.fields[ResultCount]` |
| `TargetContextId` | `target.labels[TargetContextId]` `additional.fields[TargetContextId]` | `additional.fields[TargetContextId]` |
| `ClientAppId` | `target.labels[ClientAppId]` `additional.fields[ClientAppId]` | `additional.fields[ClientAppId]` |
| `DataflowRefreshScheduleType` | `target.labels[DataflowRefreshScheduleType]` `additional.fields[DataflowRefreshScheduleType]` | `additional.fields[DataflowRefreshScheduleType]` |
| `DataClassification` | `target.labels[DataClassification]` `additional.fields[DataClassification]` | `additional.fields[DataClassification]` |
| `Schedules.RefreshFrequency` | `target.labels[RefreshFrequency]` `additional.fields[RefreshFrequency]` | `additional.fields[RefreshFrequency]` |
| `Schedules.TimeZone` | `target.labels[TimeZone]` `additional.fields[TimeZone]` | `additional.fields[TimeZone]` |
| `Schedules.Days` | `target.labels[Days]` `additional.fields[Days]` | `additional.fields[Days]` |
| `Schedules.Time` | `target.labels[Time]` `additional.fields[Time]` | `additional.fields[Time]` |
| `SubscriptionSchedule.Type` | `target.labels[Type]` `additional.fields[Type]` | `additional.fields[Type]` |
| `SubscriptionSchedule.WeekDays` | `target.labels[WeekDays]` `additional.fields[WeekDays]` | `additional.fields[WeekDays]` |
| `SubscriptionSchedule.StartDate` | `target.labels[StartDate]` `additional.fields[StartDate]` | `additional.fields[StartDate]` |
| `SubscriptionSchedule.EndDate` | `target.labels[EndDate]` `additional.fields[EndDate]` | `additional.fields[EndDate]` |
| `SubscriptionSchedule.TimeZone` | `target.labels[TimeZone]` `additional.fields[TimeZone]` | `additional.fields[TimeZone]` |
| `ChannelGuid` | `target.labels[ChannelGuid]` `additional.fields[ChannelGuid]` | `additional.fields[ChannelGuid]` |
| `TabType` | `target.labels[TabType]` `additional.fields[TabType]` | `additional.fields[TabType]` |
| `ChannelName` | `target.labels[ChannelName]` `additional.fields[ChannelName]` | `additional.fields[ChannelName]` |
| `AddOnGuid` | `target.labels[AddOnGuid]` `additional.fields[AddOnGuid]` | `additional.fields[AddOnGuid]` |
| `ChannelType` | `target.labels[ChannelType]` `additional.fields[ChannelType]` | `additional.fields[ChannelType]` |
| `AddOnName` | `target.labels[AddOnName]` `additional.fields[AddOnName]` | `additional.fields[AddOnName]` |
| `AADGroupId` | `target.labels[AADGroupId]` `additional.fields[AADGroupId]` | `additional.fields[AADGroupId]` |
| `Site` | `target.labels[Site]` `additional.fields[Site]` | `additional.fields[Site]` |
| `UniqueSharingId` | `target.labels[UniqueSharingId]` `additional.fields[UniqueSharingId]` | `additional.fields[UniqueSharingId]` |
| `ListIcon` | `target.labels[ListIcon]` `additional.fields[ListIcon]` | `additional.fields[ListIcon]` |
| `ListColor` | `target.labels[ListColor]` `additional.fields[ListColor]` | `additional.fields[ListColor]` |
| `ItemCount` | `target.labels[ItemCount]` `additional.fields[ItemCount]` | `additional.fields[ItemCount]` |
| `ListBaseTemplateType` | `target.labels[ListBaseTemplateType]` `additional.fields[ListBaseTemplateType]` | `additional.fields[ListBaseTemplateType]` |
| `ListBaseType` | `target.labels[ListBaseType]` `additional.fields[ListBaseType]` | `additional.fields[ListBaseType]` |
| `FormsUserType` | `target.labels[FormsUserType]` `additional.fields[FormsUserType]` | `additional.fields[FormsUserType]` |
| `FormsUserTypes` | `target.labels[FormsUserTypes]` `additional.fields[FormsUserTypes]` | `additional.fields[FormsUserTypes]` |
| `DestinationLocationType` | `target.labels[DestinationLocationType]` `additional.fields[DestinationLocationType]` | `additional.fields[DestinationLocationType]` |
| `SourceLabel` | `src.labels[SourceLabel]` `additional.fields[SourceLabel]` | `additional.fields[SourceLabel]` |
| `DestinationLabel` | `target.labels[DestinationLabel]` `additional.fields[DestinationLabel]` | `additional.fields[DestinationLabel]` |
| `ArtifactType` | `about.labels[ArtifactType]` `additional.fields[ArtifactType]` | `additional.fields[ArtifactType]` |
| `LastRefreshTime` | `about.labels[LastRefreshTime]` `additional.fields[LastRefreshTime]` | `additional.fields[LastRefreshTime]` |
| `Comments` | `about.labels[Comments]` `additional.fields[Comments]` | `additional.fields[Comments]` |
| `CapacityName` | `about.labels[CapacityName]` `additional.fields[CapacityName]` | `additional.fields[CapacityName]` |
| `Connectors` | `about.labels[Connectors]` `additional.fields[Connectors]` | `additional.fields[Connectors]` |
| `ShareLinkId` | `about.labels[ShareLinkId]` `additional.fields[ShareLinkId]` | `additional.fields[ShareLinkId]` |
| `CapacityUsers` | `about.labels[CapacityUsers]` `additional.fields[CapacityUsers]` | `additional.fields[CapacityUsers]` |
| `ExceptionInfo` | `about.labels[ExceptionInfo]` `additional.fields[ExceptionInfo]` | `additional.fields[ExceptionInfo]` |
| `SwitchState` | `about.labels[SwitchState]` `additional.fields[SwitchState]` | `additional.fields[SwitchState]` |
| `OnBehalfOfResId` | `about.labels[OnBehalfOfResId]` `additional.fields[OnBehalfOfResId]` | `additional.fields[OnBehalfOfResId]` |
| `Data` | `about.labels[Data]` `additional.fields[Data]` | `additional.fields[Data]` |
| `DistributionMethod` | `about.labels[DistributionMethod]` `additional.fields[DistributionMethod]` | `additional.fields[DistributionMethod]` |
| `ListTitle` | `about.labels[ListTitle]` `additional.fields[ListTitle]` | `additional.fields[ListTitle]` |
| `CommentId` | `about.labels[CommentId]` `additional.fields[CommentId]` | `additional.fields[CommentId]` |
| `LatestDeliveryLocation` | `about.labels[LatestDeliveryLocation]` `additional.fields[LatestDeliveryLocation]` | `additional.fields[LatestDeliveryLocation]` |
| `ThreatsAndDetectionTech` | `about.labels[ThreatsAndDetectionTech]` `additional.fields[ThreatsAndDetectionTech]` | `additional.fields[ThreatsAndDetectionTech]` |
| `SecurityComplianceCenterEventType` | `about.labels[SecurityComplianceCenterEventType]` `additional.fields[SecurityComplianceCenterEventType]` | `additional.fields[SecurityComplianceCenterEventType]` |
| `SharingAction` | `about.labels[SharingAction]` `additional.fields[SharingAction]` | `additional.fields[SharingAction]` |
| `ResultCountSecurityComplianceCenterEventType` | `about.labels[ResultCountSecurityComplianceCenterEventType]` `additional.fields[ResultCountSecurityComplianceCenterEventType]` | `additional.fields[ResultCountSecurityComplianceCenterEventType]` |
| `OriginalDeliveryLocation` | `about.labels[OriginalDeliveryLocation]` `additional.fields[OriginalDeliveryLocation]` | `additional.fields[OriginalDeliveryLocation]` |
| `ThreadID` | `about.labels[ThreadID]` `additional.fields[ThreadID]` | `additional.fields[ThreadID]` |
| `AssertingApplicationId` | `about.labels[AssertingApplicationId]` `additional.fields[AssertingApplicationId]` | `additional.fields[AssertingApplicationId]` |
| `SkypeForBusinessEventType` | `about.labels[SkypeForBusinessEventType]` `additional.fields[SkypeForBusinessEventType]` | `additional.fields[SkypeForBusinessEventType]` |
| `NetworkMessageId` | `about.labels[NetworkMessageId]` `additional.fields[NetworkMessageId]` | `additional.fields[NetworkMessageId]` |
| `SupportTicketId` | `about.labels[SupportTicketId]` `additional.fields[SupportTicketId]` | `additional.fields[SupportTicketId]` |
| `TemplateAppFolderObjectId` | `about.labels[TemplateAppFolderObjectId]` `additional.fields[TemplateAppFolderObjectId]` | `additional.fields[TemplateAppFolderObjectId]` |
| `RequestId` | `about.labels[RequestId]` `additional.fields[RequestId]` | `additional.fields[RequestId]` |
| `WebId` | `about.labels[WebId]` `additional.fields[WebId]` | `additional.fields[WebId]` |
| `ApplicationMode` | `about.labels[ApplicationMode]` `additional.fields[ApplicationMode]` | `additional.fields[ApplicationMode]` |
| `ServiceContextIdType` | `about.labels[ServiceContextIdType]` `additional.fields[ServiceContextIdType]` | `additional.fields[ServiceContextIdType]` |
| `IncidentId` | `about.labels[IncidentId]` `additional.fields[IncidentId]` | `additional.fields[IncidentId]` |
| `DeliveryAction` | `about.labels[DeliveryAction]` `additional.fields[DeliveryAction]` | `additional.fields[DeliveryAction]` |
| `PrimaryFieldValue` | `about.labels[PrimaryFieldValue]` `additional.fields[PrimaryFieldValue]` | `additional.fields[PrimaryFieldValue]` |
| `VersionId` | `about.labels[VersionId]` `additional.fields[VersionId]` | `additional.fields[VersionId]` |
| `PhishConfidenceLevel` | `about.labels[PhishConfidenceLevel]` `additional.fields[PhishConfidenceLevel]` | `additional.fields[PhishConfidenceLevel]` |
| `QueryResults` | `about.labels[QueryResults]` `additional.fields[QueryResults]` | `additional.fields[QueryResults]` |
| `InternalLogonType` | `about.labels[InternalLogonType]` `additional.fields[InternalLogonType]` | `additional.fields[InternalLogonType]` |
| `ModifiedObjectResolvedName` | `about.labels[ModifiedObjectResolvedName]` `additional.fields[ModifiedObjectResolvedName]` | `additional.fields[ModifiedObjectResolvedName]` |
| `CapacityId` | `about.labels[CapacityId]` `additional.fields[CapacityId]` | `additional.fields[CapacityId]` |
| `AzureADAppId` | `about.labels[AzureADAppId]` `additional.fields[AzureADAppId]` | `additional.fields[AzureADAppId]` |
| `CommunicationType` | `about.labels[CommunicationType]` `additional.fields[CommunicationType]` | `additional.fields[CommunicationType]` |
| `AppDistributionMode` | `about.labels[AppDistributionMode]` `additional.fields[AppDistributionMode]` | `additional.fields[AppDistributionMode]` |
| `SendAsUserMailboxGuid` | `about.labels[SendAsUserMailboxGuid]` `additional.fields[SendAsUserMailboxGuid]` | `additional.fields[SendAsUserMailboxGuid]` |
| `TemplateTypeId` | `about.labels[TemplateTypeId]` `additional.fields[TemplateTypeId]` | `additional.fields[TemplateTypeId]` |
| `Attachment.Id` | `about.labels[AttachmentId]` `additional.fields[AttachmentId]` | `additional.fields[AttachmentId]` |
| `HighPriorityMediaProcessing` | `about.labels[HighPriorityMediaProcessing]` `additional.fields[HighPriorityMediaProcessing]` | `additional.fields[HighPriorityMediaProcessing]` |
| `AuthenticationType` | `principal.labels[AuthenticationType]` `additional.fields[AuthenticationType]` | `additional.fields[AuthenticationType]` |
| `BrowserName` | `principal.labels[browser_name]` `additional.fields[browser_name]` | `additional.fields[browser_name]` |
| `BrowserVersion` | `principal.labels[browser_version]` `additional.fields[browser_version]` | `additional.fields[browser_version]` |
| `DeviceDisplayName` | `principal.labels[device_display_name]` `additional.fields[device_display_name]` | `additional.fields[device_display_name]` |
| `IsManagedDevice` | `principal.labels[is_managed_device]` `additional.fields[is_managed_device]` | `additional.fields[is_managed_device]` |
| `OperationProperties` | `about.labels[%{field.Name}_%{index}]` `additional.fields[%{field.Name}_%{index}]` | `additional.fields[%{field.Name}_%{index}]` |
| `OperationProperties` | `about.labels[%{field.Name}]` `additional.fields[%{field.Name}]` | `additional.fields[%{field.Name}]` |
| `AdditionalActionsAndResults` | `about.labels[AdditionalActionsAndResults]` `additional.fields[AdditionalActionsAndResults]` | `additional.fields[AdditionalActionsAndResults]` |
| `ExchangeMetaData.RecipientCount` | `about.labels[ExchangeMetaData_RecipientCount]` `additional.fields[ExchangeMetaData_RecipientCount]` | `additional.fields[ExchangeMetaData_RecipientCount]` |
| `ExchangeMetaData.Sent` | `about.labels[ExchangeMetaData_Sent]` `additional.fields[ExchangeMetaData_Sent]` | `additional.fields[ExchangeMetaData_Sent]` |
| `UserKey` | `target.labels[user_key]` `additional.fields[user_key]` | `additional.fields[user_key]` |
| `ActivityStartTime` | `about.labels[activity_start_time]` `additional.fields[activity_start_time]` | `additional.fields[activity_start_time]` |
| `AssignedTo` | `about.labels[assign_to]` `additional.fields[assign_to]` | `additional.fields[assign_to]` |
| `OperationCount` | `about.labels[OperationCount]` `additional.fields[OperationCount]` | `additional.fields[OperationCount]` |
| `OperationScope` | `about.labels[OperationScope]` `additional.fields[OperationScope]` | `additional.fields[OperationScope]` |
### Operation Specific fields Mapping Delta
The following table lists the operation specific log fields delta between old UDM mapping of `OFFICE_365` and new UDM mapping of `OFFICE_365`.
| Operation | Log Field | Old UDM Field | New UDM Field |
|---|---|---|---|
| `FileCopied` | `EventData` | `src.file.full_path` | `src.url` If the `EventData` log field is not `empty`, the extracted `src_url` field from `EventData` is mapped to the `src.url` UDM field. |
| `FileCopied` | `EventData` | `target.file.full_path` | `target.url` If the `EventData` log field is not `empty`, the extracted `target_url` field from `EventData` is mapped to the `target.url` UDM field. |
| `FileMoved` | `EventData` | `src.file.full_path` | `src.url` If the `EventData` log field is not `empty`, the extracted `src_url` field from `EventData` is mapped to the `src.url` UDM field. |
| `FileMoved` | `EventData` | `target.file.full_path` | `target.url` If the `EventData` log field is not `empty`, the extracted `target_url` field from `EventData` is mapped to the `target.url` UDM field. |
| `FolderMoved` | `EventData` | `src.file.full_path` | `src.url` If the `EventData` log field is not `empty`, the extracted `src_url` field from `EventData` is mapped to the `src.url` UDM field. |
| `FolderMoved` | `EventData` | `target.file.full_path` | `target.url` If the `EventData` log field is not `empty`, the extracted `target_url` field from `EventData` is mapped to the `target.url` UDM field. |
| `FolderCopied` | `EventData` | `src.file.full_path` | `src.url` If the `EventData` log field is not `empty`, the extracted `src_url` field from `EventData` is mapped to the `src.url` UDM field. |
| `FolderCopied` | `EventData` | `target.file.full_path` | `target.url` If the `EventData` log field is not `empty`, the extracted `target_url` field from `EventData` is mapped to the `target.url` UDM field. |
| `FileDownloaded` | `ObjectId` | `src.url` | `target.url` If the `ObjectId` log field is not `empty` and not equal to `Not Available`, the `ObjectId` log field is mapped to the `target.url` UDM field. |
| `FileDownloaded` | `SourceFileExtension` | `src.file.mime_type`\< | `target.file.mime_type` The `SourceFileExtension` log field is mapped to the `target.file.mime_type` UDM field. |
| `FileDownloaded` | `SourceFileName` | `src.file.full_path` | `target.file.full_path` The value of `%{SourceRelativeUrl}/%{SourceFileName}` is mapped to the `target.file.full_path` UDM field. |
| `FileDownloaded` | `SourceRelativeUrl` | `src.file.full_path` | `target.file.full_path` The `SourceRelativeUrl` log field is used with `SourceFileName` to map the value `%{SourceRelativeUrl}/%{SourceFileName}` to the `target.file.full_path` UDM field. |
| `FileDownloaded` | `ZipFileName` | `principal.resource.parent` | `target.file.names` The `ZipFileName` log field is mapped to the `target.file.names` UDM field. |
| `FileMalwareDetected` | `VirusVendor` | `target.labels[VirusVendor]` | `security_result.threat_feed_name` |
| `SearchQueryPerformed` | `EventData` | `target.application` | `additional.fields[client_type]` |
| `FileSyncDownloadedFull` | `ObjectId` | `src.url` | `target.url` |
| `FileSyncDownloadedFull` | `SourceFileExtension` | `src.file.mime_type` | `target.file.mime_type` The `SourceFileExtension` log field is mapped to the `target.file.mime_type` UDM field. |
| `FileSyncDownloadedFull` | `SourceFileName` | `src.file.full_path` | `target.file.full_path` The value of `%{SourceRelativeUrl}/%{SourceFileName}` is mapped to the `target.file.full_path` UDM field. |
| `FileSyncDownloadedFull` | `SourceRelativeUrl` | `src.file.full_path` | `target.file.full_path` The `SourceRelativeUrl` log field is used with `SourceFileName` to map the value `%{SourceRelativeUrl}/%{SourceFileName}` to the `target.file.full_path` UDM field. |
| `FileSyncDownloadedFull` | `FileSyncBytesCommitted` | `src.file.size` | `target.file.size` |
| `FileSyncDownloadedPartial` | `ObjectId` | `src.url` | `target.url` |
| `FileSyncDownloadedPartial` | `SourceFileExtension` | `src.file.mime_type` | `target.file.mime_type` |
| `FileSyncDownloadedPartial` | `SourceFileName` | `src.file.full_path` | `target.file.full_path` |
| `FileSyncDownloadedPartial` | `SourceRelativeUrl` | `src.file.full_path` | `target.file.full_path` The value `%{SourceRelativeUrl}/%{SourceFileName}` is mapped to the `target.file.full_path` UDM field. |
| `FileSyncDownloadedPartial` | `FileSyncBytesCommitted` | `src.file.size` | `target.file.size` |
| `ProjectCheckedOut` | `Action` | `security_result.description` If `Action` is equal to `Accepted` then, the UDM field `security_result.description` is set to "Accepted - The user accepted an event or workflow." Else if `Action` is equal to `Accessed` then, the UDM field `security_result.description` is set to "Accessed - The user accessed an entity." Else if `Action` is equal to `Activated` then, the UDM field `security_result.description` is set to "Activated - The user activated an entity, event or workflow." Else if `Action` is equal to `Cancelled` then, the UDM field `security_result.description` is set to "Cancelled - The user cancelled an event or workflow." Else if `Action` is equal to `CheckedIn` then, the UDM field `security_result.description` is set to "CheckedIn - The user check in an entity." Else if `Action` is equal to `CheckedOut` then, the UDM field `security_result.description` is set to "CheckedOut - The user checkout an entity." Else if `Action` is equal to `Copied` then, the UDM field `security_result.description` is set to "Copied - The user copied an entity." Else if `Action` is equal to `Created` then, the UDM field `security_result.description` is set to "Created - The user created an entity." Else if `Action` is equal to `Deactivated` then, the UDM field `security_result.description` is set to "Deactivated - The user deactivated an entity." Else if `Action` is equal to `Deleted` then, the UDM field `security_result.description` is set to "Deleted - The user deleted an entity." Else if `Action` is equal to `Exported` then, the UDM field `security_result.description` is set to "Exported - The user exported an entity." Else if `Action` is equal to `ForceCheckedIn` then, the UDM field `security_result.description` is set to "ForceCheckedIn - The user caused an entity to be force checked in." Else if `Action` is equal to `Modified` then, the UDM field `security_result.description` is set to "Modified - The user modified an entity." Else if `Action` is equal to `Published` then, the UDM field `security_result.description` is set to "Published - The user published an entity." Else if `Action` is equal to `Redacted` then, the UDM field `security_result.description` is set to "Redacted - The user redacted an entity." Else if `Action` is equal to `Rejected` then, the UDM field `security_result.description` is set to "Rejected - The user rejected an entity." Else if `Action` is equal to `Restarted` then, the UDM field `security_result.description` is set to "Restarted - The user restarted an event or workflow." Else if `Action` is equal to `Saved` then, the UDM field `security_result.description` is set to "Saved - The user saved an entity." Else if `Action` is equal to `Sent` then, the UDM field `security_result.description` is set to "Sent - The user sent an entity." Else if `Action` is equal to `Submitted` then, the UDM field `security_result.description` is set to "Submitted - The user submitted an entity for review or workflow." | `security_result.action_details` If `Action` is equal to `Accepted` then, the UDM field `security_result.action_details` is set to "Accepted - The user accepted an event or workflow." Else if `Action` is equal to `Accessed` then, the UDM field `security_result.action_details` is set to "Accessed - The user accessed an entity." Else if `Action` is equal to `Activated` then, the UDM field `security_result.action_details` is set to "Activated - The user activated an entity, event or workflow." Else if `Action` is equal to `Cancelled` then, the UDM field `security_result.action_details` is set to "Cancelled - The user cancelled an event or workflow." Else if `Action` is equal to `CheckedIn` then, the UDM field `security_result.action_details` is set to "CheckedIn - The user check in an entity." Else if `Action` is equal to `CheckedOut` then, the UDM field `security_result.action_details` is set to "CheckedOut - The user checkout an entity." Else if `Action` is equal to `Copied` then, the UDM field `security_result.action_details` is set to "Copied - The user copied an entity." Else if `Action` is equal to `Created` then, the UDM field `security_result.action_details` is set to "Created - The user created an entity." Else if `Action` is equal to `Deactivated` then, the UDM field `security_result.action_details` is set to "Deactivated - The user deactivated an entity." Else if `Action` is equal to `Deleted` then, the UDM field `security_result.action_details` is set to "Deleted - The user deleted an entity." Else if `Action` is equal to `Exported` then, the UDM field `security_result.action_details` is set to "Exported - The user exported an entity." Else if `Action` is equal to `ForceCheckedIn` then, the UDM field `security_result.action_details` is set to "ForceCheckedIn - The user caused an entity to be force checked in." Else if `Action` is equal to `Modified` then, the UDM field `security_result.action_details` is set to "Modified - The user modified an entity." Else if `Action` is equal to `Published` then, the UDM field `security_result.action_details` is set to "Published - The user published an entity." Else if `Action` is equal to `Redacted` then, the UDM field `security_result.action_details` is set to "Redacted - The user redacted an entity." Else if `Action` is equal to `Rejected` then, the UDM field `security_result.action_details` is set to "Rejected - The user rejected an entity." Else if `Action` is equal to `Restarted` then, the UDM field `security_result.action_details` is set to "Restarted - The user restarted an event or workflow." Else if `Action` is equal to `Saved` then, the UDM field `security_result.action_details` is set to "Saved - The user saved an entity." Else if `Action` is equal to `Sent` then, the UDM field `security_result.action_details` is set to "Sent - The user sent an entity." Else if `Action` is equal to `Submitted` then, the UDM field `security_result.action_details` is set to "Submitted - The user submitted an entity for review or workflow." |
| `ProjectAccessed` | `Action` | `security_result.description` If `Action` is equal to `Accepted` then, the UDM field `security_result.description` is set to "Accepted - The user accepted an event or workflow." Else if `Action` is equal to `Accessed` then, the UDM field `security_result.description` is set to "Accessed - The user accessed an entity." Else if `Action` is equal to `Activated` then, the UDM field `security_result.description` is set to "Activated - The user activated an entity, event or workflow." Else if `Action` is equal to `Cancelled` then, the UDM field `security_result.description` is set to "Cancelled - The user cancelled an event or workflow." Else if `Action` is equal to `CheckedIn` then, the UDM field `security_result.description` is set to "CheckedIn - The user check in an entity." Else if `Action` is equal to `CheckedOut` then, the UDM field `security_result.description` is set to "CheckedOut - The user checkout an entity." Else if `Action` is equal to `Copied` then, the UDM field `security_result.description` is set to "Copied - The user copied an entity." Else if `Action` is equal to `Created` then, the UDM field `security_result.description` is set to "Created - The user created an entity." Else if `Action` is equal to `Deactivated` then, the UDM field `security_result.description` is set to "Deactivated - The user deactivated an entity." Else if `Action` is equal to `Deleted` then, the UDM field `security_result.description` is set to "Deleted - The user deleted an entity." Else if `Action` is equal to `Exported` then, the UDM field `security_result.description` is set to "Exported - The user exported an entity." Else if `Action` is equal to `ForceCheckedIn` then, the UDM field `security_result.description` is set to "ForceCheckedIn - The user caused an entity to be force checked in." Else if `Action` is equal to `Modified` then, the UDM field `security_result.description` is set to "Modified - The user modified an entity." Else if `Action` is equal to `Published` then, the UDM field `security_result.description` is set to "Published - The user published an entity." Else if `Action` is equal to `Redacted` then, the UDM field `security_result.description` is set to "Redacted - The user redacted an entity." Else if `Action` is equal to `Rejected` then, the UDM field `security_result.description` is set to "Rejected - The user rejected an entity." Else if `Action` is equal to `Restarted` then, the UDM field `security_result.description` is set to "Restarted - The user restarted an event or workflow." Else if `Action` is equal to `Saved` then, the UDM field `security_result.description` is set to "Saved - The user saved an entity." Else if `Action` is equal to `Sent` then, the UDM field `security_result.description` is set to "Sent - The user sent an entity." Else if `Action` is equal to `Submitted` then, the UDM field `security_result.description` is set to "Submitted - The user submitted an entity for review or workflow." | `security_result.action_details` If `Action` is equal to `Accepted` then, the UDM field `security_result.action_details` is set to "Accepted - The user accepted an event or workflow." Else if `Action` is equal to `Accessed` then, the UDM field `security_result.action_details` is set to "Accessed - The user accessed an entity." Else if `Action` is equal to `Activated` then, the UDM field `security_result.action_details` is set to "Activated - The user activated an entity, event or workflow." Else if `Action` is equal to `Cancelled` then, the UDM field `security_result.action_details` is set to "Cancelled - The user cancelled an event or workflow." Else if `Action` is equal to `CheckedIn` then, the UDM field `security_result.action_details` is set to "CheckedIn - The user check in an entity." Else if `Action` is equal to `CheckedOut` then, the UDM field `security_result.action_details` is set to "CheckedOut - The user checkout an entity." Else if `Action` is equal to `Copied` then, the UDM field `security_result.action_details` is set to "Copied - The user copied an entity." Else if `Action` is equal to `Created` then, the UDM field `security_result.action_details` is set to "Created - The user created an entity." Else if `Action` is equal to `Deactivated` then, the UDM field `security_result.action_details` is set to "Deactivated - The user deactivated an entity." Else if `Action` is equal to `Deleted` then, the UDM field `security_result.action_details` is set to "Deleted - The user deleted an entity." Else if `Action` is equal to `Exported` then, the UDM field `security_result.action_details` is set to "Exported - The user exported an entity." Else if `Action` is equal to `ForceCheckedIn` then, the UDM field `security_result.action_details` is set to "ForceCheckedIn - The user caused an entity to be force checked in." Else if `Action` is equal to `Modified` then, the UDM field `security_result.action_details` is set to "Modified - The user modified an entity." Else if `Action` is equal to `Published` then, the UDM field `security_result.action_details` is set to "Published - The user published an entity." Else if `Action` is equal to `Redacted` then, the UDM field `security_result.action_details` is set to "Redacted - The user redacted an entity." Else if `Action` is equal to `Rejected` then, the UDM field `security_result.action_details` is set to "Rejected - The user rejected an entity." Else if `Action` is equal to `Restarted` then, the UDM field `security_result.action_details` is set to "Restarted - The user restarted an event or workflow." Else if `Action` is equal to `Saved` then, the UDM field `security_result.action_details` is set to "Saved - The user saved an entity." Else if `Action` is equal to `Sent` then, the UDM field `security_result.action_details` is set to "Sent - The user sent an entity." Else if `Action` is equal to `Submitted` then, the UDM field `security_result.action_details` is set to "Submitted - The user submitted an entity for review or workflow." |
| `SharingInvitationAccepted` | `EventData` | `target.resource.name` | `target.group.group_display_name` If `EventData` is not `empty`, the extracted `target_group_display_name` field from `EventData` is mapped to the `target.group.group_display_name` UDM field. |
| `AccessRequestApproved` | `EventData` | `target.resource.name` | `target.group.group_display_name` If `EventData` is not `empty`, the extracted `target_group_display_name` field from `EventData` is mapped to the `target.group.group_display_name` UDM field. |
| `Add group.` | `Target` | Iterate through each `field` in `Target` and If `field.Type` is equal to `1`, the `field.ID` field is mapped to `target.group.group_display_name`. Else if `field.Type` is equal to `1`, then If `field.ID` matches `(^.+@.+$)`, the `field.ID` field is mapped to `target.user.email_addresses`, and if `field.ID` also matches `(^.{0,256}$)`, the `field.ID` field is mapped to `target.user.userid`. Else if `field.ID` matches `(^.{0,256}$)`, the `field.ID` field is mapped to `target.user.userid`. Else, the `field.ID` field is mapped to `additional.fields.value` and the `additional.fields.key` UDM field is set to `userid`. Else, `field.ID` is mapped to the `security_result.detection_fields.value` UDM field and the UDM field `security_result.detection_fields.key` is set to the value `target_%{field.Type}".` | Iterate through each `field` in `Target` and If `field.Type` equal to `1`, the `field.ID` field is mapped to `target.group.group_display_name`. Else if `field.Type` is equal to `5` then, If `field.ID` matches `(^.+@.+$)`, then the `field.ID` field is mapped to `target.user.email_addresses`, and if `field.ID` also matches `(^.{0,256}$)`, the `field.ID` field is mapped to `target.user.userid`. Else if `field.ID` matches `(^.{0,256}$)`, the `field.ID` field is mapped to `target.user.userid`. Else, the `field.ID` field is mapped to `additional.fields.value` UDM field and the `additional.fields.key`UDM field is set to `userid`. Else, `field.ID` is mapped to `additional.fields.value` UDM field and the UDM field `additional.fields.key` is set to `target_%{field.Type}`. |
| `Update device.` | `ModifiedProperties` | If `ModifiedProperties` is not `empty`, fields are extracted from it: `os_name` is mapped to `target.platform`. `os_version` is mapped to `target.platform_version`. `device_name` is mapped to `target.resource.name`. | `target.resource.attribute.labels[device_physical_ids]` If `ModifiedProperties` is not `empty`, the extracted `device_ids` field from `ModifiedProperties` is mapped to `target.resource.attribute.labels.value` where `target.resource.attribute.labels.key` is set to `device_physical_ids`. |
| `Update device.` | `Target` | Iterate through each `field` in `Target`: If `field.Type` is equal to `1`, the field `field.ID` is mapped to the UDM field `target.group.group_display_name`. Else if `field.Type` is equal to `5`: If `field.ID` matches the regular expression pattern `(^.+@.+$)`, the field `field.ID` is mapped to the UDM field `target.user.email_addresses`, and if `field.ID` also matches the regular expression pattern `(^.{0,256}$)`, the field `field.ID` is mapped to the UDM field `target.user.userid`. Else if `field.ID` matches the regular expression pattern `(^.{0,256}$)`, the field `field.ID` is mapped to the UDM field `target.user.userid`. Else, the field `field.ID` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `userid`. Else, the field `field.ID` is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `target_%{field.Type}`. | Iterate through each `field` in `Target`: If `field.Type` is equal to `1`, the field `field.ID` is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `id`. Else if `field.Type` is equal to `5`: If `field.ID` matches the regular expression pattern `(^.+@.+$)`, the field `field.ID` is mapped to the UDM field `target.user.email_addresses`, and if `field.ID` also matches the regular expression pattern `(^.{0,256}$)`, the field `field.ID` is mapped to the UDM field `target.user.userid`. Else if `field.ID` matches the regular expression pattern `(^.{0,256}$)`, the field `field.ID` is mapped to the UDM field `target.user.userid`. Else, the field `field.ID` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `userid`. Else, the field `field.ID` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `target_%{field.Type}`. |
| `Disable account.` | `ModifiedProperties` | `security_result.description` | `security_result.action_details` Iterate through each `field` in `ModifiedProperties`: If `field.Name` is equal to `AccountEnable`, the value "AccountEnabled - %{account_enabled}" is mapped to the `security_result.action_details` UDM field. |
| `TeamsSessionStarted` | `ObjectId` | `target.resource.product_object_id` | `additional.fields[object_id]` The `ObjectId` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `object_id`. |
| `TeamSettingChanged` | `Name` | `target.resource.attribute.labels[Name]` The `Name` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `Name`. | `target.resource.name` The `Name` log field is mapped to the `target.resource.name` UDM field. |
| `Update` | `Item.Attachments` | | `about.file.names` Iterate through `Item.Attachments`, if the extracted `file_name` is not `empty` and not equal to `" "`, the extracted `file_name` field is mapped to the `about.file.names` UDM field. |
| `Update` | `Item.Attachments` | | `about.file.size` Iterate through `Item.Attachments`, if the extracted `file_name` is not `empty` and not equal to `" "`, the extracted `file_size` field is mapped to the `about.file.size` UDM field. |
| `New-InboxRule` | `ObjectId` | `target.group.product_object_id` | `target.resource.product_object_id` |
| `Set-InboxRule` | `ObjectId` | `target.group.product_object_id` | `target.resource.product_object_id` |
| `MailItemsAccessed` | `Folders` | Iterate through each `key`, `value` pair in `Folders`: The `value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{key}`. Iterate through each `key1`, `value1` pair in `value`: The `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Folders_%{key}_%{key1}`. Iterate through each `key2`, `value2` pair in `value1`: The `value2` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{key}_%{key1}_%{key2}`. Iterate through each `key3`, `value3` pair in `value2`: The `value3` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{key}_%{key1}_%{key2}_%{key3}`. | `target.resource.name` Iterate through each `key`, `value` pair in `Folders`: If `key` is equal to `Path`, the `value` is mapped to the `target.resource.name` UDM field. Else if `key` is equal to `id`, the `value` is mapped to the `target.resource.product_object_id` UDM field. Else, iterate through nested maps similar to the old UDM field logic, mapping to `additional.fields`. |
| `MailItemsAccessed` | `Folders` | Iterate through each `key`, `value` pair in `Folders`: The `value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{key}`. Iterate through each `key1`, `value1` pair in `value`: The `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Folders_%{key}_%{key1}`. Iterate through each `key2`, `value2` pair in `value1`: The `value2` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{key}_%{key1}_%{key2}`. Iterate through each `key3`, `value3` pair in `value2`: The `value3` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{key}_%{key1}_%{key2}_%{key3}`. | `target.resource.product_object_id` Iterate through each `key`, `value` pair in `Folders`: If `key` is equal to `Path`, the `value` is mapped to the `target.resource.name` UDM field. Else if `key` is equal to `id`, the `value` is mapped to the `target.resource.product_object_id` UDM field. Else, iterate through nested maps similar to the old UDM field logic, mapping to `additional.fields`. |
| `AssignWorkspaceToPipeline` | `WorkSpaceName` | `principal.resource.attribute.labels[WorkSpaceName]` The `WorkSpaceName` log field is mapped to the UDM field `principal.resource.attribute.labels.value` and the UDM field `principal.resource.attribute.labels.key` is set to `WorkSpaceName`. | `target.resource.attribute.labels[WorkSpaceName]` The `WorkSpaceName` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `WorkSpaceName`. |
| `AssignWorkspaceToPipeline` | `WorkspaceId` | `principal.resource.attribute.labels[WorkspaceId]` The `WorkspaceId` log field is mapped to the UDM field `principal.resource.attribute.labels.value` and the UDM field `principal.resource.attribute.labels.key` is set to `WorkspaceId`. | `target.resource.attribute.labels[WorkspaceId]` The `WorkspaceId` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `WorkspaceId`. |
| `CreateEmailSubscription` | `SubscribeeInformation` | `network.email.to` Iterate through each `subscriber` in `SubscribeeInformation`: The `subscriber.RecipientEmail` field is mapped to the `network.email.to` UDM field. | `about.user.email_addresses` Iterate through each `key`, `value` pair in `SubscribeeInformation`: Iterate through each `key1`, `value1` pair in `value`: If `key1` is equal to `RecipientEmail`, the `value1` is mapped to the `about.user.email_addresses` UDM field. Else if `key1` is equal to `RecipientName`, the `value1` is mapped to the `about.user.user_display_name` UDM field. Else, the `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `SubscribeeInformation_%{key}_%{key1}`. |
| `CreateEmailSubscription` | `SubscribeeInformation` | `additional.fields[SubscribeeInformation_%{key}_%{key1}]` Iterate through each `key`, `value` pair in `SubscribeeInformation`: Iterate through each `key1`, `value1` pair in `value`: If `key1` is equal to `RecipientName`, the `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `SubscribeeInformation_%{key}_%{key1}`. | `about.user.user_display_name` Iterate through each `key`, `value` pair in `SubscribeeInformation`: Iterate through each `key1`, `value1` pair in `value`: If `key1` is equal to `RecipientEmail`, the `value1` is mapped to the `about.user.email_addresses` UDM field. Else if `key1` is equal to `RecipientName`, the `value1` is mapped to the `about.user.user_display_name` UDM field. Else, the `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `SubscribeeInformation_%{key}_%{key1}`. |
| `InstallApp` | `AppName` | `target.labels[AppName]` The `AppName` log field is mapped to the UDM field `target.labels.value` and the UDM field `target.labels.key` is set to `AppName`. `additional.fields[AppName]` The `AppName` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `AppName`. | `target.resource.name` The `AppName` log field is mapped to the `target.resource.name` UDM field. |
| `InstallTemplateApp` | `TemplateAppOwnerTenantObjectId` | `principal.user.product_object_id` The `TemplateAppOwnerTenantObjectId` log field is mapped to the `principal.user.product_object_id` UDM field. | `about.user.product_object_id` The `TemplateAppOwnerTenantObjectId` log field is mapped to the `about.user.product_object_id` UDM field. |
| `UpdateEmailSubscription` | `SubscribeeInformation` | `network.email.to` Iterate through each `subscriber` in `SubscribeeInformation`: The `subscriber.RecipientEmail` field is mapped to the `network.email.to` UDM field. | `about.user.email_addresses` Iterate through each `key`, `value` pair in `SubscribeeInformation`: Iterate through each `key1`, `value1` pair in `value`: If `key1` is equal to `RecipientEmail`, the `value1` is mapped to the `about.user.email_addresses` UDM field. Else if `key1` is equal to `RecipientName`, the `value1` is mapped to the `about.user.user_display_name` UDM field. Else, the `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `SubscribeeInformation_%{key}_%{key1}`. |
| `UpdateEmailSubscription` | `SubscribeeInformation` | `network.email.to` Iterate through each `subscriber` in `SubscribeeInformation`: The `subscriber.RecipientEmail` field is mapped to the `network.email.to` UDM field. | `about.user.user_display_name` Iterate through each `key`, `value` pair in `SubscribeeInformation`: Iterate through each `key1`, `value1` pair in `value`: If `key1` is equal to `RecipientEmail`, the `value1` is mapped to the `about.user.email_addresses` UDM field. Else if `key1` is equal to `RecipientName`, the `value1` is mapped to the `about.user.user_display_name` UDM field. Else, the `value1` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `SubscribeeInformation_%{key}_%{key1}`. |
| `Set-MailUser` | `ObjectId` | `target.group.group_display_name` | `target.resource.attribute.labels[object_id]` The `ObjectId` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `object_id`. |
| `Set-MailUser` | `Parameters` | The extracted `email_address` from `group_email_address` is mapped to the `target.group.email_addresses` UDM field. | `target.user.email_addresses` The extracted `email` from `email_addresses` is mapped to the `target.user.email_addresses` UDM field. The extracted `email_address` from `group_email_address` is mapped to the `target.user.email_addresses` UDM field. |
| `Set-MailContact` | `ObjectId` | `target.group.group_display_name` | `target.resource.attribute.labels[object_id]` The `ObjectId` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `object_id`. |
| `Set-MailContact` | `Parameters` | The extracted `email_address` from `group_email_address` is mapped to the `target.group.email_addresses` UDM field. | `target.user.email_addresses` The extracted `email` from `email_addresses` is mapped to the `target.user.email_addresses` UDM field. The extracted `email_address` from `group_email_address` is mapped to the `target.user.email_addresses` UDM field. |
| `Set-Mailbox` | `ObjectId` | `target.group.group_display_name` | `target.resource.attribute.labels[object_id]` The `ObjectId` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `object_id`. |
| `Set-DistributionGroup` | `Parameters` | `security_result.description` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `AcceptMessagesOnlyFromSendersOrMembers`, the `parameter.Value` is mapped to the `security_result.description` UDM field. | `additional.fields[accept_messages_only_from_senders_or_members]` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `AcceptMessagesOnlyFromSendersOrMembers`, the `parameter.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `accept_messages_only_from_senders_or_members`. |
| `Set-Contact` | `Parameters` | The extracted `email_address` from `group_email_address` is mapped to the `target.group.email_addresses` UDM field. | `target.user.email_addresses` The extracted `email` from `email_addresses` is mapped to the `target.user.email_addresses` UDM field. The extracted `email_address` from `group_email_address` is mapped to the `target.user.email_addresses` UDM field. |
| `Remove-MigrationUser` | `Parameters` | `security_result.detection_fields.key/value` Iterate through each `parameter` in `Parameters`: The `parameter.Value` is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `%{parameter.Name}`. | `target.user.email_addresses` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the `parameter.Value` is mapped to the `target.user.email_addresses` UDM field. |
| `ViewedSearchExported` | `Case` | `metadata.description` | `about.resource.product_object_id` |
| `CreateWorkingSet` | `CaseId` | `target.resource.product_object_id` | `target.resource.attribute.labels[case_id]` The `CaseId` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `case_id`. |
| `CreateWorkingSet` | `CaseName` | `target.resource.name` | `target.resource.attribute.labels[case_name]` The `CaseName` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `case_name`. |
| `CreateWorkingSet` | `ExtendedProperties` | `target.resource.attribute.labels.key/value` Iterate through each `field` in `ExtendedProperties`: The `field.Value` is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `%{field.Name}`. | `target.resource.product_object_id` Iterate through each `field` in `ExtendedProperties`: If `field.Name` is equal to `WorkingSetId`, the `field.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `SearchUpdated` | `ExtendedProperties` | `about.labels[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `%{data.Name}`. `additional.fields[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `SearchUpdated` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `SearchPermissionUpdated` | `ExtendedProperties` | `principal.labels[Users]` Iterate through each `data` in `ExtendedProperties`: The `data.Value` is mapped to the UDM field `principal.labels.value` and the UDM field `principal.labels.key` is set to `%{data.Name}`. `additional.fields[Users]` Iterate through each `data` in `ExtendedProperties`: The `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.user.email_addresses` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `Users` and `data.Value` matches the regular expression pattern `(^.+@.+$)` and `data.Value` matches the regular expression pattern `^.{0,255}$`, the `data.Value` is mapped to the `target.user.email_addresses` UDM field. |
| `HoldUpdated` | `ExtendedProperties` | `about.labels[HoldId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `%{data.Name}`. `additional.fields[HoldId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `HoldUpdated` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `SearchRemoved` | `ExtendedProperties` | `about.labels[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `%{data.Name}`. `additional.fields[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `SearchRemoved` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `SearchPermissionRemoved` | `ExtendedProperties` | `principal.labels[Users]` Iterate through each `data` in `ExtendedProperties`: The `data.Value` is mapped to the UDM field `principal.labels.value` and the UDM field `principal.labels.key` is set to `%{data.Name}`. `additional.fields[Users]` Iterate through each `data` in `ExtendedProperties`: The `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.user.email_addresses` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `Users`, the `data.Value` is mapped to the `target.user.email_addresses` UDM field. |
| `HoldRemoved` | `ExtendedProperties` | `about.labels[HoldId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `%{data.Name}`. `additional.fields[HoldId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `HoldRemoved` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `HoldCreated` | `ExtendedProperties` | `about.labels[HoldId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `%{data.Name}`. `additional.fields[HoldId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `HoldCreated` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `SearchCreated` | `ExtendedProperties` | `about.labels[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `%{data.Name}`. `additional.fields[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `SearchCreated` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `SearchStarted` | `ExtendedProperties` | `about.labels[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `%{data.Name}`. `additional.fields[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `SearchStarted` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `SearchStopped` | `ExtendedProperties` | `about.labels[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `%{data.Name}`. `additional.fields[SearchIds]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchIds`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `SearchStopped` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `SearchPermissionCreated` | `ObjectId` | `additional.fields[ObjectId]` The `ObjectId` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ObjectId`. | `target.resource.name` The `ObjectId` log field is mapped to the `target.resource.name` UDM field. |
| `SearchPermissionCreated` | `ExtendedProperties` | `principal.labels[Users]` Iterate through each `data` in `ExtendedProperties`: The `data.Value` is mapped to the UDM field `principal.labels.value` and the UDM field `principal.labels.key` is set to `%{data.Name}`. `additional.fields[Users]` Iterate through each `data` in `ExtendedProperties`: The `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. | `target.user.email_addresses` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `Users`, the `data.Value` is mapped to the `target.user.email_addresses` UDM field. |
| `StreamInvokeVideoView` | `OperationDetails` | `metadata.description` | `additional.fields[operation_details]` The `OperationDetails` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `operation_details`. |
| `StreamInvokeVideoShare` | `OperationDetails` | `metadata.description` | `additional.fields[operation_details]` The `OperationDetails` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `operation_details`. |
| `DlpRuleMatch` | `ObjectId` | `network.email.mail_id` | `target.url` or `network.email.mail_id` If `Workload` contains one of the following values: - `Onedrive` - `Sharepoint` then the `ObjectId` log field is mapped to the `target.url` UDM field. Else if `Workload` is equal to `Exchange`, the `ObjectId` log field is mapped to the `network.email.mail_id` UDM field. |
| `DlpInfo` | `ObjectId` | `network.email.mail_id` | `target.url` or `network.email.mail_id` If `Workload` contains one of the following values: - `Onedrive` - `Sharepoint` then the `ObjectId` log field is mapped to the `target.url` UDM field. Else if `Workload` is equal to `Exchange`, the `ObjectId` log field is mapped to the `network.email.mail_id` UDM field. |
| `SiteCollectionCreated` | `EventData` | `target.resource.name` | `additional.fields[site_creation_source]` The `EventData` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `site_creation_source`. |
| `NetworkAccessPolicyChanged` | `ModifiedProperties` | `additional.fields.key/value` Iterate through each `field` in `ModifiedProperties`: If `field.NewValue` is not `empty` and if `field.Name` is equal to `IPAddressAllowList`, the `field.NewValue` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `NewIPAddressAllowList`. | `about.ip` Iterate through each `field` in `ModifiedProperties`: If `field.NewValue` is not `empty` and if `field.Name` is equal to `IPAddressAllowList`, iterate through `ip_address_allow_list` and map extracted `ip_address` to the `about.ip` UDM field. |
| `AlertEntityGenerated` | `Category` | `security_result.category` The UDM field `security_result.category` is set to `DATA_EXFILTRATION`. | `security_result.category` If `Category` is equal to `DataLossPrevention`, the UDM field `security_result.category` is set to `DATA_EXFILTRATION`. |
| `AlertEntityGenerated` | `Name` | `security_result.summary` | `security_result.description`\< |
| `AlertEntityGenerated` | `PolicyId` | `target.labels[PolicyId]` The `PolicyId` log field is mapped to the UDM field `target.labels.value` and the UDM field `target.labels.key` is set to `PolicyId`. `additional.fields[PolicyId]` The `PolicyId` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `PolicyId`. | `security_result.detection_fields[PolicyId]` The `PolicyId` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `PolicyId`. |
| `AlertEntityGenerated` | `Status` | `target.resource.attribute.labels[Status]` The `Status` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `Status`. | `security_result.detection_fields[Status]` The `Status` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `Status`. |
| `AlertEntityGenerated` | `Source` | `security_result.description` | `security_result.detection_fields[Source]` The `Source` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `Source`. |
| `AlertEntityGenerated` | `Comments` | `about.labels[Comments]` The `Comments` log field is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `Comments`. `additional.fields[Comments]` The `Comments` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Comments`. | `security_result.about.investigation.comments` The `Comments` log field is mapped to the `security_result.about.investigation.comments` UDM field. |
| `AlertEntityGenerated` | `EntityType` | `target.resource.attribute.labels[EntityType]` The `EntityType` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `EntityType`. | `target.resource.resource_subtype` The `EntityType` log field is mapped to the `target.resource.resource_subtype` UDM field. |
| `AlertTriggered` | `Category` | `security_result.category` The UDM field `security_result.category` is set to `DATA_EXFILTRATION`. | `security_result.category` If `Category` is equal to `DataLossPrevention`, the UDM field `security_result.category` is set to `DATA_EXFILTRATION`. |
| `AlertTriggered` | `Name` | `security_result.summary` | `security_result.description` The `Name` log field is mapped to the `security_result.description` UDM field. |
| `AlertTriggered` | `PolicyId` | `target.labels[PolicyId]` The `PolicyId` log field is mapped to the UDM field `target.labels.value` and the UDM field `target.labels.key` is set to `PolicyId`. `additional.fields[PolicyId]` The `PolicyId` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `PolicyId`. | `security_result.detection_fields[PolicyId]` The `PolicyId` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `PolicyId`. |
| `AlertTriggered` | `Status` | `target.resource.attribute.labels[Status]` The `Status` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `Status`. | `security_result.detection_fields[Status]` The `Status` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `Status`. |
| `AlertTriggered` | `Source` | `security_result.description` | `security_result.detection_fields[Source]` The `Source` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `Source`. |
| `AlertTriggered` | `Comments` | `about.labels[Comments]` The `Comments` log field is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `Comments`. `additional.fields[Comments]` The `Comments` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Comments`. | `security_result.about.investigation.comments` The `Comments` log field is mapped to the `security_result.about.investigation.comments` UDM field. |
| `AlertTriggered` | `EntityType` | `target.resource.attribute.labels[EntityType]` The `EntityType` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `EntityType`. | `target.resource.resource_subtype` The `EntityType` log field is mapped to the `target.resource.resource_subtype` UDM field. |
| `AlertUpdated` | `Name` | `security_result.summary` | `security_result.description` The `Name` log field is mapped to the `security_result.description` UDM field. |
| `AlertUpdated` | `PolicyId` | `target.labels[PolicyId]` The `PolicyId` log field is mapped to the UDM field `target.labels.value` and the UDM field `target.labels.key` is set to `PolicyId`. `additional.fields[PolicyId]` The `PolicyId` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `PolicyId`. | `security_result.detection_fields[PolicyId]` The `PolicyId` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `PolicyId`. |
| `AlertUpdated` | `Status` | `target.resource.attribute.labels[Status]` The `Status` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `Status`. | `security_result.detection_fields[Status]` The `Status` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `Status`. |
| `AlertUpdated` | `Source` | `security_result.description` | `security_result.detection_fields[Source]` The `Source` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `Source`. |
| `AlertUpdated` | `Comments` | `about.labels[Comments]` The `Comments` log field is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `Comments`. `additional.fields[Comments]` The `Comments` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Comments`. | `security_result.about.investigation.comments` The `Comments` log field is mapped to the `security_result.about.investigation.comments` UDM field. |
| `AlertUpdated` | `EntityType` | `target.resource.attribute.labels[EntityType]` The `EntityType` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `EntityType`. | `target.resource.resource_subtype` The `EntityType` log field is mapped to the `target.resource.resource_subtype` UDM field. |
| `Get-CaseHoldPolicy` | `Parameters` | `target.process.command_line` | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| `Remove-CaseHoldPolicy` | `Parameters` | `target.process.command_line` | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| `Set-CaseHoldPolicy` | `Parameters` | `target.process.command_line` | `target.resource.name` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| `New-CaseHoldRule` | `Parameters` | `target.process.command_line` | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_name` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| `Remove-CaseHoldRule` | `Parameters` | `target.process.command_line` | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_product_object_id` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| `Set-CaseHoldRule` | `Parameters` | `target.process.command_line` | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_product_object_id` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| `Remove-ComplianceCase` | `Parameters` | `target.process.command_line` | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| `Set-ComplianceCase` | `Parameters` | `target.process.command_line` | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| `Add-ComplianceCaseMember` | `Parameters` | `target.process.command_line` | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_name` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| `Remove-ComplianceCaseMember` | `Parameters` | `target.process.command_line` `target.user.email_addresses` `target.user.userid` | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_name` field from `Parameters` is mapped to the `target.resource.name` UDM field. |
| `ValidaterbacAccessCheck` | `RelativeUrl` | `target.url` | `additional_fields[relative_url]` The `RelativeUrl` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `relative_url`. |
| `NewComplianceTag` | `ExtendedProperties` | `target.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `target.user.user_display_name` UDM field. | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| `NewRetentionComplianceRule` | `ExtendedProperties` | `target.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `target.user.user_display_name` UDM field. | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| `NewRetentionCompliancePolicy` | `ExtendedProperties` | `target.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `target.user.user_display_name` UDM field. | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| `RemoveComplianceTag` | `ExtendedProperties` | `target.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `target.user.user_display_name` UDM field. | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| `Get-CsTeamsUpgradeOverridePolicy` | `Parameters` | `security_result.description` Iterate through each `param` in `Parameters`: If `param.Value` is not `empty` and `param.Name` is `Tenant` or `identity`, construct and map to `security_result.description`. | `target.resource.attribute.labels` Iterate through each `param` in `Parameters`: If `param.Value` is not `empty` and if `param.Name` is equal to `Tenant`, `param.Value` is mapped to `target.resource.attribute.labels.value` and `target.resource.attribute.labels.key` is set to `Tenant`. Else if `param.Name` is equal to `identity`, `param.Value` is mapped to `target.resource.attribute.labels.value` and `target.resource.attribute.labels.key` is set to `Identity`. |
| `Get-CsTeamsUpgradeOverridePolicy` | `TenantName` | `target.resource.product_object_id` | `metadata.product_deployment_id` The `TenantName` log field is mapped to the `metadata.product_deployment_id` UDM field. |
| `TeamsAdminAction` | `ExtraProperties` | `additional.fields.key/value` If `ExtraProperties` is not `empty`, iterate through `ExtraProperties`: `ExtraPropertie.Value` is mapped to `additional.fields.value` and `additional.fields.key` is set to `ExtraProperties_%{index}_%{ExtraPropertie.Key}`. | `security_result.detection_fields` If `ExtraProperties` is not `empty`, iterate through `ExtraProperties`: If `ExtraPropertie.Key` is equal to `CorrelationId`, `ExtraPropertie.Value` is mapped to `security_result.detection_fields.value` and `security_result.detection_fields.key` is set to `ExtraProperties_%{index}_%{ExtraPropertie.Key}`. The `ExtraPropertie.Value` is also mapped to `additional.fields.value` and `additional.fields.key` is set to `ExtraProperties_%{index}_%{ExtraPropertie.Key}`. |
| `TeamsAdminAction` | `UserClaims` | `security_result.description` | `principal.user.attributes.role.name` The `UserClaims` log field is mapped to the `principal.user.attributes.role.name` UDM field. |
| `Update-DistributionGroupMember` | `Parameters` | `security_result.description` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, map to `target.group.product_object_id` or `target.group.email_addresses`. Else if `parameter.Name` is equal to `Members`, map `parameter.Value` to `security_result.description`. | `target.group.group_display_name` and `about.user.user_display_name` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, `parameter.Value` is mapped to `target.group.group_display_name`. Else if `parameter.Name` is equal to `Members`, iterate through `members_list` and map `member` to `about.user.user_display_name`. |
| `TIMailData` | `SenderIp` | `src.ip` | `principal.ip` |
| `SiteDesignInvoked` | `EventData` | `target.resource.attribute.labels[SiteDesignId]` The extracted `site_design_id` from `EventData` is mapped to `target.resource.attribute.labels.value` and `target.resource.attribute.labels.key` is set to `SiteDesignId`. | `target.resource.product_object_id` The extracted `site_design_id` from `EventData` is mapped to the `target.resource.product_object_id` UDM field. |
| `Set-TransportConfig` | `Parameters` | `principal.user.email_addresses` `principal.user.userid`\< | `additional.fields` Iterate through each `data` in `Parameters`: The `data.Value` is mapped to `additional.fields.value` and `additional.fields.key` is set to `%{data.Name}`. |
| `Set-RecipientEnforcementProvisioningPolicy` | `Parameters` | `target.labels[Identity]` The `Parameters` log field is mapped to `target.labels.value` and `target.labels.key` is set to `Identity`. `additional.fields[Identity]` The `Parameters` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `Identity`. | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| `Set-OwaMailboxPolicy` | `Parameters` | `target.labels[Identity]` The `Parameters` log field is mapped to `target.labels.value` and `target.labels.key` is set to `Identity`. `additional.fields[Identity]` The `Parameters` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `Identity`. | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| `Set-MailboxPlan` | `Parameters` | `target.labels[Identity]` The `Parameters` log field is mapped to `target.labels.value` and `target.labels.key` is set to `Identity`. `additional.fields[Identity]` The `Parameters` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `Identity`. | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| `Set-LabelProperties` | `Parameters` | `target.labels[Identity]` The `Parameters` log field is mapped to `target.labels.value` and `target.labels.key` is set to `Identity`. `additional.fields[Identity]` The `Parameters` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `Identity`. | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| `Set-Label` | `Parameters` | `target.labels[Identity]` The `Parameters` log field is mapped to `target.labels.value` and `target.labels.key` is set to `Identity`. `additional.fields[Identity]` The `Parameters` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `Identity`. | `target.resource.name` The `Parameters` log field is mapped to the `target.resource.name` UDM field. |
| `Set-ExchangeAssistanceConfig` | `Parameters` | `target.url` Iterate through each `field` in `Parameters`: If `field.Name` is equal to `PrivacyStatementURL`, `field.Value` is mapped to `target.url`. | `about.url` Iterate through each `field` in `Parameters`: If `field.Name` is equal to `PrivacyStatementURL`, `field.Value` is mapped to `about.url`. |
| `RemovedSearchReport` | `ObjectId` | `additional.fields[ObjectId]` The `ObjectId` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `ObjectId`. | `target.resource.name` The `ObjectId` log field is mapped to the `target.resource.name` UDM field. |
| `Get-PrivacyManagementPolicy` | `Parameters` | `target.process.command_line` | `additional.fields[Parameters]` The `Parameters` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `Parameters`. |
| `Set-RetentionCompliancePolicy` | `Parameters` | `target.process.command_line` | `additional.fields[Parameters]` The `Parameters` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Parameters`. |
| `Set-UnifiedGroup` | `Parameters` | The extracted `email_address` from `group_email_address` is mapped to the `target.group.email_addresses` UDM field. | `target.user.email_addresses` The extracted `email` from `email_addresses` is mapped to the `target.user.email_addresses` UDM field. The extracted `email_address` from `group_email_address` is mapped to the `target.user.email_addresses` UDM field. |
| `Set-ComplianceTag` | `Parameters` | `target.process.command_line` | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| `Get-DlpSensitiveInformationTypeRulePackage` | `Parameters` | `target.process.command_line` | `target.resource.product_object_id` If `Parameters` is not `empty`, the extracted `identity_product_object_id` field from `Parameters` is mapped to the `target.resource.product_object_id` UDM field. |
| `Get-DlpDetectionsReport` | `Parameters` | `target.process.command_line` | `security_result.detection_fields` `security_result.rule_name` If `Parameters` is not `empty`, the extracted `start_date` field is mapped to `security_result.detection_fields.value` with key `start_date`. The extracted `end_date` field is mapped to `security_result.detection_fields.value` with key `end_date`. The extracted `event_type` field is mapped to `security_result.detection_fields.value` with key `event_type`. The extracted `source` field is mapped to `security_result.detection_fields.value` with key `source`. The extracted `dlp_compliance_rule` field is mapped to `security_result.rule_name`. |
| `Add-RoleGroupMember` | `Parameters` | Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the extracted `target_group_product_object_id` is mapped to `target.group.product_object_id` and `group_identity` is mapped to `target.group.email_addresses`. | `target.group.group_display_name` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the `parameter.Value` is mapped to the `target.group.group_display_name` UDM field. |
| `Update-RoleGroupMember` | `Parameters` | Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the extracted `target_group_product_object_id` is mapped to `target.group.product_object_id` and `group_identity` is mapped to `target.group.email_addresses`. | `target.group.attribute.labels[identity]` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the `parameter.Value` is mapped to the UDM field `target.group.attribute.labels.value` and the UDM field `target.group.attribute.labels.key` is set to `Identity`. |
| `New-RoleGroup` | `Parameters` | Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the extracted `target_group_product_object_id` is mapped to `target.group.product_object_id` and `group_identity` is mapped to `target.group.email_addresses`. | `target.group.attribute.labels[identity]` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Identity`, the `parameter.Value` is mapped to the UDM field `target.group.attribute.labels.value` and the UDM field `target.group.attribute.labels.key` is set to `Identity`. |
| `HoldViewed` | `ExtendedProperties` | `about.labels[HoldId]` The `ExtendedProperties` log field is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `HoldId`. `additional.fields[HoldId]` The `ExtendedProperties` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `HoldId`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `HoldId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `HoldViewed` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `Get-CaseHoldRule` | `Parameters` | `target.resource.product_object_id` | `target.resource.name` If `Parameters` is not `empty`, the extracted `target_resource_product_object_id` field is mapped to `target.resource.product_object_id` and the extracted `target_resource_name` field is mapped to `target.resource.name`. |
| `ViewedSearchReport` | `ExtendedProperties` | `about.labels[SearchIds]` The `ExtendedProperties` log field is mapped to the UDM field `about.labels.value` and the UDM field `about.labels.key` is set to `SearchIds`. `additional.fields[SearchIds]` The `ExtendedProperties` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `SearchIds`. | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `SearchId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. |
| `ViewedSearchReport` | `ExtendedProperties` | `target.resource.product_object_id` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the `target.resource.product_object_id` UDM field. | `additional.fields[CaseId]` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CaseId`, the `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `RemoveRetentionComplianceRule` | `ExtendedProperties` | `target.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `target.user.user_display_name` UDM field. | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| `NewAdaptiveScope` | `ExtendedProperties` | `target.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `target.user.user_display_name` UDM field. | `about.user.user_display_name` Iterate through each `data` in `ExtendedProperties`: If `data.Name` is equal to `CreatedBy`, the `data.Value` is mapped to the `about.user.user_display_name` UDM field. |
| `HeartBeat` | `Common.ProcessName` | `target.process.command_line` | `principal.resource.attribute.labels` The `Common.ProcessName` log field is mapped to the UDM field `principal.resource.attribute.labels.value` and the UDM field `principal.resource.attribute.labels.key` is set to `process_name`. |
| `HeartBeat` | `Common.ApplicationName` | `target.process.command_line` | `principal.resource.name` The `Common.ApplicationName` log field is mapped to the `principal.resource.name` UDM field. |
| `HeartBeat` | `Common.DeviceName` | `target.hostname` | `principal.hostname` |
| `HeartBeat` | `Common.DeviceName` | `target.asset.hostname` | `principal.asset.hostname` |
| `HeartBeat` | `Common.ApplicationId` | `target.resource.product_object_id` | `principal.resource.product_object_id` |
| `HeartBeat` | `Common.ProductVersion` | `metadata.product_version` | `metadata.product_version` or `additional.fields[version]` If `Version` is not `empty`, the `Common.ProductVersion` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `version`. Else, the `Common.ProductVersion` log field is mapped to the `metadata.product_version` UDM field. |
| `StreamEditAdminGlobalRoleMembers` | `OperationDetails` | `metadata.description` | `target.user.attribute.roles.name` |
| `StreamEditAdminGlobalRoleMembers` | `OperationDetails` | `metadata.description` | `target.user.attribute.labels` The `OperationDetails.SetTo.PrincipalIds` field is mapped to the UDM field `target.user.attribute.labels.value` and the UDM field `target.user.attribute.labels.key` is set to `PrincipalIds`. |
| `StreamEditAdminGlobalRoleMembers` | `OperationDetails` | `metadata.description` | `target.resource.attribute.labels` The `OperationDetails.ResourceType` field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `ResourceType`. |
| `StreamEditAdminGlobalRoleMembers` | `OperationDetails` | `metadata.description` | `target.resource.attribute.labels` The `OperationDetails.SetTo.AllowEveryoneInOrganization` field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `AllowEveryoneInOrganization`. |
| `StreamEditAdminGlobalRoleMembers` | `OperationDetails` | `metadata.description` | `target.resource.attribute.labels` The `OperationDetails.ResourceId` field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `ResourceId`. |
| `StreamEditAdminGlobalRoleMembers` | `OperationDetails` | `metadata.description` | `additional.fields` The `OperationDetails.Id` field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `OperationDetails_Id`. |
| `DeleteFlow` | `FormName` | `target.resource.name` | `about.resource.name` |
| `DeleteFlow` | `FormId` | `target.resource.product_object_id` | `about.resource.product_object_id` |
| `DeleteFlow` | `FormTypes` | `target.resource.attribute.labels[from_type]` The `FormTypes` log field is mapped to the UDM field `target.resource.attribute.labels.value` and the UDM field `target.resource.attribute.labels.key` is set to `from_type`. | `about.resource.resource_subtype` The `FormTypes` log field is mapped to the `about.resource.resource_subtype` UDM field. |
| `MeetingDetail` | `Modalities` | `security_result.summary` | `additional.fields[modalities]` The `Modalities` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `modalities`. |
| `UserSubmission` | `ExtendedProperties.SubmissionSource` | `security_result.rule_id` | `additional.fields[ExtendedProperties_SubmissionSource]` The `ExtendedProperties.SubmissionSource` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ExtendedProperties_SubmissionSource`. |
| `UserSubmission` | `ExtendedProperties.SubmissionCategory` | `security_result.category_details` | `additional.fields[ExtendedProperties_SubmissionCategory]` The `ExtendedProperties.SubmissionCategory` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ExtendedProperties_SubmissionCategory`. |
| `UserSubmission` | `ExtendedProperties.SubmissionId` | `security_result.rule_name` | `additional.fields[ExtendedProperties_SubmissionId]` The `ExtendedProperties.SubmissionId` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ExtendedProperties_SubmissionId`. |
| `UserSubmission` | `P1Sender` | `principal.user.email_addresses` | `network.smtp.mail_from` |
| `Get-User` | `Parameters` | `target.process.command_line` | `target.user.email_addresses` If `Parameters` is not `empty`, the extracted `identity_email` field from `Parameters` is mapped to the `target.user.email_addresses` UDM field. |
| `New-MigrationBatch` | `Parameters` | Iterate through each `data` in `Parameters`: If `data.Name` is equal to `Identity`, map to various `target.user` fields based on regex matches. | `additional.fields.key/value` Iterate through each `data` in `Parameters`: The `data.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `%{data.Name}`. |
| `UserSubmissionTriage` | `ExtendedProperties.SubmissionSource` | `security_result.rule_id` | `additional.fields[ExtendedProperties_SubmissionSource]` The `ExtendedProperties.SubmissionSource` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ExtendedProperties_SubmissionSource`. |
| `UserSubmissionTriage` | `ExtendedProperties.SubmissionCategory` | `security_result.category_details` | `additional.fields[ExtendedProperties_SubmissionCategory]` The `ExtendedProperties.SubmissionCategory` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ExtendedProperties_SubmissionCategory`. |
| `UserSubmissionTriage` | `ExtendedProperties.SubmissionId` | `security_result.rule_name` | `additional.fields[ExtendedProperties_SubmissionId]` The `ExtendedProperties.SubmissionId` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ExtendedProperties_SubmissionId`. |
| `UserSubmissionTriage` | `P1Sender` | `principal.user.email_addresses` | `network.smtp.mail_from` |
| `UserSubmissionTriage` | `P1SenderDomain` | `principal.administrative_domain` | `network.dns_domain` If `Workload` is equal to `P1SenderDomain`, the `P1SenderDomain` log field is mapped to the `network.dns_domain` UDM field. |
| `AirInvestigationData` | `Data` | Iterate through `Data.Entities`: `entity.P1Sender` is mapped to `principal.labels.value` with key `P1Sender`. | `network.smtp.mail_from` Iterate through `Data.Entities`: the `entity.P1Sender` field is mapped to the `network.smtp.mail_from` UDM field. |
| `AirInvestigationData` | `InvestigationName` | `target.resource.name` | `security_result.summary` |
| `AirInvestigationData` | `Status` | `security_result.summary` | `additional.fields[status]` The `Status` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `status`. |
| `Set-MailboxJunkEmailConfiguration` | `Parameters` | `target.user.email_addresses` Iterate through `Parameters`: If `field.Name` is `BlockedSendersAndDomains`, iterate through `field.Value`, mapping valid emails to `target.user.email_addresses`. | `about.user.email_addresses` Iterate through `Parameters`: If `field.Name` is equal to `BlockedSendersAndDomains` and `field.Value` is not `empty`, iterate through each `email` in `field.Value`. If `email` matches the regular expression pattern `(^.+@.+$)`, the `email` is mapped to the `about.user.email_addresses` UDM field. |
| `New-DistributionGroup` | `Parameters` | Iterate through `Parameters` for `Name`, `ManagedBy`, and `Members`, mapping to various `target.group` and `target.user` fields. | `target.group.group_display_name`, `about.user.attribute.labels`, `about.user.user_display_name` Iterate through each `parameter` in `Parameters`: If `parameter.Name` is equal to `Name`, the `parameter.Value` is mapped to the `target.group.group_display_name` UDM field. Else if `parameter.Name` is equal to `ManagedBy`, the `parameter.Value` is mapped to `about.user.attribute.labels.value` and `about.user.attribute.labels.key` is set to `managed_by`. Else if `parameter.Name` is equal to `Members`, the `parameter.Value` is mapped to the `about.user.user_display_name` UDM field. |
| `StreamInvokeGetTranscript` | `OperationDetails` | `metadata.description` | `additional.fields[operation_details]` The `OperationDetails` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `operation_details`. |
| `ReportingAccessed` | `Action` | `security_result.description` | `security_result.action_details` |
| `RemovableMediaUnmount` | `MDATPDeviceId` | `target.asset.asset_id` | `principal.asset.asset_id` |
| `FileUploadedToCloud` | `MDATPDeviceId` | `security_result.detection_fields[MDATPDeviceId]` The `MDATPDeviceId` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `MDATPDeviceId`. | `principal.asset.asset_id` |
| `MDCRegulatoryComplianceAssessments` | `PropertyBag.Policy.Description` | `about.labels[policy_description]` The `PropertyBag.Policy.Description` log field is mapped to `about.labels.value` and `about.labels.key` is set to `policy_description`. `additional.fields[policy_description]` The `PropertyBag.Policy.Description` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `policy_description`. | `metadata.description` The `PropertyBag.Policy.Description` log field is mapped to the `metadata.description` UDM field. |
| `MDCRegulatoryComplianceAssessments` | `PropertyBag.Policy.DetailsLink` | `about.labels[policy_details_link]` The `PropertyBag.Policy.DetailsLink` log field is mapped to `about.labels.value` and `about.labels.key` is set to `policy_details_link`. `additional.fields[policy_details_link]` The `PropertyBag.Policy.DetailsLink` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `policy_details_link`. | `security_result.url_back_to_products` The `PropertyBag.Policy.DetailsLink` log field is mapped to the `security_result.url_back_to_products` UDM field. |
| `MDCRegulatoryComplianceAssessments` | `PropertyBag.Policy.PolicyInitiativeId` | `about.labels[policy_initiative_id]` The `PropertyBag.Policy.PolicyInitiativeId` log field is mapped to `about.labels.value` and `about.labels.key` is set to `policy_initiative_id`. `additional.fields[policy_initiative_id]` The `PropertyBag.Policy.PolicyInitiativeId` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `policy_initiative_id`. | `security_result.rule_labels[policy_initiative_id]` The `PropertyBag.Policy.PolicyInitiativeId` log field is mapped to the UDM field `security_result.rule_labels.value` and the UDM field `security_result.rule_labels.key` is set to `policy_initiative_id`. |
| `MDCRegulatoryComplianceAssessments` | `PropertyBag.Policy.PolicyInitiativeName` | `about.labels[policy_initiative_name]` The `PropertyBag.Policy.PolicyInitiativeName` log field is mapped to `about.labels.value` and `about.labels.key` is set to `policy_initiative_name`. `additional.fields[policy_initiative_name]` The `PropertyBag.Policy.PolicyInitiativeName` log field is mapped to `additional.fields.value` and `additional.fields.key` is set to `policy_initiative_name`. | `security_result.rule_labels[policy_initiative_name]` The `PropertyBag.Policy.PolicyInitiativeName` log field is mapped to the UDM field `security_result.rule_labels.value` and the UDM field `security_result.rule_labels.key` is set to `policy_initiative_name`. |
| `ListViewUpdated` | `DeviceDisplayName` | `principal.labels[device_display_name]` The `DeviceDisplayName` log field is mapped to the UDM field `principal.labels.value` and the UDM field `principal.labels.key` is set to `device_display_name`. | `principal.ip` The `DeviceDisplayName` log field is mapped to the `principal.ip` UDM field. |
| `PutConnection` | `AdditionalInfo.actionName` | `security_result.detection_fields[action_name]` The `AdditionalInfo.actionName` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `action_name`. | `security_result.action_details` The `AdditionalInfo.actionName` log field is mapped to the `security_result.action_details` UDM field. |
| `AdminSubmissionTablAllow` | `SubmissionConfidenceLevel` | `security_result.detection_fields[submission_confidence_level]` The `SubmissionConfidenceLevel` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `submission_confidence_level`. | `security_result.confidence_details` The `SubmissionConfidenceLevel` log field is mapped to the `security_result.confidence_details` UDM field. |
| `PutConnectionPermission` | `AdditionalInfo.actionName` | `security_result.detection_fields[action_name]` The `AdditionalInfo.actionName` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `action_name`. | `security_result.action_details` The `AdditionalInfo.actionName` log field is mapped to the `security_result.action_details` UDM field. |
| `TimesheetSaved` | `Action` | `security_result.description` | `security_result.action_details` |
| `ResourceCheckedOut` | `Action` | `security_result.description` | `security_result.action_details` |
| `SensitivityLabelUpdated` | `DeviceName` | `target.hostname` | `principal.hostname` |
| `SensitivityLabelUpdated` | `DeviceName` | `target.asset.hostname` | `principal.asset.hostname` |
| `QuarantineDenyReleaseMessage` | `QuarantinePolicy` | `security_result.detection_fields[QuarantinePolicy]` The `QuarantinePolicy` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `QuarantinePolicy`. | `security_result.rule_name` The `QuarantinePolicy` log field is mapped to the `security_result.rule_name` UDM field. |
| `QuarantineApproveReleaseMessage` | `QuarantinePolicy` | `security_result.detection_fields[QuarantinePolicy]` The `QuarantinePolicy` log field is mapped to the UDM field `security_result.detection_fields.value` and the UDM field `security_result.detection_fields.key` is set to `QuarantinePolicy`. | `security_result.rule_name` The `QuarantinePolicy` log field is mapped to the `security_result.rule_name` UDM field. |
| `FileCopiedToRemovableMedia` | `FileExtension` | `target.file.mime_type` | `src.file.mime_type` |
| `FileCopiedToRemovableMedia` | `FileSize` | `target.file.size` | `src.file.size` |
| `FileCopiedToRemovableMedia` | `Sha1` | `target.file.sha1` | `src.file.sha1` |
| `AppCleanedUpAfterExpiration` | `AddOnGuid` | `additional.fields[AddOnGuid]` The `AddOnGuid` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `AddOnGuid`. | `target.resource.product_object_id` The `AddOnGuid` log field is mapped to the `target.resource.product_object_id` UDM field. |
| `FileCopiedToRemovableMedia` | `Sha256` | `target.file.sha256` | `src.file.sha256` |
| `EditFlow` | `FlowDetailsUrl` | `metadata.url_back_to_product` | `target.url` |
| `FileTransferredByBluetooth` | `FileExtension` | `target.file.mime_type` | `src.file.mime_type` |
| `FileTransferredByBluetooth` | `FileSize` | `target.file.size` | `src.file.size` |
| `FileTransferredByBluetooth` | `ObjectId` | `target.file.full_path` | `src.file.full_path` |
| `FileTransferredByBluetooth` | `Sha1` | `target.file.sha1` | `src.file.sha1` |
| `FileTransferredByBluetooth` | `Sha256` | `target.file.sha256` | `src.file.sha256` |
| `FileCopiedToRemoteDesktopSession` | `FileExtension` | `target.file.mime_type` | `src.file.mime_type` |
| `FileCopiedToRemoteDesktopSession` | `FileSize` | `target.file.size` | `src.file.size` |
| `FileCopiedToRemoteDesktopSession` | `ObjectId` | `target.file.full_path` | `src.file.full_path` |
| `AutoSensitivityLabelRuleMatch` | `ExchangeMetaData.MessageID` | `additional.fields[ExchangeMetaData_MessageID]` The `ExchangeMetaData.MessageID` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `ExchangeMetaData_MessageID`. | `network.email.mail_id` The `ExchangeMetaData.MessageID` log field is mapped to the `network.email.mail_id` UDM field. |
| `Add app role assignment grant to user.` | `Workload` | `intermediary.application` | `target.application`
`additional.fields[workload]`
If the log fields `EventSource` and `Workload` are not `empty` and equal, then the log field `EventSource` is mapped to the `target.application` UDM field.
Else If, the log fields `EventSource` and `Workload` are not `empty` and not equal, then the log field `EventSource` is mapped to the `target.application` UDM field and the `Workload` field is mapped to `additional.fields.value` UDM field and the `additional.fields.key` UDM field is set to `workload`.
Else If, the log field `EventSource` is not `empty`, then the log field `EventSource` is mapped to the `target.application` UDM field.
Else If, the log field `Workload` is not `empty`, then the log field `Workload` is mapped to the `target.application` UDM field. |
| `AtpDetection` | `SourceWorkload` | `target.application`
If the `Operation` log field is equal to `AtpDetection`: - If the `SourceWorkload` log field is equal to `1`, then the UDM field `target.application` is set to `OneDrive`. - If the `SourceWorkload` log field is equal to `0`, then the UDM field `target.application` is set to `SharePoint`. - If the `SourceWorkload` log field is equal to `2`, then the UDM field `target.application` is set to `Microsoft Teams`. | `src.application`
If the `Operation` log field is equal to `AtpDetection`: - If the `SourceWorkload` log field is equal to `1`, then the UDM field `src.application` is set to `OneDrive`. - If the `SourceWorkload` log field is equal to `0`, then the UDM field `src.application` is set to `SharePoint`. - If the `SourceWorkload` log field is equal to `2`, then the UDM field `src.application` is set to `Microsoft Teams`. |
| `FileRenamed` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `FileArchived` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `FileCreatedOnNetworkShare` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `FileCreatedOnRemovableMedia` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `SlimFilePrinted` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `FilePrinted` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `FileCopiedToNetworkShare` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `ArchiveCreated` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `FileDownloadedFromBrowser` | `Application` | `target.application` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field mapped to the UDM field `target.application`. | `additional.fields[Application]` If the `Workload` log field is equal to `Endpoint`, then the `Application` log field is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `Application`. |
| `Add app role assignment grant to user.` | `ExtendedProperties` | `target.application` Iterate through each `field` in `ExtendedProperties`: If `field.Name` is equal to `targetName`, the `field.Value` is mapped to the UDM field `target.application`. | `additional.fields[targetName]` Iterate through each `field` in `ExtendedProperties`: If `field.Name` is equal to `targetName`, the `field.Value` is mapped to the UDM field `additional.fields.value` and the UDM field `additional.fields.key` is set to `targetName`. |
| `CopilotInteraction` | `CopilotEventData.AppHost` | `target.application`. | `additional.fields[CopilotEventDataAppHost]` |
| `ReactedToMessage, AppCleanedUpAfterExpiration, SignInEvent, ListCreated, ListViewUpdated, FileTranscriptContentAccessed, SharingLinkCreated, SharingLinkUpdated, AddedToSharingLink, SharingLinkUsed, SecurityGroupModified, FileSensitivityLabelChanged, TaskListRead, TaskModified, Add-MailboxLocation` | `AppAccessContext.IssuedAtTime` | `target.labels[AppAccessContext_IssuedAtTime]` `additional.fields[AppAccessContext_IssuedAtTime]` | `additional.fields[AppAccessContext_IssuedAtTime]` |
| `ReactedToMessage, AppCleanedUpAfterExpiration, SignInEvent, ListCreated, ListViewUpdated, FileTranscriptContentAccessed, SharingLinkCreated, SharingLinkUpdated, AddedToSharingLink, SharingLinkUsed, SecurityGroupModified, FileSensitivityLabelChanged, TaskListRead, TaskModified, Add-MailboxLocation` | `AppAccessContext.UniqueTokenId` | `target.labels[AppAccessContext_UniqueTokenId]` `additional.fields[AppAccessContext_UniqueTokenId]` | `additional.fields[AppAccessContext_UniqueTokenId]` |
| `FileRead, FileUploadedToCloud, FileCopiedToClipboard, FileTransferredByBluetooth, FileCopiedToRemoteDesktopSession, FileCopiedToRemovableMedia` | `EvidenceFile.StorageName` | `target.labels[Evidence Storage]` `additional.fields[Evidence Storage]` | `additional.fields[Evidence Storage]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.ArnEventId` | `about.labels[ArnEventId]` `additional.fields[ArnEventId]` | `additional.fields[ArnEventId]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.CloudProvider` | `about.labels[Cloud_provider]` `additional.fields[Cloud_provider]` | `additional.fields[Cloud_provider]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.EventType` | `about.labels[EventType]` `additional.fields[EventType]` | `additional.fields[EventType]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.PolicyInitiativeName` | `about.labels[PolicyInitiativeName]` `additional.fields[PolicyInitiativeName]` | `additional.fields[PolicyInitiativeName]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.SecurityAssessmentId` | `about.labels[SecurityAssessmentId]` `additional.fields[SecurityAssessmentId]` | `additional.fields[SecurityAssessmentId]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.StatusChangeDate` | `about.labels[StatusChangeDate]` `additional.fields[StatusChangeDate]` | `additional.fields[StatusChangeDate]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.StatusCode` | `about.labels[StatusCode]` `additional.fields[StatusCode]` | `additional.fields[StatusCode]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.StatusFirstEvaluationDate` | `about.labels[StatusFirstEvaluationDate]` `additional.fields[StatusFirstEvaluationDate]` | `additional.fields[StatusFirstEvaluationDate]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.SubscriptionId` | `about.labels[SubscriptionId]` `additional.fields[SubscriptionId]` | `additional.fields[SubscriptionId]` |
| `MDCAssessments` | `PropertyBag.AssessmentStatusPerInitiative.SubscriptionName` | `about.labels[SubscriptionName]` `additional.fields[SubscriptionName]` | `additional.fields[SubscriptionName]` |
| `MDCAssessments` | `PropertyBag.DataType` | `about.labels[PropertyBag Datatype]` `additional.fields[PropertyBag Datatype]` | `additional.fields[PropertyBag Datatype]` |
| `MDCRegulatoryComplianceAssessments` | `PropertyBag.Policy.ArnEventId` | `about.labels[policy_arn_event_id]` `additional.fields[policy_arn_event_id]` | `additional.fields[policy_arn_event_id]` |
| `MDCRegulatoryComplianceAssessments` | `PropertyBag.Policy.EventTime` | `about.labels[policy_event_time]` `additional.fields[policy_event_time]` | `additional.fields[policy_event_time]` |
| `MDCRegulatoryComplianceAssessments` | `PropertyBag.Policy.EventType` | `about.labels[policy_event_type]` `additional.fields[policy_event_type]` | `additional.fields[policy_event_type]` |
| `MDCRegulatoryComplianceAssessments` | `PropertyBag.DataType` | `about.labels[PropertyBag Datatype]` `additional.fields[PropertyBag Datatype]` | `additional.fields[PropertyBag Datatype]` |
| `PutConnection, PutConnectionPermission` | `ResourceId` | `target.labels[resource_id]` `additional.fields[resource_id]` | `additional.fields[resource_id]` |
| `PutConnection, PutConnectionPermission` | `AdditionalInfo.environmentName` | `target.labels[environment_name]` `additional.fields[environment_name]` | `additional.fields[environment_name]` |
| `GenerateDataflowSasToken` | `ItemName` | `target.labels[ItemName]` `additional.fields[ItemName]` | `additional.fields[ItemName]` |
| `UserLoggedIn, UserLoginFailed` | `ErrorNumber` | `about.labels[error_number]` `additional.fields[error_number]` | `additional.fields[error_number]` |
| `UserLoggedIn, UserLoginFailed` | `ExtendedProperties` | `about.labels[RequestType]` `additional.fields[RequestType]` | `additional.fields[RequestType]` |
| `UserLoggedIn, UserLoginFailed` | `ModifiedProperties` | `about.labels[%{field.Name}]` `additional.fields[%{field.Name}]` | `additional.fields[%{field.Name}]` |
| `TaskDeleted, TaskUpdated, TaskCreated, LinkedEntityUpdated, SubTaskCreated, TaskRead, SubTaskUpdated` | `TargetActorId` | `target.labels[TargetActorId]` `additional.fields[TargetActorId]` | `additional.fields[TargetActorId]` |
| `TaskDeleted, TaskUpdated, TaskCreated, LinkedEntityUpdated, SubTaskCreated, TaskRead, SubTaskUpdated` | `TargetActorTenantId` | `target.labels[TargetActorTenantId]` `additional.fields[TargetActorTenantId]` | `additional.fields[TargetActorTenantId]` |
| `TaskDeleted, TaskUpdated, TaskCreated, LinkedEntityUpdated, SubTaskCreated, TaskRead, SubTaskUpdated` | `ActorAppId` | `target.labels[ActorAppId]` `additional.fields[ActorAppId]` | `additional.fields[ActorAppId]` |
| `TeamsUserSignedOut` | `DeviceInformation` | `principal.labels[device_information]` `additional.fields[device_information]` | `additional.fields[device_information]` |
| `TeamsUserSignedOut` | `ItemName` | `target.labels[item_name]` `additional.fields[item_name]` | `additional.fields[item_name]` |
| `TeamsUserSignedOut` | `MessageId` | `target.labels[message_id]` `additional.fields[message_id]` | `additional.fields[message_id]` |
| `TeamsUserSignedOut` | `MessageVersion` | `target.labels[message_version]` `additional.fields[message_version]` | `additional.fields[message_version]` |
| `TeamsUserSignedOut` | `ObjectId` | `target.labels[object_id]` `additional.fields[object_id]` | `additional.fields[object_id]` |
| `ConnectFromExternalApplication` | `CustomData` | `about.labels[custom_data]` `additional.fields[custom_data]` | `additional.fields[custom_data]` |
| `Add user., Delete user., Update user., Enable account.` | `ModifiedProperties` | `target.labels[target_user_type_new]` `additional.fields[target_user_type_new]` | `additional.fields[target_user_type_new]` |
| `Add user., Delete user., Update user., Enable account.` | `ModifiedProperties` | `target.labels[target_user_type_old]` `additional.fields[target_user_type_old]` | `additional.fields[target_user_type_old]` |
| `Add user., Delete user., Update user., Enable account.` | `ModifiedProperties.StrongAuthenticationPhoneAppDetail.TenantDeviceId` | `target.labels[tenant_device_id_new]` `additional.fields[tenant_device_id_new]` | `additional.fields[tenant_device_id_new]` |
| `Add user., Delete user., Update user., Enable account.` | `ModifiedProperties.StrongAuthenticationPhoneAppDetail.NotificationType` | `about.labels[notification_type_old]` `additional.fields[notification_type_old]` | `additional.fields[notification_type_old]` |
| `Add user., Delete user., Update user., Enable account.` | `ModifiedProperties.StrongAuthenticationPhoneAppDetail.TenantDeviceId` | `about.labels[tenant_device_id_old]` `additional.fields[tenant_device_id_old]` | `additional.fields[tenant_device_id_old]` |
| `DeleteGroup, UnpublishApp, UpdateApp, AddTile, CreateApp, Import, EditContentProviderProperties, DeleteTile` | `TileText` | `target.labels[TileText]` `additional.fields[TileText]` | `additional.fields[TileText]` |
| `ViewedSearchExported, SearchViewed, SearchUpdated, SearchStarted, SearchExportDownloaded, CaseAdded, SetRetentionCompliancePolicy, NewRetentionCompliancePolicy, CaseUpdated, CaseMemberUpdated, CaseViewed, SearchCreated, SearchReport, RemoveComplianceTag, RemoveRetentionCompliancePolicy, SetRetentionComplianceRule, CaseAdminUpdated, HoldUpdated, HoldCreated, HoldRemoved, SearchRemoved, Update-eDiscoveryCaseAdmin, NewRetentionComplianceRule, ApplicableAdaptiveScopeChange, NewComplianceTag, SetComplianceTag, CaseMemberAdded, CaseMemberRemoved, CaseAdminAdded, CaseAdminRemoved, SearchPermissionUpdated, SearchPermissionCreated, SearchPermissionRemoved, SearchStopped, ApplicableAdaptivePolicyChange, HoldViewed, ViewedSearchReport, NewAdaptiveScope, RemoveRetentionComplianceRule, RemovedSearchReport, CaseRemoved` | `ExtendedProperties` | `about.labels[%{data.Name}]` `additional.fields[%{data.Name}]` | `additional.fields[%{data.Name}]` |
| `ViewedSearchExported, SearchViewed, SearchUpdated, SearchStarted, SearchExportDownloaded, CaseAdded, SetRetentionCompliancePolicy, NewRetentionCompliancePolicy, CaseUpdated, CaseMemberUpdated, CaseViewed, SearchCreated, SearchReport, RemoveComplianceTag, RemoveRetentionCompliancePolicy, SetRetentionComplianceRule, CaseAdminUpdated, HoldUpdated, HoldCreated, HoldRemoved, SearchRemoved, Update-eDiscoveryCaseAdmin, NewRetentionComplianceRule, ApplicableAdaptiveScopeChange, NewComplianceTag, SetComplianceTag, CaseMemberAdded, CaseMemberRemoved, CaseAdminAdded, CaseAdminRemoved, SearchPermissionUpdated, SearchPermissionCreated, SearchPermissionRemoved, SearchStopped, ApplicableAdaptivePolicyChange, HoldViewed, ViewedSearchReport, NewAdaptiveScope, RemoveRetentionComplianceRule, RemovedSearchReport, CaseRemoved` | `ExtendedProperties` | `principal.labels[%{data.Name}]` `additional.fields[%{data.Name}]` | `additional.fields[%{data.Name}]` |
| `TIMailData` | `Connector` | `about.labels[Connector]` `additional.fields[Connector]` | `additional.fields[Connector]` |
| `Set-CsOnlineDirectoryTenant, Set-CsHostedVoicemailPolicy, Get-CSSimpleUrlConfiguration, Set-TenantObjectVersion, Install-AdminAuditLogConfig, Install-DataClassificationConfig, Install-DefaultSharingPolicy, Install-ResourceConfig` | `OperationProperties` | `target.labels[%{field.Name}]` `additional.fields[%{field.Name}]` | `additional.fields[%{field.Name}]` |
| `ValidaterbacAccessCheck, ApplicableAdaptiveScopeChange, SearchMtpStatus, RemovedSearchReport, SearchTrialOffer, SearchTIKustoClusterInformation, SearchMtpRoleInfo, SearchMailflowForwardingData, SearchDataInsightsSubscription, SearchCustomerInsight, SearchConnectorReportData, SearchAlertAggregate, SearchAlert, SearchComplianceCase, AggregateActivityData, AggregateThreatProfileDetails, SearchLabelAnalyticsActivityData, SearchSecurityRedirection, SearchCustomTag, AggregateTransportQueueData, AuthorizeCustomerInsight, AuthorizeConnectorReportData, SearchAlertOverride, AuthorizeMailflowForwardingData, SearchDomainTrafficStatus, SearchAlertActivity, AggregateMailmetadata, SaveRoleGroupMember, SearchNdrDetailData, AggregateCampaignIntelligenceData, SearchAlertStory, SearchEmailTimelineEvents, AggregateThreatDetailsBulk` | `Parameters` | `about.labels[Parameters]` `additional.fields[Parameters]` | `additional.fields[Parameters]` |
| `New-ConditionalAccessPolicy, Set-ConditionalAccessPolicy, New-QuarantinePolicy, New-ExchangeAssistanceConfig, Set-OwaMailboxPolicy, Set-MailboxPlan, Set-LabelProperties, Set-ExchangeAssistanceConfig, Add-MailboxFolderPermission, Provision-ComplianceMailboxFolder, Remove-Mailbox, Enable-AddressListPaging, New-Mailbox, New-App, Set-RecipientEnforcementProvisioningPolicy, Set-MailboxJunkEmailConfiguration` | `OperationProperties` | `target.labels[%{field.Name}]` `additional.fields[%{field.Name}]` | `additional.fields[%{field.Name}]` |
| `AirInvestigationData` | `Data.AlertType` | `target.labels[AlertType]` `additional.fields[AlertType]` | `additional.fields[AlertType]` |
| `AirInvestigationData` | `Data.Entities.AadId` | `principal.labels[AadId-%{index}]` `additional.fields[AadId-%{index}]` | `additional.fields[AadId-%{index}]` |
| `AirInvestigationData` | `Data.Entities.AntispamDirection` | `principal.labels[AntispamDirection-%{index}]` `additional.fields[AntispamDirection-%{index}]` | `additional.fields[AntispamDirection-%{index}]` |
| `AirInvestigationData` | `Data.Entities.CampaignID` | `principal.labels[CampaignID]` `additional.fields[CampaignID]` | `additional.fields[CampaignID]` |
| `AirInvestigationData` | `Data.Entities.ClickCount` | `principal.labels[ClickCount]` `additional.fields[ClickCount]` | `additional.fields[ClickCount]` |
| `AirInvestigationData` | `Data.Entities.ClusterBy` | `principal.labels[ClusterBy]` `additional.fields[ClusterBy]` | `additional.fields[ClusterBy]` |
| `AirInvestigationData` | `Data.Entities.ClusterByValue` | `principal.labels[ClusterByValue]` `additional.fields[ClusterByValue]` | `additional.fields[ClusterByValue]` |
| `AirInvestigationData` | `Data.Entities.ClusterGroup` | `principal.labels[ClusterGroup]` `additional.fields[ClusterGroup]` | `additional.fields[ClusterGroup]` |
| `AirInvestigationData` | `Data.Entities.Connector` | `principal.labels[Connector]` `additional.fields[Connector]` | `additional.fields[Connector]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.Inbox` | `principal.labels[CountByDeliveryLocation_Inbox]` `additional.fields[CountByDeliveryLocation_Inbox]` | `additional.fields[CountByDeliveryLocation_Inbox]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.DeletedFolder` | `principal.labels[CountByDeliveryLocation_DeletedFolder]` `additional.fields[CountByDeliveryLocation_DeletedFolder]` | `additional.fields[CountByDeliveryLocation_DeletedFolder]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.DeletedFolder` | `principal.labels[CountByDeliveryLocation_Dropped]` `additional.fields[CountByDeliveryLocation_Dropped]` | `additional.fields[CountByDeliveryLocation_Dropped]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.External` | `principal.labels[CountByDeliveryLocation_External]` `additional.fields[CountByDeliveryLocation_External]` | `additional.fields[CountByDeliveryLocation_External]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.Failed` | `principal.labels[CountByDeliveryLocation_Failed]` `additional.fields[CountByDeliveryLocation_Failed]` | `additional.fields[CountByDeliveryLocation_Failed]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.Forwarded` | `principal.labels[CountByDeliveryLocation_Forwarded]` `additional.fields[CountByDeliveryLocation_Forwarded]` | `additional.fields[CountByDeliveryLocation_Forwarded]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.JunkFolder` | `principal.labels[CountByDeliveryLocation_JunkFolder]` `additional.fields[CountByDeliveryLocation_JunkFolder]` | `additional.fields[CountByDeliveryLocation_JunkFolder]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.Quarantine` | `principal.labels[CountByDeliveryLocation_Quarantine]` `additional.fields[CountByDeliveryLocation_Quarantine]` | `additional.fields[CountByDeliveryLocation_Quarantine]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.Unknown` | `principal.labels[CountByDeliveryLocation_Unknown]` `additional.fields[CountByDeliveryLocation_Unknown]` | `additional.fields[CountByDeliveryLocation_Unknown]` |
| `AirInvestigationData` | `Data.Entities.CountByProtectionStatus.Blocked` | `principal.labels[CountByProtectionStatus_Blocked]` `additional.fields[CountByProtectionStatus_Blocked]` | `additional.fields[CountByProtectionStatus_Blocked]` |
| `AirInvestigationData` | `Data.Entities.CountByProtectionStatus.Delivered` | `principal.labels[CountByProtectionStatus_Delivered]` `additional.fields[CountByProtectionStatus_Delivered]` | `additional.fields[CountByProtectionStatus_Delivered]` |
| `AirInvestigationData` | `Data.Entities.CountByProtectionStatus.DeliveredAsSpam` | `principal.labels[CountByProtectionStatus_DeliveredAsSpam]` `additional.fields[CountByProtectionStatus_DeliveredAsSpam]` | `additional.fields[CountByProtectionStatus_DeliveredAsSpam]` |
| `AirInvestigationData` | `Data.Entities.CountByDeliveryLocation.DeliveredAsSpam` | `principal.labels[CountByDeliveryLocation_DeliveredAsSpam]` `additional.fields[CountByDeliveryLocation_DeliveredAsSpam]` | `additional.fields[CountByDeliveryLocation_DeliveredAsSpam]` |
| `AirInvestigationData` | `Data.Entities.CountByThreatType.HighConfPhish` | `principal.labels[CountByThreatType_HighConfPhish]` `additional.fields[CountByThreatType_HighConfPhish]` | `additional.fields[CountByThreatType_HighConfPhish]` |
| `AirInvestigationData` | `Data.Entities.CountByThreatType.MaliciousUrl` | `principal.labels[CountByThreatType_MaliciousUrl]` `additional.fields[CountByThreatType_MaliciousUrl]` | `additional.fields[CountByThreatType_MaliciousUrl]` |
| `AirInvestigationData` | `Data.Entities.CountByThreatType.Malware` | `principal.labels[CountByThreatType_Malware]` `additional.fields[CountByThreatType_Malware]` | `additional.fields[CountByThreatType_Malware]` |
| `AirInvestigationData` | `Data.Entities.CountByThreatType.Phish` | `principal.labels[CountByThreatType_Phish]` `additional.fields[CountByThreatType_Phish]` | `additional.fields[CountByThreatType_Phish]` |
| `AirInvestigationData` | `Data.Entities.CountByThreatType.Spam` | `principal.labels[CountByThreatType_Spam]` `additional.fields[CountByThreatType_Spam]` | `additional.fields[CountByThreatType_Spam]` |
| `AirInvestigationData` | `Data.Entities.DeliveryAction` | `about.labels[Entities_DeliveryAction]` `additional.fields[Entities_DeliveryAction]` | `additional.fields[Entities_DeliveryAction]` |
| `AirInvestigationData` | `Data.Entities.DeliveryLocation` | `about.labels[Entities_DeliveryLocation]` `additional.fields[Entities_DeliveryLocation]` | `additional.fields[Entities_DeliveryLocation]` |
| `AirInvestigationData` | `Data.Entities.$id` | `about.labels[Entities_id$]` `additional.fields[Entities_id$]` | `additional.fields[Entities_id$]` |
| `AirInvestigationData` | `Data.Entities.EmailCount` | `principal.labels[EmailCount]` `additional.fields[EmailCount]` | `additional.fields[EmailCount]` |
| `AirInvestigationData` | `Data.Entities.FirstSeen` | `about.labels[entity_FirstSeen]` `additional.fields[entity_FirstSeen]` | `additional.fields[entity_FirstSeen]` |
| `AirInvestigationData` | `Data.Entities.InternetMessageId` | `principal.labels[entity_InternetMessageId]` `additional.fields[entity_InternetMessageId]` | `additional.fields[entity_InternetMessageId]` |
| `AirInvestigationData` | `Data.Entities.IsVolumeAnamoly` | `principal.labels[entity_IsVolumeAnamoly]` `additional.fields[entity_IsVolumeAnamoly]` | `additional.fields[entity_IsVolumeAnamoly]` |
| `AirInvestigationData` | `Data.Entities.Language` | `principal.labels[entity_Language]` `additional.fields[entity_Language]` | `additional.fields[entity_Language]` |
| `AirInvestigationData` | `Data.Entities.MailboxPrimaryAddress` | `principal.labels[entity_MailboxPrimaryAddress]` `additional.fields[entity_MailboxPrimaryAddress]` | `additional.fields[entity_MailboxPrimaryAddress]` |
| `AirInvestigationData` | `Data.Entities.MailCount` | `principal.labels[entity_MailCount]` `additional.fields[entity_MailCount]` | `additional.fields[entity_MailCount]` |
| `AirInvestigationData` | `Data.Entities.NetworkMessageId` | `principal.labels[entity_NetworkMessageId]` `additional.fields[entity_NetworkMessageId]` | `additional.fields[entity_NetworkMessageId]` |
| `AirInvestigationData` | `networkmessage` | `principal.labels[NetworkMessage_Id]` `additional.fields[NetworkMessage_Id]` | `additional.fields[NetworkMessage_Id]` |
| `AirInvestigationData` | `Data.Entities.OriginalDeliveryLocation` | `principal.labels[entity_OriginalDeliveryLocation]` `additional.fields[entity_OriginalDeliveryLocation]` | `additional.fields[entity_OriginalDeliveryLocation]` |
| `AirInvestigationData` | `Data.Entities.P1Sender` | `principal.labels[P1Sender]` `additional.fields[P1Sender]` | `additional.fields[P1Sender]` |
| `AirInvestigationData` | `Data.Entities.P1SenderDisplayName` | `principal.labels[P1SenderDisplayName]` `additional.fields[P1SenderDisplayName]` | `additional.fields[P1SenderDisplayName]` |
| `AirInvestigationData` | `Data.Entities.P1SenderDomain` | `principal.labels[P1SenderDomain]` `additional.fields[P1SenderDomain]` | `additional.fields[P1SenderDomain]` |
| `AirInvestigationData` | `Data.Entities.P2Sender` | `principal.labels[P2Sender]` `additional.fields[P2Sender]` | `additional.fields[P2Sender]` |
| `AirInvestigationData` | `Data.Entities.PhishConfidenceLevel` | `principal.labels[PhishConfidenceLevel]` `additional.fields[PhishConfidenceLevel]` | `additional.fields[PhishConfidenceLevel]` |
| `AirInvestigationData` | `Data.Entities.Query` | `principal.labels[Query]` `additional.fields[Query]` | `additional.fields[Query]` |
| `AirInvestigationData` | `Data.Entities.QueryTime` | `principal.labels[QueryTime]` `additional.fields[QueryTime]` | `additional.fields[QueryTime]` |
| `AirInvestigationData` | `Data.Entities.ReceivedDate` | `principal.labels[ReceivedDate]` `additional.fields[ReceivedDate]` | `additional.fields[ReceivedDate]` |
| `AirInvestigationData` | `Data.Entities.Recipient` | `principal.labels[Recipient]` `additional.fields[Recipient]` | `additional.fields[Recipient]` |
| `AirInvestigationData` | `Data.Entities.RiskLevel` | `principal.labels[RiskLevel]` `additional.fields[RiskLevel]` | `additional.fields[RiskLevel]` |
| `AirInvestigationData` | `Data.Entities.Sender` | `principal.labels[Sender]` `additional.fields[Sender]` | `additional.fields[Sender]` |
| `AirInvestigationData` | `Data.Entities.SenderIP` | `principal.labels[SenderIP]` `additional.fields[SenderIP]` | `additional.fields[SenderIP]` |
| `AirInvestigationData` | `Data.Entities.Source` | `principal.labels[Source]` `additional.fields[Source]` | `additional.fields[Source]` |
| `AirInvestigationData` | `Data.Entities.Subject` | `principal.labels[Subject]` `additional.fields[Subject]` | `additional.fields[Subject]` |
| `AirInvestigationData` | `ThreatDetectionMethod` | `principal.labels[ThreatDetectionMethod]` `additional.fields[ThreatDetectionMethod]` | `additional.fields[ThreatDetectionMethod]` |
| `AirInvestigationData` | `Threat` | `principal.labels[Threats]` `additional.fields[Threats]` | `additional.fields[Threats]` |
| `AirInvestigationData` | `Data.Entities.Upn` | `principal.labels[Enities_Upn]` `additional.fields[Enities_Upn]` | `additional.fields[Enities_Upn]` |
| `AirInvestigationData` | `Data.Entities.Url` | `principal.labels[Enities_Url]` `additional.fields[Enities_Url]` | `additional.fields[Enities_Url]` |
| `AirInvestigationData` | `Data.Entities.Urls` | `principal.labels[Url - %{index4}]` `additional.fields[Url - %{index4}]` | `additional.fields[Url - %{index4}]` |
| `AirInvestigationData` | `Data.Entities.Urn` | `principal.labels[Enities_Urn]` `additional.fields[Enities_Urn]` | `additional.fields[Enities_Urn]` |
| `AirInvestigationData` | `Data.Intent` | `principal.labels[Data_Intent]` `additional.fields[Data_Intent]` | `additional.fields[Data_Intent]` |
| `AirInvestigationData` | `Data.IsIncident` | `principal.labels[Data_IsIncident]` `additional.fields[Data_IsIncident]` | `additional.fields[Data_IsIncident]` |
| `AirInvestigationData` | `Data.LogCreationTime` | `principal.labels[Data_LogCreationTime]` `additional.fields[Data_LogCreationTime]` | `additional.fields[Data_LogCreationTime]` |
| `AirInvestigationData` | `Data.ProcessingEndTime` | `about.labels[Data_ProcessingEndTime]` `additional.fields[Data_ProcessingEndTime]` | `additional.fields[Data_ProcessingEndTime]` |
| `AirInvestigationData` | `Data.ProviderAlertId` | `principal.labels[Data_ProviderAlertId]` `additional.fields[Data_ProviderAlertId]` | `additional.fields[Data_ProviderAlertId]` |
| `AirInvestigationData` | `Data.ProviderName` | `principal.labels[Data_ProviderName]` `additional.fields[Data_ProviderName]` | `additional.fields[Data_ProviderName]` |
| `AirInvestigationData` | `Data.ResourceIdentifiers.$id` | `principal.labels[Data_resourceidentifier_$id]` `additional.fields[Data_resourceidentifier_$id]` | `additional.fields[Data_resourceidentifier_$id]` |
| `AirInvestigationData` | `Data.ResourceIdentifiers.Type` | `principal.labels[Data_resourceidentifier_type]` `additional.fields[Data_resourceidentifier_type]` | `additional.fields[Data_resourceidentifier_type]` |
| `AirInvestigationData` | `Data.Investigations.Id` | `principal.labels[investigation_Id]` `additional.fields[investigation_Id]` | `additional.fields[investigation_Id]` |
| `AirInvestigationData` | `Data.Investigations.InvestigationStatus` | `principal.labels[InvestigationStatus]` `additional.fields[InvestigationStatus]` | `additional.fields[InvestigationStatus]` |
| `AirInvestigationData` | `Data.Investigations.$id` | `principal.labels[investigation_$id]` `additional.fields[investigation_$id]` | `additional.fields[investigation_$id]` |
| `AirInvestigationData` | `Data.RunningTime` | `about.labels[Data_RunningTime]` `additional.fields[Data_RunningTime]` | `additional.fields[Data_RunningTime]` |
| `AirInvestigationData` | `Data.SourceAlertType` | `about.labels[Data_SourceAlertType]` `additional.fields[Data_SourceAlertType]` | `additional.fields[Data_SourceAlertType]` |
| `AirInvestigationData` | `Data.SourceTemplateType` | `about.labels[SourceTemplateType]` `additional.fields[SourceTemplateType]` | `additional.fields[SourceTemplateType]` |
| `AirInvestigationData` | `Data.Status` | `about.labels[Status]` `additional.fields[Status]` | `additional.fields[Status]` |
| `AirInvestigationData` | `Data.TimeGenerated` | `about.labels[TimeGenerated]` `additional.fields[TimeGenerated]` | `additional.fields[TimeGenerated]` |
| `AirInvestigationData` | `Data.Version` | `about.labels[Data_Version]` `additional.fields[Data_Version]` | `additional.fields[Data_Version]` |
| `AirInvestigationData` | `Data.WorkspaceResourceGroup` | `about.labels[Data_WorkspaceResourceGroup]` `additional.fields[Data_WorkspaceResourceGroup]` | `additional.fields[Data_WorkspaceResourceGroup]` |
| `AirInvestigationData` | `Data.ExtendedLinks.Href` | `about.labels[extendedlink_Href]` `additional.fields[extendedlink_Href]` | `additional.fields[extendedlink_Href]` |
| `AirInvestigationData` | `Data.ExtendedLinks.Label` | `about.labels[extendedlink_Label]` `additional.fields[extendedlink_Label]` | `additional.fields[extendedlink_Label]` |
| `AirInvestigationData` | `Data.ExtendedLinks.Type` | `about.labels[extendedlink_Type]` `additional.fields[extendedlink_Type]` | `additional.fields[extendedlink_Type]` |
| `FileRead, FileUploadedToCloud, FileCopiedToClipboard, FileTransferredByBluetooth, FileCopiedToRemoteDesktopSession, FileCopiedToRemovableMedia` | `EnforcementMode` | `target.labels[EnforcementMode]` `additional.fields[EnforcementMode]` | `additional.fields[EnforcementMode]` |
| `FileRead, FileUploadedToCloud, FileCopiedToClipboard, FileTransferredByBluetooth, FileCopiedToRemoteDesktopSession, FileCopiedToRemovableMedia` | `OriginatingDomain` | `principal.labels[OriginatingDomain]` `additional.fields[OriginatingDomain]` | `additional.fields[OriginatingDomain]` |
| `FileRead, FileUploadedToCloud, FileCopiedToClipboard, FileTransferredByBluetooth, FileCopiedToRemoteDesktopSession, FileCopiedToRemovableMedia` | `TargetDomain` | `target.labels[TargetDomain]` `additional.fields[TargetDomain]` | `additional.fields[TargetDomain]` |
| `Enable Strong Authentication.` | `ExtendedProperties` | `about.labels[%{data.Name}]` `additional.fields[%{data.Name}]` | `additional.fields[%{data.Name}]` |
| `RemovableMediaUnmount, RemovableMediaMount` | `Scope` | `target.labels[Scope]` `additional.fields[Scope]` | `additional.fields[Scope]` |
| `Set-HostedContentFilterPolicy` | `ExternalAccess` | `about.labels[ExternalAccess]` `additional.fields[ExternalAccess]` | `additional.fields[ExternalAccess]` |
| `ViewedApprovalRequest, ApprovedRequest` | `ItemName` | `target.labels[ItemName]` `additional.fields[ItemName]` | `additional.fields[ItemName]` |
| `SignInEvent, ListCreated, ListViewUpdated, FileTranscriptContentAccessed, SharingLinkCreated, SharingLinkUpdated, AddedToSharingLink, SharingLinkUsed` | `CustomizedDoclib` | `principal.labels[CustomizedDoclib]` `additional.fields[CustomizedDoclib]` | `additional.fields[CustomizedDoclib]` |
| `SignInEvent, ListCreated, ListViewUpdated, FileTranscriptContentAccessed, SharingLinkCreated, SharingLinkUpdated, AddedToSharingLink, SharingLinkUsed` | `FromApp` | `principal.labels[FromApp]` `additional.fields[FromApp]` | `additional.fields[FromApp]` |
| `AdminSubmissionTablAllow` | `MessageDate` | `about.labels[message_date]` `additional.fields[message_date]` | `additional.fields[message_date]` |
| `AdminSubmissionTablAllow` | `ExtendedProperties` | `principal.labels[%{data.Name}]` `additional.fields[%{data.Name}]` | `additional.fields[%{data.Name}]` |
| `AdminSubmissionTablAllow` | `ExtendedProperties` | `about.labels[%{data.Name}]` `additional.fields[%{data.Name}]` | `additional.fields[%{data.Name}]` |
| `SensitivityLabeledFileRenamed, SensitivityLabeledFileOpened, SensitivityLabelUpdated, SensitivityLabelApplied, PublicEndpoint` | `TargetLocation` | `target.labels[target_location]` `additional.fields[target_location]` | `additional.fields[target_location]` |
| `SensitivityLabeledFileRenamed, SensitivityLabeledFileOpened, SensitivityLabelUpdated, SensitivityLabelApplied, PublicEndpoint` | `UserSku` | `target.labels[user_sku]` `additional.fields[user_sku]` | `additional.fields[user_sku]` |
| `SensitivityLabeledFileRenamed, SensitivityLabeledFileOpened, SensitivityLabelUpdated, SensitivityLabelApplied, PublicEndpoint` | `LabelId` | `target.labels[label_id]` `additional.fields[label_id]` | `additional.fields[label_id]` |
| `FileCopiedToClipboard, FileTransferredByBluetooth, FileCopiedToRemoteDesktopSession, FileCopiedToRemovableMedia` | `Scope` | `target.labels[Scope]` `additional.fields[Scope]` | `additional.fields[Scope]` |
| `FileCopiedToClipboard, FileTransferredByBluetooth, FileCopiedToRemoteDesktopSession, FileCopiedToRemovableMedia` | `TargetFilePath` | `target.labels[target_file_path]` `additional.fields[target_file_path]` | `additional.fields[target_file_path]` |
| `Add group., Add member to group., Remove member from group., Add user., Delete user., Update user., Change user license., Change user password., Update StsRefreshTokenValidFrom Timestamp., Set federation settings on domain., Verify domain., Delete group., Update group., Set Company Information., Reset user password., Disable account., Delete application password for user., Add registered users to device., Add registered owner to device., Add owner to group., Add OAuth2PermissionGrant., Consent to application., Add service principal., Remove service principal., Update service principal., Add member to role., Remove member from role., Add label., Create company, Update label., Add delegated permission grant., Add app role assignment to service principal., Update application., Update application -- Certificates and secrets management , Add owner to application., Add application., Add device configuration., Add unverified domain., Add policy., Add device., Delete device., Update device., Create application password for user., Device no longer managed., Enable account., Device no longer compliant., Add app role assignment to group., Remove owner from group., Add owner to policy., Add contact., Update policy., Remove delegated permission grant.` | `ExtendedProperties` | `about.labels[%{data.Name}]` `additional.fields[%{data.Name}]` | `additional.fields[%{data.Name}]` |
| `WebMembersCanShareModified, WebRequestAccessModified, NetworkAccessPolicyChanged, PreviewModeEnabledSet, OfficeOnDemandSet, SharingPolicyChanged, SiteLocksChanged, SiteIBModeSet, DeviceAccessPolicyChanged, WebAccessRequestApproverModified, UserLoggedIn, UserLoginFailed, Update StsRefreshTokenValidFrom Timestamp., AccessRequestUpdated, SiteCollectionAdminAdded, SiteCollectionAdminRemoved, SharingInvitationUpdated, Delete group., Add group., Update group., Set Company Information., Set federation settings on domain., Verify domain., Reset user password., Disable account., Delete application password for user., Consent to application., Create application password for user., Add service principal credentials., Remove service principal credentials.` | `ModifiedProperties` | `target.labels[Expire date]` `additional.fields[Expire date]` | `additional.fields[Expire date]` |
| `WebMembersCanShareModified, WebRequestAccessModified, NetworkAccessPolicyChanged, PreviewModeEnabledSet, OfficeOnDemandSet, SharingPolicyChanged, SiteLocksChanged, SiteIBModeSet, DeviceAccessPolicyChanged, WebAccessRequestApproverModified, UserLoggedIn, UserLoginFailed, Update StsRefreshTokenValidFrom Timestamp., AccessRequestUpdated, SiteCollectionAdminAdded, SiteCollectionAdminRemoved, SharingInvitationUpdated, Delete group., Add group., Update group., Set Company Information., Set federation settings on domain., Verify domain., Reset user password., Disable account., Delete application password for user., Consent to application., Create application password for user., Add service principal credentials., Remove service principal credentials.` | `ModifiedProperties` | `target.labels[%{field.Name}]` `additional.fields[%{field.Name}]` | `additional.fields[%{field.Name}]` |
| `TaskListRead` | `Tasks` | `target.labels[task]` `additional.fields[task]` | `additional.fields[task]` |
| `ConnectFromExternalApplication, GetWorkspaces` | `Activity` | `about.labels[activity]` `additional.fields[activity]` | `additional.fields[activity]` |
| `GetWorkspaces` | `ActivityId` | `about.labels[ActivityId]` `additional.fields[ActivityId]` | `additional.fields[ActivityId]` |
| `FileSensitivityLabelChanged, SensitivityLabelUpdated, FileSensitivityLabelApplied` | `SensitivityLabelEventData.ActionSource` | `principal.labels[SensitivityLabelEventData_ActionSource]` `additional.fields[SensitivityLabelEventData_ActionSource]` | `additional.fields[SensitivityLabelEventData_ActionSource]` |
| `FileSensitivityLabelChanged, SensitivityLabelUpdated, FileSensitivityLabelApplied` | `SensitivityLabelEventData.LabelEventType` | `target.labels[SensitivityLabelEventData_LabelEventType]` `additional.fields[SensitivityLabelEventData_LabelEventType]` | `additional.fields[SensitivityLabelEventData_LabelEventType]` |
| `FileSensitivityLabelChanged` | `IsManagedDevice` | `about.labels[is_managed_device]` `additional.fields[is_managed_device]` | `additional.fields[is_managed_device]` |
| `TaskListRead` | `UserKey` | `principal.labels[user_key]` `additional.fields[user_key]` | `additional.fields[user_key]` |
| `MCAS_ALERT_ANUBIS_DETECTION_NEW_COUNTRY, MCAS_ALERT_ANUBIS_DETECTION_REPEATED_ACTIVITY_FAILED_LOGIN, MCAS_ALERT_ANUBIS_DETECTION_REPEATED_ACTIVITY_DELETE, MCAS_ALERT_ANUBIS_DETECTION_REPEATED_ACTIVITY_ADMIN_ACTIVITY, MCAS_ALERT_ANUBIS_DETECTION_REPEATED_ACTIVITY_DOWNLOAD, MCAS_ALERT_ANUBIS_DETECTION_RISKY_IP_ANONYMOUS, MCAS_ALERT_ANUBIS_DETECTION_VELOCITY, TaskListRead, PutConnection, AdminSubmissionTablAllow, Add contact., PutConnectionPermission, O365SyncAdminUserPromotion` | `ObjectId` | `target.labels[object_id]` `additional.fields[object_id]` | `additional.fields[object_id]` |
| `Set-TransportRule` | | `target.resource.type (ACCESS_POLICY)` | `target.resource.resource_type (ACCESS_POLICY)` |
| `TaskModified, TaskAssigned, UpdateEmailSubscription, SubTaskCreated, TaskRead, SubTaskUpdated, TaskStatusSubmitted` | | `target.resource.type (TASK)` | `target.resource.resource_type (TASK)` |
## What's next
- [Data ingestion to Google Security Operations](https://docs.cloud.google.com/chronicle/docs/data-ingestion-flow)
## Change Log
[View the Change Log for this parser](https://docs.cloud.google.com/chronicle/docs/ingestion/parser-list/office-365-changelog.md.txt)
**Need more help?** [Get answers from Community members and Google SecOps professionals.](https://security.googlecloudcommunity.com/)