*This page
applies to **Apigee** and **Apigee hybrid**.*
*View [Apigee Edge](https://docs.apigee.com/api-platform/get-started/what-apigee-edge) documentation.*

When you call an API proxy on Apigee that has OAuth security, Apigee is responsible for
verifying access tokens. Think of Apigee as the gatekeeper -- no API call can pass through that
does not have an access token that can be verified.
> [!IMPORTANT]
> **Tip:** When verifying an access token, if you happen to see this error: "Invalid API call as no apiproduct match found", go to this [Apigee Community article](https://discuss.google.dev/t/oauth2-0-access-token-verification-throws-invalid-api-call-as-no-apiproduct-match-found-error/17064) for details on the cause of this error and steps to correct it.
## Adding a VerifyAccessToken policy
To configure token verification, place an [OAuthV2 policy](https://docs.cloud.google.com/apigee/docs/api-platform/reference/policies/oauthv2-policy.md.txt) with the
**VerifyAccessToken** operation at the very beginning of the API proxy flow (the
beginning of the ProxyEndpoint Preflow). If placed there, access tokens will be verified before
any other processing takes place, and if a token is rejected, Apigee stops processing and returns
an error back to the client.
To access the API proxies page using the Apigee UI:
1. In the Google Cloud console, go to the **Apigee \> Proxy development** \> **API proxies** page.
[Go to API proxies](https://console.cloud.google.com/apigee/proxies)
2. From the list, select the proxy you wish to protect.
3. In the proxy details page, click the **Develop** tab.
4. In the navigation menu, under **Proxy endpoints** , **default** , click **PreFlow** . Typically, the endpoint you want is called **default** , although it is possible to create multiple proxy endpoints. If you do have multiple endpoints, you will probably want to follow these steps to perform token verification on each one. 
5. In the proxy flow editor, click
**Add policy step**.
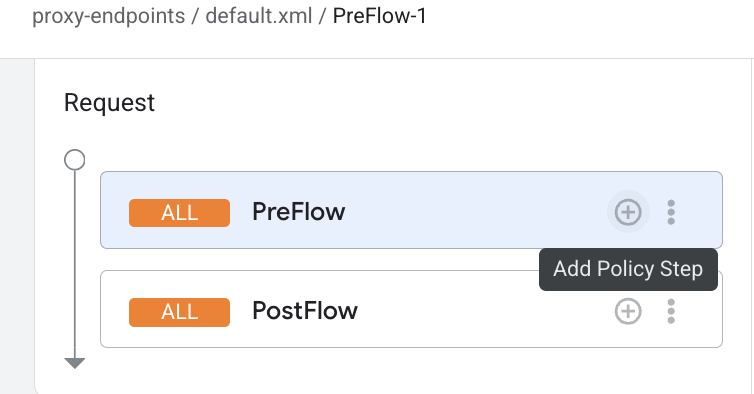
6. In the **Add policy step** dialog, select **Create new policy**.
7. From the policy list, under **Security** , select **OAuth v2.0**.
8. Optionally, change the policy name and display name. For example, for better readability, you might change the **Display name** and **Name** both to **VerifyAccessToken**.
9. Click **Add**.
The default policy is already configured with the VerifyAccessToken operation, so you do not
have to do anything further:
```
OAuth v2.0 1
false
VerifyAccessToken
```
> [!NOTE]
> **Note:** By default, VerifyAccessToken expects the access token to be sent in an Authorization header as a Bearer token. For example:
>
> ```
> -H "Authorization: Bearer Rft3dqrs56Blirls56a"
> ```
>
> You can change this default in the ` ` element in the
> OAuthV2 policy, as explained in the [OAuthV2 policy
> documentation](https://docs.cloud.google.com/apigee/docs/api-platform/reference/policies/oauthv2-policy#accesstokenelement).